
Juniper JN0-683 Practice Exam Questions & Answers
Juniper JN0-683 Exam Details
Key details for this exam, checked against the published exam outline
- Exam Code
- JN0-683
- Full Name
- Data Center Professional
- Issuing Body
- Juniper Networks
- Question Format (Our Bank)
- Multiple Choice
- Delivery
- Online proctored or at a Pearson VUE test centre
- Eligibility
- JNCIS-DC (JN0-481) or JNCIS-ENT certification required
- Full Question Set
- 65 questions Get All Questions
Free JN0-683 Practice Questions
Each question shows the correct answer and an explanation of why it is right
Question 1 Domain 1 Data Center Deployment and Management
You are asked to automatically provision new Juniper Networks devices in your network with minimal manual intervention Before you begin, which two statements are correct? (Choose two.)
Zero-Touch Provisioning (ZTP):
ZTP is a feature that allows for the automatic provisioning of devices with minimal manual intervention. It is widely used in large-scale deployments to quickly bring new devices online.
Key Requirements for ZTP:
A . DHCP Server: A DHCP server is crucial for ZTP as it provides the necessary information to new devices, such as the IP address, the location of the software image, and configuration files.
D . File Server: The file server is where the software image and configuration files are stored. The device downloads these files during the provisioning process.
Incorrect Options:
B . Syslog Server: While a syslog server is important for logging and monitoring, it is not a requirement for the initial provisioning process.
C . NTP Server: An NTP server is used for time synchronization, which is essential for accurate logging and operation but not specifically required for ZTP.
Data Center Reference:
ZTP simplifies the deployment process by automating the initial configuration steps, relying heavily on DHCP for communication and a file server for delivering the necessary configuration and software.
Question 2 Domain 1 Data Center Deployment and Management
You are deploying an IP fabric using EBGP and notice that your leaf devices are advertising and receiving all the routes. However, the routes are not installed in the routing table and are marked as hidden.
Which two statements describe how to solve the issue? (Choose two.)
Issue Overview:
The leaf devices in an IP fabric using eBGP are advertising and receiving all routes, but the routes are not being installed in the routing table and are marked as hidden. This typically indicates an issue with the BGP configuration, particularly with next-hop handling or AS path concerns.
Corrective Actions:
B . You need to configure a next-hop self policy: This action ensures that the leaf devices modify the next-hop attribute to their own IP address before advertising routes to their peers. This is particularly important in eBGP setups where the next-hop may not be directly reachable by other peers.
D . You need to configure multipath multiple-as: This setting allows the router to accept multiple paths from different autonomous systems (ASes) and use them for load balancing. Without this, the BGP process might consider only one path and mark others as hidden.
Incorrect Statements:
A . You need to configure as-override: AS-override is used to replace the AS number in the AS-path attribute to prevent loop detection issues in MPLS VPNs, not in a typical eBGP IP fabric setup.
C . You need to configure loops 2: There is no specific BGP command loops 2 relevant to resolving hidden routes in this context. It might be confused with allowas-in, which is used to allow AS path loops under certain conditions.
Data Center Reference:
Proper BGP configuration is crucial in IP fabrics to ensure route propagation and to prevent routes from being marked as hidden. Configuration parameters like next-hop self and multipath multiple-as are common solutions to ensure optimal route installation and load balancing in a multi-vendor environment.
Question 3 Domain 3 VXLAN
Exhibit.
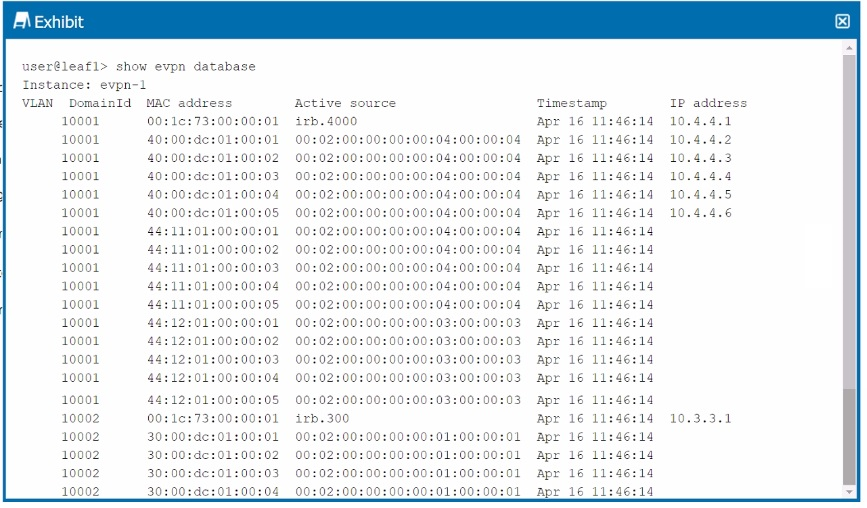
The exhibit shows the truncated output of the show evpn database command.
Given this output, which two statements are correct about the host with MAC address 40:00:dc:01:00:04? (Choose two.)
Understanding the Output:
The show evpn database command output shows the MAC address, VLAN, active source, timestamp, and IP address associated with various hosts in the EVPN instance.
Analysis of the MAC Address:
Option A: The MAC address 40:00:dc:01:00:04 is associated with the IP address 10.4.4.5, as indicated by the output in the IP address column. This confirms that this host has been assigned the IP 10.4.4.5.
Option D: The active source for the MAC address 40:00:dc:01:00:04 is listed as 00:02:00:00:00:04:00:04:00:00:04:00:04, which indicates that the host is connected via an ESI (Ethernet Segment Identifier) LAG (Link Aggregation Group). This setup is typically used in multi-homing scenarios to provide redundancy and load balancing across multiple physical links.
Conclusion:
Option A: Correct---The host with MAC 40:00:dc:01:00:04 is assigned IP 10.4.4.5.
Option D: Correct---The host is originating from an ESI LAG, as indicated by the active source value.
Get the complete JN0-683 question set
$20$40
Question 4 Domain 3 VXLAN
Exhibit.
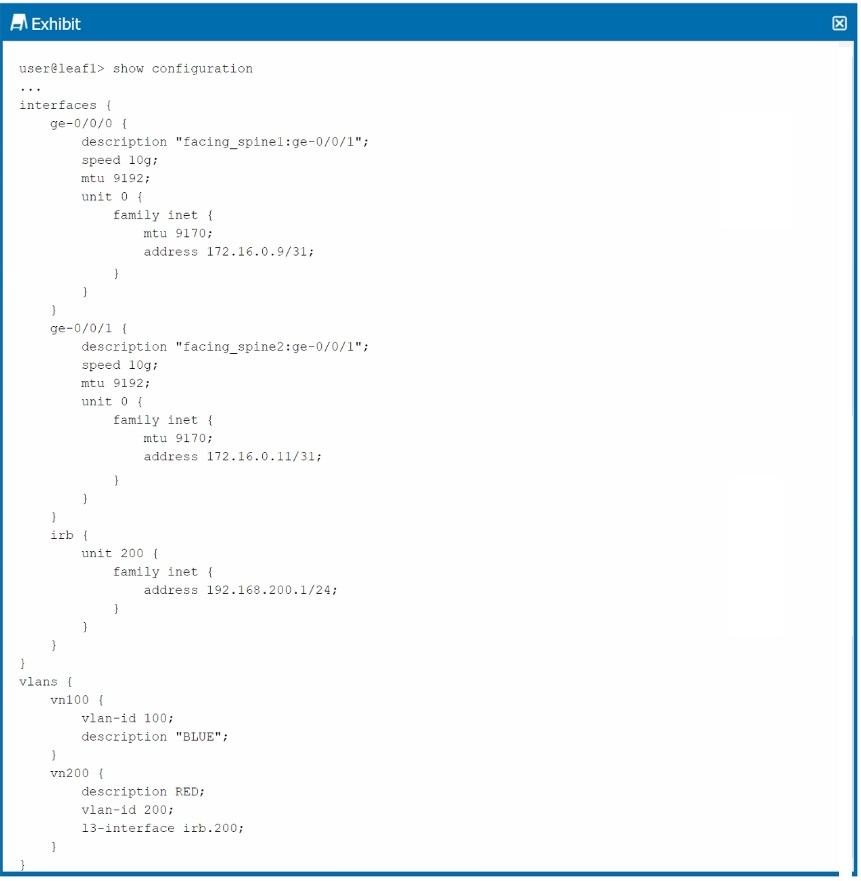
Host A is connected to vlan 100 on lead. Host B is connected to vlan 200 on leaf1. Host A and Host B ate unable to communicate. You have reviewed the touting and your hosts have the correct default route (.1)
Referring to the exhibit, which two commands will solve the problem? (Choose two.)
In the provided network configuration, Host A is in VLAN 100 and Host B is in VLAN 200. The issue arises because these two hosts are unable to communicate, which indicates that either the interfaces are not properly linked to their respective VLANs, or there is a missing static route required for inter-VLAN routing.
Step-by-Step Analysis:
VLAN Assignment:
The exhibit shows that irb.200 is correctly associated with VLAN 200 in the configuration. However, there is no corresponding irb.100 for VLAN 100. Without irb.100, the network lacks the logical interface to handle routing for VLAN 100. Thus, adding irb.100 to VLAN 100 is necessary.
Command to solve this:
set vlans vn100 13-interface irb.100
Static Route Configuration:
For inter-VLAN routing to occur, a static route needs to be configured that allows traffic to pass between different subnets (in this case, between VLAN 100 and VLAN 200). The command set routing-options static route 0.0.0.0/0 next-hop 192.168.200.10 would add a static route that directs all traffic from VLAN 100 to the correct gateway (192.168.200.10), which is necessary to route traffic between the two VLANs.
Command to solve this:
set routing-options static route 0.0.0.0/0 next-hop 192.168.200.10
Explanation of Incorrect Options:
Option A (delete vlans vn200 13-interface irb.200): This would remove the logical interface associated with VLAN 200, which is not desired because we need VLAN 200 to remain active and properly routed.
Option B (set interfaces irb unit 100 family inet address 192-168.100.1): This command would incorrectly assign an IP address that does not correspond with the subnet of VLAN 100 (192.168.200.1/24). This could create a misconfiguration, leading to routing issues.
Data Center Reference:
For a Data Center, proper VLAN management and static routing are crucial for ensuring that different network segments can communicate effectively, especially when dealing with separated subnets or zones like in different VLANs. This aligns with best practices in DCIM (Data Center Infrastructure Management) which stress the importance of proper network configuration to avoid downtime and ensure seamless communication between all critical IT infrastructure components.
Ensuring that the correct interfaces are associated with the correct VLANs and having the proper static routes in place are both essential steps in maintaining a robust and reliable data center network.
This detailed analysis reflects best practices as noted in standard data center design and network configuration guides.
Question 5 Domain 4 EVPN-VXLAN Signaling
Your organization is implementing EVPN-VXLAN and requires multiple overlapping VLAN-IDs. You decide to use a routing-instance type mac-vrf to satisfy this request.
Which two statements are correct in this scenario? (Choose two.)
Understanding the Scenario:
EVPN-VXLAN deployments often involve scenarios where multiple tenants or applications require overlapping VLAN IDs, which can be managed using the mac-vrf routing instance type. This allows you to segregate traffic within the same VLAN ID across different tenants.
Host-facing Interface Configuration:
A . Host-facing interfaces must be configured using a service-provider style configuration: This is correct. In mac-vrf configurations, host-facing interfaces (those connecting end devices) typically follow a service-provider style configuration, where each customer or tenant's traffic is isolated even if overlapping VLAN IDs are used.
B . Host-facing interfaces must be configured using enterprise-style configuration: This is incorrect for mac-vrf instances because enterprise-style configurations are more common in simpler, less segmented networks.
Routing Instance Service Type:
D . The routing-instance service type can be VLAN-based: This is correct. The service type in mac-vrf can indeed be VLAN-based, which is particularly useful in scenarios where VLAN ID overlap is needed between different tenants or services.
Data Center Reference:
The mac-vrf instance type is powerful for handling complex multi-tenant environments in EVPN-VXLAN, especially when dealing with overlapping VLAN IDs across different segments of the network.
Question 6 Domain 4 EVPN-VXLAN Signaling
Which parameter is used to associate a received route with a local VPN route table?
Understanding VPN Route Table Association:
In MPLS/VPN and EVPN networks, the route-target community is a BGP extended community attribute used to control the import and export of VPN routes. It associates received routes with the appropriate VPN route tables on the PE (Provider Edge) routers.
Function of Route-Target Community:
The route-target community tag ensures that routes are imported into the correct VRF (Virtual Routing and Forwarding) instance, allowing them to be correctly routed within the VPN.
Conclusion:
Option A: Correct---The route-target community is used to associate received routes with a local VPN route table.
Question 7 Domain 3 VXLAN
You are implementing seamless stitching between two data centers and have a proposed configuration for a border leaf device.
In this scenario, which two statements are correct? {Choose two.)
Understanding Seamless Stitching:
Seamless stitching is used in EVPN to interconnect two data centers, allowing for consistent Layer 2 and Layer 3 connectivity across them. This is often achieved by translating VNIs (Virtual Network Identifiers) between the data centers.
Translation-VNI:
Option B: The translation VNI must be different in each data center to ensure that traffic can be correctly routed and distinguished as it crosses between the data centers. This differentiation helps to maintain the integrity of the traffic flows and prevents any potential overlap or conflict in VNIs.
Ethernet Segment Identifier (ESI):
Option D: The ESI must match in both data centers to ensure that the same Ethernet segment (which could be multihomed) is recognized consistently across the data centers. Matching ESIs are crucial for maintaining a unified view of the Ethernet segment across the interconnected fabric.
Conclusion:
Option B: Correct---Translation VNIs must be unique to each data center for proper traffic distinction.
Option D: Correct---Matching ESIs are necessary to maintain consistent Ethernet segment identification across both data centers.
Question 8 Domain 6 Data Center Multitenancy and Security
You are asked to set up an IP fabric that supports Al or ML workloads. You have chosen to use lossless Ethernet in this scenario, which statement is correct about congestion management?
Understanding Lossless Ethernet and Congestion Management:
Lossless Ethernet is crucial for AI and ML workloads, where packet loss can significantly degrade performance. To implement lossless Ethernet, congestion management protocols like ECN (Explicit Congestion Notification) are used.
Role of ECN in Congestion Management:
Option A: In an IP fabric that supports lossless Ethernet, when a switch experiences congestion, it can mark packets using ECN. This marking notifies the source device of the congestion, allowing the source to reduce its transmission rate, thereby preventing packet loss.
Conclusion:
Option A: Correct---The switch experiencing congestion notifies the source device via ECN marking.
What the Juniper JN0-683 Exam Covers
Exam domains verified against the Official Juniper JN0-683 exam guide, last checked November 2026.
Domain 1 Data Center Deployment and Management
Tests knowledge of deployment phase operations including Zero-touch provisioning (ZTP) which automates device setup and configuration without manual intervention. Focuses on concepts and practices used by experienced data center architects and engineers.
Domain 2 Layer 3 Fabrics
Assesses understanding of IP-based fabric design and structure that supports scalability and performance in modern data centers. Covers IP fabric architecture and how traffic routing works within the network fabric.
Domain 3 VXLAN
Tests knowledge of VXLAN technology including both control plane mechanisms for device communication setup and data plane operations for actual traffic transmission. Candidates must understand how VXLAN works end to end.
Domain 4 EVPN-VXLAN Signaling
Evaluates understanding of Ethernet VPN architecture with focus on route types and multicast handling. Covers Multiprotocol BGP application, Centralized Routing and Bridging (CRB) and Edge Routing and Bridging (ERB) models, MAC learning and symmetric routing.
Domain 5 Data Center Interconnect
Tests knowledge of connecting multiple data centers using Layer 2 and Layer 3 stretching and stitching techniques that join different network fabrics together. Covers EVPN-signaled VXLAN technology enabling communication between interconnected data centers.
Domain 6 Data Center Multitenancy and Security
Focuses on single-tenant and multitenant data center architectures essential for shared infrastructure environments. Tests knowledge of tenant traffic isolation at both Layer 2 and Layer 3 levels and data center security concepts.
Sample question from this domain above Q8
JN0-683 Exam FAQ
Common questions about the exam itself
What background do I need before taking JN0-683?
How long should I prepare for JN0-683?
What makes JN0-683 harder than the JNCIS-DC exam?
Which objective area in JN0-683 do candidates struggle with most?
How is the JN0-683 exam delivered and what happens on exam day?
What happens if I fail JN0-683 and need to retake it?
How long is the JNCIP-DC certification valid after I pass JN0-683?
What job role does the JNCIP-DC certification (JN0-683) lead to?
How does JN0-683 fit into the Juniper Data Center certification track?
Is there an Expert level exam after JN0-683 in the data center track?
Other Juniper Exams
Free practice questions for more Juniper certification exams