Key details for this exam, checked against the published exam outline
Each question shows the correct answer and an explanation of why it is right
Click the Exhibit button.
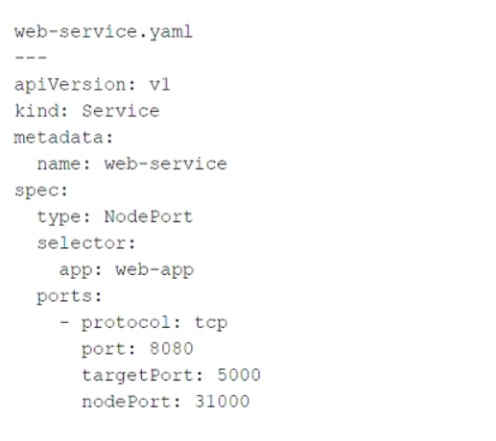
Referring to the exhibit, which port number would external users use to access the WEB application?
The YAML file provided in the exhibit defines a Kubernetes Service object of type NodePort. Let's break down the key components of the configuration and analyze how external users access the WEB application:
Key Fields in the YAML File:
type: NodePort:
This specifies that the service is exposed on a static port on each node in the cluster. External users can access the service using the node's IP address and the assigned nodePort.
port: 8080:
This is the port on which the service is exposed internally within the Kubernetes cluster. Other services or pods within the cluster can communicate with this service using port 8080.
targetPort: 5000:
This is the port on which the actual application (WEB application) is running inside the pod. The service forwards traffic from port: 8080 to targetPort: 5000.
nodePort: 31000:
This is the port on the node (host machine) where the service is exposed externally. External users will use this port to access the WEB application.
How External Users Access the WEB Application:
External users access the WEB application using the node's IP address and the nodePort value (31000).
The Kubernetes service listens on this port and forwards incoming traffic to the appropriate pods running the WEB application.
Why Not Other Options?
A . 80: Port 80 is commonly used for HTTP traffic, but it is not specified in the YAML file. The service does not expose port 80 externally.
B . 8080: Port 8080 is the internal port used within the Kubernetes cluster. It is not the port exposed to external users.
D . 5000: Port 5000 is the target port where the application runs inside the pod. It is not directly accessible to external users.
Why 31000?
NodePort Service Type: The NodePort service type exposes the application on a high-numbered port (default range: 30000--32767) on each node in the cluster.
External Accessibility: External users must use the nodePort value (31000) along with the node's IP address to access the WEB application.
JNCIA Cloud Reference:
The JNCIA-Cloud certification covers Kubernetes networking concepts, including service types like ClusterIP, NodePort, and LoadBalancer. Understanding how NodePort services work is essential for exposing applications to external users in Kubernetes environments.
For example, Juniper Contrail integrates with Kubernetes to provide advanced networking features, such as load balancing and network segmentation, for services like the one described in the exhibit.
Kubernetes Documentation: Service Types
Juniper JNCIA-Cloud Study Guide: Kubernetes Networking
Which command would you use to see which VMs are running on your KVM device?
KVM (Kernel-based Virtual Machine) is a popular open-source virtualization technology that allows you to run virtual machines (VMs) on Linux systems. The virsh command-line tool is used to manage KVM VMs. Let's analyze each option:
A . virt-install
Incorrect: The virt-install command is used to create and provision new virtual machines. It is not used to list running VMs.
B . virsh net-list
Incorrect: The virsh net-list command lists virtual networks configured in the KVM environment. It does not display information about running VMs.
C . virsh list
Correct: The virsh list command displays the status of virtual machines managed by the KVM hypervisor. By default, it shows only running VMs. You can use the --all flag to include stopped VMs in the output.
D . VBoxManage list runningvms
Incorrect: The VBoxManage command is used with Oracle VirtualBox, not KVM. It is unrelated to KVM virtualization.
Why virsh list?
Purpose-Built for KVM: virsh is the standard tool for managing KVM virtual machines, and virsh list is specifically designed to show the status of running VMs.
Simplicity: The command is straightforward and provides the required information without additional complexity.
JNCIA Cloud Reference:
The JNCIA-Cloud certification emphasizes understanding virtualization technologies, including KVM. Managing virtual machines using tools like virsh is a fundamental skill for operating virtualized environments.
For example, Juniper Contrail supports integration with KVM hypervisors, enabling the deployment and management of virtualized network functions (VNFs). Proficiency with KVM tools ensures efficient management of virtualized infrastructure.
KVM Documentation: virsh Command
Juniper JNCIA-Cloud Study Guide: Virtualization
When considering OpenShift and Kubernetes, what are two unique resources of OpenShift? (Choose two.)
OpenShift extends Kubernetes by introducing additional resources and abstractions to simplify application development and deployment. Let's analyze each option:
A . routes
Correct:
Routes are unique to OpenShift and provide a way to expose services externally by mapping a hostname to a service. They are built on top of Kubernetes Ingress but offer additional features like TLS termination and wildcard support.
B . build
Correct:
Builds are unique to OpenShift and represent the process of transforming source code into container images. OpenShift provides build configurations and strategies (e.g., Docker, S2I) to automate this process, which is not natively available in Kubernetes.
C . ingress
Incorrect:
Ingress is a standard Kubernetes resource used to manage external access to services. While OpenShift uses Ingress as the foundation for its Routes, Ingress itself is not unique to OpenShift.
D . services
Incorrect:
Services are a core Kubernetes resource used to expose applications internally within the cluster. They are not unique to OpenShift.
Why These Resources?
Routes: Extend Kubernetes Ingress to provide advanced external access capabilities, such as custom domain mappings and TLS termination.
Builds: Simplify the process of building container images directly within the OpenShift platform, enabling streamlined CI/CD workflows.
JNCIA Cloud Reference:
The JNCIA-Cloud certification covers OpenShift's unique resources as part of its curriculum on container orchestration platforms. Understanding the differences between OpenShift and Kubernetes resources is essential for leveraging OpenShift's full capabilities.
For example, Juniper Contrail integrates with OpenShift to provide advanced networking features, ensuring secure and efficient traffic routing for Routes and Builds.
OpenShift Documentation: Routes and Builds
Juniper JNCIA-Cloud Study Guide: OpenShift vs. Kubernetes
Which virtualization method requires less duplication of hardware resources?
Virtualization methods differ in how they utilize hardware resources. Let's analyze each option:
A . OS-level virtualization
Correct: OS-level virtualization (e.g., containers) uses the host operating system's kernel to run isolated user-space instances (containers). Since containers share the host OS kernel, there is less duplication of hardware resources compared to other virtualization methods.
B . hardware-assisted virtualization
Incorrect: Hardware-assisted virtualization (e.g., Intel VT-x, AMD-V) enables full virtual machines (VMs) to run on physical hardware. Each VM includes its own operating system, leading to duplication of resources like memory and CPU.
C . full virtualization
Incorrect: Full virtualization involves running a complete guest operating system on top of a hypervisor. Each VM requires its own OS, resulting in significant resource duplication.
D . paravirtualization
Incorrect: Paravirtualization modifies the guest operating system to communicate directly with the hypervisor. While it reduces some overhead compared to full virtualization, it still requires separate operating systems for each VM, leading to resource duplication.
Why OS-Level Virtualization?
Resource Efficiency: Containers share the host OS kernel, eliminating the need for multiple operating systems and reducing resource duplication.
Lightweight: Containers are faster to start and consume fewer resources compared to VMs.
JNCIA Cloud Reference:
The JNCIA-Cloud certification emphasizes understanding virtualization technologies, including OS-level virtualization. Containers are a key component of modern cloud-native architectures due to their efficiency and scalability.
For example, Juniper Contrail integrates with container orchestration platforms like Kubernetes to manage OS-level virtualization workloads efficiently.
Docker Documentation: Container Basics
Juniper JNCIA-Cloud Study Guide: Virtualization
Which two statements are correct about Network Functions Virtualization (NFV)? (Choose two.)
Network Functions Virtualization (NFV) is a framework designed to virtualize network services traditionally run on proprietary hardware. It decouples network functions from dedicated hardware appliances and implements them as software running on standard servers or virtual machines. Let's analyze each statement:
A . The NFV framework explains how VNFs fit into the whole solution.
Correct: The NFV framework provides a structured approach to deploying and managing Virtualized Network Functions (VNFs). It defines how VNFs interact with other components, such as the NFV Infrastructure (NFVI), Management and Orchestration (MANO), and the underlying hardware.
B . The NFV Infrastructure (NFVI) is a component of NFV.
Correct: The NFV Infrastructure (NFVI) is a critical part of the NFV architecture. It includes the physical and virtual resources (e.g., compute, storage, networking) that host and support VNFs. NFVI acts as the foundation for deploying and running virtualized network functions.
C . The NFV Infrastructure (NFVI) is not a component of NFV.
Incorrect: This statement contradicts the NFV architecture. NFVI is indeed a core component of NFV, providing the necessary infrastructure for VNFs.
D . The NFV framework is defined by the W3C.
Incorrect: The NFV framework is defined by the European Telecommunications Standards Institute (ETSI), not the W3C. ETSI's NFV Industry Specification Group (ISG) established the standards and architecture for NFV.
Why These Answers?
Framework The NFV framework provides a comprehensive view of how VNFs integrate into the overall solution, ensuring scalability and flexibility.
NFVI Role: NFVI is essential for hosting and supporting VNFs, making it a fundamental part of the NFV architecture.
JNCIA Cloud Reference:
The JNCIA-Cloud certification covers NFV as part of its cloud infrastructure curriculum. Understanding the NFV framework and its components is crucial for deploying and managing virtualized network functions in cloud environments.
For example, Juniper Contrail integrates with NFV frameworks to deploy and manage VNFs, enabling service providers to deliver network services efficiently and cost-effectively.
ETSI NFV Framework Documentation
Juniper JNCIA-Cloud Study Guide: Network Functions Virtualization
65 questions covering all exam domains, starting from $20
Exam domains verified against: Official Juniper JN0-214 exam guide, last checked September 2026.
Cloud Fundamentals covers deployment models such as public, private, and hybrid cloud environments, along with service models including SaaS, IaaS, and PaaS. Candidates learn cloud-native architecture principles and explore automation tools used in modern cloud infrastructure. This domain establishes the foundational concepts needed to understand how cloud systems operate and interoperate.
This domain examines Network Functions Virtualization including NFV architecture, orchestration, and virtual network functions, plus software-defined networking concepts covering SDN architecture, controllers, and solutions. Candidates understand how virtualization and SDN technologies transform traditional network infrastructure. Understanding both NFV and SDN is essential for designing flexible, scalable cloud networks.
Sample question from this domain above: Q4
Network Virtualization covers virtual network types and the distinction between underlay and overlay networks. Candidates study encapsulation and tunneling technologies including MPLS over GRE, MPLS over UDP, VXLAN, EVPN with VXLAN, and GENEVE. These techniques enable multiple logical networks to coexist on shared physical infrastructure.
Sample question from this domain above: Q1
Cloud Virtualization explores Linux architecture, hypervisor types (type 1 and type 2), and hypervisor operations including KVM and QEMU concepts. Candidates learn to create and manage virtual machines within Linux environments. The domain also covers containers, their relationship to virtual machines, container components, and Docker-based container creation.
This domain focuses on OpenStack concepts and operations including creating and managing virtual machines, using HEAT templates written in YAML for automation, and navigating OpenStack user interfaces. Candidates learn about OpenStack networking plugins and how to configure security groups. OpenStack provides an open-source foundation for building private clouds.
Kubernetes orchestration covers creating and managing containers at scale using Kubernetes API objects such as Pods, ReplicaSets, Deployments, and Services. Candidates learn about Kubernetes namespaces and Container Network Interface plug-ins. Kubernetes enables declarative management of containerized applications across clusters.
OpenShift orchestration includes creating, managing, and monitoring workloads on the OpenShift platform using both the CLI and WebUI. Candidates distinguish between node types including provisioner and control plane nodes, and understand different network types such as routable, provisioning, and management networks. OpenShift builds on Kubernetes to provide enterprise-ready container orchestration.
Common questions about the exam itself

