
Palo Alto Networks NetSec-Analyst Practice Exam Questions & Answers
Palo Alto Networks NetSec-Analyst Exam Details
Key details for this exam, checked against the published exam outline
- Exam Code
- NetSec-Analyst
- Full Name
- Palo Alto Networks Network Security Analyst
- Issuing Body
- Palo Alto Networks
- Question Format (Our Bank)
- Multiple Choice
- Delivery
- In-person at Pearson VUE test centre
- Eligibility
- No formal prerequisites. Hands-on experience with Palo Alto Networks platforms assumed.
- Validity
- 2 years from the date earned
- Full Question Set
- 74 questions Get All Questions
Free NetSec-Analyst Practice Questions
Each question shows the correct answer and an explanation of why it is right
Question 1 Domain 4 Troubleshooting
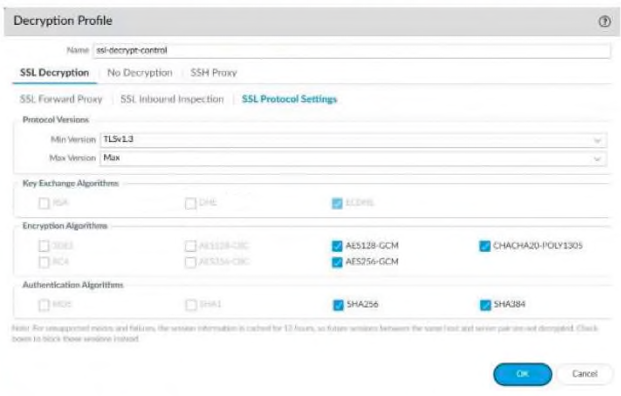
Based on the image below, what is a risk associated with this configuration?
Comprehensive and Detailed 150 to 250 words of Explanation From Palo Alto Networks Network Security Analyst Knowledge:
In the provided image, the Decryption Profile is configured with a Min Version of TLSv1.3. While this represents a high security posture, it introduces a significant operational risk: compatibility issues with legacy applications or clients.
Many older operating systems, web browsers, and legacy internal applications do not support TLS 1.3. If a client or server attempts to negotiate a connection using an older, unsupported protocol version (such as TLS 1.2 or 1.1), the firewall will drop the connection because it falls below the configured minimum threshold. A Network Security Analyst must balance the need for modern encryption with the functional requirements of the network.
Option C is incorrect because disabling weak algorithms like 3DES and RC4 actually improves the security posture. Option D is incorrect because the firewall is fully capable of decrypting traffic using Perfect Forward Secrecy (PFS) if the appropriate certificates are installed. Option B is a general concern for all decryption but is not a specific risk of the versioning shown. Therefore, the most immediate risk of setting the minimum version to TLS 1.3 is the potential disruption of services for any user or system still relying on the widely-used TLS 1.2 protocol or older.
Question 2 Domain 2 Policy Creation and Application
An administrator is using Strata Cloud Manager (SCM) and notices that several firewalls are reporting a low health score due to "Untrusted Certificates" being used for management. Which specific SCM dashboard provides the fastest way to identify which certificates are nearing expiration across the entire estate?
Comprehensive and Detailed 150 to 250 words of Explanation From Palo Alto Networks Network Security Analyst Knowledge:
In a modern Palo Alto Networks environment managed by Strata Cloud Manager (SCM), the Activity Insights dashboard is specifically designed to provide visibility into operational risks that are not necessarily 'threats' but impact the stability of the security posture. One of its core functions is monitoring the lifecycle of certificates used throughout the network, including those for SSL Decryption, GlobalProtect, and web interface management.
While the Device Health Dashboard (Option D) provides a generalized health score based on operational metrics like CPU and memory, Activity Insights drills down into specific configuration risks such as expired or weak certificates. This allows a Network Security Analyst to proactively identify which firewalls or service profiles are at risk of service disruption before a certificate actually expires. By centralizing this information, SCM eliminates the need for analysts to manually check local certificate stores on dozens or hundreds of individual firewalls, significantly reducing administrative overhead and ensuring that secure management channels remain operational without interruption.
Question 3 Domain 1 Object Configuration Creation and Application
In Strata Cloud Manager (SCM), which logical container is used to group firewalls that share the same configuration requirements, such as those at a specific regional office?
Comprehensive and Detailed 150 to 250 words of Explanation From Palo Alto Networks Network Security Analyst Knowledge:
In the SCM management architecture, Folders are the primary organizational units used to manage both policies and network settings for groups of firewalls. Folders replace the separate 'Device Group' and 'Template' hierarchy found in traditional Panorama deployments, providing a more streamlined 'Unified Policy' approach.
Folders support inheritance, meaning an analyst can define a 'Global' folder with company-wide policies and then create sub-folders (e.g., 'Region-North') that inherit those global rules while adding region-specific configurations. This structure allows the analyst to manage hundreds of devices as a single entity, ensuring consistency across the fleet. Understanding the SCM folder structure is a core objective for analysts migrating to cloud-based management, as it is the foundation for scaling security operations without increasing complexity.
Get the complete NetSec-Analyst question set
$20$40
Question 4 Domain 1 Object Configuration Creation and Application
Which action ensures that sensitive information such as medical records, financial transactions, and legal communications are not decrypted and that they maintain strong security?
Comprehensive and Detailed 150 to 250 words of Explanation From Palo Alto Networks Network Security Analyst Knowledge:
In a Palo Alto Networks environment, decryption is essential for visibility, but legal and compliance requirements often dictate that certain types of traffic---specifically those involving sensitive personal data---must remain encrypted. To comply with these regulations while still inspecting other high-risk traffic, a Network Security Analyst should create a 'no-decrypt' policy for traffic matching specific URL categories (D).
Palo Alto Networks provides predefined URL categories such as financial-services, health-and-medicine, and government. When these categories are used as matching criteria in a Decryption Policy rule with the action set to 'No Decrypt,' the firewall will bypass the SSL/TLS decryption process for that specific traffic. This ensures that the privacy of sensitive transactions, like medical records or banking, is maintained and that the raw data is never exposed in the firewall's memory or logs.
Furthermore, to maintain 'strong security' as requested, the analyst should attach a Decryption Profile to this no-decrypt rule. This profile can be configured to block sessions that use weak protocols (like SSLv3 or TLS 1.0) or expired certificates, ensuring that even if the traffic is not decrypted, it is still forced to meet modern security standards before entering or leaving the network.
Question 5 Domain 2 Policy Creation and Application
Which type of Security profile is required to prevent a "Brute Force" attack on a management portal or server by monitoring the rate of connection attempts?
Comprehensive and Detailed 150 to 250 words of Explanation From Palo Alto Networks Network Security Analyst Knowledge:
The Vulnerability Protection Profile is the primary mechanism for protecting against exploit attempts and protocol-specific attacks, including Brute Force. While many associate vulnerability protection with software patches, it also includes signatures designed to detect anomalies in connection patterns.
An analyst can configure 'threshold' based signatures within this profile. For example, a signature might trigger if more than 10 login attempts are made to a specific service within 60 seconds. By setting the action to block or reset, the analyst can automatically neutralize the brute force attempt before the attacker can guess a valid credential. This is a core objective for an analyst responsible for protecting high-value internal assets. Using vulnerability protection in this manner provides a reactive defense layer that complements strong password policies and multi-factor authentication.
Question 6 Domain 1 Object Configuration Creation and Application
Which type of object should be used to ensure that a Security policy rule automatically updates when a new virtual machine is spun up in a public cloud environment and assigned a specific tag?
Comprehensive and Detailed 150 to 250 words of Explanation From Palo Alto Networks Network Security Analyst Knowledge:
A Dynamic Address Group (DAG) is a powerful object type used to create agile security policies in environments where IP addresses change frequently, such as cloud-based infrastructures. Unlike a static group, where an analyst must manually add or remove IP addresses, a DAG uses tags as its membership criteria.
In this scenario, as a new virtual machine is deployed with a specific tag (e.g., 'Web-Server'), the firewall or Panorama learns the IP address associated with that tag via the XML API or a VM Information Source. The firewall then automatically populates that IP address into the DAG. Because the Security policy refers to the DAG rather than specific IPs, the rule immediately applies to the new VM without requiring a manual configuration change or a commit. This automation is a fundamental objective for analysts working in DevOps or cloud-native environments, as it ensures that security scales at the same pace as the infrastructure.
Question 7 Domain 3 Management and Operations
An organization uses several different web-conferencing tools (Zoom, Microsoft Teams, WebEx). The analyst wants to create a single security rule to allow all these tools without listing each App-ID individually. What should the analyst create?
Comprehensive and Detailed 150 to 250 words of Explanation From Palo Alto Networks Network Security Analyst Knowledge:
To manage a specific, known set of applications, an Application Group is the most appropriate object. The analyst manually adds the specific App-IDs (Zoom, Teams, etc.) to the group and then uses that group object in the 'Application' column of a security rule.
This is distinct from an Application Filter (Option A), which dynamically groups applications based on shared characteristics like 'Category: collaboration'. While a filter is more automated, an Application Group provides the analyst with explicit control over which 'sanctioned' apps are allowed. Using groups simplifies the rulebase, making it easier to read and audit. If the company decides to switch conferencing providers, the analyst only needs to update the single group object, and the change will automatically apply to all security rules referencing that group.
What the Palo Alto Networks NetSec-Analyst Exam Covers
Exam domains verified against the Official Palo Alto Networks NetSec-Analyst exam guide, last checked November 2026.
Domain 1 Object Configuration Creation and Application
30%Create and apply security profiles, decryption profiles, external dynamic lists, and custom objects like URL categories and signatures. Configure Log Forwarding, data security, IoT security, DoS protection, and SD-WAN profiles to build a complete security infrastructure.
Domain 2 Policy Creation and Application
30%Create Security policies using App-ID, User-ID, and Content-ID to control application and user-based traffic. Build NAT, decryption, application override, and Policy-Based Forwarding policies alongside SD-WAN routing and SLA policies.
Domain 3 Management and Operations
26%Use Strata Cloud Manager for centralized management with folders, snippets, automations, and variables. Leverage Command Center, Activity Insights, and Policy Optimizer to improve posture, then use Log Viewer and Incidents pages to identify and remediate security issues.
Sample question from this domain above Q7
Domain 4 Troubleshooting
14%Troubleshoot configuration problems across both management and on-box options when policies do not work as expected. Diagnose runtime errors, commit and push failures, and device health issues to restore normal operations.
Sample question from this domain above Q1
NetSec-Analyst Exam FAQ
Common questions about the exam itself
What prior experience do I need before taking the NetSec-Analyst exam?
How does NetSec-Analyst fit into the Palo Alto Networks certification track?
How long should I prepare for the NetSec-Analyst exam?
Which objective area of NetSec-Analyst do candidates find most difficult?
What happens if I fail the NetSec-Analyst exam and want to retake it?
What does the NetSec-Analyst exam day actually involve?
How long does the NetSec-Analyst certification stay valid?
What job role does NetSec-Analyst certification prepare me for?
Is the NetSec-Analyst exam hard and who should take it?
How many questions are on the NetSec-Analyst exam and what types are they?
Other Palo Alto Networks Exams
Free practice questions for more Palo Alto Networks certification exams