
Versa Networks VNX301 Practice Exam Questions & Answers
Versa Networks VNX301 Exam Details
Key details for this exam, checked against the published exam outline
- Exam Code
- VNX301
- Full Name
- Versa Certified Administrator - SD-WAN Specialist
- Issuing Body
- Versa Networks
- Question Format (Our Bank)
- Multiple Choice
- Eligibility
- Versa Certified SD-WAN Associate (VNX100)
- Full Question Set
- 60 questions Get All Questions
Free VNX301 Practice Questions
Each question shows the correct answer and an explanation of why it is right
Question 1 Domain 3 SD-WAN network topologies and routing concepts
You are troubleshooting a branch that cannot form SD-WAN overlay tunnels. The branch has WAN interfaces up, but you suspect remote endpoint objects were not learned. Which VSM command should you use to verify whether remote site objects were learned from BGP or from configuration?
The correct answer is A. Versa data-path troubleshooting documentation gives a specific VSM control-plane workflow for checking SD-WAN tunnel objects. After connecting to the VSM daemon, administrators can use show vsm p2mp local-tunnel-sites 0 to inspect local site objects. To check whether remote site objects were learned from BGP or from configuration, Versa instructs administrators to issue show vsm p2mp tunnel-remote-endpoint tenant <tenant-id> on the VSM control plane.
This command is highly relevant when local WAN interfaces are operational, but overlay tunnel formation is incomplete. It shows remote endpoints such as Controllers, hubs, or branches, along with site type, site name, branch ID, tenant ID, remote WAN link information, and tunnel state-related fields.
show interfaces brief confirms interface state and IP addresses, but it does not show learned remote SD-WAN endpoint objects. CGNAT summary is unrelated to tunnel endpoint learning. System storage is useful for disk checks, but not for SD-WAN overlay endpoint troubleshooting.
Question 2 Domain 4 Versa SD-WAN services
Examine the CLI output in the exhibit.
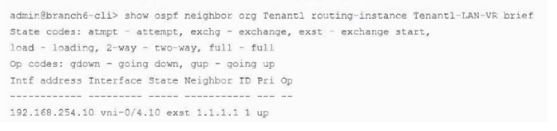
You are reviewing the OSPF adjacency on a VOS CPE, and the output is shown in the exhibit. In this scenario, what is the probable cause of the OSPF adjacency issue?
The correct answer is B. The exhibit shows the OSPF neighbor in the exst state, which means Exchange Start. Versa documentation lists the OSPF neighbor state codes and identifies exst as ''exchange start,'' followed by exchange, loading, and full. In normal OSPF adjacency formation, neighbors progress through initialization and two-way communication before they negotiate database exchange. If the neighbor becomes stuck in ExStart or Exchange, a common and highly probable cause is an MTU mismatch between the two OSPF peers. During database description packet negotiation, the peers must agree on parameters that allow LSDB exchange; an MTU mismatch can prevent the adjacency from advancing to Full.
Option A is less likely because an area mismatch usually prevents the neighbor relationship from forming correctly rather than leaving it stuck in ExStart. Option C is also incorrect because the neighbor has already progressed beyond early states, which indicates that bidirectional communication has occurred. Option D is not the best answer because dropping OSPF multicast 224.0.0.5 would typically prevent discovery or keep the adjacency in an earlier state, not specifically in ExStart. Therefore, the probable cause is an interface MTU mismatch.
Question 3 Domain 5 Versa security services
A customer is running VOS Release 22.1.3 on both the speed-test client and server. Which sequence is used by the Versa speed test to calculate bandwidth?
The correct answer is C. Versa documentation states that for Releases 22.1.3 and later, the speed test factors in network latency to derive results. In these releases, the speed test is performed in three stages: a ping test, an upload test, and a download test. The ping test calculates link latency, and the speed test uses that latency data while performing the upload and download portions.
The same documentation notes that the speed test can measure bandwidth speeds up to 1 Gbps, with actual measurement depending on factors such as in-path shapers and latency. It also states that the test may use up to 45 MB of data per upload or download in the best case and 90 MB for a complete test.
Older releases behave differently. For Releases 21.2 and earlier, the speed test is performed in two stages: upload and download. Therefore, because the question specifically states Release 22.1.3 on both client and server, the correct sequence is ping, upload, and download.
Get the complete VNX301 question set
$20$40
Question 4 Domain 5 Versa security services
A branch using DIA with CGNAT reports that new internet sessions intermittently fail. CGNAT pool counters show increasing out-of-ports errors, while out-of-address errors remain zero. What is the most likely problem?
The correct answer is A. Versa CGNAT troubleshooting documentation includes per-pool and resource counters that show allocation behavior and failures. The counters include values such as bindings allocated, bindings freed, allocation failures, out-of-address errors, and out-of-ports errors. It also shows that CGNAT source-port resources are divided and distributed to worker threads by Versa RFD/RFM, and that allocated source-port ranges can be viewed using show rfm table src-port allocated.
If out-of-ports errors increase while out-of-address errors remain zero, the pool still has usable translated IP addresses, but the available port resource for NAT bindings is exhausted. This commonly occurs when too many concurrent sessions share a limited public IP or source-port range. The corrective action would be to expand the NAT resource, add more public translated IPs, adjust port allocation, or reduce excessive session usage.
A missing NAT IP pool would more likely produce out-of-address problems. A wrong zone match might prevent translation entirely, and OSPF in the LAN VR is unrelated to CGNAT port-resource exhaustion.
Question 5 Domain 7 SD-WAN infrastructure administration
You are onboarding a branch with one WAN and one LAN interface. After a successful branch activation, the branch is not able to reach the Versa Controller. You realize that the WAN gateway IP address originally entered under the Device Bind Data menu in Versa Director is incorrect. Which action will you perform to solve the problem?
The correct action is to update the WAN gateway IP address in Device Bind Data and onboard the branch appliance again. Device Bind Data supplies site-specific values, such as WAN interface addressing and gateway information, that are merged with the workflow and template configuration during onboarding. If the wrong WAN gateway is entered, the branch may activate successfully from a workflow perspective, but the resulting WAN routing configuration is incorrect. As a result, the branch cannot establish proper transport reachability to the Controller. Versa troubleshooting documentation explains that, after establishing transport connectivity from a branch to a Controller, at least one WAN interface must be available, and the branch then establishes IKE-based IPsec connectivity to the Controller. If that IKE/IPsec connectivity fails, the Controller-facing ptvi interface remains down.
Changing the configuration only from the Appliance context is not the best answer because the incorrect value originated in the bind-data source used for provisioning. Modifying it manually from the branch CLI is also not recommended because the device is managed by Versa Director and template-driven configuration. Resetting the device does not automatically discover or ''ping'' the correct gateway. The correct remediation is to fix the bind data and repeat onboarding so the branch receives the correct generated configuration.
Question 6 Domain 7 SD-WAN infrastructure administration
A customer has purchased 10 Versa SD-WAN licenses. In this scenario, which statement is correct?
The correct answer is C. In Versa Secure SD-WAN, licensing and device management are centralized through Versa Director, not directly through the Controller. During zero-touch provisioning and staging, the branch device is brought under centralized management, and Director pushes the required staging and operational configuration. Versa staging documentation explains that during Stage 2 and Stage 3, Versa Director pushes configuration to the branch device, and after Stage 3 the branch becomes fully operational as part of the customer SD-WAN network.
Versa monitoring documentation also shows that the Director node provides license visibility, specifically stating that the Director monitoring view includes a License pane that displays information about the licenses installed on the VOS devices managed by the Director node. This confirms that license administration is handled from Director, not from the Controller. The Controller is responsible for SD-WAN control-plane functions and tunnel connectivity, but it is not the primary system for managing customer license subscriptions.
Option A is incomplete because the practical operational model is not simply receiving individual soft licenses. Option B incorrectly implies licenses are preloaded on physical CPEs as the key licensing method. Option D is incorrect because ZTP management and license subscription handling are not performed by the Controller.
Question 7 Domain 6 Configuration and provisioning
What are two features of the Stateful Firewall service in the Versa Operating System? (Choose two.)
The correct answers are A and D. Versa stateful firewall service includes classic firewall functions that track sessions and enforce traffic policy, and it can work with DoS policy enforcement. Versa's CLI guide includes Configuring DoS policies under the security configuration area, where DoS rules can match on source, destination, services, applications, URL category, IP version, DSCP, TTL, EtherType, and other packet or session attributes, and can then apply aggregate or classified DoS profiles. This validates DoS protection as a stateful firewall/security service capability.
Application-Level Gateways, or ALGs, are also associated with stateful firewall/NAT behavior because they inspect and assist protocol handling for applications that embed addressing or dynamic port information inside the payload or control channel. This is part of traditional stateful firewall service behavior rather than UTM content inspection.
What the Versa Networks VNX301 Exam Covers
Exam domains verified against the Official Versa Networks VNX301 exam guide, last checked November 2026.
Domain 1 Underlay/Overlay technologies
Covers the physical and logical network layers that form the foundation of SD-WAN, including transport technologies like MPLS, broadband, and LTE. Explains how overlay tunnels such as IPsec and GRE are built on top of underlay networks to create virtual connectivity between sites.
Domain 2 Versa Secure SD-WAN infrastructure
Focuses on the core components of Versa's SD-WAN architecture, including the Director, Analytics, and Controller nodes. Covers how the control plane, data plane, and management plane are structured and interact within the Versa platform.
Domain 3 SD-WAN network topologies and routing concepts
Explores common SD-WAN deployment topologies such as hub-and-spoke, full mesh, and partial mesh designs. Covers routing protocols and path selection mechanisms used within SD-WAN environments, including BGP and OSPF integration.
Sample question from this domain above Q1
Domain 4 Versa SD-WAN services
Covers the core SD-WAN service features offered by Versa, including application identification, traffic steering, and SLA-based policies. Includes Quality of Service, WAN optimization, and link bonding capabilities for improving application performance.
Sample question from this domain above Q2
Domain 5 Versa security services
Covers the integrated security stack within Versa SD-WAN, including Next-Generation Firewall, IPS, and URL filtering. Addresses secure access capabilities such as DNS security, SSL inspection, and application-layer threat prevention.
Domain 6 Configuration and provisioning
Covers the methods used to configure Versa SD-WAN components, including template-based provisioning through the Director GUI and CLI. Addresses zero-touch provisioning workflows that enable automated, rapid deployment of branch devices at scale.
Sample question from this domain above Q7
Domain 7 SD-WAN infrastructure administration
Covers day-to-day operational tasks including monitoring, troubleshooting, and maintaining the health of the SD-WAN environment. Addresses the use of Versa Analytics for visibility into traffic flows, application performance, and security events.
VNX301 Exam FAQ
Common questions about the exam itself
What background do I need before attempting VNX301?
How is VNX301 different from VNX100?
What does the VNX301 exam cover?
Which topic area do most candidates find most challenging on VNX301?
How long should I prepare for VNX301?
What happens on exam day for VNX301?
Can I retake VNX301 if I don't pass?
How long is the VNX301 certification valid once I pass?
What job roles is VNX301 designed for?
What comes after VNX301 in the Versa certification track?
Other Versa Networks Exams
Free practice questions for more Versa Networks certification exams