- Home
- Trend
- Deep-Security-Professional Exam Questions
Trend Deep-Security-Professional Practice Exam Questions & Answers
7 Free Questions
· Last reviewed: October 22, 2026
· Prepared & Reviewed by the ValidExamDumps Editorial Team
Exam Facts
Trend Deep-Security-Professional Exam Details
Key details for this exam, checked against the published exam outline
80
Practice Questions (Our Bank)
- Exam Code
- Deep-Security-Professional
- Full Name
- Trend Micro Certified Professional for Deep Security Exam
- Issuing Body
- Trend Micro
- Question Format (Our Bank)
- Multiple Choice
Practice Questions
Free Deep-Security-Professional Practice Questions
Each question shows the correct answer and an explanation of why it is right
VA
ValidExamDumps Editorial Team
Every question and its answer is checked by our Deep-Security-Professional exam
preparation team, who also write the explanation shown with each one.
How we research and review these pages
Which of the following file types would not be evaluated by the Application Control Protection Module?
Correct Answer:
D
Explanation
The Application Control Protection Module monitors and restricts execution of programs based on file type and content. Document files like .docx are not executable programs, so they fall outside the module's scope. The other options (executable files, DLLs, and scripts) are all evaluated because they can be executed and therefore present a security risk that the module is designed to control.
Which of the following operations makes use of the Intrusion Prevention Protection Module?
Correct Answer:
D
Explanation
Web Reputation uses credibility scores from 0 to 100, where higher scores mean safer sites. When the Security Level is set to High, the threshold is typically around 80. A credibility score of 78 falls below this threshold, so the Deep Security Agent blocks the connection and displays an error page in the browser instead of allowing access to the potentially unsafe website.
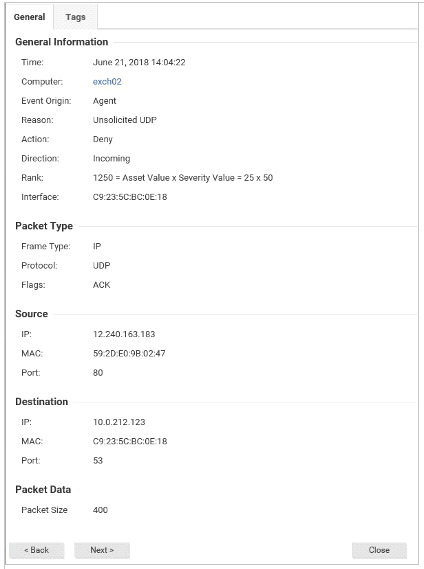
The details for an event are displayed in the exhibit. Based on these details, which Protection Module generated the event?
Correct Answer:
B
Explanation
Deep Security Manager stores database credentials in the dsm.properties configuration file rather than in environment variables, separate files, or the system registry. This file contains essential configuration settings that the Manager needs to authenticate with the database during startup and ongoing operations. Storing credentials here allows the Manager to maintain persistent database connectivity.
How is caching used by the Web Reputation Protection Module?
Correct Answer:
A
Explanation
IntelliScan is a smart file identification technology that looks at file headers and content to determine the actual file type, regardless of the file extension. This allows Deep Security to correctly identify which files need to be scanned for malware. Without IntelliScan, malware could hide by using incorrect file extensions, and legitimate files might be scanned unnecessarily, wasting resources.
New servers are added to the Computers list in Deep Security Manager Web config by running a Discover operation. What behavior can you expect for newly discovered computers?
Correct Answer:
B
Explanation
When running a Discovery operation with Automatically Resolve IPs to hostnames enabled, it is possible that the discovery operation will find hostnames where Deep Security Manager can not.
Discovery is able to fall back to using a WINS query or NetBIOS broadcast to resolve the
hostname in addition to DNS. Deep Security Manager only supports hostname lookup via DNS.
* Computers identified with this method can be automatically assigned a group, but not a policy.
* Agent software found on those computers will NOT be automatically activated.
* If a computer is listed through other detection methods, it will NOT be listed in the results of this search.
Study Guide - pages (345, 80)
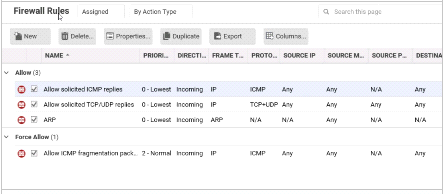
While viewing the details of the Firewall Protection Module, as displayed in the exhibit, you note that a few rules have already been assigned. You try to disable these rules, but they can not be unassigned. Why can the displayed rules not be unassigned?
Correct Answer:
B
Explanation
Deep Security Relays act as intermediaries between agents and the manager in environments where direct communication is difficult or inefficient. Agents connect to relays to receive security updates, policy changes, and other critical information. Relays then communicate with the Deep Security Manager, reducing the load on the manager and improving scalability in large deployments with many agents.
Which of the following statements is true regarding Event Tagging?
Correct Answer:
C
Explanation
Recommendation scans identify vulnerabilities by checking files against the Intrusion Prevention rule database. New vulnerabilities are discovered regularly and new rules are added to Deep Security. By enabling ongoing scans to run on a regular schedule, the system will continuously check for new vulnerabilities and apply newly available Intrusion Prevention rules as they become available from Trend Micro.
Full Access
Get the complete Deep-Security-Professional question set
- 80 questions covering all exam domains
- Correct answers with explanations, like the free questions above
- PDF and online practice test
- 90 days of free updates
Study Guide
What the Trend Deep-Security-Professional Exam Covers
11 domains from the Trend Deep-Security-Professional exam outline, with approximate weightings. Every sample question above is tagged
with the domain it comes from
Domain 1: Product Overview
Understand the core concepts of Trend Micro Deep Security, its protection modules, and the key components that form the foundation of the platform. This objective area establishes the baseline knowledge needed for all deployment and configuration tasks.
Sample questions from this domain above:
Q1Q4
Domain 2: Deep Security Manager
Learn the requirements, components, and installation processes for Deep Security Manager. This section covers how the Manager centralizes policy administration and orchestrates protection across your environment.
Domain 3: Deep Security Agent
Master the architecture, deployment, activation, and ongoing management of Deep Security Agents. Agents deliver protection to individual servers and virtual machines and report back to the Manager.
Sample question from this domain above:
Q6
Domain 4: Protecting Servers from Vulnerabilities
Study virtual patching, protocol controls, intrusion prevention, and web application protection. This area covers how Deep Security shields servers from known and zero-day vulnerabilities without waiting for vendor patches.
Sample questions from this domain above:
Q2Q7
Domain 5: Enabling Integrity Monitoring
Learn how to run recommendation scans, establish baselines, detect unauthorized changes to critical files and registry, and use event tagging. Integrity Monitoring alerts you when systems deviate from their known-good state.
Domain 6: Protecting Servers from Vulnerabilities
Study virtual patching, protocol controls, intrusion prevention, and web application protection. This area covers how Deep Security shields servers from known and zero-day vulnerabilities without waiting for vendor patches.
Domain 7: Enabling Integrity Monitoring
Learn how to run recommendation scans, establish baselines, detect unauthorized changes to critical files and registry, and use event tagging. Integrity Monitoring alerts you when systems deviate from their known-good state.
Domain 8: Activating and Managing Multiple Tenants
Understand how to enable multi-tenancy, create and manage isolated tenants, activate Deep Security Agents within tenant boundaries, and monitor cross-tenant operations. This objective covers the architecture and controls for shared or service provider deployments.
Sample question from this domain above:
Q3
Domain 9: Detecting Emerging Malware Through Connected Threat Defens
Study the requirements for Connected Threat Defense, how it integrates with Trend Micro Deep Discovery Analyzer and Control Manager, and how threat intelligence flows through your infrastructure. This area addresses advanced threat detection and response.
Domain 10: Detecting Emerging Malware Through Connected Threat Defense
Study the requirements for Connected Threat Defense, how it integrates with Trend Micro Deep Discovery Analyzer and Control Manager, and how threat intelligence flows through your infrastructure. This area addresses advanced threat detection and response.
Domain 11: Protecting Virtual Machines using the Deep Security Virtual Appliance
Learn agentless protection strategies and how to deploy Deep Security as a Virtual Appliance on VMware ESXi. This objective covers scenarios where installing agents on every VM is not feasible.
Sample question from this domain above:
Q5
FAQ
Deep-Security-Professional Exam FAQ
Common questions about the exam itself
What does the Deep-Security-Professional exam test and who should take it?
The exam validates your ability to deploy, configure, and manage Trend Micro Deep Security across enterprise environments. It is aimed at IT security professionals and system administrators responsible for protecting physical and virtual server infrastructure.
What background or hands-on experience should I have before taking Deep-Security-Professional?
You should have practical experience with Trend Micro Deep Security solutions and a solid understanding of network security concepts. While there are no formal prerequisites, familiarity with virtual machine environments and server security practices is strongly recommended.
Which objective areas in Deep-Security-Professional are typically the hardest?
Candidates often struggle most with multi-tenant activation due to role and isolation complexities, virtual appliance placement in vSphere environments, and failover or high availability scenarios. Tracing data paths and understanding component interaction in production layouts helps.
How long does it typically take to prepare for Deep-Security-Professional?
Most candidates benefit from three to six months of study, depending on existing Deep Security experience. Those with hands-on lab access and exposure to the product typically prepare faster than those relying only on documentation.
What is the exam format for Deep-Security-Professional?
The exam combines multiple-choice questions with scenario-based items. Questions progress in difficulty and require you to apply concepts to realistic situations such as policy design, agent deployment decisions, and troubleshooting production scenarios.
Can I retake Deep-Security-Professional if I don't pass on my first attempt?
Yes, you can retake the exam, but you should verify the current retake policy on the official Trend Micro certification website or with the exam delivery provider.
How long does the Deep-Security-Professional certification stay valid?
You should verify the validity period and renewal requirements on the official Trend Micro certification website, as this information is not consistently published across third-party sources.
What job roles does Deep-Security-Professional certification map to?
This certification is designed for security professionals, system administrators, and IT operations staff who manage Deep Security deployments in enterprise environments. It demonstrates expertise in endpoint protection and vulnerability management.
How does Deep-Security-Professional fit within the Trend Micro certification track?
Deep-Security-Professional covers foundational platform skills. Trend offers additional certifications such as Deep Security Advanced for more complex topics like policy management and system administration.
Where can I find official exam information and schedule Deep-Security-Professional?
Visit the official Trend Micro certification website or contact authorized exam delivery providers such as Pearson VUE to access official exam details, pricing, scheduling, and policies.

