Key details for this exam, checked against the published exam outline
Each question shows the correct answer and an explanation of why it is right
What is the main change to the IT operating model that MuleSoft recommends to organizations to improve innovation and clock speed?
Correct Answe r: Drive consumption as much as production of assets; this enables developers to discover and reuse assets from other projects and encourages standardization
*****************************************
>> The main motto of the new IT Operating Model that MuleSoft recommends and made popular is to change the way that they are delivered from a production model to a production + consumption model, which is done through an API strategy called API-led connectivity.
>> The assets built should also be discoverable and self-serveable for reusablity across LOBs and organization.
>> MuleSoft's IT operating model does not talk about SDLC model (Agile/ Lean etc) or MDM at all. So, options suggesting these are not valid.
https://blogs.mulesoft.com/biz/connectivity/what-is-a-center-for-enablement-c4e/
https://www.mulesoft.com/resources/api/secret-to-managing-it-projects
A company deploys Mule applications with default configurations through Runtime Manager to customer-hosted Mule runtimes. Each Mule application is an API
implementation that exposes RESTful interfaces to API clients. The Mule runtimes are managed by the MuleSoft-hosted control plane. The payload is never used by any Logger
components.
When an API client sends an HTTP request to a customer-hosted Mule application, which metadata or data (payload) is pushed to the MuleSoft-hosted control plane?
Understanding the Data Flow Between Mule Runtimes and Control Plane:
When Mule applications are deployed on customer-hosted Mule runtimes, the MuleSoft-hosted control plane (Anypoint Platform) can monitor and manage these applications. However, due to data privacy and security, the control plane only collects specific types of information.
Typically, only metadata about the request and response (such as headers, status codes, and timestamps) is sent to the MuleSoft-hosted control plane. The actual payload data is not transmitted unless explicitly configured, ensuring that sensitive data remains within the customer's network.
Evaluating the Options:
Option A (Only the data): This is incorrect because the payload data itself is not automatically sent to the control plane in default configurations.
Option B (No data): This is incorrect as well; while the payload is not sent, metadata is still collected and sent to the control plane.
Option C (The data and metadata): This option is incorrect because data (payload) is not transmitted to the control plane by default.
Option D (Correct Answer): Only the metadata is sent to the MuleSoft-hosted control plane by default, aligning with MuleSoft's design to prioritize security and data privacy for customer-hosted runtimes.
Conclusion:
Option D is the correct answer, as by default, only metadata is sent to the MuleSoft-hosted control plane, and not the payload. This configuration is designed to protect sensitive data from being exposed outside the customer's hosted environment.
For more details, refer to MuleSoft's documentation on telemetry data collected in customer-hosted Mule runtimes and the MuleSoft control plane.
What API policy would be LEAST LIKELY used when designing an Experience API that is intended to work with a consumer mobile phone or tablet application?
Correct Answe r: IP whitelist
*****************************************
>> OAuth 2.0 access token and Client ID enforcement policies are VERY common to apply on Experience APIs as API consumers need to register and access the APIs using one of these mechanisms
>> JSON threat protection is also VERY common policy to apply on Experience APIs to prevent bad or suspicious payloads hitting the API implementations.
>> IP whitelisting policy is usually very common in Process and System APIs to only whitelist the IP range inside the local VPC. But also applied occassionally on some experience APIs where the End User/ API Consumers are FIXED.
>> When we know the API consumers upfront who are going to access certain Experience APIs, then we can request for static IPs from such consumers and whitelist them to prevent anyone else hitting the API.
However, the experience API given in the question/ scenario is intended to work with a consumer mobile phone or tablet application. Which means, there is no way we can know all possible IPs that are to be whitelisted as mobile phones and tablets can so many in number and any device in the city/state/country/globe.
So, It is very LEAST LIKELY to apply IP Whitelisting on such Experience APIs whose consumers are typically Mobile Phones or Tablets.
Refer to the exhibit.
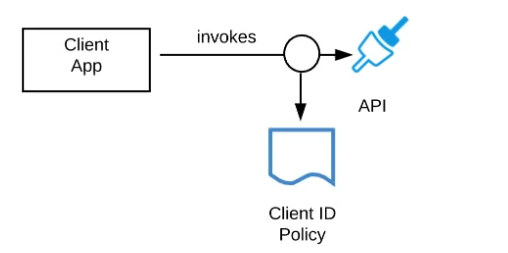
A developer is building a client application to invoke an API deployed to the STAGING environment that is governed by a client ID enforcement policy.
What is required to successfully invoke the API?
Correct Answe r: The client ID and secret obtained from Anypoint Exchange for the API instance in the STAGING environment
*****************************************
>> We CANNOT use the client ID and secret of Anypoint Platform account or any individual environments for accessing the APIs
>> As the type of policy that is enforced on the API in question is 'Client ID Enforcment Policy', OAuth token based access won't work.
Right way to access the API is to use the client ID and secret obtained from Anypoint Exchange for the API instance in a particular environment we want to work on.
Managing API instance Contracts on API Manager
https://docs.mulesoft.com/api-manager/1.x/request-access-to-api-task
https://docs.mulesoft.com/exchange/to-request-access
https://docs.mulesoft.com/api-manager/2.x/policy-mule3-client-id-based-policies
A system API is deployed to a primary environment as well as to a disaster recovery (DR) environment, with different DNS names in each environment. A process API is a client to the system API and is being rate limited by the system API, with different limits in each of the environments. The system API's DR environment provides only 20% of the rate limiting offered by the primary environment. What is the best API fault-tolerant invocation strategy to reduce overall errors in the process API, given these conditions and constraints?
Correct Answe r: Invoke the system API deployed to the primary environment; add timeout and retry logic to the process API to avoid intermittent failures; if it still fails, invoke the system API deployed to the DR environment
*****************************************
There is one important consideration to be noted in the question which is - System API in DR environment provides only 20% of the rate limiting offered by the primary environment. So, comparitively, very less calls will be allowed into the DR environment API opposed to its primary environment. With this in mind, lets analyse what is the right and best fault-tolerant invocation strategy.
1. Invoking both the system APIs in parallel is definitely NOT a feasible approach because of the 20% limitation we have on DR environment. Calling in parallel every time would easily and quickly exhaust the rate limits on DR environment and may not give chance to genuine intermittent error scenarios to let in during the time of need.
2. Another option given is suggesting to add timeout and retry logic to process API while invoking primary environment's system API. This is good so far. However, when all retries failed, the option is suggesting to invoke the copy of process API on DR environment which is not right or recommended. Only system API is the one to be considered for fallback and not the whole process API. Process APIs usually have lot of heavy orchestration calling many other APIs which we do not want to repeat again by calling DR's process API. So this option is NOT right.
3. One more option given is suggesting to add the retry (no timeout) logic to process API to directly retry on DR environment's system API instead of retrying the primary environment system API first. This is not at all a proper fallback. A proper fallback should occur only after all retries are performed and exhausted on Primary environment first. But here, the option is suggesting to directly retry fallback API on first failure itself without trying main API. So, this option is NOT right too.
This leaves us one option which is right and best fit.
- Invoke the system API deployed to the primary environment
- Add Timeout and Retry logic on it in process API
- If it fails even after all retries, then invoke the system API deployed to the DR environment.
The asset version 2.0.0 of the Order API is successfully published in Exchange and configured in API Manager with the Autodiscovery API ID correctly linked to the
API implementation, A new GET method is added to the existing API specification, and after updates, the asset version of the Order API is 2.0.1,
What happens to the Autodiscovery API ID when the new asset version is updated in API Manager?
Understanding API Autodiscovery in MuleSoft:
API Autodiscovery links an API implementation in Anypoint Platform with its configuration in API Manager. This is controlled by the API ID which is set in the API Autodiscovery element in the Mule application.
The API ID remains consistent across minor updates to the API asset version in Exchange (e.g., from 2.0.0 to 2.0.1) as long as it is the same API.
Effect of Asset Version Update on API Autodiscovery:
When the asset version is updated (e.g., from 2.0.0 to 2.0.1), the API ID remains the same. Therefore, no changes are needed in the Autodiscovery configuration within the Mule application. The Autodiscovery will continue to link the API implementation to the latest version in API Manager.
Evaluating the Options:
Option A: Incorrect, as the API ID does not automatically change with minor asset version updates.
Option B: Incorrect, as the API ID remains the same, so no update is needed in the API implementation.
Option C (Correct Answer): The API ID does not change, so no changes are necessary in the API implementation for the new asset version.
Option D: Incorrect, as there is no need to update the API implementation in the Autodiscovery global element for minor version changes.
Conclusion:
Option C is the correct answer, as the API ID remains unchanged with minor version updates, and no changes are needed in the API Autodiscovery configuration.
Refer to MuleSoft documentation on API Autodiscovery and version management for more details.
Exam domains verified against: Official Salesforce MuleSoft-Platform-Architect-I exam guide, last checked October 2026.
Identify and differentiate between technologies for deploying API-led connectivity. Assign APIs to tiers according to ownership, change level, and functional focus.
Suggest how to establish a Center for Enablement and explain KPIs for measuring its success. Contrast Identity Management and Client Management choices.
Identify dependencies between an API, its specification, implementation, and clients. Explain creation and publication of reusable API-related assets.
Identify the right APIs to implement a business process and assign them to layers of API-led connectivity. Assign APIs based on change rate, ownership, and functional focus.
Make the right utilization choice of API instances and environments in API Manager. Choose the right API policy to support non-functional requirements and identify changes needed to API specifications.
Describe and utilize auto-discovery to link a web API implementation to an API instance managed with API Manager. Explain the needs of using an Anypoint Virtual Private Cloud.
Describe scenarios for which Object Store should be used with CloudHub. Choose CloudHub worker sizes and configurations as appropriate.
Sample question from this domain above: Q2
Design and differentiate between scenarios using Object Store or caching. Choose resilience strategies that help web API clients guard against failures.
Pinpoint the elements of Anypoint Platform that generate data for monitoring and alerting. Define the metrics collected for API invocations across all layers of API-led connectivity.
Sample question from this domain above: Q5
Common questions about the exam itself

