Key details for this exam, checked against the published exam outline
Each question shows the correct answer and an explanation of why it is right
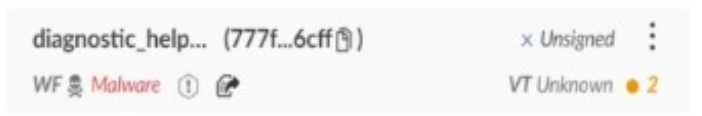
Based on the artifact details in the image below, what can an analyst infer from the hexagon-shaped object with the exclamation mark (!) at the center?
Comprehensive and Detailed Explanation From Exact Extract:
The correct answer is B -- The artifact verdict has changed from a previous state to 'Malware.'
The hexagon-shaped object with an exclamation mark in Cortex XSIAM artifact analysis indicates a change or escalation in verdict---typically from 'Unknown' or another previous state to 'Malware.' This symbol is a visual cue for analysts to pay attention to the updated status, as the system has reclassified the file/object to 'Malware' based on new intelligence or analysis.
''The exclamation mark in a hexagon is used to signal that the verdict of the artifact has changed, most commonly to indicate a new classification as 'Malware.'''
Document Reference: XSIAM Analyst ILT Lab Guide.pdf
Page: Page 37 (Threat Intel Management section, Artifact verdict/status changes)
An incident in Cortex XSIAM contains the following series of alerts:
10:24:17 AM - Informational Severity - XDR Analytics BIOC - Rare process execution in organization
10:24:18 AM - Low Severity - XDR BIOC - Suspicious AMSI DLL load location
10:24:20 AM - Medium Severity - XDR Agent - WildFire Malware
11:57:04 AM - High Severity - Correlation - Suspicious admin account creation
Which alert was responsible for the creation of the incident?
The correct answer is B - Rare process execution in organization.
In Cortex XSIAM, when an incident is created, the first alert generated within the incident's timeline is considered the initiating event or the trigger responsible for the creation of the incident. Based on the provided timestamps, the earliest alert generated was the 'Rare process execution in organization', at 10:24:17 AM. Subsequent alerts within the same causality chain or event flow would be added to this already-created incident.
Hence, the initiating alert is always the earliest alert chronologically within an incident's timeline.
'Incidents are created based on the earliest alert in the causality chain. Subsequent related alerts are grouped under the same incident.'
Document Reference: XSIAM Analyst ILT Lab Guide.pdf
Exact Page: Page 32 (Incident Handling and Response Section)
During an investigation of an alert with a completed playbook, it is determined that no indicators exist from the email "[email protected]" in the Key Assets & Artifacts tab of the parent incident. Which command will determine if Cortex XSIAM has been configured to extract indicators as expected?
The correct answer is C, the !checkIndicatorExtraction text='[email protected]' command.
This command specifically verifies if Cortex XSIAM has been correctly configured to extract indicators from given text. It ensures that the text provided ('[email protected]') would indeed be recognized and extracted as an indicator under the current configuration of Cortex XSIAM.
Other provided commands do not directly verify the indicator extraction configuration:
Option A: IcreateNewIndicator manually creates an indicator; it does not validate extraction capability.
Option B: !extractIndicators attempts extraction immediately but does not verify existing configuration explicitly.
Option D: Iemailvalue command is generally for creating or querying email indicators, not verifying extraction configuration.
Therefore, the explicit functionality for checking if indicator extraction is configured correctly within Cortex XSIAM is precisely covered by !checkIndicatorExtraction.
Reference Extract from Official Document:
'Verify if Cortex XSIAM is correctly configured to extract indicators using the command !checkIndicatorExtraction text=<value>.'
This exact description confirms that option C is the correct answer to validate the configuration explicitly.
Which configuration will ensure any alert involving a specific critical asset will always receive a score of 100?
The correct answer is D, a risk scoring policy for the critical asset.
In Cortex XSIAM, to consistently apply a high score (e.g., 100) to any alert involving a particular asset, analysts should define and apply a risk scoring policy. Such policies allow organizations to specifically customize and enforce a scoring framework to reflect the critical nature of certain assets, ensuring they are always prioritized during incident response activities.
Asset criticality alone (option A) doesn't automatically assign a static high score to every alert.
SmartScore (option B) is AI-driven and dynamic; it cannot guarantee a fixed, always-maximized score.
User scoring rules (option C) target user entities, not specifically the assets themselves.
'Risk scoring policies are explicitly defined to consistently assign specific scores to incidents or alerts involving critical assets, ensuring prioritized visibility in the incident queue.'
While investigating an incident on the Incident Overview page, an analyst notices that the playbook encountered an error. Upon playbook work plan review, it is determined that the error was caused by a timeout. However, the analyst does not have the necessary permissions to fix or create a new playbook.
Given the critical nature of the incident, what can the analyst do to ensure the playbook continues executing the remaining steps?
The correct answer is D -- Pause the step with the error, thus automatically triggering the execution of the remaining steps.
When a playbook encounters an error and the analyst does not have permissions to modify or recreate the playbook, the recommended action is to pause the step with the error. This will skip the problematic step and allow the remaining steps of the playbook to execute, ensuring the investigation or response continues.
'Pausing a failed step in the playbook work plan allows the remaining steps to continue executing, useful when immediate playbook edits are not possible due to permission restrictions.'
Document Reference: XSIAM Analyst ILT Lab Guide.pdf
Page: Page 39 (Automation section)
50 questions covering all exam domains, starting from $20
Exam domains verified against: Official Palo Alto Networks XSIAM-Analyst exam guide, last checked September 2026.
Identify alert types and configure prioritization using incident scoring, alert starring, and featured fields. Understand alert sources including correlations, XDR agents, and indicators of compromise.
Sample question from this domain above: Q3
Review alert evidence using forensics, ITDR, causality chains, and timelines. Investigate security events, apply automation actions, and hunt IOCs while interpreting incident context data.
Use playbooks for automated incident response. Understand task types, sub-playbooks, error handling, and the playground environment for testing automation workflows.
Sample question from this domain above: Q4
Work with Cortex Data Models (XDMs) and write XQL queries. Understand XQL syntax, schema, data sources, Query Library, XQL Helper, and scheduled queries for event investigation.
Sample question from this domain above: Q5
Validate endpoint profiles, policies, and agent operational status. Respond to endpoint alerts using live terminal, isolation, malware scan, and file retrieval capabilities.
Import and manage indicators, validate artifacts and verdicts, and create prevention and detection rules. Use attack surface threat response to identify and remediate emerging threats.
Common questions about the exam itself

