Key details for this exam, checked against the published exam outline
Each question shows the correct answer and an explanation of why it is right
You host your application on a stack in Oracle Cloud Infrastructure (OCI) Resource Manager. Because of recent growth in your user base, you decide to add a CIDR block to your VCN, add a subnet, and provision a compute instance in it.
Which statement is true?
Oracle Cloud Infrastructure (OCI) Resource Manager uses Terraform to manage infrastructure resources. If you need to add new resources (e.g., a new CIDR block, subnet, and compute instance), you can simply make the necessary changes to the Terraform code defining the stack.
After modifying the Terraform configuration to include the new resources, you can run an Apply job in Resource Manager. The Apply job will provision the new resources in your OCI environment according to the updated Terraform code.
Your team is responsible for deploying a new version of an application that is being used by your company's finance department. The application is critical to the department's operations, and any downtime could have serious consequences.
What is the recommended approach in OCI for creating environments for this scenario?
For critical applications, such as the one used by the finance department, a blue-green deployment strategy is recommended to ensure minimal or zero downtime during upgrades. The blue-green strategy involves running two separate environments: blue (current version) and green (new version).
A software development team is working on a prototype using Node.js and MongoDB as their programming language and database, respectively. They need to develop and test isolated web applications or RESTful APIs. They are looking for a simple, quick, and secure way to run containers without managing any servers.
Which OCI service is best suited for this use case?
OCI Container Instances provide a serverless way to run containers in Oracle Cloud Infrastructure (OCI). They allow you to run containers without having to manage any underlying servers or clusters. This is ideal for development teams that need a simple, quick, and secure way to develop and test isolated web applications or RESTful APIs.
A fully qualified path to a particular image in an OCIR repository is given as iad.ocir.io/ansh81vru1zp/project01/acme-web-app:version2.0.test.
Identify the two options with correct terms and their associated values. (Choose two.)
ansh81vru1zp is the <tenancy-namespace>. In Oracle Cloud Infrastructure Registry (OCIR), the tenancy namespace uniquely identifies the tenancy and is used as part of the image path.
iad is the <region-key>. The region key is the shorthand identifier for the OCI region (iad represents Ashburn region), and it is used in the fully qualified path for images stored in the Oracle Cloud Infrastructure Registry (OCIR).
Which of the following statement is INCORRECT with respect to a Dockerfile?
The WORKDIR instruction sets the working directory for all subsequent RUN, CMD, ENTRYPOINT, COPY, and ADD instructions in the Dockerfile. This means that after specifying WORKDIR, all these instructions will use the specified directory as their current working directory.
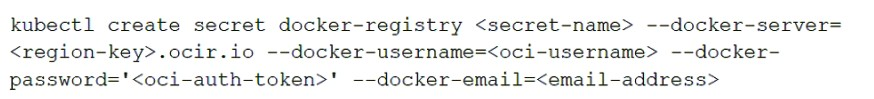
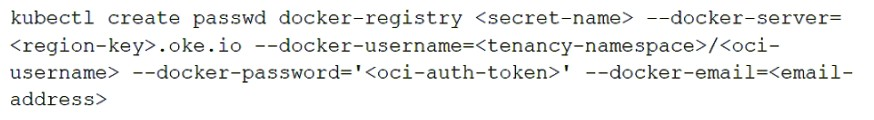
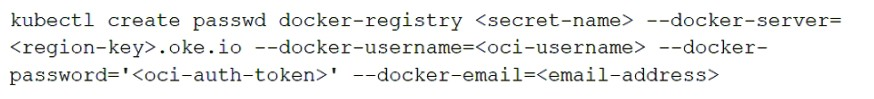
Which command creates the docker registry secret required in the application manifests for OKE to pull images from Oracle Cloud Infrastructure Registry?
A)
B)
C)
D)
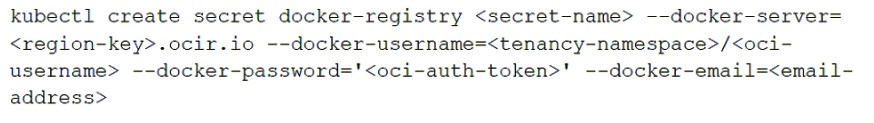
To create a Docker registry secret to pull images from the Oracle Cloud Infrastructure Registry (OCIR), you need to specify the correct parameters such as the region key, namespace, OCI username, and OCI authentication token.
Chosen command is correct because:
The kubectl create secret docker-registry command creates a Docker registry secret.
The --docker-server=<region-key>.ocir.io specifies the correct endpoint for OCIR.
The --docker-username=<tenancy-namespace>/<oci-username> provides both the tenancy namespace and the OCI username, which is the required format for authentication with OCIR.
The --docker-password='<oci-auth-token>' specifies the OCI auth token, which acts as a password for authentication.
The --docker-email=<email-address> is also included.
The other commands have errors, such as missing tenancy namespace or using incorrect flags (passwd instead of secret).
As a DevOps engineer at XYZ Corp, you have been assigned the task of setting up a new OKE (Oracle Kubernetes Engine) cluster to manage the organization's Kubernetes applications hosted on Oracle Cloud Infrastructure (OCI). Your goal is to ensure a smooth and efficient process while preparing for the cluster creation.
Which of the following statements is false regarding the preparation process for setting up a new OKE cluster?
This statement is false because Container Engine for Kubernetes (OKE) can utilize existing network resources such as Virtual Cloud Networks (VCNs), subnets, security lists, and route tables for the creation of a new cluster. You can either use pre-existing network resources or let OKE create new network resources automatically.
Exam domains verified against: Official Oracle 1Z0-1109-25 exam guide, last checked October 2026.
Demonstrate proficiency in DevOps practices, tools, and solutions through real-world problem-solving. Explain and implement microservices architecture, identify containerization needs, and create Docker containers. Create and manage Oracle Cloud Infrastructure Registry OCIR and Container Instances.
Deploy infrastructure using Infrastructure as Code and Terraform on OCI. Streamline infrastructure deployment and configuration with OCI Resource Manager to automate and manage cloud resource provisioning.
Sample question from this domain above: Q1
Automate the software development life cycle using OCI DevOps Service. Configure source code repositories, create artifacts for automated deployment, and evaluate and configure build and deployment pipelines. Create and configure deployment strategies.
Review Container Engine for Kubernetes principles and create, manage, and optimize Kubernetes clusters in OCI. Understand cluster types, cluster access, deployments, networking, storage, and observability. Perform scaling, cluster upgrades, admission controllers, and execute applications on specialized nodes.
Configure security using DevSecOps best practices in OCI. Create and manage encryption keys and secrets in OCI Vault. Evaluate and configure security within OCI DevOps CI/CD pipelines and for container images used in OCI.
Explain the concepts of DevOps measurement and monitoring. Monitor metrics using OCI Monitoring Service and analyze and manage logs with OCI Logging Service for distributed application health and performance.
Common questions about the exam itself

