
Nokia 4A0-D03 Practice Exam Questions & Answers
Nokia 4A0-D03 Exam Details
Key details for this exam, checked against the published exam outline
- Exam Code
- 4A0-D03
- Full Name
- Nokia SR Linux EVPN and Data Center Interconnect
- Issuing Body
- Nokia
- Question Format (Our Bank)
- Multiple Choice
- Delivery
- Online proctored or at a Pearson VUE test centre
- Eligibility
- No mandatory prerequisites
- Full Question Set
- 56 questions Get All Questions
Free 4A0-D03 Practice Questions
Each question shows the correct answer and an explanation of why it is right
Question 1 Domain 1 EVPN on SR Linux
Consider the exhibit.

Leaf-1 has received an ARP request from host-1 for host-2. Leaf-1 has added host-1's MAC address in its MAC table and host-1's MAC/IP addresses in its proxy-ARP table.
Which of the following steps is FALSE?
Comprehensive and Detailed 150 to 250 words of Explanation From [SR Linux EVPN and Data Center Interconnect/Course Guide/topics]:
When Leaf-1 receives an ARP request from Host-1, it learns the source MAC address in the local MAC table and learns the source IP/MAC binding in the proxy ARP table. For EVPN distribution, the relevant control-plane advertisement is an EVPN route type 2 MAC/IP advertisement containing Host-1's MAC and the actual host IP address, 192.168.100.1. This allows remote PEs to populate their EVPN-derived forwarding and proxy ARP state with the correct endpoint binding. Option A is false because advertising the host MAC with the IP address set to 0.0.0.0 does not represent the learned MAC/IP binding required for proxy ARP synchronization. A MAC-only RT-2 advertisement may exist in EVPN contexts, but the question specifically states that Leaf-1 has learned the MAC/IP binding through ARP and is distributing that information. Therefore, the valid advertisement must include the real host IP address. Remote PEs use the MAC/IP route to learn the endpoint, not an all-zero IP placeholder for this proxy ARP learning event. Reference: EVPN RT-2 MAC/IP advertisement, proxy ARP table population, endpoint synchronization.
Question 2 Domain 4 L2 and L3 EVPN Multi-homing
Which of the following statements about the decoupled gateway-based data center interconnect solution is FALSE?
Comprehensive and Detailed 150 to 250 words of Explanation From [SR Linux EVPN and Data Center Interconnect/Course Guide/topics]:
In a decoupled gateway-based DCI design, the data center border leaf and the WAN PE are separate devices. Traffic between them can be identified using VLAN tags, allowing different data center EVPN services to be mapped to corresponding WAN VPN services. This architecture provides a clean operational boundary: the border leaf remains aligned with the data center EVPN/VXLAN fabric, while the WAN PE handles WAN VPN transport, QoS, security policy, and service interconnection. The separation gives a strong demarcation point for troubleshooting and administrative control. Option D is false because the WAN PE does not maintain an MP-BGP EVPN peering session with the data center route reflector. In the decoupled model, the route reflector remains part of the data center EVPN control plane, while the WAN PE exchanges routing or service information with the border leaf through the local handoff model. Direct WAN PE-to-data-center-RR peering would blur the separation that defines the decoupled design and would make the WAN PE part of the data center EVPN overlay control plane, which is not the intended architecture. Reference: decoupled gateway DCI, VLAN handoff, WAN VPN mapping, security/QoS demarcation, route-reflector separation.
Question 3 Domain 2 Layer 2 EVPN
Which of the following statements about the Layer 2 EVPN configuration/operation in a Nokia SR Linux is FALSE?
Comprehensive and Detailed 150 to 250 words of Explanation From [SR Linux EVPN and Data Center Interconnect/Course Guide/topics]:
In SR Linux, a Layer 2 EVPN service is implemented using a MAC-VRF network instance. The MAC-VRF represents the tenant bridge domain and is associated with access subinterfaces and a VXLAN data-plane mapping. Local hosts are learned through the data plane when Ethernet frames arrive on local interfaces. Remote hosts, however, are not learned by flooding or by configuring static per-peer VXLAN interfaces. They are learned through MP-BGP EVPN updates, especially EVPN route type 2 MAC/IP Advertisement routes. Option B is false because SR Linux does not require a separate manually configured VXLAN interface toward each remote VTEP for the MAC-VRF. Instead, the MAC-VRF is bound to VXLAN encapsulation and a VNI, while remote VTEPs and their MAC reachability are discovered dynamically through the EVPN control plane. This is one of the central advantages of EVPN compared with static VXLAN flood-and-learn models: the overlay endpoints and endpoint reachability are signaled through BGP, reducing manual configuration and improving scale. Reference: SR Linux L2 EVPN MAC-VRF configuration, MP-BGP EVPN learning, VXLAN data-plane mapping.
Get the complete 4A0-D03 question set
$20$40
Question 4 Domain 3 L3 EVPN
Which of the following statements about the configuration of a Layer 3 multi-homing with a centralized router is FALSE?
Comprehensive and Detailed 150 to 250 words of Explanation From [SR Linux EVPN and Data Center Interconnect/Course Guide/topics]:
Layer 3 EVPN multi-homing with a centralized router uses an Ethernet Segment to associate multiple leaf routers with a common external L3 attachment. The centralized router is part of that attached segment from the forwarding perspective, and the connected leaf routers advertise third-party or customer prefixes into EVPN so that remote leaves can reach those prefixes through the multi-homed attachment. For L3 EVPN, learned customer prefixes are normally advertised using EVPN route type 5, which carries IP prefix reachability. In an all-active design, remote leaf routers may load balance traffic to the customer prefix through multiple attached leaf routers because the ES next-hop allows the remote PE to understand that the prefix is reachable through a multi-homed Ethernet Segment. The false statement is that every router participating in the Ethernet Segment must be configured with all-active mode. Multi-homing mode is a design and configuration property of the EVPN PEs participating in the ES, and designs may use single-active or all-active behavior depending on redundancy and forwarding requirements. Reference: L3 EVPN multi-homing, centralized router attachment, EVPN RT-5 prefix advertisement.
Question 5 Domain 2 Layer 2 EVPN
Which of the following is always found in an extended community associated with an EVPN update?
Comprehensive and Detailed 150 to 250 words of Explanation From [SR Linux EVPN and Data Center Interconnect/Course Guide/topics]:
The route target is the extended community consistently associated with EVPN updates to control route import and export between EVPN instances. In SR Linux EVPN services, route targets determine which MAC-VRF or IP-VRF should import a received EVPN route. This is essential for tenant separation because multiple tenants may use overlapping MAC or IP address spaces while sharing the same physical fabric and BGP control plane. The AFI/SAFI is not an extended community; it identifies the BGP address family and subsequent address family used to carry EVPN NLRI. The EVPN route type is also not an extended community; it is part of the EVPN NLRI structure and identifies whether the route is RT-1, RT-2, RT-3, RT-4, RT-5, and so on. The VXLAN network ID may be carried or inferred through service and encapsulation-specific attributes, but it is not universally present as the required extended community in every EVPN update. The route target is the mandatory policy element that enables receiving PEs to place EVPN routes into the correct service context. Reference: EVPN extended communities, route-target import/export policy, tenant service identification.
Question 6 Domain 1 EVPN on SR Linux
Which EVPN route-type (RT) is used in multi-homing scenarios to support aliasing and fast convergence?
Comprehensive and Detailed 150 to 250 words of Explanation From [SR Linux EVPN and Data Center Interconnect/Course Guide/topics]:
The EVPN route type used for aliasing and fast convergence in multi-homing is RT-1, the Ethernet Auto-Discovery route. RT-1 has two important forms: Ethernet A-D per Ethernet Segment and Ethernet A-D per EVI. These routes advertise reachability to a multi-homed Ethernet Segment and to a specific EVPN instance on that segment. Remote PEs use this information for aliasing, meaning they can forward traffic toward any eligible PE attached to the same Ethernet Segment, even when a specific MAC was advertised by only one PE. RT-1 also supports fast convergence because withdrawal of Ethernet A-D routes quickly informs remote PEs that an attachment path or PE is no longer valid, avoiding slow MAC aging as the primary failure-detection mechanism. RT-4 Ethernet Segment routes are related to multi-homing, but their main function is Ethernet Segment discovery and Designated Forwarder election. RT-2 advertises host MAC/IP reachability, and RT-3 builds multicast/BUM replication lists. Therefore, RT-1 is the precise answer for aliasing and fast convergence. Reference: EVPN multi-homing route types, Ethernet Auto-Discovery, aliasing and convergence behavior.
Question 7 Domain 4 L2 and L3 EVPN Multi-homing
Consider the exhibit.
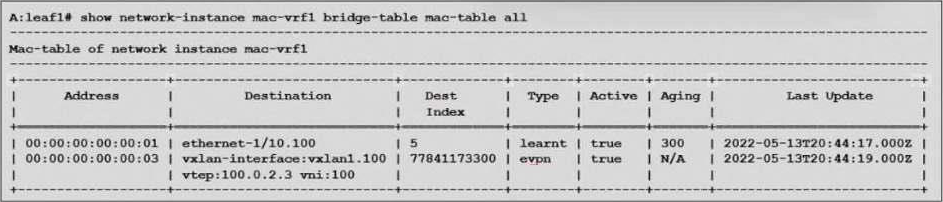
Which of the following statements is FALSE?
Comprehensive and Detailed 150 to 250 words of Explanation From [SR Linux EVPN and Data Center Interconnect/Course Guide/topics]:
In an SR Linux Layer 2 EVPN MAC-VRF, locally attached MAC addresses are learned through the data plane on local access interfaces, while remote MAC addresses are learned from MP-BGP EVPN control-plane advertisements and installed with a VXLAN next-hop. The exhibit shows one local learned MAC on an Ethernet subinterface and another MAC learned through EVPN with a VXLAN interface and VNI 100. The remote VTEP or next-hop information identifies the remote endpoint, and the VNI maps the received VXLAN traffic to the correct MAC-VRF service. The false statement is C because saying that the MAC address associated with the vxlan-interface ''will not age out'' is too absolute. A remote EVPN MAC is not aged in the same way as a local data-plane-learned MAC, but it can still be removed when the corresponding EVPN route is withdrawn, invalidated, or no longer present in the control plane. The ''N/A'' style aging behavior does not mean permanent retention. Reference: SR Linux MAC-VRF verification, local MAC learning, EVPN-learned remote MACs, VXLAN VNI mapping.
What the Nokia 4A0-D03 Exam Covers
Exam domains verified against the Official Nokia 4A0-D03 exam guide, last checked November 2026.
Domain 1 EVPN on SR Linux
Understand the purpose and application of EVPN in data centers, including EVPN building blocks with MP-BGP control plane and VXLAN data plane. Study BGP EVPN route types, basic EVPN operations, and hands-on configuration of BGP and VXLAN tunnels for EVPN on SR Linux, including leaf and spine underlay networks and BGP route reflectors.
Domain 2 Layer 2 EVPN
Learn L2 EVPN use cases and operations, including configuration of MAC-VRF for L2 EVPN with SR Linux CLI. Examine L2-related EVPN routes, MAC protection, MAC mobility and MAC duplication monitoring. Study proxy-ARP implementation for IP duplication detection and anti-spoofing in L2 EVPN environments.
Domain 3 L3 EVPN
Explain the use case for L3 EVPN; Describe the L3 EVPN Asymmetric Model and its implementation using the EVPN MAC/IP route type 2; Describe the L3 Symmetric Model and its implementation using the EVPN IP Prefix Route Type 5; Explain the purpose of IRB interfaces and the anycast-gateway IP address; Configure both an Asymmetric and Symmetric L3 EVPN with SR Linux CLI; Configure a L3 EVPN PE-CE BGP peering and verify how BGP path attributes are propagated across the EVPN; Hands-on Labs:; L3 EVPN – Asymmetric model with anycast-gateway IP addresses; L3 EVPN – Symmetric model with host-route advertising; Configure a PE-CE BGP peering in the L3 EVPN
Sample question from this domain above Q4
Domain 4 L2 and L3 EVPN Multi-homing
Understand multi-homing use cases and redundancy modes including all-active and single-active configurations. Study Ethernet Segment concepts, designated forwarder election algorithms with EVPN route type 4, and the local-bias mechanism to prevent L2 traffic loops. Learn EVPN auto-discovery route type 1 variants for aliasing and mass withdrawals.
Domain 5 DCI And 7750 SR interoperability
Learn data center interconnection options including gateway-less and gateway-based solutions over WAN networks. Configure and verify L2 EVPN DCI solutions demonstrating SR Linux interoperability with 7750 SR MPLS-based EVPN-VPLS and L3 EVPN DCI solutions with legacy MPLS-based IP-VPN solutions.
4A0-D03 Exam FAQ
Common questions about the exam itself
What background do I need to take the 4A0-D03 exam?
How difficult is the 4A0-D03 exam and what makes it challenging?
Which topics are typically the hardest for candidates preparing for 4A0-D03?
How long should I prepare for the 4A0-D03 exam?
What happens on exam day for the 4A0-D03?
What are the retake and rescheduling policies for 4A0-D03?
How long is the 4A0-D03 certification valid for?
What job roles is the 4A0-D03 certification suited for?
How does 4A0-D03 fit into the Nokia Data Center Fabric certification track?
Can I take 4A0-D03 without completing the Data Center Fabric Fundamentals exam?
Other Nokia Exams
Free practice questions for more Nokia certification exams