
Microsoft SC-401 Practice Exam Questions & Answers
Microsoft SC-401 Exam Details
Key details for this exam, checked against the published exam outline
- Exam Code
- SC-401
- Full Name
- Administering Information Security in Microsoft 365
- Issuing Body
- Microsoft
- Question Format (Our Bank)
- Multiple Choice, Hotspot, Drag & Drop, Case Studies
- Delivery
- Online proctored or at a Pearson VUE test centre
- Eligibility
- No formal prerequisites required. Familiarity with Microsoft 365 services, PowerShell, Microsoft Entra, and Microsoft Defender tools is recommended.
- Validity
- 1 year from the date of passing. renewal requires passing a free online assessment on Microsoft Learn
- Full Question Set
- 223 questions Get All Questions
Free SC-401 Practice Questions
Each question shows the correct answer and an explanation of why it is right
Question 1 Domain 1 Implement information protection
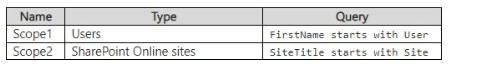
You have a Microsoft 365 E5 subscription that contains the adaptive scopes shown in the following table.
You create the retention policies shown in the following table.
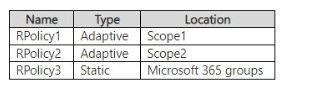
Which retention policies support a preservation lock?
Question 2 Domain 1 Implement information protection
You have a Microsoft 365 subscription.
You create a new trainable classifier.
You need to train the classifier.
Which source can you use to train the classifier?
Question 3 Domain 2 Implement data loss prevention and retention
You create a retention label that has a retention period of seven years.
You need to ensure that documents containing a credit card number are retained for seven years. Other documents must not be retained.
What should you create?
Get the complete SC-401 question set
$20$40
Question 4 Domain 1 Implement information protection
You have a Microsoft 36S E5 subscription that has a Microsoft Purview exact data match (EDM) classifier named EDM1.
You plan to create the Microsoft Purview policies shown in the following table.
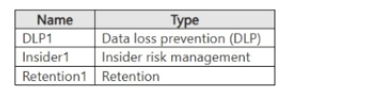
Which policies can use EDM1?
Question 5 Domain 1 Implement information protection
You need to meet the technical requirements for the creation of the sensitivity labels.
To which user or users must you assign the Sensitivity Label Administrator role?
To meet the requirement that all administrative users must be able to create Microsoft 365 sensitivity labels, we need to assign the Sensitivity Label Administrator role to the correct users.
Sensitivity Label Administrator Role Responsibilities
This role allows users to:
Create and manage sensitivity labels in Microsoft Purview.
Publish and configure auto-labeling policies.
Modify label encryption and content marking settings.
Review of Admin Roles from the Table:
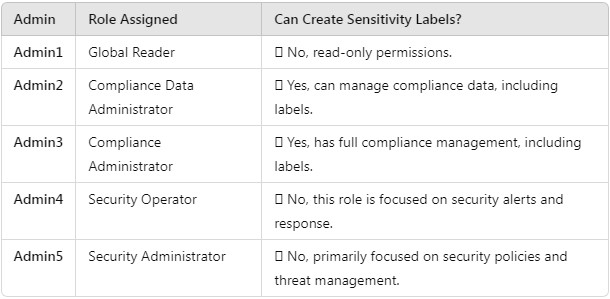
Users that must be assigned the Sensitivity Label Administrator role:
Admin2 (Compliance Data Administrator)
Admin3 (Compliance Administrator)
Admin1 (Global Reader) (should be assigned this role to fulfill the requirement that all admins can create labels).
Question 6 Domain 2 Implement data loss prevention and retention
You have a sensitive information type based on a trainable classifier.
You are unsatisfied with the result of the trainable classifier.
You need to retrain the classifier.
What should you use in the Microsoft Purview portal?
Question 7 Domain 1 Implement information protection
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have a Microsoft 365 tenant and 500 computers that run Windows 11. The computers are onboarded to Microsoft Purview.
You discover that a third-party application named Tailspin_scanner.exe accessed protected sensitive information on multiple computers. Tailspin_scanner.exe is installed locally on the computers.
You need to block Tailspin_scanner.exe from accessing sensitive documents without preventing the application from accessing other documents.
Solution: From Microsoft Defender for Cloud Apps, you create an app discovery policy.
Does this meet the goal?
Creating an app discovery policy in Microsoft Defender for Cloud Apps is used for detecting and monitoring cloud application usage, but it does not prevent a locally installed application (Tailspin_scanner.exe) from accessing sensitive files on Windows 11 devices.
To block Tailspin_scanner.exe from accessing sensitive documents while allowing it to access other files, the correct solution is to use Microsoft Purview Endpoint Data Loss Prevention (Endpoint DLP) and add Tailspin_scanner.exe to the Restricted Apps list.
Endpoint DLP allows you to block specific applications from accessing sensitive files while keeping general access available. Restricted Apps List in Endpoint DLP ensures that Tailspin_scanner.exe cannot open, copy, or process protected documents, but it can still function normally for non-sensitive content.
What the Microsoft SC-401 Exam Covers
Exam domains verified against the Official Microsoft SC-401 exam guide, last checked November 2026.
Domain 1 Implement information protection
30% - 35%This domain covers data classification, sensitivity labels, and information protection across Windows, file shares, and Exchange. You need hands-on experience creating and managing sensitivity labels, configuring protection settings, and applying labels to containers like Teams, Groups, and SharePoint. Practice building custom sensitive info types and implementing the Purview Information Protection client to classify data across on-premises and cloud environments.
Domain 2 Implement data loss prevention and retention
30% - 35%Focus on designing and configuring data loss prevention policies, implementing Endpoint DLP, and managing retention policies and labels. You should understand policy precedence, configure adaptive protection, and set up just-in-time protection. Hands-on work with DLP policy creation, testing policies to trigger alerts, and configuring retention labels for data lifecycle management will strengthen your readiness for this equally weighted domain.
Domain 3 Manage risks, alerts, and activities
30% - 35%This domain covers Insider Risk Management implementation, managing information security alerts, and protecting data used by AI services. You need to configure insider risk policies, manage alerts and cases, and respond to Purview alerts. Additionally, understand audit logging, content search, and the new controls for Data Security Posture Management for AI. All three domains carry equal weight, so ignoring this area will cost points.
SC-401 Exam FAQ
Common questions about the exam itself
What is the SC-401 exam format and how much time do I have?
How hard is SC-401 compared to SC-400?
What hands-on preparation is most important for SC-401?
Do I need any certifications before attempting SC-401?
What is the passing score for SC-401 and how is it calculated?
How long should I study for SC-401?
How long does the SC-401 certification stay valid and how do I renew it?
Which domain on SC-401 do most candidates struggle with?
What is the difference between SC-401 and SC-400, and which should I take?
What job role does SC-401 prepare me for?
Other Microsoft Exams
Free practice questions for more Microsoft certification exams