Key details for this exam, checked against the published exam outline
Each question shows the correct answer and an explanation of why it is right
You have an Azure AD tenant that contains an access package named Package1 and a user named User1. Package1 is configured as shown in the following exhibit.
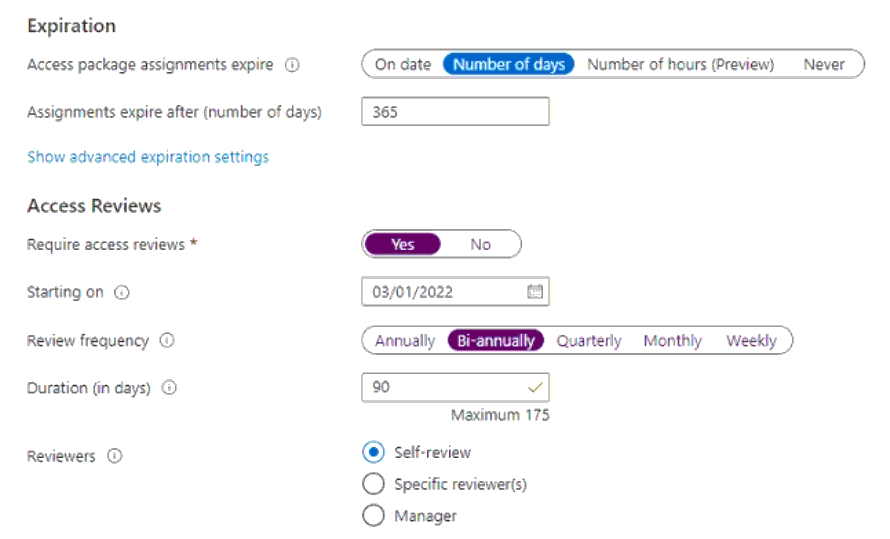
You need to ensure that User1 can modify the review frequency of Package1. The solution must use the principle of least privilege.
Which role should you assign to User1?
This question refers to Azure AD Entitlement Management under Identity Governance. The goal is to let User1 modify the review frequency (i.e., Access Reviews) for an existing access package named Package1, following the principle of least privilege.
In Azure AD, the ability to create and manage access packages, catalogs, and access reviews is granted through certain administrative roles:
Global Administrator and Identity Governance Administrator --- Full control over all Identity Governance settings.
Catalog Owner or Access Package Manager --- Manage access packages and settings within a catalog.
User Administrator --- Can configure access reviews and manage users, groups, and limited governance settings.
Privileged Role Administrator, Security Administrator, and External Identity Provider Administrator --- Have no direct control over access review settings in Entitlement Management.
From Microsoft documentation (''Azure AD Entitlement Management Delegation and Roles''):
''A user administrator can manage access reviews and entitlement management settings for the directory and assigned catalogs, including adjusting the review frequency or review settings.''
Thus, to modify the Access Review configuration (frequency, reviewers, etc.) in Package1, the User Administrator role provides the minimum necessary privilege without granting excessive permissions like Identity Governance Administrator or Global Administrator.
You need to locate licenses to the
According to the Microsoft SC-300: Identity and Access Administrator official study guide and the Microsoft Learn module ''Manage user and group licenses in Microsoft Entra ID (Azure AD)'', when you need to automatically assign licenses to users based on specific attributes (such as department, location, or a custom attribute like LWLicenses), you should use a Dynamic User Security Group in Azure Active Directory (Entra ID).
In the scenario, Litware wants to:
''Manage the assignment of Azure AD licenses by modifying the value of the LWLicenses attribute. Users who have the appropriate value for LWLicenses must be added automatically to the Microsoft 365 group that has the appropriate license assigned.''
This requirement directly maps to a Dynamic User security group, which supports dynamic membership rules that automatically include users when their attributes meet defined conditions (for example, user.extensionAttribute15 -eq 'E5'). When a license is assigned to this dynamic group, Azure AD automatically provisions or removes licenses for members based on their attribute values --- eliminating manual license management.
Per Microsoft documentation:
''You can assign licenses to a group that has dynamic membership. When a user's attributes change, Azure AD automatically adds or removes them from the group, which updates their license assignments accordingly.''
Now, analyzing the other options:
B . An OU (Organizational Unit): Used in on-premises Active Directory, not Azure AD. It cannot manage cloud-based license assignments.
C . A Distribution Group: Used for email distribution in Exchange Online; cannot be used for license assignment.
D . An Administrative Unit: Used for scoping administrative permissions, not for license assignment.
Therefore, the only object type that satisfies both the technical and automation requirements is a Dynamic User Security Group.
You have an Azure Active Directory (Azure AD) tenant that uses conditional access policies.
You plan to use third-party security information and event management (SIEM) to analyze conditional access usage.
You need to download the Azure AD log that contains conditional access policy data.
What should you export from Azure AD?
As per the Microsoft SC-300: Identity and Access Administrator Study Guide and official Microsoft Learn content under ''Monitor and troubleshoot Azure AD using reports and logs'', Conditional Access policy data is captured in the Sign-ins log within Azure Active Directory. Each sign-in record contains detailed information about the authentication process, including which conditional access policies were evaluated, the policies applied, and their enforcement results (e.g., ''Grant access,'' ''Block,'' or ''Require MFA'').
The Audit logs in Azure AD, on the other hand, track directory-level changes such as policy creation, modification, or administrative actions --- they do not include user authentication or conditional access evaluation data. Therefore, to analyze Conditional Access activity in an external SIEM system, you must export Sign-in logs, which contain the conditional access evaluation details.
Microsoft documentation specifies that exporting in JSON format is preferred for integration with third-party SIEM systems because JSON preserves nested policy evaluation data structures that CSV format cannot fully represent. CSV exports omit detailed conditional access results (e.g., policy IDs and results per policy), making them unsuitable for automated parsing and deep analysis.
Thus, based on official Microsoft documentation:
''Conditional Access policy evaluation results are only available in Sign-in logs and should be exported in JSON format for SIEM integration.''
Correct Answe r: A. sign-ins in JSON format
A user named User1 receives an error message when attempting to access the Microsoft Defender for Cloud Apps portal.
You need to identify the cause of the error. The solution must minimize administrative effort.
What should you use?
According to the Microsoft SC-300: Identity and Access Administrator Study Guide and Microsoft Entra ID (Azure AD) documentation, sign-in logs are the primary source for diagnosing and troubleshooting authentication and access issues for Azure AD--integrated services, including Microsoft Defender for Cloud Apps (formerly Microsoft Cloud App Security).
The sign-in logs record all user authentication attempts --- successful and failed --- along with critical details such as:
User identity (User Principal Name)
Application name (in this case, ''Microsoft Cloud App Security'' or ''Microsoft Defender for Cloud Apps'')
IP address and device details
Conditional Access policy outcomes
Failure reasons (e.g., MFA requirement, denied by Conditional Access, invalid token, etc.)
These logs can be accessed directly from the Microsoft Entra admin center Monitoring Sign-in logs. They allow administrators to quickly identify why a user was unable to access a specific cloud service, without needing to configure or collect extra data sources.
Other log types do not fit this scenario:
Audit logs record changes (e.g., policy updates, role assignments) but not authentication attempts.
Provisioning logs track synchronization and provisioning events from connected applications.
Log Analytics is a log aggregation workspace; it's not the first-line diagnostic tool and requires extra configuration.
Hence, to identify the cause of User1's access error with minimal administrative effort, the correct choice is sign-in logs.
You have a Microsoft Entra ID P2 tenant named contoso.com that contains a registered app named App1. On January 1, App1 was deleted. You need to restore Appl.
What is the last day on which you can restore Appl1?
You have an Azure AD tenant that uses Azure AD Identity Protection and contains the resources shown in the following table.
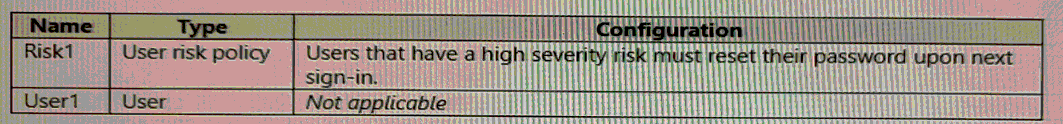
Azure Multi-Factor Authentication (MFA) is enabled for all users.
User1 triggers a medium severity alert that requires additional investigation.
You need to force User1 to reset his password the next time he signs in. the solution must minimize administrative effort.
What should you do?
According to the Microsoft Identity and Access Administrator (SC-300) Official Study Guide and Microsoft Learn: ''Azure AD Identity Protection -- User Risk Policies and Remediation'', Azure AD Identity Protection provides mechanisms to automatically or manually remediate risky user accounts based on detected user risk levels (low, medium, high).
The scenario states:
A User risk policy (Risk1) exists that requires users with a high severity risk to reset their password upon next sign-in.
User1 has triggered a medium severity alert, not high.
The goal is to force User1 to reset his password on the next sign-in, with minimal administrative effort.
Analysis of Options:
A. Configure a sign-in risk policy: This policy targets sign-in risks (suspicious sign-ins), not user risks, and would not directly force a password reset --- it only enforces MFA or blocks access.
B. Mark User1 as compromised: When an administrator marks a user as compromised in Azure AD Identity Protection, it immediately elevates the user's risk level to ''high.'' Since the existing User risk policy (Risk1) automatically forces password reset for high-risk users, User1 will be required to change his password the next time he signs in --- satisfying the requirement automatically. This approach uses the existing configuration, meeting the ''minimize administrative effort'' criterion.
C. Reconfigure the user risk policy to trigger on medium or low severity: This would affect all users globally, not just User1, which is not minimal effort and could increase false positives.
D. Reset the Azure MFA registration for User1: This affects MFA credentials, not password resets, and doesn't remediate risk.
From Microsoft's documentation:
''Marking a user as compromised increases their risk level to High, triggering any configured user risk policy to require password reset upon next sign-in.''
Therefore, the most efficient and compliant action according to Microsoft's SC-300 study materials is to mark User1 as compromised.
Exam domains verified against: Official Microsoft SC-300 exam guide, last checked October 2026.
Configure and administer Microsoft Entra tenant and its domains. Manage user lifecycle from creation through deprovisioning. Set up custom organizational units and manage user properties throughout their lifecycle in the directory.
Sample question from this domain above: Q3
Plan and deploy Microsoft Entra user authentication methods including MFA and SSPR. Implement and manage Conditional Access policies. Configure access management for Azure resources and Azure roles based on Zero Trust principles.
Select and configure identities for Azure workloads including managed identities and service principals. Register applications in Entra and manage app access permissions. Monitor and govern enterprise application integration and usage.
Sample question from this domain above: Q2
Design and deploy entitlement management in Entra for access provisioning and deprovisioning. Conduct access reviews and manage privileged access using Privileged Identity Management. Monitor identity activity through logs, workbooks and reports to track security posture.
Sample question from this domain above: Q5
Common questions about the exam itself

