
Microsoft MD-102 Practice Exam Questions & Answers
Microsoft MD-102 Exam Details
Key details for this exam, checked against the published exam outline
- Exam Code
- MD-102
- Full Name
- Microsoft 365 Certified: Endpoint Administrator Associate
- Issuing Body
- Microsoft
- Question Format (Our Bank)
- Multiple Choice, Hotspot, Drag & Drop, Order List, Case Studies
- Delivery
- Online proctored via Pearson VUE OnVUE or at a Pearson VUE test centre
- Eligibility
- Experience with Microsoft Entra ID and Microsoft 365 technologies including Intune, plus hands-on experience deploying, configuring, and maintaining Windows client and non-Windows devices
- Full Question Set
- 465 questions Get All Questions
Free MD-102 Practice Questions
Each question shows the correct answer and an explanation of why it is right
Question 1 Domain 3 Protect devices
Your network contains an Active Directory domain.
You deploy a Microsoft Entra tenant.
Another administrator configures the domain to synchronize to the Microsoft Entra tenant.
You discover that 10 user accounts in an organizational unit (OU) are NOT synchronized to the Microsoft Entra tenant. All the other user accounts synchronized successfully.
You review Microsoft Entra Connect Health and discover that all the user account synchronizations completed successfully You need to ensure that the 10 user accounts are synchronized to the Microsoft Entra tenant.
Solution: From Microsoft Entra Connect Sync, you modify the Microsoft Entra credentials. Does this meet the goal?
This solution does NOT meet the goal. The 10 user accounts are not synchronizing because of a scoping or filtering issue at the synchronization level, not because of incorrect Entra credentials. Modifying the Microsoft Entra credentials would not affect which accounts get synchronized from on-premises Active Directory. This action is unnecessary and would not resolve the synchronization issue.
Question 2 Domain 1 Prepare infrastructure for devices
You have a Microsoft Entra tenant that contains the devices shown in the following table.
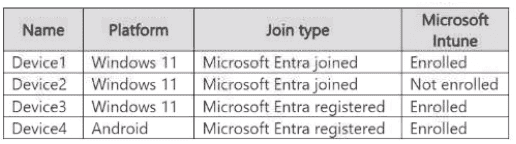
On which devices can you implement Endpoint Privilege Management (EPM)?
Endpoint Privilege Management (EPM) is supported on Windows devices enrolled in Intune. EPM allows users to run applications with elevated privileges without needing local administrator rights, and it is currently available for Windows 10 and Windows 11 devices. macOS and mobile devices do not support EPM at this time.
Question 3 Domain 5 Optimize endpoint operations by using automation, monitoring, and reporting
You ate implementing Microsoft Intune Suite.
You enroll devices in Intune as shown in the following table.
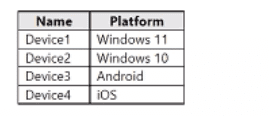
The performance of which devices can be analyzed by using Endpoint analytics?
https://learn.microsoft.com/en-us/mem/analytics/overview#bkmk_prereq
Get the complete MD-102 question set
$20$40
Question 4 Domain 1 Prepare infrastructure for devices
You have 200 computers that run Windows 10. The computers are joined to Microsoft Entra and enrolled in Microsoft Intune. You need to enable self-service password reset on the sign-in screen. Which settings should you configure from the Microsoft Intune admin center?
To enable self-service password reset (SSPR) on the Windows 10 sign-in screen, configure Windows 10 sign-in options or create a device configuration profile with the password reset setting enabled. This allows users to reset their password directly from the sign-in screen without contacting support.
Question 5 Domain 4 Manage and secure applications
Your company has a Microsoft 365 subscription.
All the users in the finance department own personal devices that run iOS or Android. All the devices are enrolled in Microsoft Intune.
The finance department adds new users each month.
The company develops a mobile application named App1 for the finance department users.
You need to ensure that only the finance department users can download Appl.
What should you do first?
To ensure only finance department users can access App1, you should first create a security group containing the finance department users. This group can then be used in subsequent steps to assign the app in Intune, restrict access via Conditional Access policies, or manage app distribution. Creating the group is the foundational first step before any access control can be implemented.
Question 6 Domain 3 Protect devices
You have a Microsoft 365 subscription. You use Microsoft Intune to manage devices. You need to review details about device wipes. Which report should you review?
To review details about device wipes, you should review the Device wipe report. This Intune report provides comprehensive information about all device wipe operations, including which devices were wiped, when they were wiped, who initiated the wipe, and the status of each wipe operation.
Question 7 Domain 1 Prepare infrastructure for devices
You have a Microsoft 365 subscription that contains a user named User1 and uses Microsoft Intune Suite.
You use Microsoft Intune to manage devices that run Windows 11.
User1 provides remote support for 75 devices in the marketing department.
You need to add User1 to the Remote Desktop Users group on each marketing department device.
What should you configure?
https://learn.microsoft.com/en-us/mem/intune/protect/endpoint-security-account-protection-policy#manage-local-groups-on-windows-devices
What the Microsoft MD-102 Exam Covers
Exam domains verified against the Official Microsoft MD-102 exam guide, last checked October 2026.
Domain 1 Prepare infrastructure for devices
20% - 25%This domain covers adding devices to Microsoft Entra ID and enrolling them to Microsoft Intune. You need to understand device registration, enrollment methods, and initial configuration for hybrid and cloud-native management scenarios. Hands-on experience with Windows Autopilot and enrollment policies is essential.
Domain 2 Manage and maintain devices
25% - 30%This is the largest domain and focuses on deploying and upgrading Windows clients via cloud-based tools, designing device configuration profiles, and implementing Intune Suite capabilities. You will also need to perform remote actions on managed devices such as troubleshooting and retirement. Proficiency with Intune configuration at depth is critical here.
Domain 3 Protect devices
15% - 20%This domain covers configuring endpoint security including antivirus, encryption, and firewall settings via Intune policies. You also need to manage device updates and understand compliance monitoring. Knowledge of Microsoft Defender for Endpoint integration and security baselines is important.
Domain 4 Manage and secure applications
15% - 20%Deploy and update apps; Prepare applications for deployment by using Intune; Deploy apps by using Intune, including Win32 apps, line-of-business (LOB) apps, and Microsoft Store apps; Configure Quiet Time policies for Android and iOS apps; Deploy Microsoft 365 Apps by using Intune; Configure policies for Office apps by using Microsoft Intune or the Microsoft 365 Apps admin center; Deploy Microsoft 365 Apps as part of a Windows Autopilot deployment, including using the Office Deployment Tool (ODT) or Microsoft Intune; Manage Microsoft 365 Apps by using the Microsoft 365 Apps admin center; Deploy apps from platform-specific app stores by using Intune, including Apple Volume Purchase Program and Google Play; Monitor app deployment status and troubleshoot installation failures by using Microsoft Intune; Plan and implement app protection and app configuration policies; Plan and implement app protection policies for managed and unmanaged (BYOD) devices by using Microsoft Intune; Implement Microsoft Entra Conditional Access policies for app protection policies; Plan and implement app configuration policies for managed apps and managed devices
Sample question from this domain above Q5
Domain 5 Optimize endpoint operations by using automation, monitoring, and reporting
10% - 15%Automate management tasks; Automate Intune management tasks by using PowerShell and Microsoft Graph; Investigate threats identified by Security Copilot agents in Intune; Analyze device performance by using Security Copilot agents in Intune; Review and respond to Security Copilot agent recommendations to make management decisions; Extend device compliance by using PowerShell; Monitor and optimize health; Implement reporting and data visibility in Microsoft Intune, including customizing reports and filters, using workbooks and dashboards, and exporting reporting data; Monitor endpoint performance by using Endpoint Analytics, including proactive remediations, device health scores, and app startup performance; Configure and manage proactive remediation scripts, including detecting and fixing common device issues, and scheduling remediation runs; Analyze endpoint reliability and user experience scores, including startup performance, restart frequency, and application reliability metrics; Monitor tenant health and Intune service communications, including reviewing service health dashboards, message center notifications, and establishing operational baselines; Configure alerts and notifications for policy and compliance changes, including setting up alert rules for compliance drift, enrollment failures, and configuration conflicts
Sample question from this domain above Q3
MD-102 Exam FAQ
Common questions about the exam itself
What background do I need before attempting MD-102?
Why is domain 2, Manage and maintain devices, considered the hardest part?
How long does MD-102 certification stay valid?
How long should I spend preparing for MD-102?
What happens on exam day for MD-102?
What if I fail MD-102? Can I retake it quickly?
Does MD-102 require any prerequisite certifications?
How does MD-102 relate to MS-102?
What job role does MD-102 prepare me for?
How does MD-102 differ from the older MD-100 and MD-101 exams?
Other Microsoft Exams
Free practice questions for more Microsoft certification exams