
Microsoft AZ-800 Practice Exam Questions & Answers
Microsoft AZ-800 Exam Details
Key details for this exam, checked against the published exam outline
- Exam Code
- AZ-800
- Full Name
- Administering Windows Server Hybrid Core Infrastructure
- Issuing Body
- Microsoft
- Question Format (Our Bank)
- Multiple Choice, Hotspot, Order List, Drag & Drop, Case Studies
- Delivery
- Online proctored via OnVUE or at a Pearson VUE test center
- Eligibility
- Several years of practical Windows Server administration experience in on-premises and hybrid environments recommended
- Full Question Set
- 260 questions Get All Questions
Free AZ-800 Practice Questions
Each question shows the correct answer and an explanation of why it is right
Question 1
Your network contains an Active Directory Domain Services (AD DS) forest. The forest contains three Active Directory sites named Site1, Site2, and Site3. Each site contains two domain controllers. The sites are connected by using DEFAULTIPSITELINK.
You open a new branch office that contains only client computers.
You need to ensure that the client computers in the new office are primarily authenticated by the domain controllers in Site1.
Solution: You create a new subnet object that is associated to Site1.
Does this meet the goal?
In the Administering Windows Server Hybrid Core Infrastructure guidance for ''Implement and manage AD DS sites and replication,'' Microsoft explains that client computers are site-aware and ''select domain controllers in their own site whenever possible.'' A client's site membership is determined solely by the mapping of its IP subnet to an AD DS site. The material further notes that administrators should ''create subnet objects and associate them to the appropriate site so that clients resolve and authenticate to DCs in that site; if a subnet is not mapped, clients may use any reachable site through site coverage.'' By creating a new subnet object for the branch office and associating it with Site1, all clients in that subnet will treat Site1 as their site and will therefore query and authenticate primarily against Site1's domain controllers, only failing over to other sites if necessary via DEFAULTIPSITELINK. This meets the stated goal without requiring domain controllers in the new office, because site affinity controls the preferred DC selection for Kerberos/NTLM authentication and LDAP/GC queries.
Question 2 Domain 1 Deploy and manage Active Directory Domain Services (AD DS) in on-premises and cloud environments
Your on-premises network contains an Active Directory domain named contoso.com. You have an Azure AD tenant. You plan to sync contoso.com with the Azure AD tenant by using Azure AD Connect cloud sync. You need to create an account that will be used by Azure AD Connect cloud sync. Which type of account should you create?
In the AZ-800/''Administering Windows Server Hybrid Core Infrastructure'' content, Azure AD Connect cloud sync uses a lightweight provisioning agent that reads from on-premises AD DS. The agent runs under a Group Managed Service Account (gMSA) so it can securely obtain and rotate credentials automatically. The implementation guidance states that during agent installation you provide domain admin credentials once so the installer can create and delegate a gMSA for the agent; alternatively, you can pre-create the gMSA and assign it. The documentation emphasizes that cloud sync does not rely on user or computer accounts with static passwords; instead it ''deploys a gMSA for the agent service to ensure secure, automatic password management and least-privilege directory access.'' System-assigned managed identities apply to Azure resources only (not on-prem AD DS), and InetOrgPerson is an object class for users, not a service identity. A regular user account would introduce password management and rotation issues and is not the recommended nor required identity type for the cloud sync agent. Therefore, to satisfy Azure AD Connect cloud sync prerequisites, you create and use a gMSA.
Question 3 Domain 4 Implement and manage an on-premises and hybrid networking infrastructure
SIMULATION
Task 5
You need to ensure that a DHCP scope named scope! on SRV1 can service client requests.
One possible solution to ensure that a DHCP scope named scope1 on SRV1 can service client requests is to activate the scope on the DHCP server. A scope must be activated before it can assign IP addresses to DHCP clients. To activate a DHCP scope on SRV1, perform the following steps:
On SRV1, openDNS Managerfrom theAdministrative Toolsmenu or by typingdnsmgmt.mscin the Run box.
In the left pane, expand your DHCP server and click onIPv4.
In the right pane, right-click on the scope that you want to activate, such asscope1, and selectActivate.
Wait for the scope to be activated. You can verify the activation status by checking the icon next to the scope name. A green arrow indicates that the scope is active, while a red arrow indicates that the scope is inactive.
Now, the DHCP scope named scope1 on SRV1 can service client requests and lease IP addresses to DHCP clients. You can test the DHCP service by using theipconfig /renewcommand on a DHCP client computer that is connected to the same subnet as the scope.
Get the complete AZ-800 question set
$20$40
Question 4 Domain 4 Implement and manage an on-premises and hybrid networking infrastructure
You have an on-premises Active Directory Domain Services (AD DS) domain that syncs with an Azure Active Directory (Azure AD) tenant The on-premises network is connected to Azure by using a Site-to-Site VPN. You have the DNS zones shown in the following table.
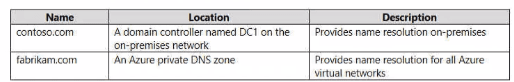
You need to ensure that names from fabrikam.com can be resolved from the on-premises network Which two actions should you perform? Each correct answer presents part of the solution, NOTE: Each correct selection Is worth one point
In hybrid name-resolution designs covered in Administering Windows Server Hybrid Core Infrastructure, Azure Private DNS does not support zone transfers and therefore you cannot host it on, or pull it into, on-premises DNS by using stub or secondary zones. The guidance states that when on-premises clients must resolve names that live in an Azure Private DNS zone, the recommended pattern is to place a DNS forwarder in Azure (typically a Windows Server VM running the DNS role) that can directly query the Azure resolver from inside the virtual network. Then, on-premises Windows DNS servers are configured with a conditional forwarder that forwards queries for the private zone's suffix to the Azure DNS forwarder over the VPN/ExpressRoute connection.
This achieves the following:
Keeps the authoritative zone in Azure Private DNS while making it reachable from on-premises.
Avoids unsupported mechanisms (no AXFR/IXFR available from Azure Private DNS, so stub and secondary zones won't work).
Uses least privilege and minimal change on both sides: add a DNS VM in Azure (E) and create a conditional forwarder on DC1 for fabrikam.com pointing to that VM's private IP (A).
Options B and C require zone transfers, which are not available from Azure Private DNS, and D (changing VNet DNS servers) affects Azure VMs' resolver settings but does not enable on-premises resolution of the Azure-hosted private zone.
Question 5 Domain 2 Manage Windows Servers and workloads in a hybrid environment
You have an on premises Active Directory Domain Services (AD DS) domain that syncs with an Azure Active Directory (Azure AD) tenant. The domain contains two servers named Server1 and Server2.
A user named Admin1 is a member of the local Administrators group on Server1 and Server2.
You plan to manage Server1 and Server2 by using Azure Arc. Azure Arc objects will be added to a resource group named RG1.
You need to ensure that Admin1 can configure Server1 and Server2 to be managed by using Azure Arc.
What should you do first?
In the Administering Windows Server Hybrid Core Infrastructure content for Azure Arc--enabled servers, the onboarding script (interactive or service-principal based) requires that the identity used to connect a machine has the least-privilege built-in role at the intended scope. The guide states that for scripted or portal onboarding you should ''grant the Azure RBAC role Azure Connected Machine Onboarding at the subscription or resource-group scope to the identity that will run the connect process; this role includes only the permissions necessary to register and connect the server resource.'' It also notes that no hybrid Azure AD join is required just to onboard Arc, and that local admin on the target server is sufficient for installing the Connected Machine agent. Therefore, before Admin1 runs the onboarding script for Server1 and Server2 into RG1, you must first assign Admin1 the Azure Connected Machine Onboarding role at RG1. This satisfies least privilege and enables the script to create the Microsoft.HybridCompute/machines resource entries and related artifacts while avoiding broader roles like Contributor or Owner.
Question 6 Domain 1 Deploy and manage Active Directory Domain Services (AD DS) in on-premises and cloud environments
You have an Active Directory Domain Services (AD DS) domain. The domain contains a member server named Server1 that runs Windows Server.
You need to ensure that you can manage password policies for the domain from Serve1.
Which command should you run first on Server1?
In Windows Server hybrid environments, domain password policy and fine-grained password policy (PSO) administration is performed with the Active Directory administration tools. The AZ-800 study domain states that to ''manage AD DS, including users, groups, OUs, Group Policy, and fine-grained password policies from a member server, you must first install the Remote Server Administration Tools (RSAT) for Active Directory.'' The RSAT AD DS package (RSAT-AD-Tools) installs Active Directory Users and Computers (ADUC), Active Directory Administrative Center (ADAC) (which includes the Password Settings container UI), and Windows PowerShell for Active Directory (the ActiveDirectory module). The guidance further clarifies: ''ADAC exposes Password Settings Objects (PSOs) and lets administrators create, link, and manage fine-grained password and lockout policies without signing in to a domain controller.'' Therefore, on Server1 the first required command is: Install-WindowsFeature RSAT-AD-Tools. Options for only PowerShell, DHCP, or WINS features do not provide ADAC/ADUC and cannot manage PSOs or domain password policies from a member server.
Question 7 Domain 3 Manage virtual machines and containers
What should you implement for the deployment of DC3?
The exam materials explain that to add a new domain controller to an existing AD DS forest in Azure, you deploy a Windows Server IaaS VM and then promote it: ''To extend on-premises AD DS into Azure, provision a Windows Server VM in Azure and run AD DS to create an additional domain controller for the existing domain.'' Conversely, Azure Active Directory Domain Services (Azure AD DS) provides a managed domain that is separate from and not writable by your on-premises administrators---you ''do not get domain admin rights or access to DCs''---so it cannot be used to add a DC (dc3.corp.fabrikam.com) to the existing corp.fabrikam.com forest. Azure AD Application Proxy and Azure AD administrative units are unrelated to deploying DCs. Therefore, the correct implementation is to deploy an Azure virtual machine in Vnet1, install AD DS/DNS, and promote it to become DC3 in the existing domain.
Question 8 Domain 5 Manage storage and file services
You have four testing devices that are configured with static IP addresses as shown in the following table.
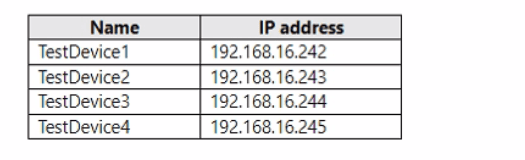
The test devices are turned on once a month.
You need to prevent Server1 from assigning the IP addresses allocated to the test devices to other devices when the test devices are offline. The solution must minimize administrative effort.
What should you do?
The DHCP planning and configuration section in Administering Windows Server Hybrid Core Infrastructure states: ''Use exclusion ranges to prevent the DHCP Server from leasing specific addresses that are in use by statically assigned hosts.'' Reservations are intended for DHCP clients that must always receive the same IP from the scope; they do not apply to devices configured with static IPs and would add unnecessary administration. Because the four test devices are statically addressed and are powered on only monthly, the simplest way to ensure the DHCP server never leases their addresses is to exclude those exact IP addresses from the scope. Scope options and policies do not reserve or block individual addresses from lease assignment. Therefore, to prevent conflicts with minimal effort, configure exclusion entries for 192.168.16.242--245 in the relevant scope.
What the Microsoft AZ-800 Exam Covers
Exam domains verified against the Official Microsoft AZ-800 exam guide, last checked November 2026.
Domain 1 Deploy and manage Active Directory Domain Services (AD DS) in on-premises and cloud environments
30% - 35%Cover domain controller deployment in hybrid scenarios, multi-site and multi-forest management, security principals, and hybrid identity implementation. Group Policy administration is a core part of this domain, which carries the heaviest exam weight.
Domain 2 Manage Windows Servers and workloads in a hybrid environment
10% - 15%Focus on administering Windows Servers across on-premises and Azure using hybrid management tools. Integration with Azure services like Azure Arc and Windows Admin Center is central to this objective area.
Sample question from this domain above Q5
Domain 3 Manage virtual machines and containers
15% - 20%Handle Hyper-V guest configuration, container creation and orchestration, and Azure Virtual Machines running Windows Server. Practical deployment and lifecycle management of both traditional VMs and modern containerized workloads are tested.
Sample question from this domain above Q7
Domain 4 Implement and manage an on-premises and hybrid networking infrastructure
15% - 20%Design name resolution, IP addressing, and network connectivity across on-premises and hybrid scenarios. This includes DNS, DHCP, VPN, and Azure networking integration for seamless infrastructure.
Domain 5 Manage storage and file services
15% - 20%Configure Azure File Sync, Windows Server file shares, and on-premises storage solutions. Hybrid storage scenarios and cloud-integrated file management are practical skills tested in this domain.
Sample question from this domain above Q8
AZ-800 Exam FAQ
Common questions about the exam itself
What experience do I need before taking AZ-800?
How hard is the AZ-800 exam compared to other Microsoft certifications?
Which domain should I study first for AZ-800?
How long does it realistically take to prepare for AZ-800?
What happens on exam day for AZ-800?
What is the passing score for AZ-800 and how is it calculated?
Can I retake AZ-800 if I fail, and are there any restrictions?
How long does the Windows Server Hybrid Administrator Associate certification stay valid?
What job role does AZ-800 prepare me for?
How does AZ-800 relate to other Microsoft exams like AZ-801 and the newer AZ-802?
Other Microsoft Exams
Free practice questions for more Microsoft certification exams