Key details for this exam, checked against the published exam outline
Each question shows the correct answer and an explanation of why it is right
You have two Azure App Service instances that host the web apps shown the following table.
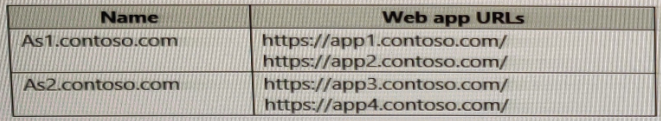
You deploy an Azure application gateway that has one public frontend IP address and two backend pools.
You need to publish all the web apps to the application gateway. Requests must be routed based on the HTTP host headers.
What is the minimum number of listeners and routing rules you should configure? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
The question describes deploying an Application Gateway to route traffic to web apps hosted on two App Service instances based on HTTP host headers, but the specific table showing the web apps is not provided.
To determine the minimum number of listeners and routing rules:
The general principle is: if you have N unique host headers, you need N listeners and N routing rules minimum.
Without seeing the specific web app hostnames in the table, the typical answer for 2 App Service instances with different hostnames would be: 2 listeners and 2 routing rules.
SIMULATION
Task 4
You need to ensure that connections to the storage34280945 storage account can be made by using an IP address in the 10.1.1.0/24 range and the name storage34280945.pnvatelinlcblob.core.windows.net.
Here are the steps and explanations for ensuring that connections to the storage34280945 storage account can be made by using an IP address in the 10.1.1.0/24 range and the name stor-age34280945.pnvatelinlcblob.core.windows.net:
To allow access from a specific IP address range, you need to configure the Azure Storage firewall and virtual network settings for your storage account.You can do this in the Azure portal by selecting your storage account and then selecting Networking under Settings1.
On the Networking page, select Firewalls and virtual networks, and then select Selected networks under Allow access from1. This will block all access to your storage account except from the networks or resources that you specify.
Under Firewall, select Add rule, and then enter 10.1.1.0/24 as the IP address or range.You can also enter an optional rule name and description1. This will allow access from any IP address in the 10.1.1.0/24 range.
Select Save to apply your changes1.
To map a custom domain name to your storage account, you need to create a CNAME record with your domain provider that points to your storage account endpoint2. A CNAME record is a type of DNS record that maps a source domain name to a destination domain name.
Sign in to your domain registrar's website, and then go to the page for managing DNS settings2.
Create a CNAME record with the following information2:
Source domain name: stor-age34280945.pnvatelinlcblob.core.windows.net
Destination domain name: stor-age34280945.pnvatelinlcblob.core.windows.net
Save your changes and wait for the DNS propagation to take effect2.
To register the custom domain name with Azure, you need to go back to the Azure portal and select your storage account.Then select Custom domain under Blob service2.
On the Custom domain page, enter stor-age34280945.pnvatelinlcblob.core.windows.net as the custom domain name and select Save2.
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have an Azure application gateway that has Azure Web Application Firewall (WAF) enabled.
You configure the application gateway to direct traffic to the URL of the application gateway.
You attempt to access the URL and receive an HTTP 403 error. You view the diagnostics log and discover the following error.
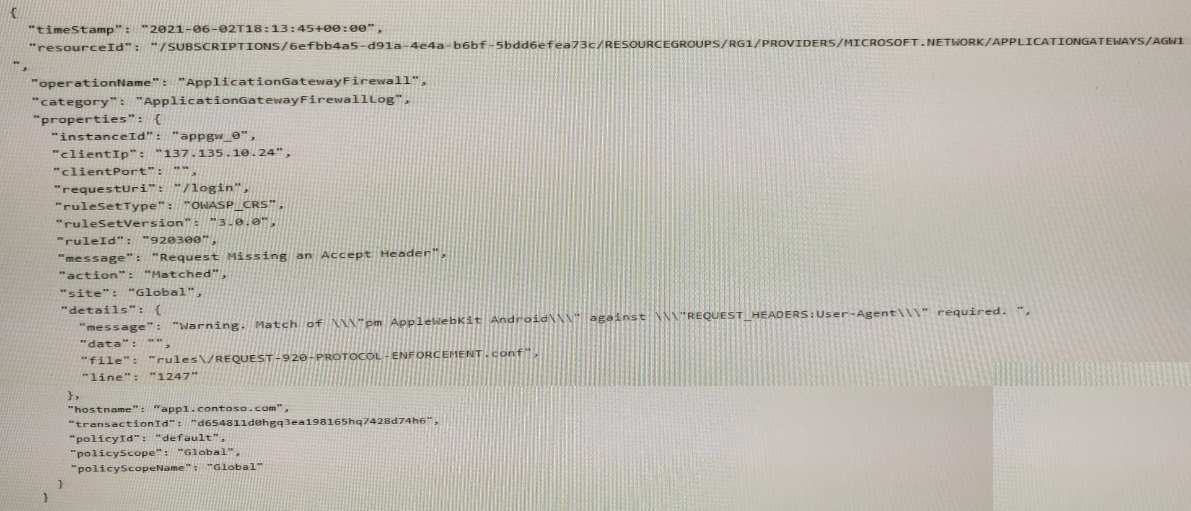
You need to ensure that the URL is accessible through the application gateway.
Solution: You configure a custom cookie and an exclusion rule.
Does this meet the goal?
The question asks if configuring a custom cookie and an exclusion rule meets the goal of making a URL accessible through the application gateway that is receiving an HTTP 403 error due to WAF.
Assessment:
This solution is partially correct but the description is somewhat vague:
The correct answer likely depends on interpretation:
More precise solution: Create a WAF policy exclusion rule that exempts the specific cookie/header/body element triggering the 403 error from WAF rule evaluation.
You have an Azure subscription that contains a virtual network name Vnet1. Vnet1 contains a virtual machine named VM1 and an Azure firewall named FW1.
You have an Azure Firewall Policy named FP1 that is associated to FW1.
You need to ensure that RDP requests to the public IP address of FW1 route to VM1.
What should you configure on FP1?
Answer: Configure a DNAT (Destination Network Address Translation) rule on FP1
Explanation:
What DNAT does:
A DNAT rule translates incoming traffic destined for the firewall's public IP address to an internal IP address of VM1.
Configuration:
How it works:
Why DNAT: DNAT is specifically designed for port forwarding and allowing external access to internal resources. This is the standard method for exposing internal services through a firewall's public IP address.
You are configuring two network virtual appliances (NVAs) in an Azure virtual network. The NVAs will be used to inspect all the traffic within the virtual network.
You need to provide high availability for the NVAs. The solution must minimize administrative effort. What shtraffic ould you include in the solution?
https://docs.microsoft.com/en-us/azure/architecture/reference-architectures/dmz/nva-ha?tabs=cli
SIMULATION
Task 9
You need to ensure that subnet4-3 can accommodate 507 hosts.
Here are the steps and explanations for ensuring that subnet4-3 can accommodate 507 hosts:
To determine the subnet size that can accommodate 507 hosts, you need to use the formula:number of hosts = 2^(32 - n) - 2, wherenis the number of bits in the subnet mask1. You need to find the value ofnthat satisfies this equation for 507 hosts.
To solve this equation, you can use trial and error or a binary search method. For example, you can start withn = 24, which is the default subnet mask for Class C networks. Then, plug in the value ofninto the formula and see if it is too big or too small for 507 hosts.
If you tryn = 24, you getnumber of hosts = 2^(32 - 24) - 2 = 254, which is too small. You need to increase the value ofnto get a larger number of hosts.
If you tryn = 25, you getnumber of hosts = 2^(32 - 25) - 2 = 510, which is just enough to accommodate 507 hosts. You can stop here or try a smaller value ofnto see if it still works.
If you tryn = 26, you getnumber of hosts = 2^(32 - 26) - 2 = 254, which is too small again. You need to decrease the value ofnto get a larger number of hosts.
Therefore, the smallest value ofnthat can accommodate 507 hosts isn = 25.This means that the subnet mask for subnet4-3 should be/25or255.255.255.128in dot-decimal notation1.
To change the subnet mask for subnet4-3, you need to go to the Azure portal and select your virtual network.Then select Subnets under Settings and select subnet4-3 from the list2.
On the Edit subnet page, under Address range (CIDR block), change the value from/24to/25.Then select Save2.
You have the Azure resources shown in the following table.
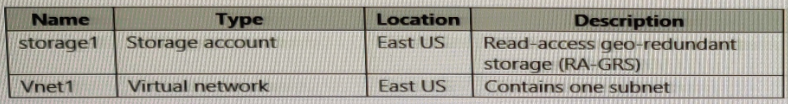
You configure storage1 to provide access to the subnet in Vnet1 by using a service endpoint.
You need to ensure that you can use the service endpoint to connect to the read-only endpoint of storage1 in the paired Azure region.
What should you do first?
Exam domains verified against: Official Microsoft AZ-700 exam guide, last checked October 2026.
This domain covers the foundational networking components you need to build in Azure, including virtual networks, IP addressing, DNS configuration, and the routing that connects everything together. You will work with subnets, public IP prefixes, VNet peering, and Azure's monitoring tools to ensure your network infrastructure is solid and observable.
Sample question from this domain above: Q6
This domain focuses on connecting Azure to on-premises networks and remote users through VPN gateways, ExpressRoute circuits, and Virtual WAN. You need to understand when to use site-to-site VPN versus point-to-site VPN, how to configure ExpressRoute for hybrid scenarios, and how to manage the various peering options and gateway types.
This domain covers the load balancing and application routing services that distribute traffic across your resources. You will implement Azure Load Balancer, Traffic Manager, Application Gateway, and Front Door, configuring rules, health checks, and routing based on the needs of your applications.
This domain addresses how to provide secure, private connectivity to Azure platform services without exposing them to the public internet. You will work with private endpoints, Private Link services, and service endpoints to control access and keep traffic within the Azure network or on-premises.
This domain covers the security controls and policies that protect your Azure networks. You will configure network security groups, application security groups, Azure Firewall, and Web Application Firewall, and use Microsoft Defender for Cloud to identify and resolve security issues in your network design.
Sample question from this domain above: Q4
Common questions about the exam itself

