Key details for this exam, checked against the published exam outline
Each question shows the correct answer and an explanation of why it is right
You have an Azure Automation account that contains a webbook. The webbook is used to configure the application infrastructure of an Azure subscription.
You have a project in Azure DevOps named Project). Project1 contains a repository that stores code for the webbook.
You need to ensure that every committed change to the code will update automatically and publish the webbook to Azure Automation.
What should you configure?
To ensure every committed change to the webhook code automatically updates and publishes the webhook to Azure Automation, you should configure a webhook in your GitHub repository that triggers when code is committed. This webhook should point to an Azure Automation endpoint or trigger an Azure Pipeline that runs a runbook publication script. Alternatively, configure a pipeline trigger that automatically runs when repository code changes, then include a task to publish the runbook to Azure Automation.
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
The lead developer at your company reports that adding new application features takes longer than expected due to a large accumulated technical debt.
You need to recommend changes to reduce the accumulated technical debt.
Solution: You recommend increasing the test coverage.
Does this meet the goal?
Instead reduce the code complexity.
https://dzone.com/articles/fight-through-the-pain-how-to-deal-with-technical
SIMULATION
Your company plans to implement a new compliance strategy that will require all Azure web apps to be backed up every five hours.
You need to back up an Azure web app named az400-11566895-main every five hours to an Azure Storage accountin your resource group.
To complete this task, sign in to the Microsoft Azure portal.
With the storage account ready, you can configure backs up in the web app or App Service.
Open the App Serviceaz400-11566895-main, which you want to protect, in the Azure Portal and browse to Settings > Backups. Click Configure and a Backup Configuration blade should appear.
Select the storage account.
Click + to create a private container. You could name this container after the web app or App Service.
Select the container.
If you want to schedule backups, then set Scheduled Backup to On and configure a schedule: every five hours
Select your retention. Note that 0 means never delete backups.
Decide if at least onebackup should always be retained.
Choose if any connected databases should be included in the web app backup.
Click Save to finalize the backup configuration.
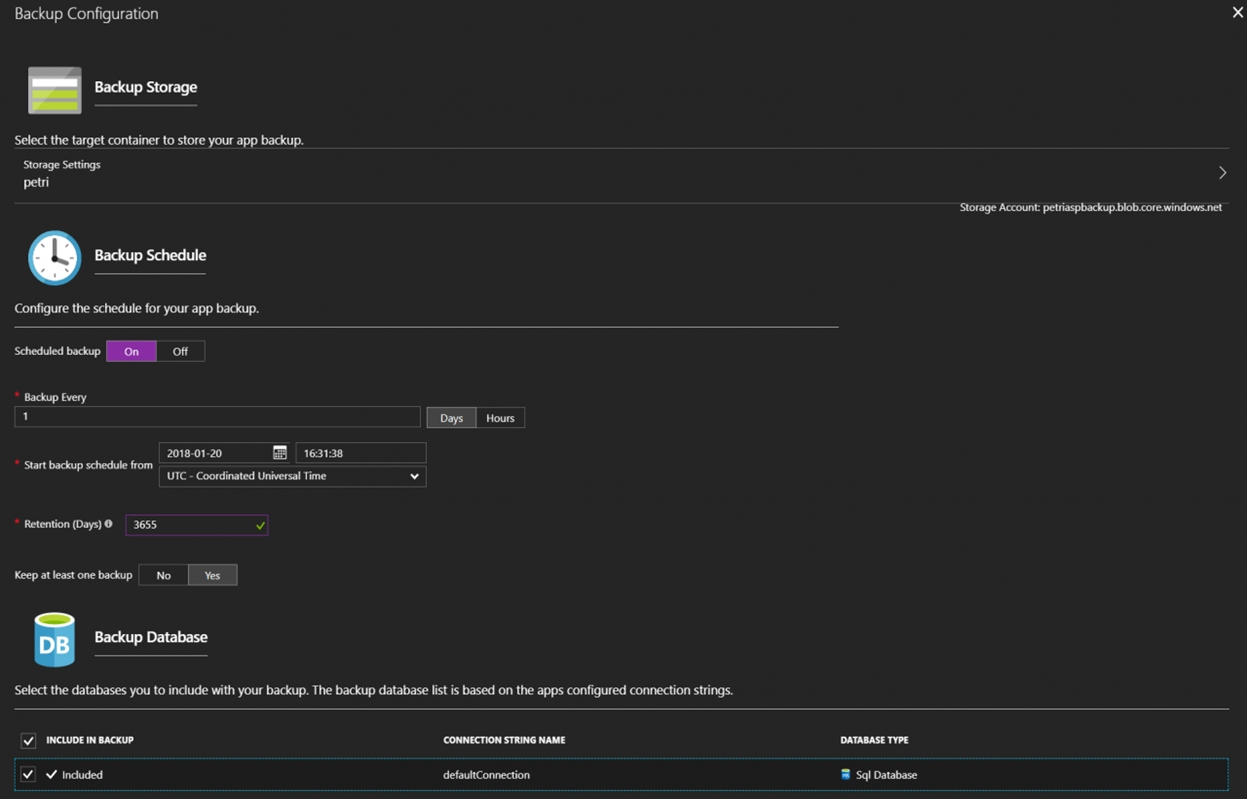
https://petri.com/backing-azure-app-service
You use GitHub Enterprise for source control repositories. The repositories store C# code. You need to enable CodeQL scanning for the repositories. What should you do?
To enable CodeQL scanning for C# code in GitHub Enterprise repositories:
github/codeql-action with C# language specificationYou have an Azure DevOps release pipeline named Pipeline1. You plan to use Pipelinel to deploy infrastructure as code (laC) resources to Azure. You need to create templates to define which resources to deploy. Which template formats should you use?
For deploying Infrastructure as Code (IaC) resources to Azure using an Azure DevOps release pipeline, you should use template formats that Azure natively supports. The correct template formats are: Azure Resource Manager (ARM) templates (JSON format) and Bicep (which is a higher-level language that compiles to ARM templates). These are the official Azure IaC template formats. Terraform could also be used but is not Azure-specific. The question specifically asks for template formats for Azure deployment, so the answers should be ARM templates and/or Bicep templates.
You have an Azure DevOps project named Project! that uses an Azure Pipelines pipeline to build, test, and deploy an app named Appl.
You have a credential named credl.
You need to ensure that credl can be used to deploy builds of Appl to production The solution must ensure that credl is available for use only by specific users and pipelines in Project 1.
What should you do?
To ensure a credential (cred1) can be used to deploy builds to production while restricting access to specific users and pipelines in Project1, you should: (1) Store the credential in Azure DevOps Library (variable groups) with appropriate pipeline permissions, or (2) Use service connections with role-based access control. The best approach is to create a service connection or variable group with restricted authorization that specifies which pipelines and users can access it. Azure DevOps allows you to set pipeline-level permissions on variable groups and service connections to ensure only specific pipelines can use the credential, and only authorized users can manage it.
You plan to publish build artifacts by using an Azure pipeline.
You need to create an. artifactignore file that meets the following requirements:
* Includes all files in the build output folder and all subfolders
* Excludes files that have the .dll extension
What should you include in the file?
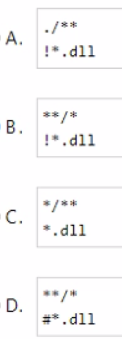
The .artifactignore file uses a gitignore-like syntax. To meet the requirements:
** - Matches all files in the build output folder and all subfolders\n - Line break to separate patterns!**/*.dll - Excludes files with the .dll extension using the negation operator (!)The correct syntax should include all files by default and then exclude .dll files: **\n!**/*.dll
Exam domains verified against: Official Microsoft AZ-400 exam guide, last checked October 2026.
Structure workflow and feedback mechanisms using GitHub Flow, GitHub issues, and Azure Boards. Implement dashboards to track cycle times, lead time, and time to recovery across development, testing, security, and operations metrics. Document projects using wikis and Markdown, automate release notes from Git history, and configure webhooks and integrations with Microsoft Teams.
Choose branching strategies including trunk-based, feature branch, and release branch patterns. Implement pull request workflows with branch policies and protection rules. Manage large files with Git LFS, optimize repositories with Scalar, configure permissions and tags, and recover or remove specific data using Git commands.
Sample question from this domain above: Q7
Select automation solutions like GitHub Actions and Azure Pipelines. Design package feeds, dependency versioning with SemVer and CalVer, and quality gates including security and governance. Build testing strategies with local, unit, integration, and load tests. Develop YAML pipelines with job parallelism, create reusable templates and task groups, implement deployment strategies like blue-green and canary releases, and manage infrastructure as code using Bicep and Azure Resource Manager.
Implement authentication using service principals, managed identities, GitHub Apps, and personal access tokens. Configure secrets management with Azure Key Vault and secretless authentication via workload identity federation. Design scanning strategies for dependencies, code, secrets, and licensing. Integrate GitHub Advanced Security with Microsoft Defender for Cloud and automate container scanning with CodeQL analysis.
Sample question from this domain above: Q3
Configure Azure Monitor, Application Insights, and VM/Container Insights for telemetry collection. Set up GitHub and Azure Pipelines alerting for pipeline events. Analyze performance metrics including CPU, memory, disk, and network indicators. Use Application Insights distributed tracing and Kusto Query Language for log analysis.
Sample question from this domain above: Q4
Common questions about the exam itself

