
Free Logical Operations CFR-210 Exam Practice Questions & Explanations
Prepared & Reviewed by the ValidExamDumps Editorial Team
At ValidExamDumps, we consistently monitor updates to the Logical Operations CFR-210 exam questions by Logical Operations. Whenever our team identifies changes in the exam questions, objectives, focus areas or requirements, We immediately update our exam questions for both PDF and online practice exams. This commitment ensures our customers always have access to the most current and accurate questions. By preparing with these up to date and 100% exam domain coverage questions, our customers can successfully pass the Logical Operations Certified CyberSec First Responder exam on their first attempt without needing additional materials or study guides.
Other certification materials providers often include outdated or removed questions by Logical Operations in their CFR-210 exam. These outdated questions lead to customers failing their Logical Operations Certified CyberSec First Responder exam. In contrast, we ensure our questions bank includes only precise and up-to-date questions. Our main priority is your success in the Logical Operations CFR-210 exam, not profiting from selling obsolete exam questions in PDF or Online Practice Test.
A company website was hacked via the SQL query below:
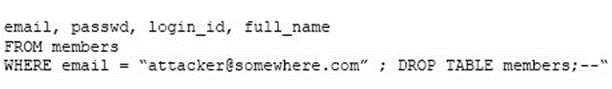
Which of the following did the hackers perform?
Which of the following mitigations will remain intact, regardless of the underlying network protocol?
An incident responder suspects that a host behind a firewall is infected with malware. Which of the following should the responder use to find the IP address of the infected machine?
Which of the following technologies is used as mitigation to XSS attacks?
Organizations should exercise their Incident Response (IR) plan following initial creation. The primary objective for this first IR plan exercise is to identify:
Which of the following describes the MOST important reason for capturing post-attack metadata?
An organization needs to determine of any systems on its network (10.0.25.0/24) have web services running on port 80 or 443. Which of the following is the BEST command to do this?
A security analyst discovers a zero-day vulnerability affecting Windows, which has not been publicly identified. The security analyst assumes this vulnerability is present on millions of computer system and feels an obligation to share this information with other security professionals. Which of the following would be the MOST adverse consequences of the analyst sharing this information?