Key details for this exam, checked against the published exam outline
Each question shows the correct answer and an explanation of why it is right
You are preparing an sFlow monitoring system configuration.
In this scenario, what Information will be included in the datagram sent to the sFlow collector? (Choose two.)
Understanding sFlow Monitoring:
sFlow is a packet sampling technology used to monitor traffic in a network. It sends sampled packet data and interface counters to an sFlow collector, which analyzes the traffic patterns.
Information Included in sFlow Datagram:
Option A: The datagram sent to the sFlow collector includes information about the interface through which the packets entered the agent (the switch or router). This is crucial for understanding where in the network the traffic was captured.
Option D: sFlow datagrams also include the source and destination VLAN for the sampled packets. This allows for detailed analysis of the traffic flow within different VLANs.
Conclusion:
Option A: Correct---The ingress interface is included in the sFlow datagram.
Option D: Correct---The source and destination VLANs are also included, providing context for the sampled traffic.
You are asked for TX and RX traffic statistics for each interface to which an application server is attached. The statistics need to be reported every five seconds. Using the Junos default settings, which telemetry method would accomplish this request?
Telemetry Methods in Junos:
Telemetry is used to collect and report data from network devices. For high-frequency statistics reporting, such as every five seconds, you need a telemetry method that supports this level of granularity and real-time monitoring.
Junos Native Sensors:
Option C: Native Sensors in Junos provide detailed, high-frequency telemetry data, including TX and RX traffic statistics for interfaces. They are designed to offer real-time monitoring with customizable sampling intervals, making them ideal for the five-second reporting requirement.
Conclusion:
Option C: Correct---Native Sensors in Junos are capable of providing the required high-frequency telemetry data every five seconds.
As part of the onboarding process for new switches being added to your data centers, your company uses Juniper Networks' ZTP process. As part of the ZTP process, a script is executed by the devices being onboarded.
Which statement is correct in this scenario?
Zero Touch Provisioning (ZTP):
Juniper Networks' ZTP (Zero Touch Provisioning) process automates the deployment of new devices by allowing them to fetch and execute scripts for configuration and setup as they are powered on and connected to the network.
Supported Scripting Languages:
The Junos OS supports several scripting languages that can be used during the ZTP process:
Shell scripts are often used for general automation tasks.
Python is a widely supported language in Junos, offering powerful scripting capabilities for automating network tasks.
SLAX (Service Logic Execution Environment) is a scripting language specific to Junos, designed to automate configuration tasks and simplify network operations.
Conclusion:
Option D: Correct---Junos ZTP supports Shell, Python, and SLAX, making it the correct choice among the provided options.
Which two statements are true about IP fabrics using unnumbered BGP? (Choose two.)
Understanding Unnumbered BGP:
Unnumbered BGP (Border Gateway Protocol) allows BGP peering between routers without assigning specific IP addresses to the interfaces. Instead, it uses the loopback address or another router identifier for the BGP session, making IP address management more straightforward in large-scale networks.
Family inet Configuration:
Option C: The family inet configuration is required on each interface involved in unnumbered BGP peering to support IPv4 address families. This ensures that IPv4 peering sessions can be established between devices.
Automatic IPv4 Peering:
Option D: Unnumbered BGP peering automatically provisions IPv4 peering sessions. This simplifies the configuration by eliminating the need to manually assign and manage IP addresses for BGP peering.
Conclusion:
Option C: Correct---Unnumbered BGP requires the family inet configuration for IPv4.
Option D: Correct---Unnumbered BGP automatically provisions IPv4 peering, simplifying setup.
You are using a single tenant data center with a bridged overlay architecture. In this scenario, how do hosts of the different virtual networks communicate with each other?
Understanding Bridged Overlay Architecture:
In a single-tenant data center using a bridged overlay architecture, virtual networks (VLANs) are typically isolated within the fabric, with traffic between these VLANs handled outside the fabric.
Communication Between Different Virtual Networks:
A . off-fabric using an external device: This is correct. In many bridged overlay architectures, communication between different virtual networks is handled off-fabric, often using an external router or firewall that connects the different VLANs. The fabric itself primarily provides Layer 2 connectivity within each VLAN, leaving inter-VLAN routing to be handled externally.
Data Center Reference:
This design is common in smaller or simpler data center environments where a single tenant does not require complex on-fabric routing and prefers to handle inter-VLAN routing through dedicated devices.
Exhibit.
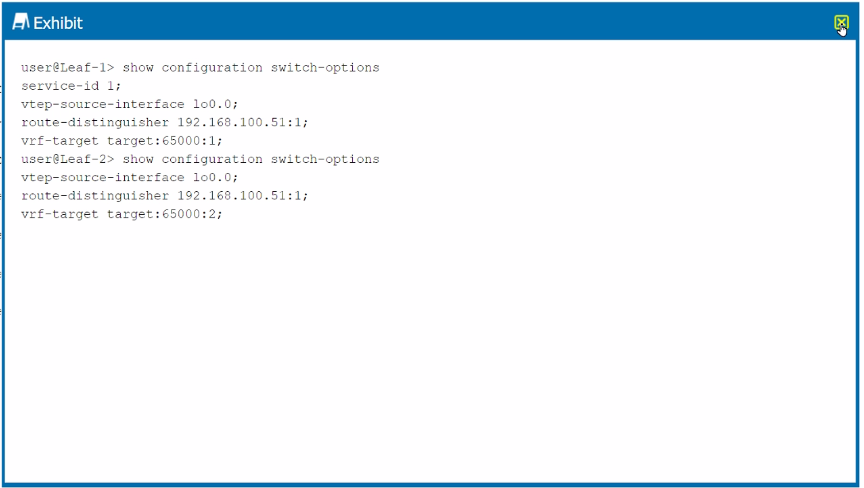
Connections between hosts connected to Leaf-1 and Leaf-2 are not working correctly.
Issue Analysis:
The problem in the exhibit suggests a mismatch in configuration parameters between Leaf-1 and Leaf-2, leading to communication issues between hosts connected to these leaf devices.
Configuration Mismatches:
Service-ID: Leaf-1 has service-id 1 configured, while Leaf-2 does not have this parameter. For consistency and proper operation, the service-id should be the same across both leaf devices.
VRF Target: Leaf-1 is configured with vrf-target target:65000:1, while Leaf-2 is configured with vrf-target target:65000:2. To allow proper VRF import/export between the two leafs, these should match.
Corrective Actions:
C . Configure the set switch-options vrf-target target:65000:1 parameter on Leaf-2: This aligns the VRF targets between the two leaf devices, ensuring they can correctly import and export routes.
E . Configure the set switch-options service-id 1 parameter on Leaf-2: This ensures that both Leaf-1 and Leaf-2 use the same service ID, which is necessary for consistency in the EVPN-VXLAN setup.
Data Center Reference:
Correct configuration of VRF targets and service IDs is critical in EVPN-VXLAN setups to ensure that routes and services are correctly shared and recognized between different devices in the network fabric.
Which two statements are true about EVPN routes for Data Center Interconnect? (Choose two.)
Type 2 EVPN Routes:
Type 2 routes advertise MAC addresses within an EVPN instance and are used primarily for Layer 2 bridging. These routes do not require a VXLAN tunnel to the protocol next hop because they operate within the same Layer 2 domain.
Type 5 EVPN Routes:
Type 5 routes are used to advertise IP prefixes (Layer 3 routes) within EVPN. Similar to Type 2 routes, they do not require a VXLAN tunnel to the protocol next hop because they represent L3 routes, which are managed at the routing layer without the need for VXLAN encapsulation.
Conclusion:
Option B: Correct---Type 2 routes do not need a VXLAN tunnel to the next hop, as they are used for Layer 2.
Option D: Correct---Type 5 routes also do not need a VXLAN tunnel because they operate at Layer 3, handling IP prefixes.
Exam domains verified against: Official Juniper JN0-683 exam guide, last checked October 2026.
Tests knowledge of deployment phase operations including Zero-touch provisioning (ZTP) which automates device setup and configuration without manual intervention. Focuses on concepts and practices used by experienced data center architects and engineers.
Sample question from this domain above: Q1
Assesses understanding of IP-based fabric design and structure that supports scalability and performance in modern data centers. Covers IP fabric architecture and how traffic routing works within the network fabric.
Tests knowledge of VXLAN technology including both control plane mechanisms for device communication setup and data plane operations for actual traffic transmission. Candidates must understand how VXLAN works end to end.
Evaluates understanding of Ethernet VPN architecture with focus on route types and multicast handling. Covers Multiprotocol BGP application, Centralized Routing and Bridging (CRB) and Edge Routing and Bridging (ERB) models, MAC learning and symmetric routing.
Tests knowledge of connecting multiple data centers using Layer 2 and Layer 3 stretching and stitching techniques that join different network fabrics together. Covers EVPN-signaled VXLAN technology enabling communication between interconnected data centers.
Focuses on single-tenant and multitenant data center architectures essential for shared infrastructure environments. Tests knowledge of tenant traffic isolation at both Layer 2 and Layer 3 levels and data center security concepts.
Sample question from this domain above: Q7
Common questions about the exam itself

