
Juniper JN0-650 Practice Exam Questions & Answers
Juniper JN0-650 Exam Details
Key details for this exam, checked against the published exam outline
- Exam Code
- JN0-650
- Full Name
- Enterprise Routing and Switching, Professional
- Issuing Body
- Juniper Networks
- Question Format (Our Bank)
- Multiple Choice
- Delivery
- Pearson VUE (online proctored or test center)
- Eligibility
- JNCIS-ENT (Juniper Networks Certified Specialist - Enterprise Routing and Switching)
- Validity
- 3 years
- Full Question Set
- 72 questions Get All Questions
Free JN0-650 Practice Questions
Each question shows the correct answer and an explanation of why it is right
Question 1 Domain 2 BGP
Which three conditions does the Junos OS use to create a figure-of-merit value for each BGP route in the routing table? (Choose three.)
In Junos OS, the figure-of-merit is an internal numerical value used by the BGP Route Damping mechanism to quantify the stability of a specific BGP route. When a route 'flaps' (becomes unstable), the Junos OS increases this value by assigning a specific penalty based on the type of event that occurred:
The route is withdrawn (Option A): When a BGP neighbor sends a withdrawal message for a prefix, Junos assigns a significant penalty---typically 1,000 by default---to the route's figure-of-merit.
The route is readvertised (Option C): When a previously withdrawn route is announced again by the neighbor, the Junos OS adds another penalty to the figure-of-merit value to track the continued instability.
The route's path attributes changed (Option E): If a route remains reachable but its BGP attributes (such as the AS Path or Community) change, it is considered a flap. Junos assigns a smaller penalty---typically 500 by default---for this attribute change.
As the figure-of-merit accumulates and exceeds a predefined suppress threshold, the route is suppressed and no longer used for forwarding. Over time, the value decreases according to a configured half-life until it falls below a reuse threshold, at which point the route becomes active again. Factors like local preference or the origin (IBGP/EBGP) do not trigger these internal penalty increments for the figure-of-merit.
Question 2 Domain 4 Ethernet Switching and Spanning Tree
You have created a private community VLAN called RND The private community VLAN works fine within switch S1, but traffic in the private RND community VLAN does not reach VLAN members connected to switch S2.
Which statement is correct in this scenario?
Private VLANs (PVLANs) allow for granular port isolation within a single broadcast domain. When extending a PVLAN across multiple switches (S1 to S2), the secondary VLANs (Community or Isolated) must be preserved across the trunk links.
802.1Q Tagging (Option B): For traffic from a Community VLAN (RND) to reach members on a different switch, the Community VLAN must have its own 802.1Q VLAN tag (VLAN ID) associated with it. When a frame from a community port on S1 traverses the trunk to S2, it is tagged with this specific secondary VLAN ID. S2 receives the tagged frame, identifies it as belonging to the RND community, and forwards it to the appropriate community or promiscuous ports.
Why it fails without a tag: If the RND community is only defined locally on S1 without a global VLAN ID, the trunk port will not know how to distinguish that traffic from the Primary VLAN or other communities.
Incorrect Options: Option A is incorrect because the community VLAN must have a different tag than the parent (Primary) VLAN to maintain the internal PVLAN logic. Option C is incorrect because stripping tags would lead to the traffic being merged into the native VLAN or dropped. Option D is incorrect because RND is a community VLAN; changing it to an isolated VLAN would change its behavior (preventing communication between members of that same group).
Question 3 Domain 2 BGP
Your router is discarding an EBGP route because the next hop is not directly connected. Which BGP configuration would you use to override this behavior?
In External BGP (EBGP), there is a default safety mechanism that requires the peer's next hop to be on a directly connected network.
TTL Constraint: By default, EBGP packets are sent with a Time-to-Live (TTL) value of 1. If the next hop is not directly connected (e.g., when peering via loopback interfaces or across a multi-hop path), the packet will expire before reaching the destination, causing the route to be discarded or the session to fail.
The Multihop Solution (Option B): To override this behavior, you must configure the multihop statement under the BGP neighbor or group hierarchy. This allows the BGP session to establish by increasing the TTL (typically to 64 or a user-defined value) and bypasses the 'directly connected' check.
Incorrect Options: Option A (accept-remote-nexthop) is used in internal BGP or specific routing-instance scenarios to resolve next hops that aren't in the local routing table, but it doesn't solve the EBGP TTL/direct-connection requirement. Option C (advertise-inactive) allows BGP to advertise routes that are not the best path in the routing table, which is irrelevant to next-hop reachability. Option D (multipath) is used for load-sharing across multiple paths.
Get the complete JN0-650 question set
$20$40
Question 4 Domain 7 Class of service (CoS)
Exhibit
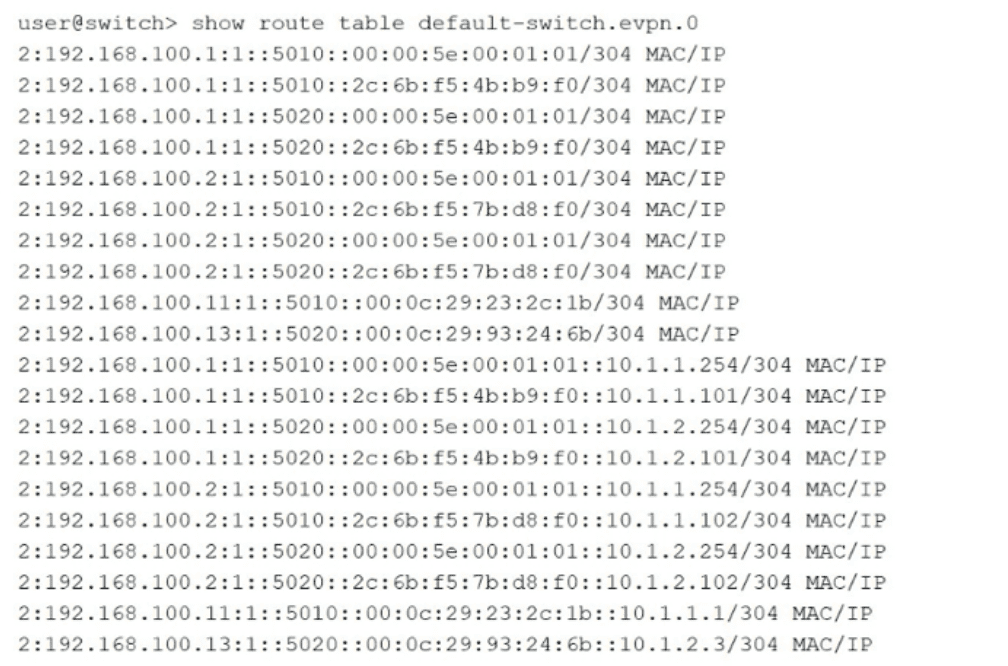
Referring to the exhibit output, which statement is correct?
The exhibit displays the default-switch.evpn.0 routing table, which is used on Juniper leaf devices to store EVPN Type 2 (MAC/IP) routes.
Route Distinguisher (Option C): In EVPN, the Route Distinguisher (RD) is an 8-byte prefix added to a route to make it unique within the BGP control plane. The RD format in the exhibit is <IP-Address>:<Identifier>.
For example, the prefix 2:192.168.100.1:1::5010::... indicates an EVPN Type 2 route (2:) where 192.168.100.1:1 is the Route Distinguisher.
This RD identifies the specific routing instance on the originating VTEP that advertised the MAC/IP address.
Option A is incorrect: The RD 192.168.100.2:1 does not necessarily mean the host device has that IP; it means the originating switch has that router ID/IP used for its RD.
Option B is incorrect: While the RD often incorporates the router ID, the RD itself is the full string (e.g., 192.168.100.1:1), which is distinct from the raw Router ID used in the BGP summary.
Option D is incorrect: Looking at the entries for 10.1.1.1 and 10.1.2.3, they are associated with different identifiers in the RD strings (5010 and 5020 respectively), which typically map to different VNIs or bridge domains.
Question 5 Domain 2 BGP
You configured MVRP in your Layer 2 network and you are adding two new interfaces to your distribution switch. You are asked to ensure that if a rogue device that uses MVRP is connected to these interfaces, that the MVRP PDUs are ignored
In this scenario, what should you configure to accomplish this task?
To secure a Layer 2 network running Multiple VLAN Registration Protocol (MVRP) against unauthorized VLAN propagation from rogue devices, you must control the registration state of the ports.
Forbidden Registration Mode (Option D): This mode is specifically designed to prevent an interface from participating in the MVRP exchange.
When a port is set to forbidden, it will neither register nor declare VLANs (except those statically configured on the interface).
If a rogue device sends MVRP PDUs to this interface, the distribution switch will ignore those PDUs, preventing the rogue device from dynamically creating or learning VLANs through that port.
Registration Hierarchy: In Junos OS 24.4, this is configured at the [edit protocols mvrp interface <interface-name> registration forbidden] level.
Other Modes: normal (default) allows full participation, while restricted ignores joins for VLANs not already statically defined on the switch but still declares its own.
Question 6 Domain 4 Ethernet Switching and Spanning Tree
Exhibit
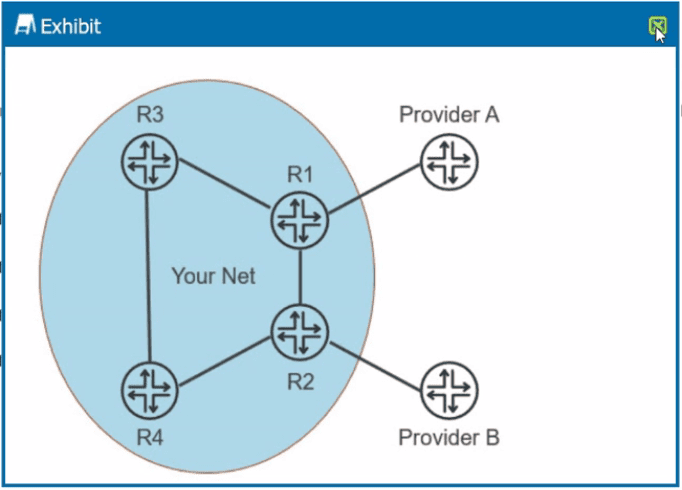
Your network receives the full Internet BGP routing table from two different ISPs. You want your local routers to use Provider A to forward all Internet traffic as long as Provider A is available.
Referring to the exhibit, which two actions would satisfy this requirement? (Choose two.)
In BGP path selection, the Local Preference attribute is one of the most common ways to influence outbound traffic from an Autonomous System (AS). It is a well-known discretionary attribute that is propagated throughout the AS to tell internal routers which path is preferred for a specific destination.
Priority Rule: In the BGP selection algorithm, a higher local preference value is always preferred over a lower one. The default value in Junos OS is 100.
Influencing Outbound Traffic (Option A): To ensure that Provider A is always preferred, you would apply an import policy on R1 (the router connected to Provider A) to set the local preference of all received routes to a value higher than the default (e.g., 200). Since 200 > 100, R3 and R4 will prefer the path via R1.
Alternative Method (Option C): Conversely, you can achieve the same result by applying an import policy on R2 (the router connected to Provider B) to set the local preference to a value lower than the default (e.g., 50). Since the routes from R1 remain at the default of 100, and 100 > 50, the path via R1 (Provider A) is preferred.
Why B and D are incorrect: Setting a higher local preference on R2 (Option B) would make Provider B the preferred exit point. Setting a lower local preference on R1 (Option D) would make Provider A the least preferred exit point.
Question 7 Domain 2 BGP
Your Layer 2 network uses 802.1X to authenticate user devices connecting to the network. You are asked to include a new Layer 2 interface connection from the conference room in your network. You must ensure that only a single device is allowed to authenticate on this port at one time to avoid users from being able to plug in a rogue switch to this port.
In this scenario, which 802.1X method would you use for the new interface?
This question focuses on port security and preventing 'rogue switches' or multiple devices from accessing a single physical port simultaneously.
Single-Secure Supplicant Mode (Option A): This is the most restrictive 802.1X mode in Junos OS. It allows exactly one MAC address to be authenticated on the port at a time. If a device successfully authenticates, the switch will drop any traffic coming from any other MAC address on that same physical interface. If a user tries to plug in a switch, only the first device that authenticates will have access; all other devices behind that switch will be blocked.
Single Supplicant Mode (Option C): This mode allows the first authenticated user to 'open' the port for all other users. This would actually allow a rogue switch to function once the first device is authorized.
Multiple Supplicant Mode (Option B): This allows multiple devices to connect, provided each one authenticates individually. While secure, it does not prevent a user from connecting multiple devices to the port, which violates the requirement to allow only one.
MAC-RADIUS (Option D): This is an authentication method, not a port-access mode that limits the number of supplicants.
Question 8 Domain 5 Layer 2 Authentication and Access Control
You run a multivendor switching environment where you have configured VSTP. You have 450 VLANs and notice that some of your VLANs do not function properly. How should you change the configuration to get all 450 VLANs working?
VSTP (VLAN Spanning Tree Protocol) is Juniper's implementation that provides a separate spanning tree instance for each VLAN, ensuring compatibility with Cisco's PVST+. However, it has significant scaling limitations:
Instance Limits: On many Juniper EX and QFX series switches, VSTP is restricted to a maximum of 253 or 510 VLAN instances depending on the software version (ELS vs. non-ELS). In your scenario, having 450 VLANs exceeds the standard 253-instance limit found on many platforms.
The Solution (Option B): When the number of VLANs exceeds the VSTP capacity, the recommended best practice is to enable RSTP (Rapid Spanning Tree Protocol). Unlike VSTP, RSTP runs a single spanning tree instance for the entire switch, regardless of how many VLANs are configured. This ensures that all 450 VLANs are protected from loops without hitting the hardware's instance-count limit.
Other Options: Option A (force-version) only affects the BPDU format for compatibility but doesn't solve the instance limit. Option C and Option D are parameter tuning actions that do not address the architectural limitation of the number of running instances.
What the Juniper JN0-650 Exam Covers
Exam domains verified against the Official Juniper JN0-650 exam guide, last checked November 2026.
Domain 1 Interior Gateway Protocols (IGPs)
Understand the operation and configuration of OSPF and IS-IS in enterprise networks. Troubleshooting IGPs requires deep knowledge of link-state fundamentals and routing policy application to control protocol behavior across large deployments.
Domain 2 BGP
Master BGP route selection, next hop resolution, and community-based attribute manipulation. Advanced BGP scenarios demand hands-on troubleshooting of path selection issues and policy implementation in multi-AS environments.
Domain 3 IP Multicast
Learn PIM-SM operation, RP election, MSDP, and IGMP configuration from first principles. Many candidates struggle with multicast RPF logic and source-to-RP discovery. practice with live tree state debugging is essential.
Domain 4 Ethernet Switching and Spanning Tree
Configure and monitor advanced VLANs, MSTP or VSTP, and Layer 2 tunneling. Understanding filter-based VLAN binding and Q-in-Q encapsulation requires hands-on lab work beyond reading documentation.
Domain 5 Layer 2 Authentication and Access Control
Implement 802.1x, MAC RADIUS, captive portal, and guest VLAN fallback mechanisms. Real-world scenarios test your ability to diagnose authentication state machine failures and server integration issues.
Sample question from this domain above Q8
Domain 6 IP Telephony Features
Configure Power over Ethernet, LLDP-MED, and voice VLAN to support unified communications deployments. Exam questions test both the configuration commands and the protocol discovery process used by IP phones.
Domain 7 Class of service (CoS)
Design and troubleshoot CoS policies covering classification, queuing, dropping, and shaping across Layer 2 and 3 networks. CoS requires strong understanding of packet header fields and forwarding class manipulation throughout the pipeline.
Sample question from this domain above Q4
Domain 8 EVPN
Deploy VXLAN with EVPN route types and multi-homing in data center or campus fabrics. Configuration scenarios test your ability to integrate EVPN with BGP and validate MAC and IP reachability across VXLAN overlays.
JN0-650 Exam FAQ
Common questions about the exam itself
What is the prerequisite for taking JN0-650?
How difficult is JN0-650 compared to other Juniper exams?
Which topic area on JN0-650 do most candidates find hardest?
How long should I prepare for the JN0-650 exam?
What does the exam day experience involve for JN0-650?
How long does the JN0-650 certification remain valid?
How does JN0-650 relate to other exams in the Enterprise Routing and Switching track?
What job role does JN0-650 map to?
Can I retake JN0-650 if I fail?
Does JN0-650 certification require renewal or ongoing education?
Other Juniper Exams
Free practice questions for more Juniper certification exams