
Free Juniper JN0-636 Exam Practice Questions & Explanations
Prepared & Reviewed by the ValidExamDumps Editorial Team
At ValidExamDumps, we consistently monitor updates to the Juniper JN0-636 exam questions by Juniper. Whenever our team identifies changes in the exam questions, objectives, focus areas or requirements, We immediately update our exam questions for both PDF and online practice exams. This commitment ensures our customers always have access to the most current and accurate questions. By preparing with these up to date and 100% exam domain coverage questions, our customers can successfully pass the Juniper Security, Professional exam on their first attempt without needing additional materials or study guides.
Other certification materials providers often include outdated or removed questions by Juniper in their JN0-636 exam. These outdated questions lead to customers failing their Juniper Security, Professional exam. In contrast, we ensure our questions bank includes only precise and up-to-date questions. Our main priority is your success in the Juniper JN0-636 exam, not profiting from selling obsolete exam questions in PDF or Online Practice Test.
Which method does an SRX Series device in transparent mode use to learn about unknown devices in a network?
The SRX Series device in transparent mode uses packet flooding to learn about unknown devices in a network. Packet flooding is a process wherein the device sends out packets to every device it knows about or suspects in the network. When the packets are returned, the device can identify and classify the unknown devices in the network.
What are two important function of the Juniper Networks ATP appliance solution? (Choose two.).
You are asked to deploy filter-based forwarding on your SRX Series device for incoming traffic sourced from the 10.10 100 0/24 network in this scenario, which three statements are correct? (Choose three.)
set routing-instances <instance-name> instance-type forwarding
set firewall family inet filter <filter-name> term <term-name> from source-address 10.10.100.0/24set firewall family inet filter <filter-name> term <term-name> then routing-instance <instance-name>set interfaces <interface-name> unit <unit-number> family inet filter input <filter-name>
set routing-options rib-groups <rib-group-name> import-rib inet.0set routing-options rib-groups <rib-group-name> import-rib <instance-name>.inet.0set routing-instances <instance-name> routing-options instance-import <rib-group-name>
The following steps are not required or incorrect:
You do not need to create a VRF-type routing instance. A VRF-type routing instance is a type of routing instance that is used for virtual routing and forwarding. It allows you to create multiple logical routers on the same physical device, each with its own interfaces, routing protocols, and routing tables. VRF-type routing instances are typically used for VPNs, MPLS, or network segmentation. However, they are not necessary for FBF, which can be achieved with a forwarding-type routing instance.
You do not need to create and apply a firewall filter that matches on the destination address 10.10.100.0/24 and then sends this traffic to your routing instance. This would be redundant and unnecessary, as the destination address of the incoming traffic is already determined by the routing table of the forwarding-type routing instance. Moreover, this would create a loop, as the traffic would be sent back to the same routing instance that it came from.
Exhibit
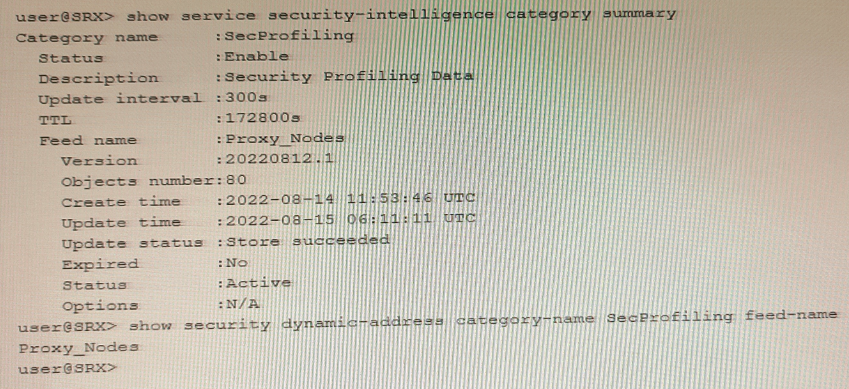
You have recently configured Adaptive Threat Profiling and notice 20 IP address entries in the monitoring section of the Juniper ATP Cloud portal that do not match the number of entries locally on the SRX Series device, as shown in the exhibit.
What is the correct action to solve this problem on the SRX device?
The correct action to solve this problem on the SRX device is to refresh the feed in ATP Cloud. This is because the number of IP address entries in the monitoring section of the Juniper ATP Cloud portal does not match the number of entries locally on the SRX Series device. This discrepancy can be caused by a number of factors, such as the SRX device not being properly configured for Adaptive Threat Profiling, or the feed not being properly downloaded from the Juniper ATP Cloud portal. By refreshing the feed in ATP Cloud, the SRX device can synchronize its local feed with the latest feed from the cloud service and ensure that the entries are consistent and accurate.Reference: Juniper Security, Professional (JNCIP-SEC) Reference Materials source and documents: https://www.juniper.net/documentation/en_US/junos/topics/task/configuration/security-adaptive-threat-profiling-configuring.html
You are asked to deploy Juniper atp appliance in your network. You must ensure that incidents and
alerts are sent to your SIEM.
In this scenario, which logging output format is supported?
D) Binary is a numeric system that uses only two digits: 0 and 1. Binary is not a logging output format for Juniper ATP Appliance or any SIEM platform.
SIEM Syslog, LEEF and CEF Logging