
Free Juniper JN0-335 Exam Practice Questions & Explanations
Prepared & Reviewed by the ValidExamDumps Editorial Team
At ValidExamDumps, we consistently monitor updates to the Juniper JN0-335 exam questions by Juniper. Whenever our team identifies changes in the exam questions, objectives, focus areas or requirements, We immediately update our exam questions for both PDF and online practice exams. This commitment ensures our customers always have access to the most current and accurate questions. By preparing with these up to date and 100% exam domain coverage questions, our customers can successfully pass the Juniper Security, Specialist Exam exam on their first attempt without needing additional materials or study guides.
Other certification materials providers often include outdated or removed questions by Juniper in their JN0-335 exam. These outdated questions lead to customers failing their Juniper Security, Specialist Exam exam. In contrast, we ensure our questions bank includes only precise and up-to-date questions. Our main priority is your success in the Juniper JN0-335 exam, not profiting from selling obsolete exam questions in PDF or Online Practice Test.
How does Juniper ATP Cloud protect a network from zero-day threats?
Juniper ATP Cloud is a cloud-based service that provides advanced threat prevention and detection for your network. It integrates with SRX Series firewalls and MX Series routers to analyze files and network traffic for signs of malicious activity. Juniper ATP Cloud protects a network from zero-day threats by using dynamic analysis, which is a method of executing files in a sandbox environment and observing their behavior and network interactions. Dynamic analysis can uncover unknown malware that may evade static analysis or signature-based detection methods.
How does the SSL proxy detect if encryption is being used?
The SSL proxy can detect if encryption is being used by looking at the destination port number of the packet. If the port number is 443, then the proxy can assume that the packet is being sent over an encrypted connection. If the port number is different, then the proxy can assume that the packet is not encrypted. For more information, please refer to the Juniper Networks JNCIS-SEC Study Guide.
The SSL proxy is a security feature that provides visibility and control over SSL/TLS encrypted traffic. When SSL proxy is enabled, it intercepts SSL/TLS traffic and decrypts it to allow visibility into the content of the encrypted traffic. However, before decrypting the traffic, the SSL proxy must first determine if the traffic is encrypted.
To detect if encryption is being used, the SSL proxy looks at the destination port number. If the destination port number is a known SSL/TLS port (e.g., TCP port 443), the SSL proxy assumes that encryption is being used and intercepts the traffic. If the destination port is not a known SSL/TLS port, the SSL proxy does not intercept the traffic and allows it to pass through the device unmodified.
Click the Exhibit button.
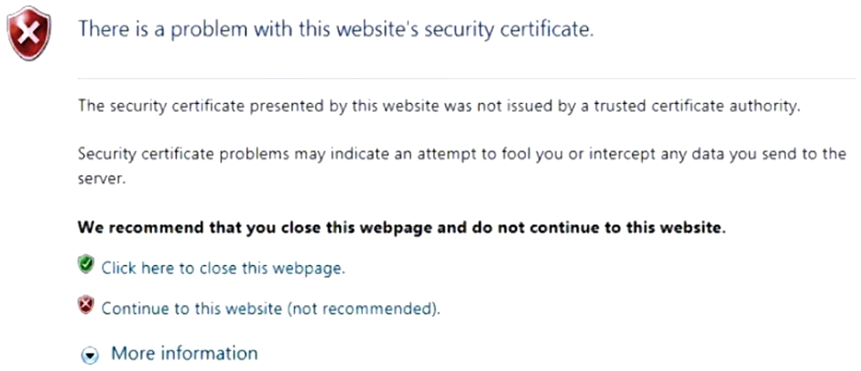
You have implemented SSL client protection proxy. Employees are receiving the error shown in the exhibit.
How do you solve this problem?
A client has attempted communication with a known command-and-control server and it has reached the configured threat level threshold.
Which feed will the clients IP address be automatically added to in this situation?
Which two statements are correct about the Junos IPS feature? (Choose two.)
Junos IPS is a feature that provides intrusion prevention and detection services on SRX Series devices. It monitors network traffic and compares it against predefined signatures or custom rules to identify and block malicious or unwanted packets. Two statements that are correct about the Junos IPS feature are:
IPS is integrated as a security service on SRX Series devices: Junos IPS is not a separate platform or device, but a security service that runs on SRX Series firewalls. It can be enabled and configured as part of the security policy on the SRX Series device and applied to specific zones, interfaces, or traffic flows.
IPS uses protocol anomaly rules to detect unknown attacks: Junos IPS uses two types of rules to detect attacks: signature rules and protocol anomaly rules. Signature rules match traffic against known attack patterns or signatures and block them based on predefined actions. Protocol anomaly rules detect deviations from the expected behavior or structure of common protocols, such as TCP, UDP, ICMP, etc. Protocol anomaly rules can help identify unknown or zero-day attacks that may not have a signature yet.