Key details for this exam, checked against the published exam outline
Each question shows the correct answer and an explanation of why it is right
You configured a tunneled SSID with captive portal and a ClearPass Guest Self Registration workflow when testing and launching the self-registration workflow, after successful registration, the login action shows the following error:
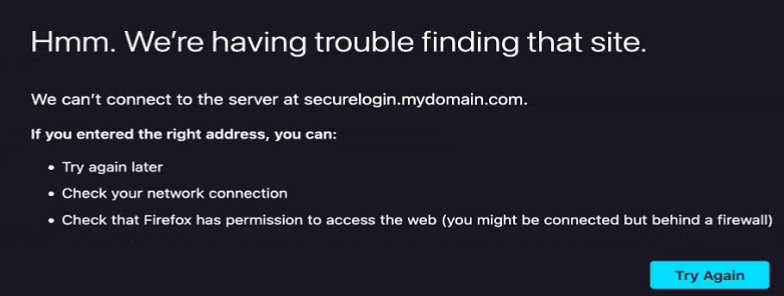
What is the best solution to resolve this error?
Including the root and intermediate certificates in the captive portal certificate for the gateway will resolve the error seen during the login action after successful registration. This is necessary to ensure the SSL/TLS handshake can be completed successfully, as the client browser needs to validate the entire certificate chain.
Exhibit.
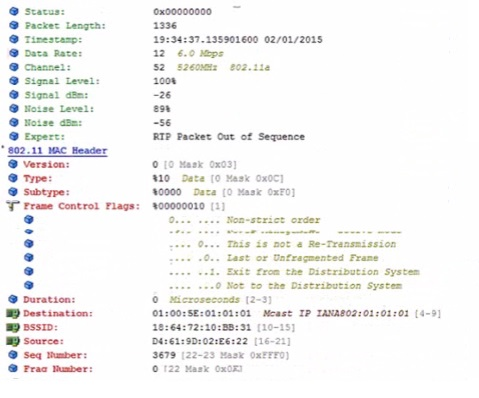
A university runs its own TV station in the city The IT department deploys a multimedia server so the TV productions can be sent out to the entire campus over the IP network using multicast-based communications in order to improve the bandwidth consumption. PlM sparse Mode and IGMP snooping features are enabled.
When wireless users join the multicast groups, all users connected to the same WLAN experience poor network performance. However, wired users are not affected in this way While troubleshooting the network administrator saves the packet captures shown in the exhibit and concludes that all users even those not joining the multicast group, receive the same multicast flow at slow speeds.
Which features should the network administrator enable to fix the problem?
Dynamic Multicast Optimization (DMO) and Multicast Transmission Optimization are features that can help address issues with multicast traffic in wireless environments. DMO optimizes the way multicast traffic is transmitted over the air by converting multicast streams into unicast streams to the clients that need them. This reduces unnecessary traffic for clients that have not subscribed to the multicast group and can improve overall network performance. Multicast Transmission Optimization adjusts the transmission rate of multicast frames to ensure they are sent at optimal speeds, addressing the issue of multicast flow being received at slow speeds by all users.
A Windows device attempts to connect to an 802.1X network but it is not receiving the correct role. TEAP has been configured as the only authentication method in ClearPass. The wireless configuration is correct.
Exhibit.

What is me most likely cause?
The issue likely stems from the Windows device not being configured to use TEAP (Tunneled Extensible Authentication Protocol) as specified in the ClearPass configuration. TEAP is an EAP method that encapsulates an inner EAP method for secure authentication. The Windows device must have TEAP enabled and correctly configured in its network settings to authenticate successfully on the network using ClearPass.
You are testing the use of the automated port-access role configuration process using RadSec authentication over VXLAN. During your testing you observed that the RadSec connection will fan during the digital certificate exchange
What would be the cause of this Issue?
During the testing of RadSec authentication over VXLAN, if the RadSec connection fails during the digital certificate exchange, it typically indicates an issue with the establishment of the TLS tunnel, which is required for RadSec's secure communication. The failure of TLS tunnel establishment can occur due to RADIUS TCP packets being dropped, preventing the secure exchange of digital certificates necessary for RadSec authentication. The other options, such as IPv6 address reachability, tracking mode settings, and proxy server misconfiguration, are not directly related to the failure of the TLS tunnel establishment during the certificate exchange process
An AOS 10 multi-site deployment has sites with AP-only bridged SSlDs and other sites with APs and gateways operating tunneled SSiDs. Client session state sync errors exist between secure lab environments and public -facing areas at several sites.
What is causing the issues?
In a multi-site deployment with a mix of bridged and tunneled SSIDs, if there are session sync errors between different areas, it could be due to connectivity issues with the central management platform, which in the case of Aruba, is likely HPE Aruba Networking Central. This interruption could cause inconsistencies in session states across the network.
Your customer asked for help to apply an ACL for wireless guest users with the following criteria:
* Wi-Fi guests are on VLAN 555
* allow internet access
* only allow access to public DNS servers
* deny access to all internal networks except for any DHCP server
These session ACLs are already present in the CLI of the mobility gateway group:
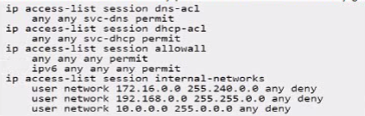
You have access to the CLl. Which user role meets all the criteria?
A)
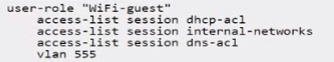
B)
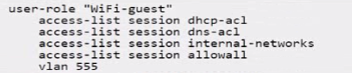
C)
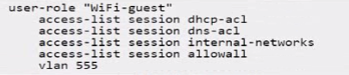
D)
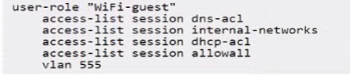
Based on the criteria provided for wireless guest users, the correct user role configuration must allow internet access, only allow access to public DNS servers, deny access to all internal networks except for any DHCP server, and place the Wi-Fi guests on VLAN 555. The ACLs must permit services necessary for basic internet access (such as DNS and DHCP) and block access to internal networks.
Option A satisfies these criteria with the following configurations:
user-role 'WiFi-guest': This defines the role for Wi-Fi guests.
access-list session dhcp-acl: This applies the access list that likely permits DHCP, which is necessary for guests to obtain an IP address.
access-list session dns-acl: This applies the DNS access list, which likely restricts guests to using public DNS servers.
access-list session internal-networks: This applies the internal networks access list, which denies access to internal networks.
vlan 555: This sets the VLAN for Wi-Fi guests to 555.
Options B, C, and D are incorrect because they include access-list session allowall which would permit all traffic, contradicting the requirement to deny access to all internal networks.
Exam domains verified against: Official HP HPE7-A07 exam guide, last checked October 2026.
In this section of the exam, the focus is given to ZTP and OTP, manual provisioning, using Central UI Groups to configure APs, SWs, and GWs in addition to using Sync devices' configuration with Aruba Central.
Configure VSX, MC-LAGs, VLANs, and SVIs to establish core switching infrastructure. Set up ports for AP and gateway connectivity and implement device profiles with MAC and 802.1X authentication methods.
Sample question from this domain above: Q3
Build secure tunnel and mixed mode WLANs to meet specific customer requirements. Classify and limit wireless client traffic, configure gateway clusters with VIP and CoA functionality for advanced network behaviors.
Configure VSX, MC-LAGs, VLANs, and SVIs to establish core switching infrastructure. Set up ports for AP and gateway connectivity and implement device profiles with MAC and 802.1X authentication methods.
Sample question from this domain above: Q5
Monitor wireless networks using UXI and visualize campus topology with Central Sites and Floor plans. Create labels and reports, use the Central REST API for automation, and implement network monitoring strategies.
Resolve authentication issues using Audit Trail and CLI troubleshooting techniques. Fix device connectivity problems to Aruba Central and use both GUI and device CLI for effective issue diagnosis.
Sample question from this domain above: Q4
Implement AAA and WLAN security controls across your infrastructure. Deploy User-Based Tunneling and Network Access Control on campus switches using Aruba User Roles and security policies.
Sample question from this domain above: Q6
Common questions about the exam itself

