
Free HP HPE6-A84 Exam Practice Questions & Explanations
Prepared & Reviewed by the ValidExamDumps Editorial Team
At ValidExamDumps, we consistently monitor updates to the HPE6-A84 exam questions by HP. Whenever our team identifies changes in the exam questions, objectives, focus areas or requirements, We immediately update our exam questions for both PDF and online practice exams. This commitment ensures our customers always have access to the most current and accurate questions. By preparing with these up to date and 100% exam domain coverage questions, our customers can successfully pass the HP Aruba Certified Network Security Expert Written Exam exam on their first attempt without needing additional materials or study guides.
Other certification materials providers often include outdated or removed questions by HP in their HPE6-A84 exam. These outdated questions lead to customers failing their HP Aruba Certified Network Security Expert Written Exam exam. In contrast, we ensure our questions bank includes only precise and up-to-date questions. Our main priority is your success in the HPE6-A84 exam, not profiting from selling obsolete exam questions in PDF or Online Practice Test.
Refer to the scenario.
A customer has an Aruba ClearPass cluster. The customer has AOS-CX switches that implement 802.1X authentication to ClearPass Policy Manager (CPPM).
Switches are using local port-access policies.
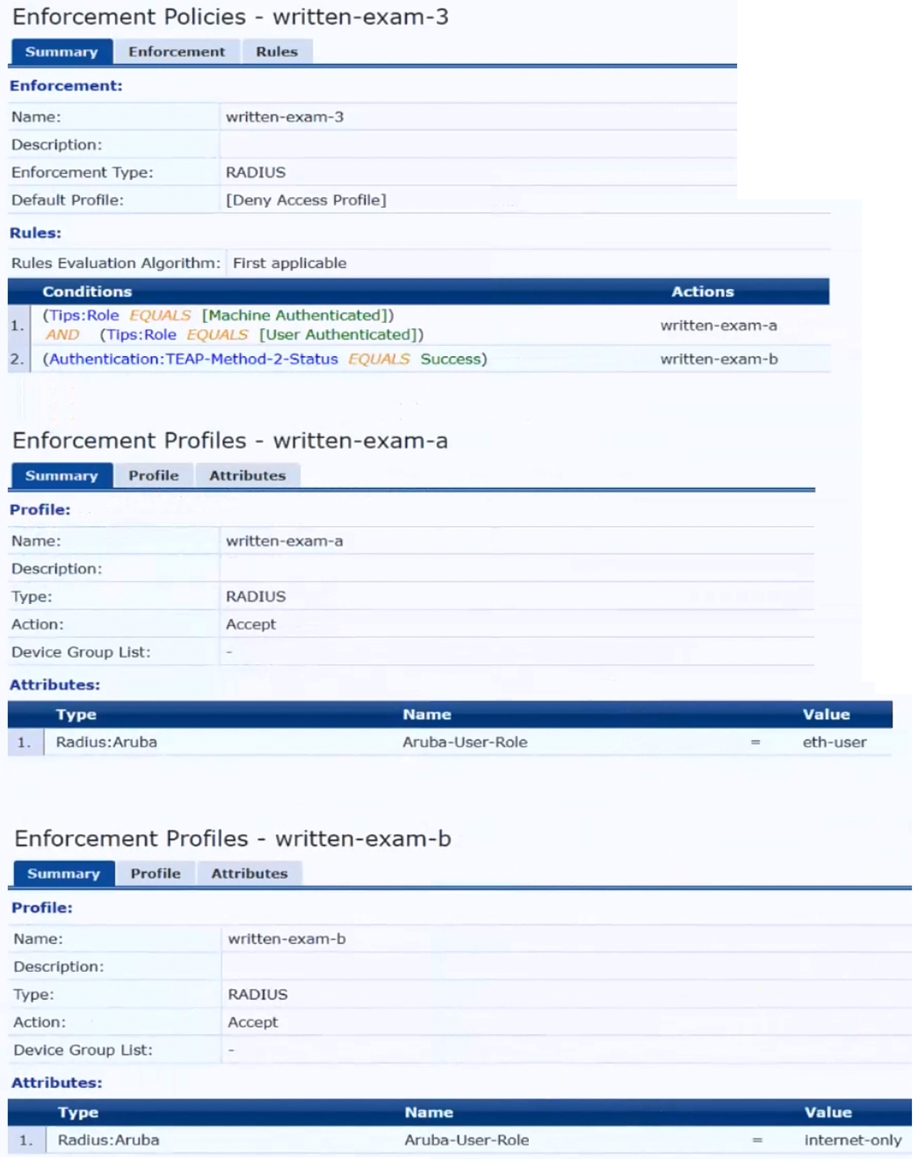
The customer wants to start tunneling wired clients that pass user authentication only to an Aruba gateway cluster. The gateway cluster should assign these clients to the ''eth-internet" role. The gateway should also handle assigning clients to their VLAN, which is VLAN 20.
The plan for the enforcement policy and profiles is shown below:
The gateway cluster has two gateways with these IP addresses:
* Gateway 1
o VLAN 4085 (system IP) = 10.20.4.21
o VLAN 20 (users) = 10.20.20.1
o VLAN 4094 (WAN) = 198.51.100.14
* Gateway 2
o VLAN 4085 (system IP) = 10.20.4.22
o VLAN 20 (users) = 10.20.20.2
o VLAN 4094 (WAN) = 198.51.100.12
* VRRP on VLAN 20 = 10.20.20.254
The customer requires high availability for the tunnels between the switches and the gateway cluster. If one gateway falls, the other gateway should take over its tunnels. Also, the switch should be able to discover the gateway cluster regardless of whether one of the gateways is in the cluster.
Assume that you are using the ''myzone'' name for the UBT zone.
Which is a valid minimal configuration for the AOS-CX port-access roles?
Refer to the scenario.
A customer requires these rights for clients in the ''medical-mobile'' AOS firewall role on Aruba Mobility Controllers (MCs):
External devices should not be permitted to initiate sessions with ''medical-mobile'' clients, only send return traffic.
The exhibits below show the configuration for the role.
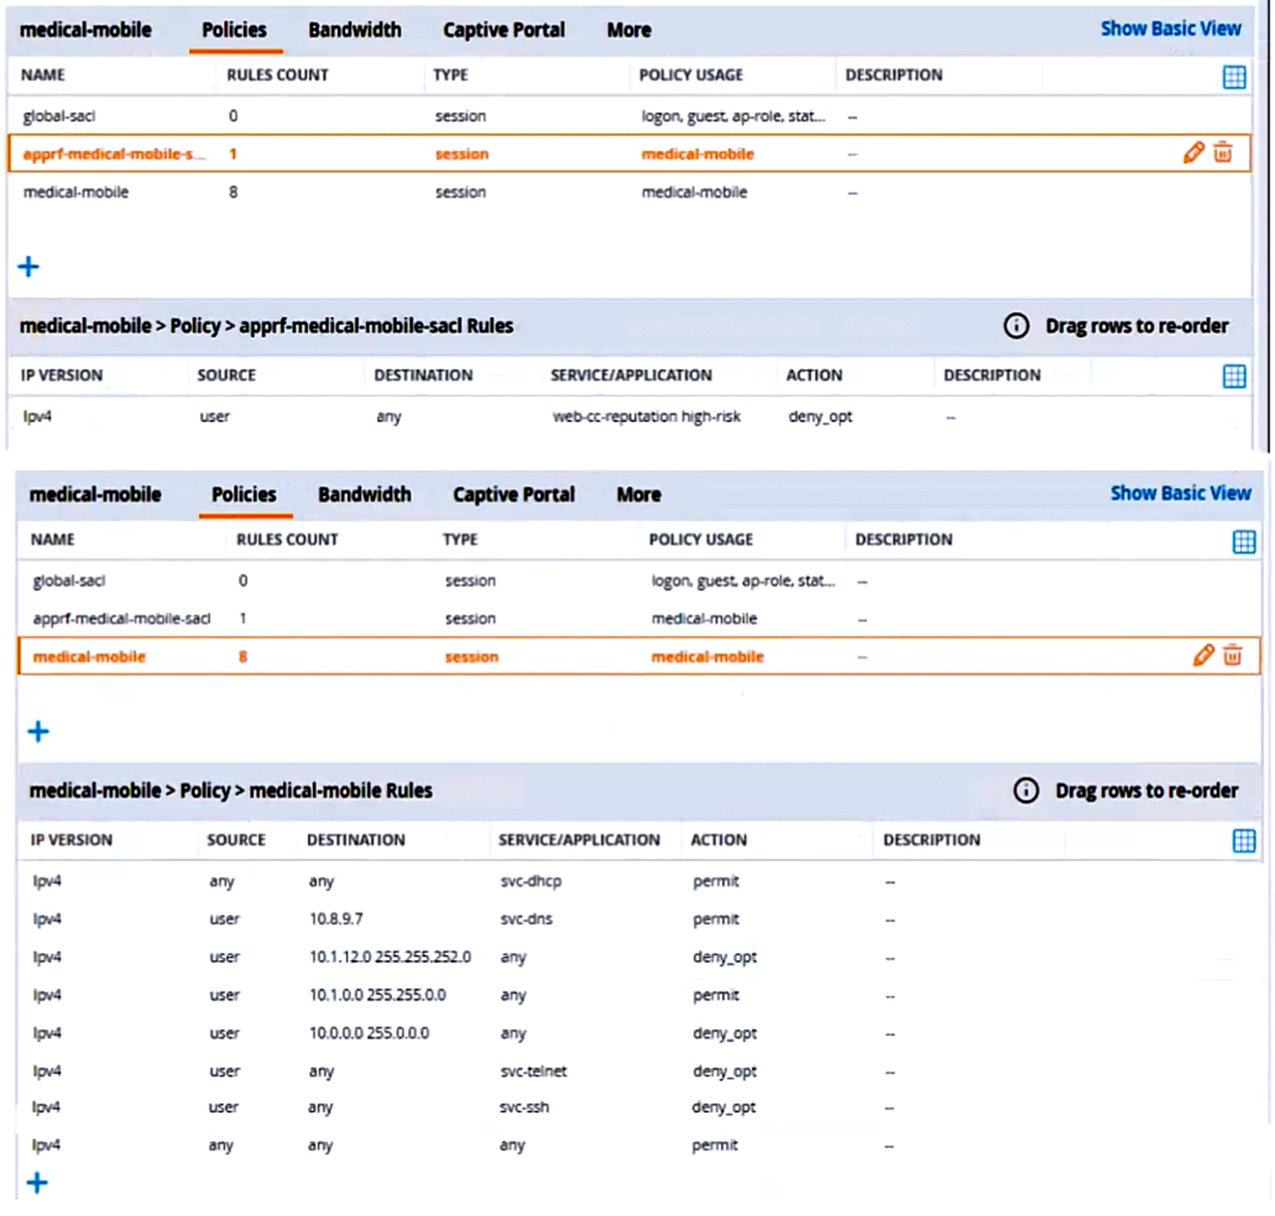
There are multiple issues with this configuration. What is one change you must make to meet the scenario requirements? (In the options, rules in a policy are referenced from top to bottom. For example, ''medical-mobile'' rule 1 is ''ipv4 any any svc-dhcp permit,'' and rule 8 is ''ipv4 any any any permit''.)
Refer to the scenario.
A customer is migrating from on-prem AD to Azure AD as its sole domain solution. The customer also manages both wired and wireless devices with Microsoft Endpoint Manager (Intune).
The customer wants to improve security for the network edge. You are helping the customer design a ClearPass deployment for this purpose. Aruba network devices will authenticate wireless and wired clients to an Aruba ClearPass Policy Manager (CPPM) cluster (which uses version 6.10).
The customer has several requirements for authentication. The clients should only pass EAP-TLS authentication if a query to Azure AD shows that they have accounts in Azure AD. To further refine the clients' privileges, ClearPass also should use information collected by Intune to make access control decisions.
Assume that the Azure AD deployment has the proper prerequisites established.
You are planning the CPPM authentication source that you will reference as the authentication source in 802.1X services.
How should you set up this authentication source?
An authentication source is a configuration element in CPPM that defines how to connect to an external identity provider and retrieve user or device information . CPPM supports various types of authentication sources, such as Active Directory, LDAP, SQL, Kerberos, and HTTP .
To authenticate wireless and wired clients to Azure AD, you need to set up an authentication source as HTTP type, referencing Azure AD's FQDN . This type of authentication source allows CPPM to use REST API calls to communicate with Azure AD and validate the user or device credentials . You also need to configure the OAuth 2.0 settings for the authentication source, such as the client ID, client secret, token URL, and resource URL .
To use information collected by Intune to make access control decisions, you need to set up another authentication source as HTTP type, referencing the Intune extension . This type of authentication source allows CPPM to use REST API calls to communicate with Intune and retrieve the device compliance status . You also need to configure the OAuth 2.0 settings for the authentication source, such as the client ID, client secret, token URL, and resource URL .
Refer to the scenario.
A customer has an Aruba ClearPass cluster. The customer has AOS-CX switches that implement 802.1X authentication to ClearPass Policy Manager (CPPM).
Switches are using local port-access policies.
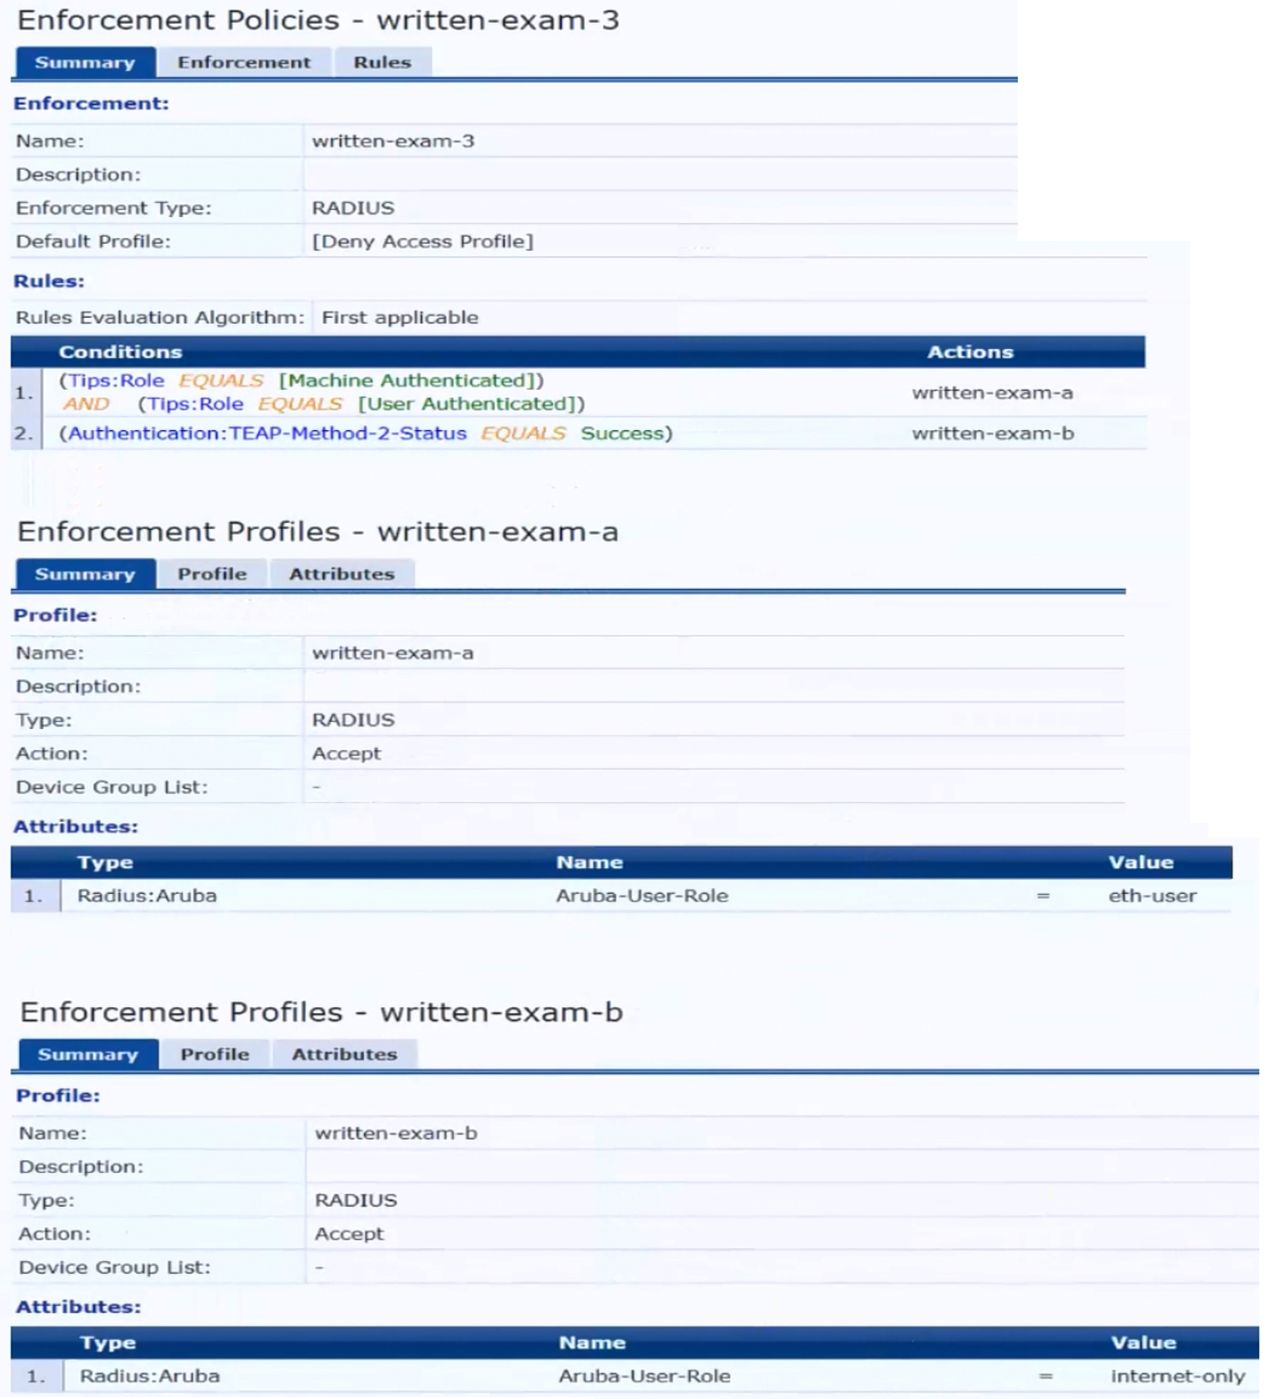
The customer wants to start tunneling wired clients that pass user authentication only to an Aruba gateway cluster. The gateway cluster should assign these clients to the ''eth-internet" role. The gateway should also handle assigning clients to their VLAN, which is VLAN 20.
The plan for the enforcement policy and profiles is shown below:
The gateway cluster has two gateways with these IP addresses:
* Gateway 1
o VLAN 4085 (system IP) = 10.20.4.21
o VLAN 20 (users) = 10.20.20.1
o VLAN 4094 (WAN) = 198.51.100.14
* Gateway 2
o VLAN 4085 (system IP) = 10.20.4.22
o VLAN 20 (users) = 10.20.20.2
o VLAN 4094 (WAN) = 198.51.100.12
* VRRP on VLAN 20 = 10.20.20.254
The customer requires high availability for the tunnels between the switches and the gateway cluster. If one gateway falls, the other gateway should take over its tunnels. Also, the switch should be able to discover the gateway cluster regardless of whether one of the gateways is in the cluster.
You are setting up the UBT zone on an AOS-CX switch.
Which IP addresses should you define in the zone?
You are designing an Aruba ClearPass Policy Manager (CPPM) solution for a customer. You learn that the customer has a Palo Alto firewall that filters traffic between clients in the campus and the data center.
Which integration can you suggest?