
HashiCorp Vault-Associate Practice Exam Questions & Answers
HashiCorp Vault-Associate Exam Details
Key details for this exam, checked against the published exam outline
- Exam Code
- Vault-Associate
- Full Name
- HashiCorp Certified: Vault Associate (002)
- Issuing Body
- HashiCorp
- Question Format (Our Bank)
- Multiple Choice, Hotspot
- Delivery
- Online proctored or at testing facilities
- Eligibility
- Six months of practical Vault experience recommended, though not strictly required
- Full Question Set
- 57 questions Get All Questions
Free Vault-Associate Practice Questions
Each question shows the correct answer and an explanation of why it is right
Question 1 Domain 2 2 Create Vault policies
Which statement describes the results of this command: $ vault secrets enable transit
Question 2 Domain 2 2 Create Vault policies
Which of the following are replication methods available in Vault Enterprise? Choose two correct answers.
The replication methods available in Vault Enterprise are performance replication and disaster recovery replication. These methods allow critical data to be replicated across clusters to support horizontally scaling and disaster recovery workloads.
Performance replication enables a primary cluster to replicate data to one or more secondary clusters, which can handle client requests and improve performance and availability. Performance replication replicates most Vault data, such as secrets, policies, auth methods, and leases, but not tokens. Performance secondaries generate their own tokens and leases, which are not replicated back to the primary. Performance replication also supports filtering, which allows selective replication of data based on namespaces or paths.
Question 3 Domain 6 6 Utilize Vault CLI
When an auth method is disabled all users authenticated via that method lose access.
Get the complete Vault-Associate question set
$20$40
Question 4 Domain 2 2 Create Vault policies
Your DevOps team would like to provision VMs in GCP via a CICD pipeline. They would like to integrate Vault to protect the credentials used by the tool. Which secrets engine would you recommend?
Question 5 Domain 10 10 Explain encryption as a service
The key/value v2 secrets engine is enabled at secret/ See the following policy:
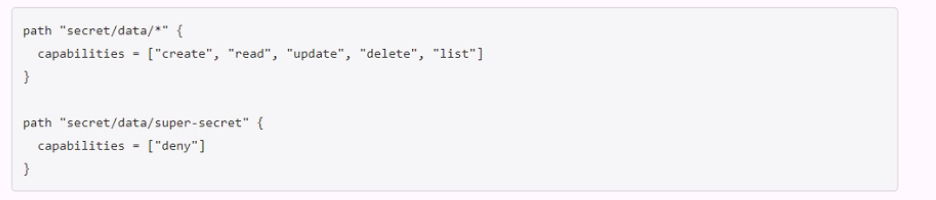
Which of the following operations are permitted by this policy? Choose two correct answers.
The policy shown in the image is:
path ''secret/data/webapp1'' { capabilities = [''create'', ''read'', ''update'', ''delete'', ''list''] }
path ''secret/data/super-secret'' { capabilities = [''deny''] }
This policy grants or denies access to the key/value v2 secrets engine mounted at secret/ according to the following rules:
Question 6 Domain 6 6 Utilize Vault CLI
When using Integrated Storage, which of the following should you do to recover from possible data loss?
Question 7 Domain 9 9 Explain Vault architecture
What can be used to limit the scope of a credential breach?
What the HashiCorp Vault-Associate Exam Covers
Exam domains verified against the Official HashiCorp Vault-Associate exam guide, last checked November 2026.
Domain 1 1 Compare authentication methods
Understand the range of authentication methods Vault supports and make selections that match your use case. Learn to differentiate between human-centric methods like LDAP and GitHub, and machine-oriented methods like AWS IAM and Kubernetes auth. The right auth method determines how identities establish trust with Vault.
Domain 2 2 Create Vault policies
Master Vault's policy language to grant and restrict access to secrets and API endpoints. Policies define what authenticated users can do. Build policies that express your organization's access rules using path-based restrictions and fine-grained capability controls.
Domain 3 3 Assess Vault tokens
Tokens are Vault's core authentication mechanism. Learn the token lifecycle from generation through expiration and revocation. Understand the differences between service tokens for long-lived automation and batch tokens for one-time operations. Master concepts like accessors, time-to-live, and orphaned tokens.
Domain 4 4 Manage Vault leases
Secrets returned by Vault come with a lease that defines how long they are valid. You must be able to renew leases to extend validity and revoke them when they are no longer needed. Lease IDs uniquely identify each secret instance and track its lifecycle.
Domain 5 5 Compare and configure Vault secrets engines
Secrets engines are Vault's plugins for managing different types of secrets. Learn to choose between dynamic secrets that Vault generates on-the-fly and static secrets stored directly. The transit engine provides encryption as a service. Each engine solves different secrets management problems.
Domain 6 6 Utilize Vault CLI
The command-line interface is how operators interact with Vault in scripts and automation. You must be able to authenticate, configure auth methods and policies, enable secret engines, retrieve secrets, and set environment variables. The CLI mirrors the capabilities of the Vault API.
Domain 7 7 Utilize Vault UI
The web interface provides a graphical way to interact with Vault for authentication, configuration, and secret access. The UI is useful for exploration and administration tasks. You need to be comfortable performing the same operations you can do from the CLI, but through the browser interface.
Domain 8 8 Be aware of the Vault API
Vault's REST API is the foundation that both the CLI and UI use. You should understand how to authenticate and retrieve secrets using HTTP clients like Curl. The API is language-agnostic and powers integrations with other tools.
Domain 9 9 Explain Vault architecture
Understand how Vault works internally from encryption at rest to the high-availability cluster topology. Learn about storage backends, the Vault agent for client-side integration, secrets caching, seal and unseal mechanisms, identity and group management, Shamir secret sharing, replication, response wrapping, and why short-lived dynamic secrets are valuable.
Sample question from this domain above Q7
Domain 10 10 Explain encryption as a service
The transit secret engine provides encryption, decryption, and key rotation without your applications ever seeing the key material. You configure the transit engine, then use Vault to encrypt data at rest and decrypt it on retrieval. This pattern lets your applications stay encryption-aware without managing keys directly.
Sample question from this domain above Q5
Vault-Associate Exam FAQ
Common questions about the exam itself
How much hands-on Vault experience do I need before taking the Vault Associate exam?
How long is the Vault Associate exam and how many questions does it have?
What is the passing score for Vault Associate?
Is the Vault Associate certification hard to pass and why?
How long does it typically take to prepare for the Vault Associate exam?
Can I take the Vault Associate exam online or do I have to go to a test center?
How long is the Vault Associate certification valid after I pass?
What job roles are a good fit for the Vault Associate certification?
What comes after Vault Associate in the HashiCorp certification path?
Are there any prerequisites or prior certifications I need before taking Vault Associate?
Other HashiCorp Exams
Free practice questions for more HashiCorp certification exams