At ValidExamDumps, we consistently monitor updates to the Google Professional-Cloud-Network-Engineer exam questions by Google. Whenever our team identifies changes in the exam questions, objectives, focus areas or requirements, We immediately update our exam questions for both PDF and online practice exams. This commitment ensures our customers always have access to the most current and accurate questions. By preparing with these up to date and 100% exam domain coverage questions, our customers can successfully pass the Google Professional Cloud Network Engineer exam on their first attempt without needing additional materials or study guides.
Other certification materials providers often include outdated or removed questions by Google in their Professional-Cloud-Network-Engineer exam. These outdated questions lead to customers failing their Google Professional Cloud Network Engineer exam. In contrast, we ensure our questions bank includes only precise and up-to-date questions. Our main priority is your success in the Google Professional-Cloud-Network-Engineer exam, not profiting from selling obsolete exam questions in PDF or Online Practice Test.
Your company recently migrated to Google Cloud in a Single region. You configured separate Virtual Private Cloud (VPC) networks for two departments. Department A and Department B. Department A has requested access to resources that are part Of Department Bis VPC. You need to configure the traffic from private IP addresses to flow between the VPCs using multi-NIC virtual machines (VMS) to meet security requirements Your configuration also must
* Support both TCP and UDP protocols
* Provide fully automated failover
* Include health-checks
Require minimal manual Intervention In the client VMS
Which approach should you take?
The correct answer is D. Create an instance template and a managed instance group. Configure two separate internal TCP/UDP load balancers for each protocol (TCP/UDP), and configure the client VMs to use the internal load balancers' virtual IP addresses.
This answer is based on the following facts:
The other options are not correct because:
Option A is not suitable. Creating the VMs in the same zone does not provide high availability or failover. Using static routes with IP addresses as next hops requires manual intervention when NVAs are added or removed.
Option B is not optimal. Creating the VMs in different zones provides high availability, but not failover. Using static routes with instance names as next hops requires manual intervention when NVAs are added or removed.
Option C is not feasible. Creating an instance template and a managed instance group provides high availability and reliability, but using a single internal load balancer does not support both TCP and UDP protocols. You cannot define a custom static route with an internal load balancer as the next hop.
Your organization recently exposed a set of services through a global external Application Load Balancer. After conducting some testing, you observed that responses would intermittently yield a non-HTTP 200 response. You need to identify the error. What should you do? (Choose 2 answers)
To identify errors with intermittent non-HTTP 200 responses:
Enable and review health check logs for your backend to identify potential issues with backend availability or connectivity (Option B).
Enable logging on the load balancer and review Cloud Logging, particularly the statusDetails field, to gather insights on error types and sources (Option C).
These steps allow for precise error identification by leveraging both health checks and detailed logging features available through Google Cloud's external load balancer diagnostics.
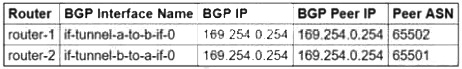
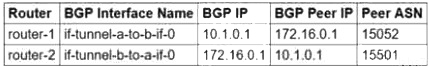
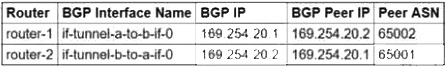
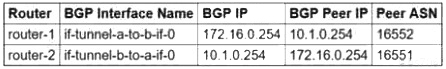
You need to configure the Border Gateway Protocol (BGP) session for a VPN tunnel you just created between two Google Cloud VPCs, 10.1.0.0/16 and 172.16.0.0/16. You have a Cloud Router (router-1) in the 10.1.0.0/16 network and a second Cloud Router (router-2) in the 172.16.0.0/16 network. Which configuration should you use for the BGP session?
A.
B.
C.
D.
You created a new VPC for your development team. You want to allow access to the resources in this VPC via SSH only.
How should you configure your firewall rules?
Your organization has a single project that contains multiple Virtual Private Clouds (VPCs). You need to secure API access to your Cloud Storage buckets and BigQuery datasets by allowing API access only from resources in your corporate public networks. What should you do?

