
GIAC GCFR Practice Exam Questions & Answers

7 Free Questions Last reviewed October 27, 2026 Prepared & Reviewed by the ValidExamDumps Editorial Team

82 Practice Questions (Our Bank)
180 minutes Exam Duration
62% Passing Score
USD 949-999 Official Exam Fee
Exam Facts

GIAC GCFR Exam Details

Key details for this exam, checked against the published exam outline

Exam Code
GCFR
Full Name
GIAC Cloud Forensics Responder Exam
Issuing Body
GIAC (Global Information Assurance Certification)
Question Format (Our Bank)
Multiple Choice
Delivery
Online proctored via ProctorU or at PearsonVUE test centre
Validity
4 years
Practice Questions

Free GCFR Practice Questions

Each question shows the correct answer and an explanation of why it is right

VA
ValidExamDumps Editorial Team Every question and its answer is checked by our GCFR exam preparation team, who also write the explanation shown with each one. How we research and review these pages

Question 1 Domain 1 AWS Cloud Platform Logging

In Azure, which of the following describes a "Contributor"?

Correct Answer A
Explanation VPC Flow Log is a logging feature specific to AWS virtual private clouds that captures network traffic information. The question asks you to identify a log type from a snippet, which requires knowledge of AWS logging services and their formats. Understanding what VPC Flow Logs contain and how they appear is essential for forensic analysis of AWS network activity and security investigation within AWS environments.

Question 2 Domain 11 In-Cloud Investigations

The Azure URI for the Develop VM is shown below. What will change in the notation when referencing the VM's OS disk?
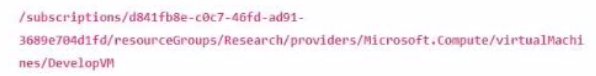
Question 2 exhibit

Correct Answer A
Explanation When you analyze a snapshot outside of AWS, you must first download it from the cloud to your local system or forensic workstation. This download process can take a very long time depending on the snapshot size and your network bandwidth. Other options might suggest technical limitations that do not actually apply to external snapshot analysis. The time factor is a real operational drawback when conducting investigations outside the cloud environment.

Question 3 Domain 4 Azure & M365 Structure and Access Methods

The Azure PowerShell output below is an example of which of the following?
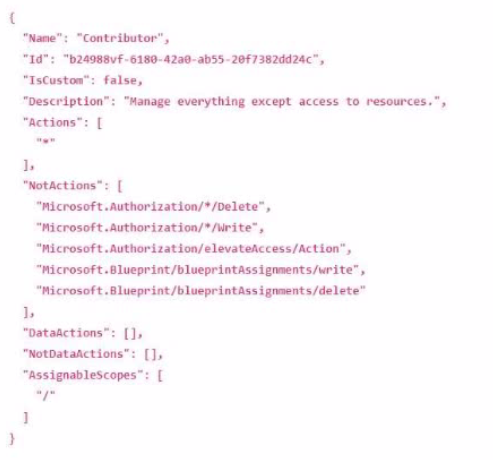
Question 3 exhibit

Correct Answer B
Explanation After registering an application in Azure AD, the next step to use Microsoft Graph API is to configure app permissions. These permissions define what resources and data the application can access through the API. Without proper permission configuration, the application cannot make authorized calls to Graph API even though it is registered. The correct answer reflects the logical sequence in the Azure application setup process for API access.

Get the complete GCFR question set $20$40

Get Full Access

Question 4 Domain 6 Cloud Storage Platforms

What Amazon EC2 instance prefix should be monitored to detect potential crypto mining?

Correct Answer B
Explanation In AWS S3 Server Access Logs, the first field identifies the request ID, which is a unique identifier assigned to each request made to the bucket. This request ID appears at the start of each log record and helps track individual operations. Understanding S3 log format is important for forensic investigations because it allows you to correlate specific requests with their outcomes. The request ID makes it possible to follow the chain of events in storage access investigations.

Question 5 Domain 3 Azure & M365 Cloud Platform Logging

An organization has optimized their S3 buckets to quick an their data collection across a global infrastructure. Which reflects the bucket URL root?

Correct Answer A
Explanation Logic Apps is an Azure SaaS solution that automates workflows without requiring you to write traditional code. It uses a visual designer and pre-built connectors to execute business processes. Other Azure options like Functions require code development, while Logic Apps focuses on workflow automation through configuration. This distinction is important for understanding what tools are available in Azure for different types of automation and investigation tasks.

Question 6 Domain 2 AWS Structure and Access Methods

An engineer has set up log forwarding for a new data source and wants to use that data to run reports and create dashboards in Kiban

a. What needs to be created in order to properly handle these logs?

Correct Answer B
Explanation IAM policies are JSON-formatted documents that define permissions and access control in AWS. These policies specify which actions are allowed or denied on which resources for specific principals. Understanding IAM policy structure is fundamental to cloud forensics because access controls determine who can perform what actions. Analyzing policies helps investigators understand the security posture and identify potential unauthorized access or privilege escalation in AWS environments.

Question 7 Domain 8 Cloud-based Attacks

What is the maximum file size for Azure Page Blob storage?

Correct Answer C
Explanation The screenshot shows MITRE ATT&CK tactics, which is a framework documenting adversary tactics and techniques based on real-world observations. MITRE ATT&CK helps security teams understand how attackers operate across different stages of an attack. This framework is directly relevant to cloud forensics because cloud-based attacks follow these documented patterns and tactics. Understanding MITRE ATT&CK allows investigators to classify observed attack behaviors and understand attacker methodology in cloud environments.
Study Guide

What the GIAC GCFR Exam Covers

Exam domains verified against the Official GIAC GCFR exam guide, last checked October 2026.

Domain 1 AWS Cloud Platform Logging

Master the generation, collection, retention, and storage of logs in AWS. Develop insights into AWS log management for effective monitoring and security analysis.

Sample question from this domain above Q1

Domain 2 AWS Structure and Access Methods

Explore AWS architectures, logging capabilities, data access patterns, and investigative possibilities. Understand the structural elements that support forensic analysis.

Sample question from this domain above Q6

Domain 3 Azure & M365 Cloud Platform Logging

Understand log generation, collection, retention, and storage in Azure and M365. Focus on effective log management for monitoring and forensic analysis.

Sample question from this domain above Q5

Domain 4 Azure & M365 Structure and Access Methods

Explore Azure and M365 architectures, logging systems, data access, and investigative possibilities. Master structural and access-related elements of these platforms.

Sample question from this domain above Q3

Domain 5 Cloud Forensic Artifact Techniques

Learn about services, tools, and resources available for cloud forensic investigations. Understand techniques used to assist and automate forensic processes in cloud environments.

Domain 6 Cloud Storage Platforms

Understand different cloud storage resource types and their characteristics. Learn how to create, secure, access, and use storage resources for forensic investigations.

Sample question from this domain above Q4

Domain 7 Cloud Virtual Machine Architecture

Learn the types, configurations, and availability options of virtual machines across cloud platforms. Understand VM management and how to investigate VM-related security incidents.

Domain 8 Cloud-based Attacks

Study tactics and techniques used to attack cloud provider computing resources. Understand the strategies and methods employed in cloud-based cyber attacks.

Sample question from this domain above Q7

Domain 9 GCP and Google Workspace Cloud Platform Logging

Understand log generation, collection, retention, and storage in GCP and Google Workspace. Learn effective log management techniques for incident response.

Domain 10 GCP and Google Workspace Structure and Access Methods

Learn the architectures, logging systems, data access patterns, and investigative options in GCP and Google Workspace. Understand how to navigate these environments for forensic work.

Domain 11 In-Cloud Investigations

Master the collection of forensic images and extraction of data from cloud resources. Learn techniques for conducting thorough investigations within cloud environments.

Sample question from this domain above Q2

Domain 12 Introduction to Enterprise Cloud Digital Forensics and Incident Response

Understand popular cloud concepts and key resources used in forensic investigations. Learn how logs facilitate incident response and forensic analysis in enterprise cloud environments.

Domain 13 Multi-Cloud Virtual Networking

Master each cloud provider's networking topology and resource grouping. Learn to inspect and control network traffic across multi-cloud environments.

FAQ

GCFR Exam FAQ

Common questions about the exam itself

What makes GCFR harder than other forensics certifications?
GCFR is the first certification that tests your ability to respond and investigate across all three major cloud providers in a single exam. You need to understand how logs work differently in AWS, Azure, GCP and Google Workspace, then use that knowledge in performance-based CyberLive scenarios rather than just answering multiple-choice questions. This hands-on, multi-cloud approach is what makes it rigorous.
What background do I need before attempting GCFR?
GIAC does not publish official prerequisites, but candidates should have practical experience with at least one major cloud platform and understand basic incident response concepts. Many candidates come from cloud security or traditional forensics roles, but the exam assumes you can already navigate cloud environments and interpret technical logs.
How long does realistic GCFR preparation take?
Most candidates spend 100 to 150 hours preparing, depending on their prior cloud and forensics experience. If you already work with cloud platforms daily, you might need less time. If cloud is new to you, expect to spend time building hands-on lab experience across all three providers.
What is the CyberLive format and how does it change exam day?
Instead of only multiple-choice questions, CyberLive presents performance-based challenges where you perform real forensic tasks in a virtual machine environment. You interact with actual cloud logs, command-line tools, and interfaces to solve incident scenarios. You have 180 minutes total for all questions and tasks combined.
Which GCFR objective area do most candidates struggle with?
Multi-cloud virtual networking and the GCP objective areas tend to be challenging because many candidates have deeper AWS or Azure experience. The distributed logging and networking concepts in GCP operate differently from AWS, so candidates with uneven cloud experience should invest extra lab time there.
What are the GCFR retake and rescheduling rules?
You have 120 days from activation to schedule and sit your exam. If you fail, there is a 30-day waiting period before you can retake. A retake costs USD 879. You can reschedule your exam before your attempt date, and missing a proctored appointment incurs a USD 175 reseating fee plus a 7-day deadline extension.
How long does the GCFR certification stay valid and what renewal costs?
Your GCFR credential is valid for four years. To renew, you pay USD 499 and either retake the exam or earn Continuing Professional Education credits. If you renew multiple certifications within two years, additional renewals within that period cost USD 249 each instead of USD 499.
What job roles does GCFR prepare me for?
GCFR is designed for cloud incident responders, cloud forensics analysts, and security incident handlers who work across multiple cloud platforms. It validates your ability to investigate security incidents in AWS, Azure, and Google Cloud environments, making you qualified for roles focused on post-incident analysis and root cause investigation in enterprise cloud settings.
How does GCFR fit into the broader GIAC forensics track?
GCFR is a practitioner-level certification that complements traditional forensics certs like GCFE and GCFA by adding specialized cloud expertise. Once you earn GCFR, you can stack it toward higher GIAC credentials like GSP or GSE. It fills a gap in forensics training by focusing specifically on what happens after a cloud incident occurs rather than cloud security configuration.

Other GIAC Exams

Free practice questions for more GIAC certification exams

All GIAC exams