Fortinet NSE8_812 Practice Exam Questions & Answers
7 Free Questions
· Last reviewed: October 13, 2026
· Prepared & Reviewed by the ValidExamDumps Editorial Team
Exam Facts
Fortinet NSE8_812 Exam Details
Key details for this exam, checked against the published exam outline
105
Practice Questions (Our Bank)
120 minutes
Exam Duration
70%
Passing Score
USD 400
Official Exam Fee
- Exam Code
- NSE8_812
- Full Name
- Fortinet NSE 8 - Network Security Expert 8 Written Exam
- Issuing Body
- Fortinet
- Question Format (Our Bank)
- Multiple Choice
- Delivery
- Online proctored at Pearson VUE
- Eligibility
- No formal prerequisites, but industry experience is expected
- Validity
- 2 years
Practice Questions
Free NSE8_812 Practice Questions
Each question shows the correct answer and an explanation of why it is right
VA
ValidExamDumps Editorial Team
Every question and its answer is checked by our NSE8_812 exam
preparation team, who also write the explanation shown with each one.
How we research and review these pages
Refer to the exhibit.
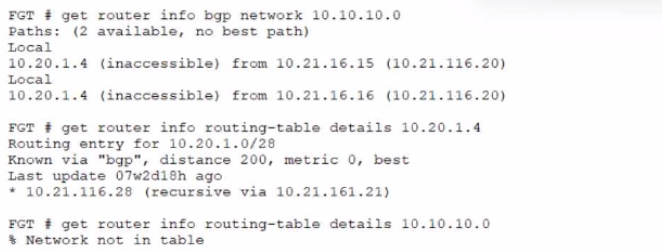
A customer reports that they are not able to reach subnet 10.10.10.0/24 from their FortiGate device.
Based on the exhibit, what should you do to correct the situation?
Correct Answer:
C
Explanation
When a BGP neighbor cannot reach a subnet, the next-hop-self feature needs to be enabled so that the FortiGate advertises itself as the next hop for routes it sends to BGP peers. Without this feature, the device forwards the original next hop address, which may not be reachable from the receiving peer. This is a common issue in hub-and-spoke BGP topologies where the spoke cannot reach the original next hop address advertised by a route reflector or hub.
Refer to the exhibit.
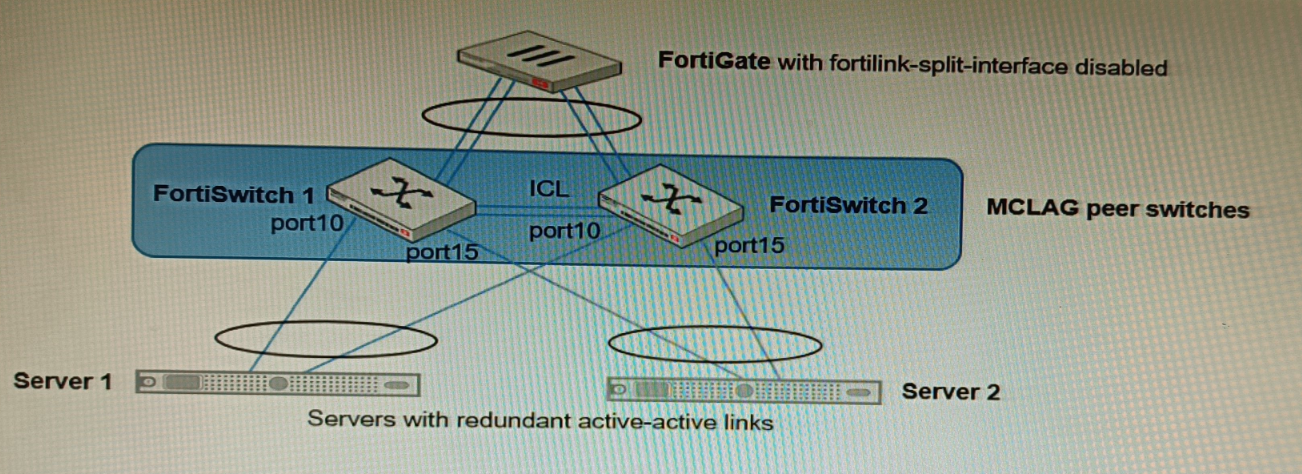
You have been tasked with replacing the managed switch Forti Switch 2 shown in the topology.
Which two actions are correct regarding the replacement process? (Choose two.)
Correct Answer:
A, B
Explanation
Ais correct because the automatically created trunk name is based on the MAC address of the FortiSwitch unit. When the FortiSwitch unit is replaced, the MAC address will change, but the trunk name will not change.
Bis correct because CLAG-ICL is a manually configured link aggregation group. When the FortiSwitch unit is replaced, the CLAG-ICL configuration will need to be manually reconfigured on the new FortiSwitch unit.
The other options are incorrect. Option C is incorrect because the automatically created trunk name does not change when the FortiSwitch unit is replaced. Option D is incorrect because MCLAG-ICL is a manually configured link aggregation group and will not be automatically reconfigured when the FortiSwitch unit is replaced.
Configuring link aggregation on FortiSwitches | FortiSwitch / FortiOS 7.0.4 - Fortinet Document Library
Managing FortiLink | FortiGate / FortiOS 7.0.4 - Fortinet Document Library
https://docs.fortinet.com/document/fortiswitch/7.0.8/devices-managed-by-fortios/173284/replacing-a-managed-fortiswitch-unit
Review the following FortiGate-6000 configuration excerpt:
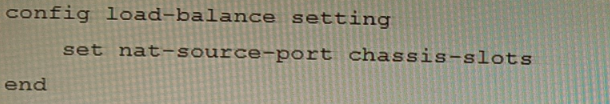
Based on the configuration, which statement is correct regarding SNAT source port partitioning behavior?
Correct Answer:
C
Which feature must you enable on the BGP neighbors to accomplish this goal?
Correct Answer:
A
A Hub FortiGate is connecting multiple branch FortiGate devices separating the traffic centrally in unique VRFs. Routing information is exchanged using BGP between the Hub and the Branch FortiGate devices.
You want to efficiently enable route leaking of specific routes between the VRFs.
Which two steps are required to achieve this requirement? (Choose two.)
Correct Answer:
A, D
Refer to the exhibit.
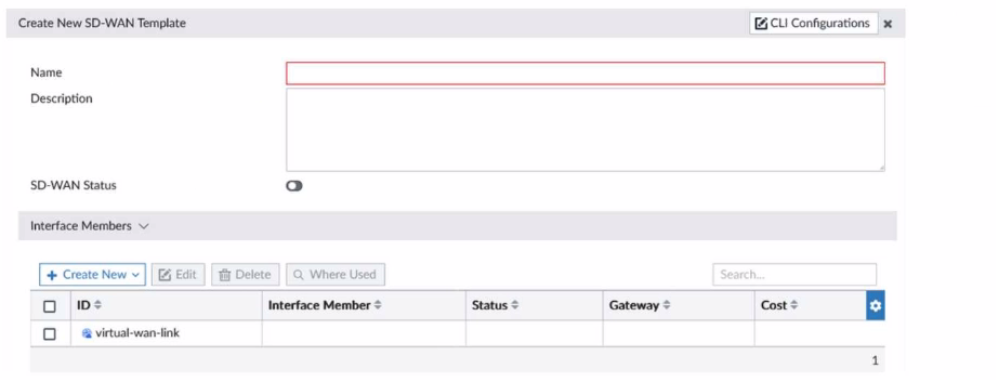
You need to create a base SD-WAN configuration that includes SD-WAN rules and Performance SLAs for spoke sites with various connectivity types. It needs to be done in a way that can be easily applied to new sites with a minimum amount of change. How should you create the SD-WAN zones?
Correct Answer:
A
Explanation
When designing SD-WAN configurations that need to scale across multiple sites, creating SD-WAN zones with members and overlay interfaces provides a template-based approach. You define the zone structure once with the overlay interfaces as members, then apply it to different sites by simply changing the physical interface assignments. This minimizes configuration changes and ensures consistent policy application across new sites. Other approaches like defining individual members per site would require more manual configuration for each deployment.
What is the benefit of using FortiGate NAC LAN Segments?
Correct Answer:
B
Full Access
Get the complete NSE8_812 question set
- 105 questions covering all exam domains
- Correct answers with explanations, like the free questions above
- PDF and online practice test
- 90 days of free updates
Domain 1: Secure SD-WAN
Candidates must demonstrate knowledge of SD-WAN advanced architecture and design, including advanced features and troubleshooting techniques for secure software-defined wide area networks.
Sample questions from this domain above:
Q5Q6
Domain 2: Networking
This domain covers advanced routing and VPN design methodologies, Fortinet access solutions configuration and integration, and application delivery technologies required for complex network environments.
Sample questions from this domain above:
Q1Q4
Domain 3: Automation
Candidates must understand Fortinet Automation tools, built-in scripting capabilities, and API configuration and usage for automating security operations across Fortinet solutions.
Domain 4: Security Operations
This covers knowledge of Fortinet SOC solutions and endpoint security solutions, focusing on detecting, analyzing, and responding to security threats in enterprise environments.
Domain 5: Security Solutions
Candidates must demonstrate knowledge of Fortinet application and network security solutions, including authentication mechanisms and their deployment across the security infrastructure.
Sample question from this domain above:
Q7
Domain 6: Infrastructure
This domain includes FortiGate operation modes and hardware technology, non-FortiGate hardware integration, and Fortinet cloud security solutions for hybrid and multi-cloud environments.
Sample questions from this domain above:
Q2Q3
Domain 7: Security Architecture
Candidates must understand FortiGate Network Security products, Security Fabric deployments, and high-availability solutions for designing resilient and scalable security architectures.
FAQ
NSE8_812 Exam FAQ
Common questions about the exam itself
How difficult is the NSE8_812 written exam compared to lower NSE levels?
The NSE 8 is designed for experienced network security professionals and is significantly harder than NSE 1-7. It requires expert-level understanding of complex Fortinet architecture and presents design scenarios with exhibits, configuration extracts, and troubleshooting challenges that test deep practical knowledge.
What background do I need before attempting NSE8_812?
While there are no formal prerequisites, the exam expects candidates to have substantial industry experience working with Fortinet security solutions. You should be familiar with FortiGate, FortiManager, FortiAnalyzer, and advanced networking concepts before attempting this expert-level certification.
Which objective area is typically hardest for NSE8_812 candidates?
Security Architecture tends to challenge candidates the most because it requires understanding how all Fortinet products integrate into deployments and how to design high-availability solutions. Focus on Security Fabric concepts, FortiGate Network Security products, and multi-site deployment scenarios.
How long should I study to prepare for NSE8_812?
Most experienced professionals require between 8 to 12 weeks of dedicated preparation for NSE 8. The exam is substantial enough that rushed preparation is unlikely to succeed, and you should allocate time to work through practical scenarios, not just memorize concepts.
What happens on exam day for NSE8_812?
You take a 120-minute online proctored exam at Pearson VUE. The exam contains 60 questions in multiple choice and multiple select format, many with exhibits. Each question must be answered 100 percent correctly for credit, with no partial credit given.
What are the retake rules if I fail NSE8_812?
You are allowed a maximum of three attempts to pass the NSE 8 written exam. After passing the written exam, you can then register for the practical exam, which is also mandatory for the full FCX Fortinet Certified Expert certification.
How long is the NSE8_812 certification valid, and what renewal requires?
The NSE 8 certification is valid for 2 years from the date you pass both the written and practical exams. To renew, you must either retake both exams or pass the FCX recertification assessment within the validity period.
What job role does NSE8_812 qualify me for?
The FCX (Fortinet Certified Expert) credential targets senior network security architects and engineers who design, deploy, and troubleshoot complex Fortinet security solutions. It is valued for roles requiring expert-level security architecture and strategic Fortinet implementation experience.
How does NSE8_812 relate to other exams in the Fortinet track?
NSE 8 is the highest level in the Fortinet certification track. The written exam (NSE8_812) is a prerequisite for the NSE 8 practical exam, and both are required to earn the full FCX certification. You do not need to hold NSE 7 first, but NSE 8 assumes knowledge covered in lower NSE levels.

