
Free Fortinet NSE7_PBC-7.2 Exam Practice Questions & Explanations
Prepared & Reviewed by the ValidExamDumps Editorial Team
At ValidExamDumps, we consistently monitor updates to the Fortinet NSE7_PBC-7.2 exam questions by Fortinet. Whenever our team identifies changes in the exam questions, objectives, focus areas or requirements, We immediately update our exam questions for both PDF and online practice exams. This commitment ensures our customers always have access to the most current and accurate questions. By preparing with these up to date and 100% exam domain coverage questions, our customers can successfully pass the Fortinet NSE 7 - Public Cloud Security 7.2 exam on their first attempt without needing additional materials or study guides.
Other certification materials providers often include outdated or removed questions by Fortinet in their NSE7_PBC-7.2 exam. These outdated questions lead to customers failing their Fortinet NSE 7 - Public Cloud Security 7.2 exam. In contrast, we ensure our questions bank includes only precise and up-to-date questions. Our main priority is your success in the Fortinet NSE7_PBC-7.2 exam, not profiting from selling obsolete exam questions in PDF or Online Practice Test.
How does Terraform keep track of provisioned resources?
Terraform manages and tracks the state of infrastructure resources through a file known as terraform.tfstate. This file is automatically created by Terraform and is updated after the application of a Terraform plan to capture the current state of the resources.
State File Purpose: The terraform.tfstate file contains a JSON object that records the IDs and properties of resources Terraform manages, so that it can map real-world resources to your configuration, keep track of metadata, and improve performance for large infrastructures.
State File Management: This file is crucial for Terraform to perform resource updates, deletions, and for creating dependencies. It's essentially the 'source of truth' for Terraform about your managed infrastructure and services.
Refer to the exhibit
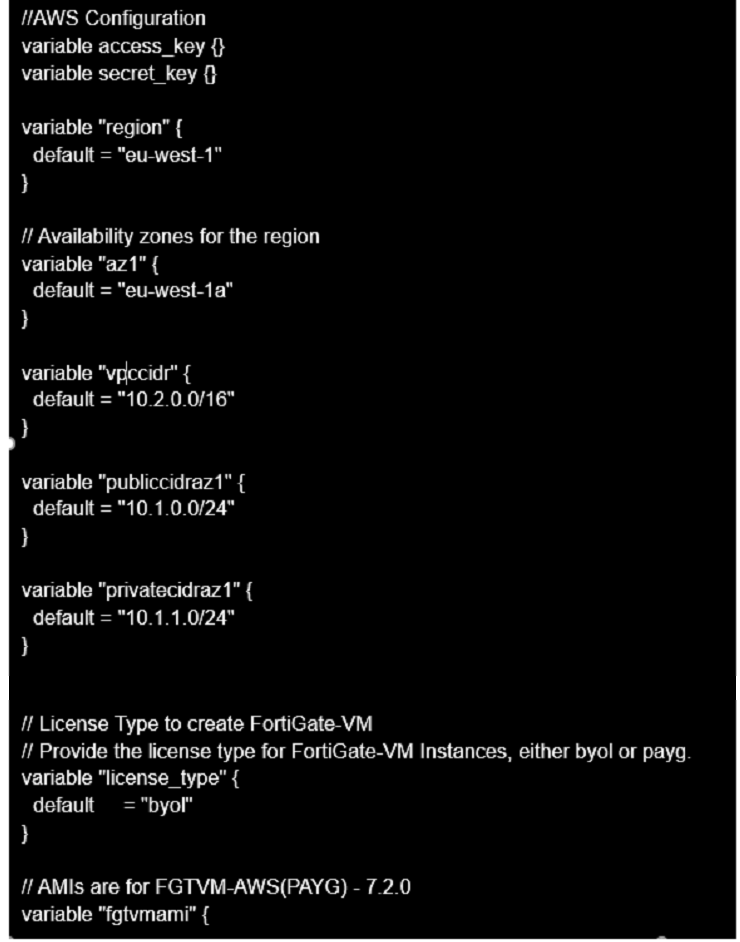
You are tasked to deploy a FortiGate VM with private and public subnets in Amazon Web Services (AWS).
You examined the variables.tf file.
What will be the final result after running the terraform init and terraform apply commands?
The variables.tf file shows that the FortiGate VM will be deployed in the eu-West-Ia region with private and public subnets. The region variable is set to ''eu-west-1'' and the availability_zone variable is set to ''eu-west-1a''. The vpc_id variable is set to ''vpc-0e9d6a6f'' and the subnets variable is set to a list of two subnet IDs: ''subnet-0f9d6a6f'' and ''subnet-1f9d6a6f''. The license_type variable is set to ''on-demand'' and the ami_id variable is set to ''ami-0e9d6a6f''.
Refer to the exhibit.
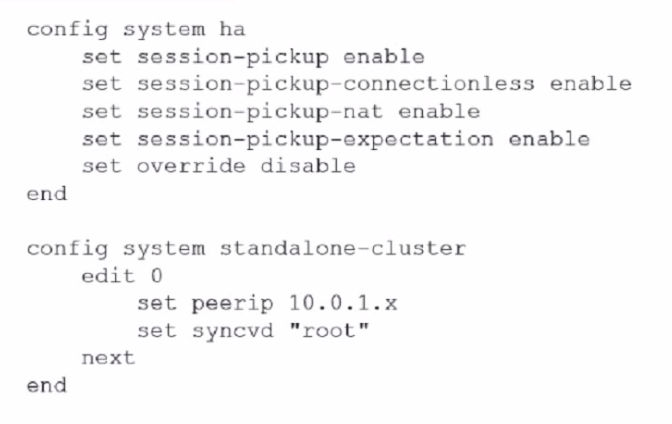
You deployed an HA active-active load balance sandwich with two FortiGate VMs in Microsoft Azure.
After the deployment, you prefer to use FGSP to synchronize sessions, and allow asymmetric return traffic In the environment, FortiGate port 1 and port 2 are facing external and internal load balancers respectively
What IP address must you use in the peerip configuration?
In an HA active-active load balance configuration with FortiGate VMs, especially in Microsoft Azure where FGSP (FortiGate Session Life Support Protocol) is used for session synchronization, the correct configuration for the peerip is:
Refer to the exhibit.


What value or values must the administrator use in the SSH Key section to deploy a FortiGate VM using Terraform in Amazon Web Services (AWS)?
For deploying a FortiGate VM using Terraform in AWS, the administrator must use:
B . Use the Name of the key pair.
Terraform and AWS SSH Keys: When deploying instances in AWS using Terraform, it is required to specify the name of the SSH key pair to enable key-based authentication to the instance post-deployment.
Configuration Syntax: The variable keyname within the Terraform configuration should match the exact name of the SSH key pair as it is stored in AWS. This ensures that Terraform can reference the correct key during the deployment process to set up SSH access to the FortiGate VM.
Terraform Variables: The variable 'keyname' block in the Terraform configuration will look for the key pair name as it should be declared in the terraform.tfvars file or passed as a variable during execution. This does not require the key pair's ID or fingerprint, just its name.
Refer to Exhibit:
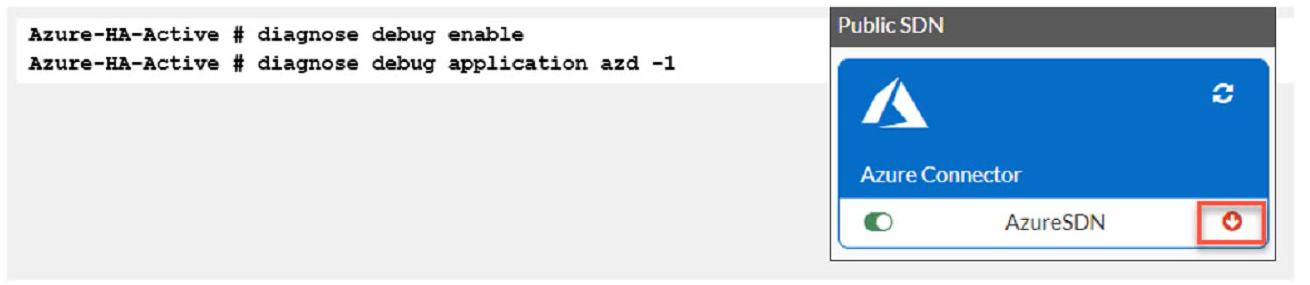
You are troubleshooting a Microsoft Azure SDN connector issue on your FortiGate VM in Azure
Which three settings should you check while troubleshooting this problem? (Choose three.)
The three settings that should be checked while troubleshooting this problem are: