
Free Fortinet NSE7_ADA-6.3 Exam Practice Questions & Explanations
Prepared & Reviewed by the ValidExamDumps Editorial Team
At ValidExamDumps, we consistently monitor updates to the Fortinet NSE7_ADA-6.3 exam questions by Fortinet. Whenever our team identifies changes in the exam questions, objectives, focus areas or requirements, We immediately update our exam questions for both PDF and online practice exams. This commitment ensures our customers always have access to the most current and accurate questions. By preparing with these up to date and 100% exam domain coverage questions, our customers can successfully pass the Fortinet NSE 7 - Advanced Analytics 6.3 exam on their first attempt without needing additional materials or study guides.
Other certification materials providers often include outdated or removed questions by Fortinet in their NSE7_ADA-6.3 exam. These outdated questions lead to customers failing their Fortinet NSE 7 - Advanced Analytics 6.3 exam. In contrast, we ensure our questions bank includes only precise and up-to-date questions. Our main priority is your success in the Fortinet NSE7_ADA-6.3 exam, not profiting from selling obsolete exam questions in PDF or Online Practice Test.
What are the modes of Data Ingestion on FortiSOAR? (Choose three.)
Refer to the exhibit.
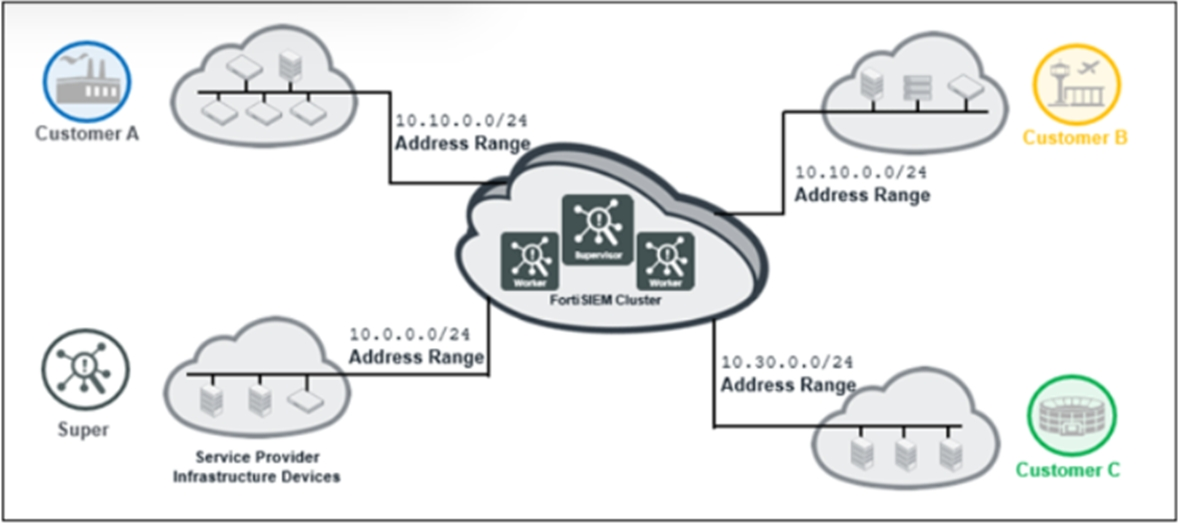
The service provider deployed FortiSIEM without a collector and added three customers on the supervisor.
What mistake did the administrator make?
The mistake that the administrator made is that customer A and customer B have overlapping IP addresses. This will cause confusion and errors in event collection and correlation, as well as CMDB discovery and classification. To avoid this problem, each customer should have a unique IP address range or use NAT to translate their IP addresses.
Refer to the exhibit.
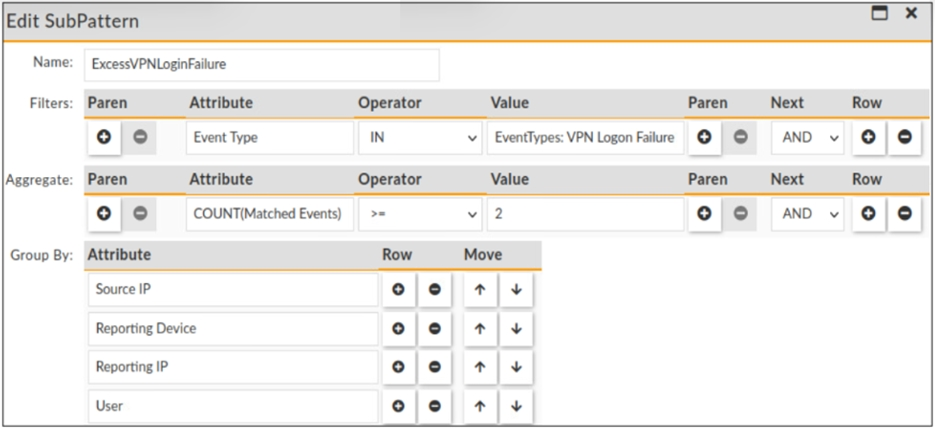
The rule evaluates multiple VPN logon failures within a ten-minute window. Consider the following VPN failure events received within a ten-minute window:
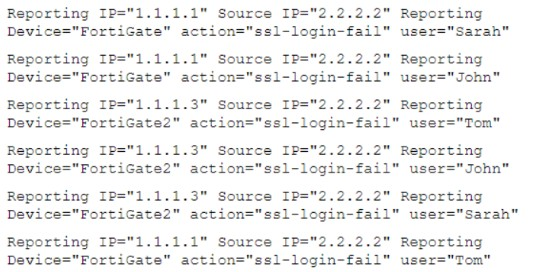
How many incidents are generated?
The rule evaluates multiple VPN logon failures within a ten-minute window. The rule will generate an incident if there are more than three VPN logon failures from the same source IP address within a ten-minute window. Based on the VPN failure events received within a ten-minute window, there are two incidents generated:
One incident for source IP address 10.10.10.10, which has four VPN logon failures at 09:01, 09:02, 09:03, and 09:04.
One incident for source IP address 10.10.10.11, which has four VPN logon failures at 09:06, 09:07, 09:08, and 09:09.
Refer to the exhibit.
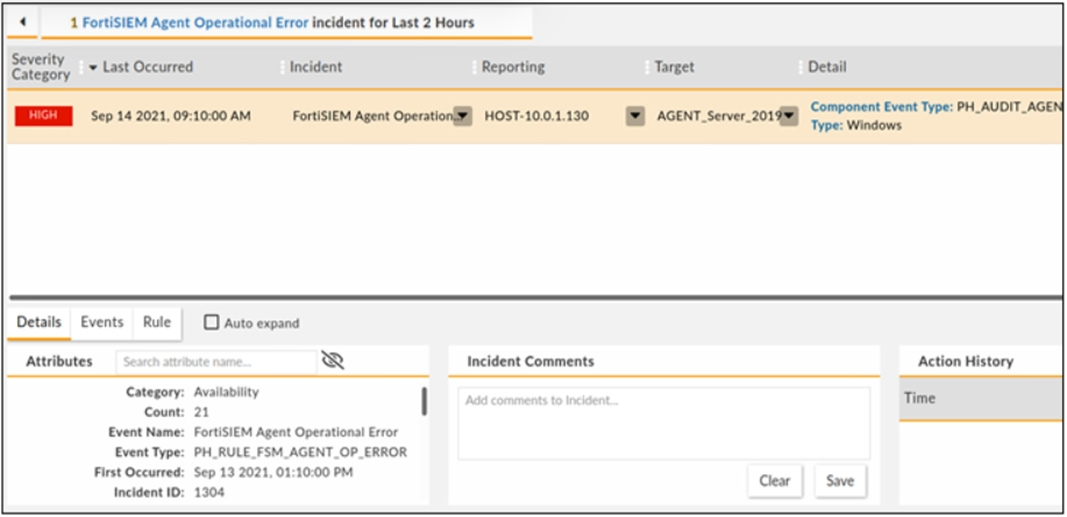
How long has the UEBA agent been operationally down?
The UEBA agent status shows that it has been operationally down for one day and three hours ago (1d3h). This means that it has been down for 24 hours plus three hours, which is equal to 21 hours.
Which three processes are collector processes? (Choose three.)
The collector processes are responsible for receiving, parsing, normalizing, correlating, and monitoring events from various sources. The collector processes are phParser, phRuleMaster, and phMonitorAgent.