
Free Fortinet NSE6_WCS-7.0 Exam Practice Questions & Explanations
Prepared & Reviewed by the ValidExamDumps Editorial Team
At ValidExamDumps, we consistently monitor updates to the Fortinet NSE6_WCS-7.0 exam questions by Fortinet. Whenever our team identifies changes in the exam questions, objectives, focus areas or requirements, We immediately update our exam questions for both PDF and online practice exams. This commitment ensures our customers always have access to the most current and accurate questions. By preparing with these up to date and 100% exam domain coverage questions, our customers can successfully pass the Fortinet NSE 6 - Cloud Security 7.0 for AWS exam on their first attempt without needing additional materials or study guides.
Other certification materials providers often include outdated or removed questions by Fortinet in their NSE6_WCS-7.0 exam. These outdated questions lead to customers failing their Fortinet NSE 6 - Cloud Security 7.0 for AWS exam. In contrast, we ensure our questions bank includes only precise and up-to-date questions. Our main priority is your success in the Fortinet NSE6_WCS-7.0 exam, not profiting from selling obsolete exam questions in PDF or Online Practice Test.
Which three statements correctly describe FortiGate Cloud-Native Firewall (CNF)? (Choose three.)
Scalability:
FortiGate Cloud-Native Firewall (CNF) is designed to scale seamlessly with your cloud infrastructure, providing the necessary protection without requiring manual intervention for scaling (Option B).
Firewall-as-a-Service:
FortiGate CNF is offered as a Firewall-as-a-Service (FWaaS), which simplifies the deployment and management of firewall capabilities directly in the cloud environment (Option D).
Management:
FortiGate CNF can be managed using FortiManager and AWS Firewall Manager, providing comprehensive management capabilities both from Fortinet's platform and AWS's native management tools (Option E).
Other Considerations:
Option A (carrier-grade protection) is not specifically highlighted as a feature of FortiGate CNF.
Option C (uses AWS Elastic Load Balancing) is incorrect as FortiGate CNF operates independently of AWS ELB, although it can integrate with various AWS services.
FortiGate CNF Documentation: FortiGate CNF
An organization has created a VPC with two subnets and deployed a FortiGate-VM (VM04/c4.xlarge) in AWS.
The EC2 instance is initially configured with two Elastic Network Interfaces (ENIs). The primary ENI is configured on the public subnet, and the secondary ENI is configured on the private subnet. To provide internet access for the FortiGate-VM, they now want to associate an EIP to its primary ENI, but the assignment is failing.
Which action would allow the EIP assignment to be successful?
Internet Gateway Requirement:
For an Elastic IP (EIP) to be assigned to an instance's primary ENI, the VPC must have an Internet Gateway (IGW) attached. The IGW enables the VPC to communicate with the internet, allowing the EIP to function properly (Option C).
Process of Assigning EIP:
Once the Internet Gateway is attached to the VPC, the EIP can be successfully assigned to the primary ENI of the FortiGate VM, providing it with internet access.
Other Options Analysis:
Option A is incorrect because the primary ENI is already in a public subnet.
Option B is not necessary and may not solve the issue without an attached Internet Gateway.
Option D is partially correct about the routing table but does not address the primary issue of needing an Internet Gateway.
An administrator needs to attach an Elastic Network Interface (ENI) to an application instance in a VPC with multiple availability zones. An instance runs in availability zone 1.
Which ENI property must the administrator consider when implementing this requirement?
ENI Attachment Across Availability Zones:
Elastic Network Interfaces (ENIs) are associated with a specific Availability Zone. They cannot be attached to instances that are in a different Availability Zone than where the ENI was created. Therefore, an ENI created in Availability Zone 1 cannot be attached to an instance in Availability Zone 2 (Option A).
ENI Reattachment:
ENIs can be detached from one instance and reattached to another instance within the same Availability Zone. This flexibility allows for network interface configuration to be preserved across instance changes within the same AZ.
Other Options Analysis:
Option B is incorrect because an ENI can be reattached to any instance in the same AZ.
Option C is incorrect as the primary ENI (eth0) cannot be detached from an instance.
Option D is incorrect because when an ENI is moved, the traffic is directed to the new instance, and there is no redirection to the old instance.
Refer to the exhibit.
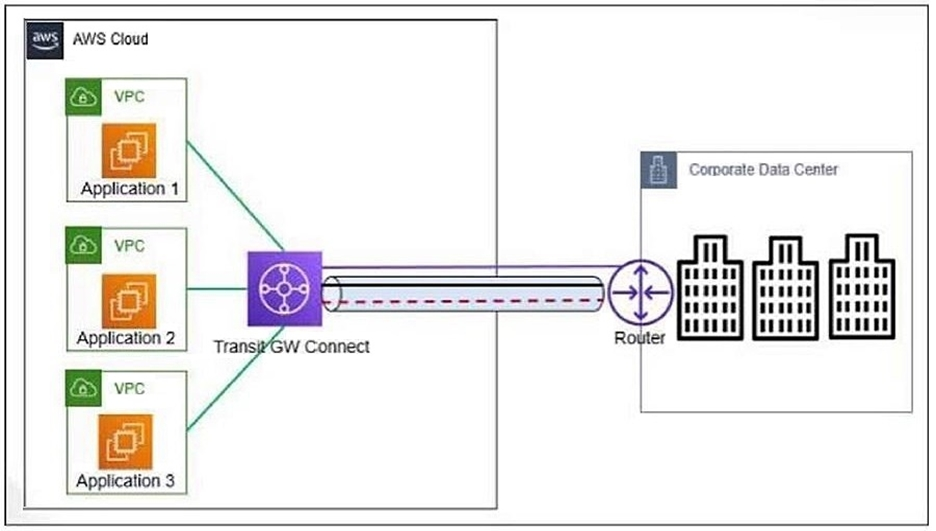
An organization deployed the application servers in the AWS VPC that connects to the corporate data center using Transit Gateway Connect. Demand for the applications has grown and the connection requires more bandwidth.
What is required to achieve higher bandwidth?
Understanding Transit Gateway Connect:
Transit Gateway Connect is a feature of AWS Transit Gateway that simplifies the integration of SD-WAN networks with AWS. It uses Generic Routing Encapsulation (GRE) tunnels to facilitate this connection.
GRE Tunnels and Bandwidth:
GRE tunnels can dynamically scale to meet increasing bandwidth demands. They allow multiple tunnels between the same endpoints, which can aggregate bandwidth without requiring additional configuration.
Scaling Bandwidth with GRE:
The GRE protocol used by Transit Gateway Connect can support high bandwidth requirements by spreading traffic across multiple tunnels. As demand grows, additional tunnels can be automatically used to handle the increased traffic load.
Comparison with Other Options:
Option A suggests using public IP addresses, which is not relevant to bandwidth scaling.
Option B is incorrect because bandwidth can be increased through GRE scaling.
Option D suggests adding a Transit VPC, which is unnecessary for increasing bandwidth when using Transit Gateway Connect.
A customer has deployed FortiGate Cloud-Native Firewall (CNF).
Which two statements are correct about policy sets? (Choose two.)
Implicit Deny Rule:
Similar to traditional firewall rule sets, FortiGate Cloud-Native Firewall (CNF) includes an implicit deny rule at the bottom of each policy set. This means any traffic that does not match an existing rule in the policy set is automatically denied (Option A).
Policy Set Creation:
When a new CNF instance is deployed, a new policy set is created specifically for that instance. This ensures that each CNF instance can have a tailored set of security policies based on the specific needs of the deployment (Option C).
Other Options Analysis:
Option B is incorrect because policy sets do not require manual synchronization; they are applied automatically once configured.
Option D is incorrect as a single CNF instance operates with a single policy set at a time.
FortiGate CNF Documentation: FortiGate CNF
Firewall Policy Best Practices: Fortinet Policies