
Free Fortinet NSE6_FSW-7.2 Exam Practice Questions & Explanations
Prepared & Reviewed by the ValidExamDumps Editorial Team
At ValidExamDumps, we consistently monitor updates to the Fortinet NSE6_FSW-7.2 exam questions by Fortinet. Whenever our team identifies changes in the exam questions, objectives, focus areas or requirements, We immediately update our exam questions for both PDF and online practice exams. This commitment ensures our customers always have access to the most current and accurate questions. By preparing with these up to date and 100% exam domain coverage questions, our customers can successfully pass the Fortinet NSE 6 - FortiSwitch 7.2 exam on their first attempt without needing additional materials or study guides.
Other certification materials providers often include outdated or removed questions by Fortinet in their NSE6_FSW-7.2 exam. These outdated questions lead to customers failing their Fortinet NSE 6 - FortiSwitch 7.2 exam. In contrast, we ensure our questions bank includes only precise and up-to-date questions. Our main priority is your success in the Fortinet NSE6_FSW-7.2 exam, not profiting from selling obsolete exam questions in PDF or Online Practice Test.
Refer to the exhibit.
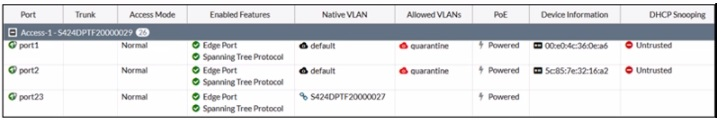
The exhibit shows the current status of the ports on the managed FortiSwitch. Access-1.
Why would FortiGate display a serial number in the Native VLAN column associated with the port23 entry?
The information in the 'Native VLAN' column for port23 on the FortiSwitch indicates that a standalone switch is connected to it. This is because the column displays '$424MPTF20000027,' which matches the format of a Fortinet device serial number.
Here's a breakdown of the evidence in the image:
Native VLAN: The 'Native VLAN' column typically displays the VLAN ID for untagged traffic on a trunk port. However, in this case, it shows a serial number format ('$424MPTF20000027').
No Trunk Information: The 'Trunk' column is blank for port23, indicating it's not configured as a trunk member.
Other Ports: Port1 and port2 show 'default' in the 'Native VLAN' column, which is the expected behavior for access ports.
Fortinet FortiSwitch devices typically don't display the serial number of adjacent FortiSwitch devices in the 'Native VLAN' column. This column is reserved for VLAN information on trunk ports.
Which two statements about VLAN assignments on FortiSwitch ports are true? (Choose two.)
VLAN assignments on FortiSwitch ports must follow certain rules and guidelines to ensure network integrity and proper traffic segregation:
Only Assign One Native VLAN on a Port (C):
Native VLAN Configuration: Each switch port can have only one native VLAN. The native VLAN carries untagged traffic for that port. If the port receives untagged frames, they are assumed to belong to the native VLAN.
Importance of Singular Native VLAN: This is crucial for preventing VLAN hopping attacks and ensures clear and secure VLAN demarcation on each port.
Assign Untagged VLANs Using FortiGate CLI (D):
CLI Configuration: Untagged VLANs, often equivalent to the native VLAN, can be assigned through the FortiGate CLI when managing a FortiSwitch via FortiLink. This allows for central management and configuration of VLANs across connected switches.
Operational Efficiency: Using the CLI ensures that VLAN settings are applied uniformly, reducing the likelihood of misconfigurations that might occur when managing VLANs individually on each switch.
Which two statements about the FortiLink authorization process are true? (Choose two.)
The FortiLink authorization process is an integral part of setting up FortiSwitch to be managed by FortiGate. The correct statements regarding the FortiLink authorization process are:
C . A FortiLink frame is sent by FortiGate to FortiSwitch to complete the authorization. This is a part of the FortiLink protocol, where FortiGate communicates with the connected FortiSwitch to establish management and control. This frame initiates the configuration and management process, allowing FortiGate to effectively control the switch.
D . FortiLink authorization sets the FortiSwitch management mode to FortiLink. Once authorized, the management mode of FortiSwitch is set to FortiLink, indicating that it is being managed via a FortiLink connection from a FortiGate appliance. This changes the operational mode of the switch to be under the control of the FortiGate for centralized management and policy application.
FortiGate is unable to establish a tunnel with the FortiSwitch device it is supposed to manage Based on the debug output shown in the exhibit, what is the reason for the failure?
The issue described pertains to the establishment of a tunnel (likely a CAPWAP tunnel for management purposes between FortiGate and FortiSwitch). Based on typical error analysis in tunnel setup scenarios:
The CAPWAP tunnel failed to come up due to a mismatch in time (Option C): This answer is plausible because time synchronization is crucial for security protocols that underpin tunnel establishments, such as DTLS (Datagram Transport Layer Security) used within CAPWAP tunnels. If the clocks on FortiGate and FortiSwitch are significantly out of sync, the security handshake (which can include timestamp validation) could fail, preventing the tunnel from coming up.
Fortinet's technical documentation typically outlines the importance of time synchronization for secure communications. In CAPWAP/DLTS scenarios, precise time matching is crucial to ensure that the cryptographic parameters align correctly during the handshake process.
What are two reasons why time synchronization between FortiGate and its managed FortiSwitch is critical in switch management? (Choose two.)
Time synchronization between FortiGate and its managed FortiSwitch devices is essential for several reasons:
A . FortiSwitch does not retain its time after a reboot, which gets reset after each reboot. This characteristic of FortiSwitch underlines the importance of time synchronization with FortiGate. Since FortiSwitch loses its time settings upon reboot, synchronizing with FortiGate ensures that its system clock is accurate, which is vital for logging, troubleshooting, and security timestamping.
C . FortiSwitch cannot complete the DTLS handshake used in the CAPWAP tunnel. Accurate time synchronization is crucial for security protocols such as DTLS, which rely on timestamped certificates for establishing a secure connection. If the time on FortiSwitch is not synchronized with FortiGate, the DTLS handshake used in the CAPWAP tunnel for secure communication may fail due to time discrepancies, impacting the management and operation of the switch.