
Free Fortinet NSE6_FAC-6.4 Exam Practice Questions & Explanations
Prepared & Reviewed by the ValidExamDumps Editorial Team
At ValidExamDumps, we consistently monitor updates to the Fortinet NSE6_FAC-6.4 exam questions by Fortinet. Whenever our team identifies changes in the exam questions, objectives, focus areas or requirements, We immediately update our exam questions for both PDF and online practice exams. This commitment ensures our customers always have access to the most current and accurate questions. By preparing with these up to date and 100% exam domain coverage questions, our customers can successfully pass the Fortinet NSE 6 - FortiAuthenticator 6.4 exam on their first attempt without needing additional materials or study guides.
Other certification materials providers often include outdated or removed questions by Fortinet in their NSE6_FAC-6.4 exam. These outdated questions lead to customers failing their Fortinet NSE 6 - FortiAuthenticator 6.4 exam. In contrast, we ensure our questions bank includes only precise and up-to-date questions. Our main priority is your success in the Fortinet NSE6_FAC-6.4 exam, not profiting from selling obsolete exam questions in PDF or Online Practice Test.
You are a Wi-Fi provider and host multiple domains.
How do you delegate user accounts, user groups and permissions per domain when they are authenticating on a single FortiAuthenticator device?
Realms are a way to delegate user accounts, user groups and permissions per domain when they are authenticating on a single FortiAuthenticator device. A realm is a logical grouping of users and groups based on a common attribute, such as a domain name or an IP address range. Realms allow administrators to apply different authentication policies and settings to different groups of users based on their realm membership.
An administrator has an active directory (AD) server integrated with FortiAuthenticator. They want members of only specific AD groups to participate in FSSO with their corporate FortiGate firewalls.
How does the administrator accomplish this goal?
To allow members of only specific AD groups to participate in FSSO with their corporate FortiGate firewalls, the administrator can configure SSO groups and assign them to FortiGate groups. SSO groups are groups of users or devices that are defined on FortiAuthenticator based on various criteria, such as user group membership, source IP address, MAC address, or device type. FortiGate groups are groups of users or devices that are defined on FortiGate based on various criteria, such as user group membership, firewall policy, or authentication method. By mapping SSO groups to FortiGate groups, the administrator can control which users or devices can access the network resources protected by FortiGate.
What are three key features of FortiAuthenticator? (Choose three)
FortiAuthenticator is a user and identity management solution that provides strong authentication, wireless 802.1X authentication, certificate management, RADIUS AAA (authentication, authorization, and accounting), and Fortinet Single Sign-On (FSSO). It also offers portal services for guest management, self-service password reset, and device registration. It is not a log server or an RSSO server. Reference: https://docs.fortinet.com/document/fortiauthenticator/6.4/release-notes
Examine the screenshot shown in the exhibit.
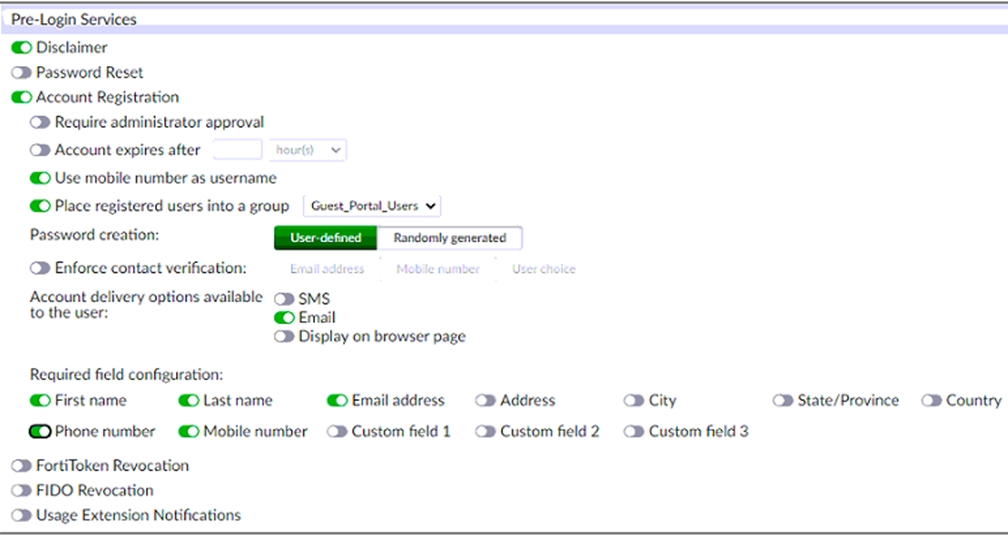
Which two statements regarding the configuration are true? (Choose two.)
The screenshot shows that the account registration feature is enabled for the guest portal and that the guest group is set to Guest_Portal_Users.This means that all guest accounts created using this feature will be placed under that group1. The screenshot also shows that email validation is enabled for the guest portal and that the email validation link expires after 24 hours.This means that all accounts registered through the guest portal must be validated through email within that time frame1.
What are three key features of FortiAuthenticator? (Choose three)
FortiAuthenticator is a user and identity management solution that provides strong authentication, wireless 802.1X authentication, certificate management, RADIUS AAA (authentication, authorization, and accounting), and Fortinet Single Sign-On (FSSO). It also offers portal services for guest management, self-service password reset, and device registration. It is not a log server or an RSSO server. Reference: https://docs.fortinet.com/document/fortiauthenticator/6.4/release-notes