At ValidExamDumps, we consistently monitor updates to the Fortinet FCSS_NST_SE-7.6 exam questions by Fortinet. Whenever our team identifies changes in the exam questions, objectives, focus areas or requirements, We immediately update our exam questions for both PDF and online practice exams. This commitment ensures our customers always have access to the most current and accurate questions. By preparing with these up to date and 100% exam domain coverage questions, our customers can successfully pass the Fortinet NSE 6 - Network Security 7.6 Support Engineer exam on their first attempt without needing additional materials or study guides.
Other certification materials providers often include outdated or removed questions by Fortinet in their FCSS_NST_SE-7.6 exam. These outdated questions lead to customers failing their Fortinet NSE 6 - Network Security 7.6 Support Engineer exam. In contrast, we ensure our questions bank includes only precise and up-to-date questions. Our main priority is your success in the Fortinet FCSS_NST_SE-7.6 exam, not profiting from selling obsolete exam questions in PDF or Online Practice Test.
Refer to the exhibit.
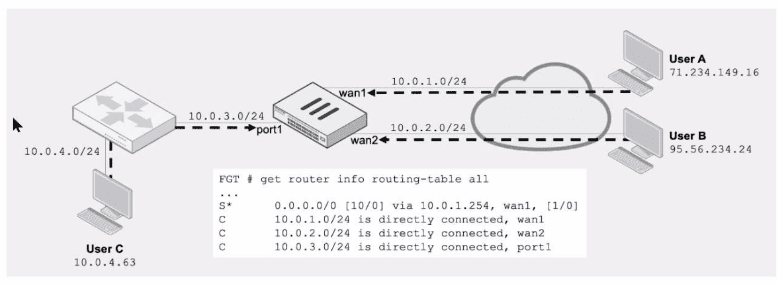
Assuming a default configuration, which three statements are true? (Choose three.)
References:
Fortinet Technical Note: RPF Default Configuration and Routing Table Matching
FortiGate Administration Guide: Routing and Asymmetric Routing Controls
Community Knowledgebase: Route Lookups and RPF Enforcement on FortiOS
Refer to the exhibit.
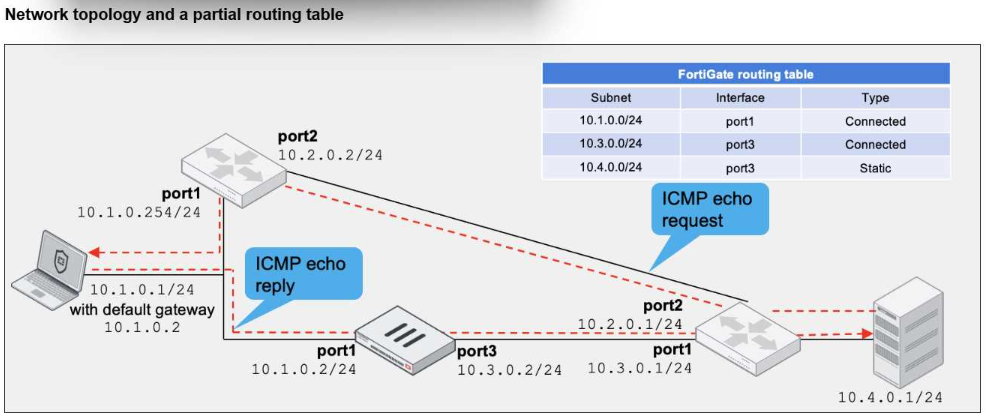
A network topology and a partial routing table are shown.
FortiGate has already been configured with a firewall policy that allows all ICMP traffic to flow from port1 to port3.
Which two changes can the administrator perform to ensure the server at 10.4.0.1/24 receives the ICMP echo reply from the laptop at 10.1.0.1/24? (Choose two.)
The correct answers are A and C.
The study guide describes this exact asymmetric ICMP scenario. It states:
''The server sends an echo request to the PC through port2 of the local router, effectively bypassing FortiGate. When it receives the echo request, the PC responds with an echo reply through its default gateway, 10.1.0.2, which is port1 on FortiGate. Because there is no existing session, the echo reply is dropped. All subsequent echo replies are blocked.''
That means the current problem exists because:
the ICMP request bypasses FortiGate
the ICMP reply goes through FortiGate
FortiGate has no matching session, so it drops the reply
The study guide then shows the exact corrective option:
''Allowing asymmetric routing:''
config system settings
set asymroute enable
end
It further explains:
''After the packet passes through the FortiGate CPU, FortiGate forwards the packet using the FIB, even though there are no session matches. FortiGate forwards all subsequent echo replies using the FIB.''
So A is correct.
The other valid fix is to make the traffic symmetric by changing the laptop's default gateway so the reply no longer goes through FortiGate. In the exhibit, the alternate gateway is 10.1.0.254, which is the local router on the same subnet. If the laptop uses 10.1.0.254 instead of 10.1.0.2, the ICMP echo reply follows the same bypass path as the echo request, so the server receives it without involving FortiGate session validation. This makes C correct.
Why the other options are wrong:
B is wrong because this is not an RPF problem. The study guide explains RPF as a reverse path lookup used to validate whether a packet arrived on a legitimate interface, mainly for spoofing protection. The issue in this scenario is a missing session due to asymmetric routing, not a strict-versus-feasible RPF failure
D is wrong because FortiGate already has the specific route 10.4.0.0/24 through port3 in the routing table shown in the exhibit, so adding a default static route to port3 is unnecessary and not the reason the echo reply is being dropped
So the verified answers are: A, C.
Refer to the exhibit.
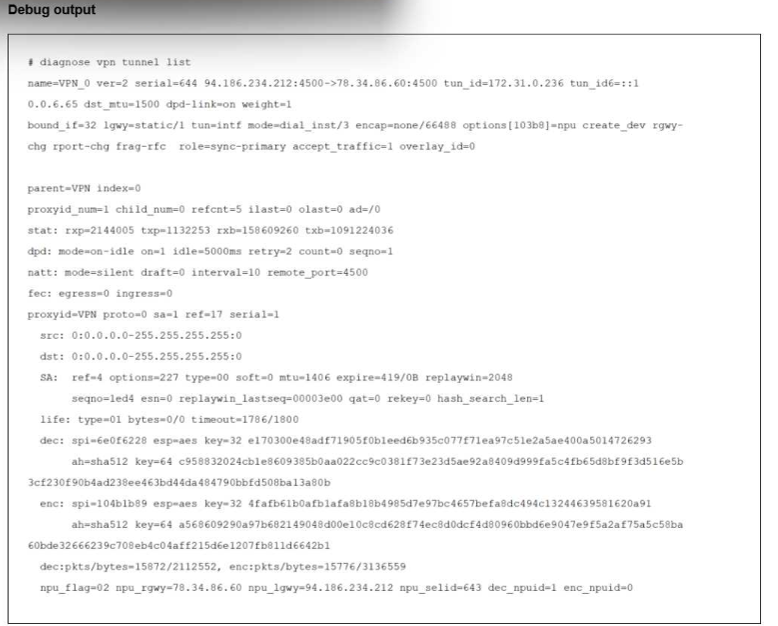
The output of the command diagnose vpn tunnel list is shown.
Reviewing the debug command, what is the current status of the traffic flowing through the tunnel?
The correct answer is D. The inbound IPsec SA was copied to the NPU.
The exhibit shows:
npu_flag=02
dec_npuid=1
enc_npuid=0
The study guide gives the exact meaning of the npu_flag field:
npu_flag=00 = Both IPsec SAs loaded to the kernel
npu_flag=01 = Outbound IPsec SA copied to NPU
npu_flag=02 = Inbound IPsec SA copied to NPU
npu_flag=03 = Both outbound and inbound IPsec SAs copied to NPU
It also explains: ''If the first IPsec packet is inbound and can be offloaded, the inbound SA is copied to the NPU and the npu_flag changes to 02. After both SAs are copied to the NPU, the npu_flag changes to 03.''
So with npu_flag=02, only the inbound SA has been copied to the NPU. That makes D correct.
Why the other options are wrong:
A is wrong because outbound-only offload would be npu_flag=01, not 02
C is wrong because both directions offloaded would be npu_flag=03, not 02
B is wrong because dec_npuid=1 identifies the NPU ID used for decryption, but it does not state that the processor is specifically NP6. The study guide only maps the offload state through the npu_flag values in this context, not the NPU model from this field alone
So the verified answer is: D.
Which two statements about conserve mode are true? (Choose two.)
Refer to the exhibit.
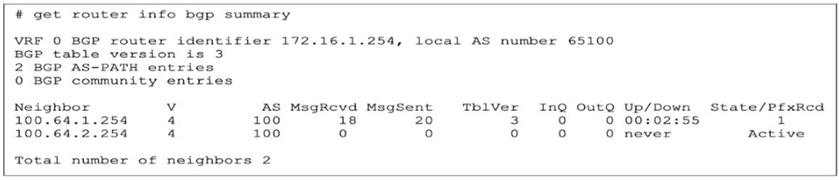
The output of the get router info bgp summary command is shown.
Which statement regarding adjacencies between the local router and its neighbors is correct?
The correct answer is B.
In the exhibit:
Neighbor 100.64.1.254 shows State/PfxRcd = 1, which means the session is established and the local FortiGate has received 1 prefix
Neighbor 100.64.2.254 shows State/PfxRcd = Active
The study guide explains the BGP states exactly:
Connect: Waiting for a successful three-way TCP connection
Active: Unable to establish the TCP session
OpenSent: Waiting for an OPEN message from the peer
OpenConfirm: Waiting for the keepalive message from the peer
Established: Peers have successfully exchanged OPEN and keepalive messages
It also explains how to read the State/PfxRcd column:
''If the state is not established, this column displays the BGP state. If the state is established, this column displays the number of prefixes that the local FortiGate received from that neighbor.''
Therefore, because neighbor 100.64.2.254 is in Active state, the correct conclusion is that the BGP adjacency cannot form because the TCP session could not be established.
Why the other options are wrong:
A is wrong because BGP can establish adjacencies with multiple neighbors independently; one established neighbor does not block another
C is wrong because BGP adjacency is not established based on neighbor ''priority''; the output shows adjacency is established because the session completed and prefixes were exchanged
D is wrong because having two neighbors in the same remote AS is valid in BGP and does not prevent adjacency formation
So the verified answer is: B.

