
Free Fortinet FCP_WCS_AD-7.4 Exam Practice Questions & Explanations
Prepared & Reviewed by the ValidExamDumps Editorial Team
At ValidExamDumps, we consistently monitor updates to the Fortinet FCP_WCS_AD-7.4 exam questions by Fortinet. Whenever our team identifies changes in the exam questions, objectives, focus areas or requirements, We immediately update our exam questions for both PDF and online practice exams. This commitment ensures our customers always have access to the most current and accurate questions. By preparing with these up to date and 100% exam domain coverage questions, our customers can successfully pass the Fortinet FCP - AWS Cloud Security 7.4 Administrator exam on their first attempt without needing additional materials or study guides.
Other certification materials providers often include outdated or removed questions by Fortinet in their FCP_WCS_AD-7.4 exam. These outdated questions lead to customers failing their Fortinet FCP - AWS Cloud Security 7.4 Administrator exam. In contrast, we ensure our questions bank includes only precise and up-to-date questions. Our main priority is your success in the Fortinet FCP_WCS_AD-7.4 exam, not profiting from selling obsolete exam questions in PDF or Online Practice Test.
A customer has deployed FortiGate Cloud-Native Firewall (CNF).
Which two statements are correct about policy sets? (Choose two.)
Implicit Deny Rule:
Similar to traditional firewall rule sets, FortiGate Cloud-Native Firewall (CNF) includes an implicit deny rule at the bottom of each policy set. This means any traffic that does not match an existing rule in the policy set is automatically denied (Option A).
Policy Set Creation:
When a new CNF instance is deployed, a new policy set is created specifically for that instance. This ensures that each CNF instance can have a tailored set of security policies based on the specific needs of the deployment (Option C).
Other Options Analysis:
Option B is incorrect because policy sets do not require manual synchronization; they are applied automatically once configured.
Option D is incorrect as a single CNF instance operates with a single policy set at a time.
FortiGate CNF Documentation: FortiGate CNF
Firewall Policy Best Practices: Fortinet Policies
Refer to the exhibit.
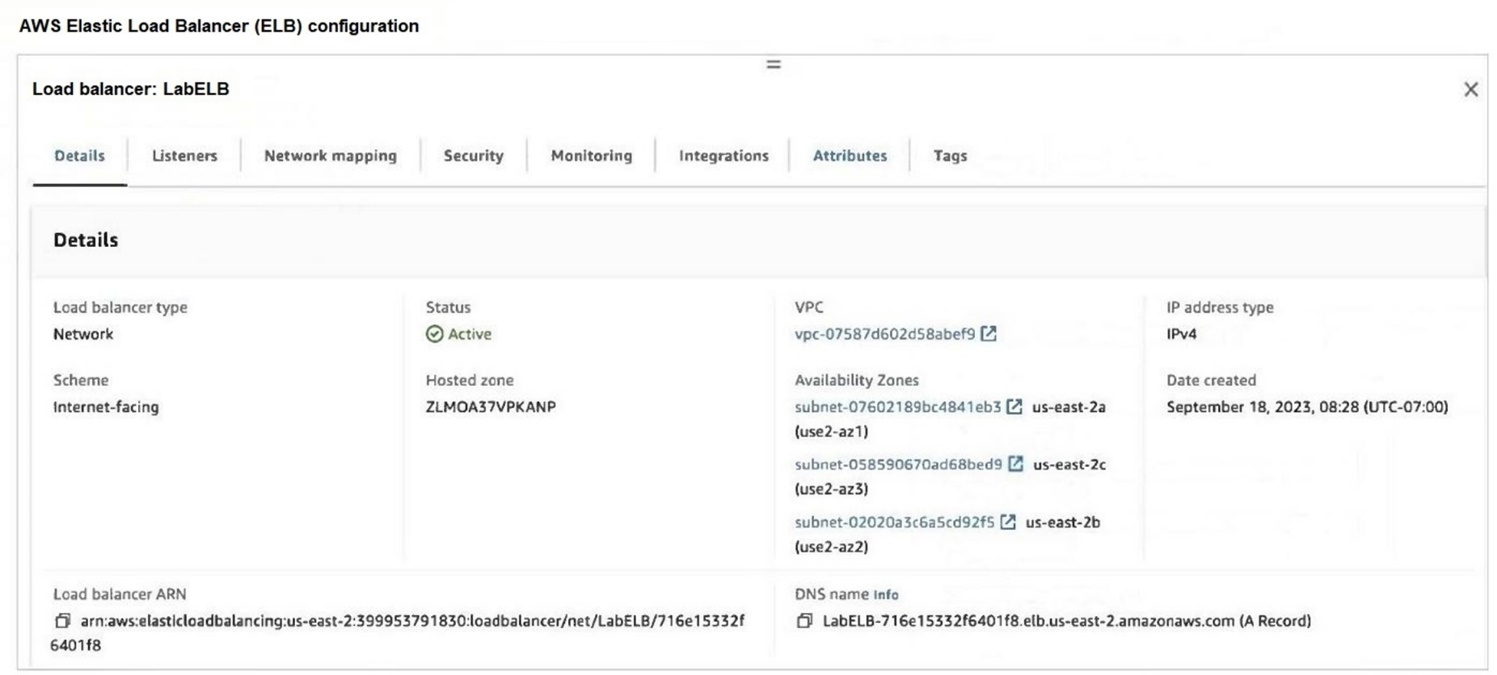
A customer is using the AWS Elastic Load Balancer (ELB).
Which two statements are correct about the ELB configuration? (Choose two.)
Load Balancer Configuration Overview:
The provided configuration indicates that the ELB is an internet-facing load balancer.
Multi-AZ Load Balancing:
The load balancer is configured to distribute traffic across multiple availability zones (A, B, and C), ensuring high availability and fault tolerance (Option A).
Accessing Targets via DNS:
The DNS name of the load balancer (LabELB-716e15332f6401f8.elb.us-east-2.amazonaws.com) can be used to reach the targets behind the ELB, facilitating traffic routing to the appropriate instances (Option C).
Comparison with Other Options:
Option B is incorrect as the ARN is not used to access the load balancer directly.
Option D is incorrect because the load balancer is configured for internet-facing traffic, not just internal VPC traffic.
An organization has created a VPC with two subnets and deployed a FortiGate-VM (VM04/c4.xlarge) in AWS.
The EC2 instance is initially configured with two Elastic Network Interfaces (ENIs). The primary ENI is configured on the public subnet, and the secondary ENI is configured on the private subnet. To provide internet access for the FortiGate-VM, they now want to associate an EIP to its primary ENI, but the assignment is failing.
Which action would allow the EIP assignment to be successful?
Internet Gateway Requirement:
For an Elastic IP (EIP) to be assigned to an instance's primary ENI, the VPC must have an Internet Gateway (IGW) attached. The IGW enables the VPC to communicate with the internet, allowing the EIP to function properly (Option C).
Process of Assigning EIP:
Once the Internet Gateway is attached to the VPC, the EIP can be successfully assigned to the primary ENI of the FortiGate VM, providing it with internet access.
Other Options Analysis:
Option A is incorrect because the primary ENI is already in a public subnet.
Option B is not necessary and may not solve the issue without an attached Internet Gateway.
Option D is partially correct about the routing table but does not address the primary issue of needing an Internet Gateway.
Your organization is deciding between deploying an active-active (A-A) or active-passive (A-P) FortiGate high availability (HA) cluster in AWS cloud.
Which two statements are true about A-A clusters compared to A-P clusters? (Choose two.)
Symmetric Traffic Flow with SNAT:
In active-active (A-A) clusters, symmetric traffic flow is essential for maintaining session integrity across multiple instances. Source Network Address Translation (SNAT) is performed inbound to ensure that return traffic is routed correctly (Option A).
Load Balancer Requirement:
A-A clusters require a load balancer to distribute incoming traffic evenly across the active instances. This is crucial for balancing the load and providing high availability (Option C).
API Calls and Failovers:
Option B is incorrect because failovers in A-A clusters do not typically rely on API calls but are managed by the load balancer and the clustering mechanism itself.
Software-Defined Network (SDN) Failover:
Option D is incorrect as SDN is not specifically required for performing failovers in A-A clusters. The failover mechanism is typically managed by the load balancer and FortiGate's clustering technology.
FortiGate High Availability on AWS: FortiGate HA
You are troubleshooting network connectivity issues between two VMs deployed in AWS.
One VM is a FortiGate located on subnet "LAN" that is part of the VPC "Encryption". The other VM is a Windows server located on the subnet "servers" which is also in the "Encryption" VPC. You are unable to ping the Windows server from FortiGate.
What are two reasons for this? (Choose two.)
Windows Firewall Blocking Traffic:
The firewall on the Windows VM might be configured to block incoming ICMP traffic (ping requests). By default, Windows Firewall is set to block ICMP traffic, which could be a reason for the connectivity issue (Option A).
Security Group Configuration:
AWS Security Groups act as virtual firewalls for instances. If there is no rule allowing ICMP traffic in the security group attached to the Windows server, the ping requests from FortiGate will be blocked. An inbound allow ICMP rule must be added to the security group to permit this traffic (Option D).
Other Options Analysis:
Option B is incorrect because the default AWS Network Access Control List (NACL) allows all inbound and outbound traffic.
Option C is incorrect as AWS does allow ICMP traffic between subnets if properly configured with Security Groups and NACLs.