Key details for this exam, checked against the published exam outline
Each question shows the correct answer and an explanation of why it is right
Exhibit.
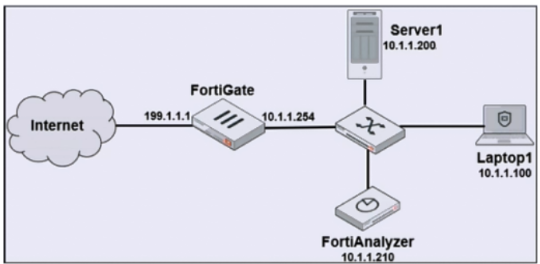
Laptop1 is used by several administrators to manage FortiAnalyzer. You want to configure a generic text filter that matches all login attempts to the web interface generated by any user other than admin'', and coming from Laptop1.
Which filter will achieve the desired result?
Study Guide p.83: generic text filters support field operators, including equality and inequality, for precise event-handler matching.
Technical Deep Dive: The correct answer is A. The required filter must match login operations to the GUI from Laptop1 and exclude the admin user. Option A includes the login operation, the correct GUI/IP value for Laptop1, and user!=admin. Option B uses the wrong IP address. Option C incorrectly matches user==admin, which is the opposite of the requirement. Option D lacks the correct performed_on GUI condition and has malformed inequality syntax. For event-handler filters, small syntax or field mistakes change the result completely.
Refer to the exhibit.
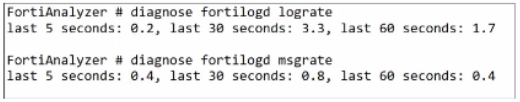
What can you conclude about the output?
Study Guide p.139: one compressed log message can contain multiple logs; message/log rate differences should be interpreted carefully.
Technical Deep Dive: The correct answer is C. If the exhibit shows message rate higher than log rate, that is not the normal relationship highlighted in the guide. FortiAnalyzer explains the normal case where one log message can contain multiple logs, making log rate higher than message rate. Options A and B cannot be concluded without indexing-completion or log-type breakdown information. Option D is wrong because these fortilogd rate outputs are not ADOM-specific unless a specific ADOM-scoped command is used.
Which two statements regarding the outbreak detection service are true? (Choose two.)
Study Guide p.134-p.135: Outbreak Detection Service is licensed and downloads related event handlers and reports from FortiGuard.
Technical Deep Dive: The correct answers are A and B. The Outbreak Detection Service requires a license and allows FortiAnalyzer to receive outbreak alerts and automatically download related event handlers and reports created by Fortinet for emerging threats. Option C is wrong because outbreak alerts are available on all ADOMs, not root only. Option D is not the core mechanism described in the guide; the feature is FortiGuard-delivered content within FortiAnalyzer, not simply email-based alerting.
(An analyst is using FortiAI on FortiAnalyzer to simplify certain tasks but is worried about exceeding the monthly token limit. Which query will take the fewest FortiAI tokens? (Choose one answer)
Study Guide p.118: token usage includes prompt and response; more text and larger responses consume more tokens.
Technical Deep Dive: The correct answer is A. The best low-token prompt is concise and scoped: it specifies the endpoint and limits the response to the past week. Option C is verbose and asks for all log entries, increasing both input and output tokens. Option B asks for all logs for the past week without limiting to an endpoint, which can generate a large response. Option D is short, but it lacks a time window, so it can produce a broader and more token-heavy response than option A.
Exhibit.
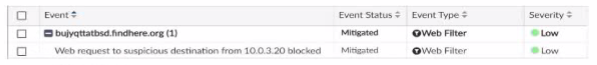
Which statement about the event displayed is correct?
Study Guide p.82: 'Unhandled' indicates the security event risk is considered open.
Technical Deep Dive: The displayed event is best interpreted as open/unhandled, so the correct answer is C. In FortiAnalyzer, event status is not just a label; it tells the analyst whether the risk still requires action. A risk source being isolated would map to Contained, while traffic being blocked or dropped maps to Mitigated. An incident being created from an event is a separate workflow action and cannot be concluded from the event status alone unless the exhibit explicitly shows the incident linkage.
You created a playbook on FortiAnalyzer that uses a FortiOS connector.
When configuring the FortiGate side, which type of trigger must be used so that the actions in an automation stitch are available in the FortiOS connector?
Study Guide p.202: FortiOS connector actions appear only after enabling an automation rule using the Incoming Webhook Call trigger on FortiGate.
Technical Deep Dive: The correct answer is D. A FortiAnalyzer playbook can list a FortiOS connector after FortiGate is added, but the available FortiOS actions depend on FortiGate-side automation rules. FortiGate must expose an Incoming Webhook trigger so FortiAnalyzer can call the automation stitch. A FortiAnalyzer Event Handler is used on FortiAnalyzer to generate events, not to expose FortiOS connector actions. Fabric Connector events and FortiOS Event Log triggers do not provide the FortiAnalyzer-to-FortiGate action handoff tested here.
Which two statements regarding FortiAnalyzer operating modes are true? (Choose two.)
Study Guide p.22-p.24: analyzer is the default mode; collector mode forwards logs, including to syslog/CEF, and mixed deployments improve scale.
Technical Deep Dive: The correct answers are A and D. In collector mode, FortiAnalyzer collects logs and forwards them to another analyzer, syslog server, or CEF server depending on forwarding mode. A topology using both collectors and analyzers can improve performance and regional scalability by offloading collection and keeping analysis/reporting on analyzer devices. Option B is wrong because analyzer mode is the default, not collector mode. Option C is wrong because collector mode has fewer features and does not provide reporting or event-management capabilities.
Exam domains verified against: Official Fortinet FCP_FAZ_AN-7.6 exam guide, last checked October 2026.
Explain Security Fabric integration and log collection. Explain log data flow, normalization, and parsing. Explain SOC features on FortiAnalyzer.
Sample question from this domain above: Q4
Analyze logs, events, and incidents. Analyze FortiView dashboards and widgets. Diagnose and troubleshoot report generation issues.
Sample question from this domain above: Q1
Configure and manage events and event handlers. Configure incidents and indicators. Configure playbooks and fabric automation. Troubleshoot playbook and fabric automation issues.
Explain the use of reports, charts, and datasets. Configure reports. Troubleshoot report generation.
Sample question from this domain above: Q3
Common questions about the exam itself

