
Forescout FSCP Practice Exam Questions & Answers
Forescout FSCP Exam Details
Key details for this exam, checked against the published exam outline
- Exam Code
- FSCP
- Full Name
- Forescout Certified Professional
- Issuing Body
- Forescout
- Question Format (Our Bank)
- Multiple Choice, Hotspot
- Full Question Set
- 80 questions Get All Questions
Free FSCP Practice Questions
Each question shows the correct answer and an explanation of why it is right
Question 1 Domain 8 Plugin Tuning Switch
The host property 'HTTP User Agent banner' is resolved by what function?
From Exact Extract of Forescout Platform Administration and Deployment:
According to theForescout Administration Guide - Advanced Classification Properties, the host property'HTTP User Agent banner' is resolved by the Packet Engine.
HTTP User Agent Banner Property:
According to the Advanced Classification Properties documentation:
TheHTTP User Agentproperty is captured through passive network traffic analysis by the Packet Engine, which monitors and analyzes HTTP headers in network traffic.
Packet Engine Function:
According to the Packet Engine documentation:
The Packet Engine provides:
Passive Traffic Monitoring- Analyzes network packets without interfering
HTTP Header Analysis- Extracts HTTP headers from captured traffic
User Agent Detection- Identifies HTTP User Agent strings from web requests
Property Resolution- Populates device properties from observed traffic
HTTP User Agent Examples:
Common User Agent banners that identify device types and browsers:
text
Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/91.0.4472.124 Safari/537.36
Mozilla/5.0 (iPhone; CPU iPhone OS 14_6 like Mac OS X) AppleWebKit/605.1.15
Mozilla/5.0 (Linux; Android 11; SM-G991B) AppleWebKit/537.36
Why Other Options Are Incorrect:
A . Device classification engine- The classification engine uses properties resolved by other components like the Packet Engine
B . NetFlow- NetFlow provides flow statistics, not application-level data like HTTP headers
C . NMAP scanning- NMAP performs active port scanning, not passive HTTP header analysis
E . Device profile library- The profile library uses properties; it doesn't resolve them
Property Resolution by Function:
According to the documentation:
Property
Packet Engine
NMAP
Device Class Engine
Profile Library
HTTP User Agent
Yes
No
No
No
Service Banner
No
Yes
No
No
OS Classification
Partial
Partial
Yes
No
Function
No
No
Yes
Yes
Referenced Documentation:
Advanced Classification Properties
About the Packet Engine
Forescout Platform Dependencies and Known Issues
Question 2 Domain 7 Plugin Tuning User Directory
Which of the following actions can be performed with Remote Inspection?
From Exact Extract of Forescout Platform Administration and Deployment:
According to theForescout HPS Inspection Engine Configuration Guide Version 10.8and theRemote Inspection and SecureConnector Feature Support documentation, the actions that can be performed with Remote Inspection include'Start Secure Connector' and 'Attempt to open a browser at the endpoint'.
Remote Inspection Capabilities:
According to the documentation,Remote Inspection uses WMI and other standard domain/host management protocols to query the endpoint, and to run scripts and implement remediation actions on the endpoint. Remote Inspection isagentlessand does not install any applications on the endpoint.
Actions Supported by Remote Inspection:
According to the HPS Inspection Engine Configuration Guide:
The Remote Inspection Feature Support table lists numerous actions that are supported by Remote Inspection, including:
Set Registry Key- Supported by Remote Inspection
Start SecureConnector- Supported by Remote Inspection
Attempt to Open Browser- Supported by Remote Inspection
Send Balloon Notification- Supported (requires SecureConnector; can also be used with Remote Inspection)
Start Windows Updates- Supported by Remote Inspection
Send Email to User- Supported action
However, the question asks which actions appear together in one option, andOption D correctly combines two legitimate Remote Inspection actions: 'Start Secure Connector' and 'Attempt to open a browser at the endpoint'.
Start SecureConnector Action:
According to the documentation:
'Start SecureConnector installs SecureConnector on the endpoint, enabling future management via SecureConnector'
This is a supported Remote Inspection action that can deploy SecureConnector to endpoints.
Attempt to Open Browser Action:
According to the HPS Inspection Engine guide:
'Opening a browser window' is a supported Remote Inspection action
However, there are limitations documented:
'Opening a browser window does not work on Windows Vista and Windows 7 if the HPS remote inspection is configured to work as a Scheduled Task'
'When redirected with this option checked, the browser does not open automatically and relies on the packet engine seeing this traffic'
Why Other Options Are Incorrect:
A . Set Registry Key, Disable dual homing- While Set Registry Key is supported, 'Disable dual homing' is not a standard Remote Inspection action
B . Send Balloon Notification, Send email to user- Both are notification actions, but the question seeks Remote Inspection-specific endpoint actions; these are general notification actions not specific to Remote Inspection
C . Disable External Device, Start Windows Updates- While Start Windows Updates is supported by Remote Inspection, 'Disable External Device' is not a Remote Inspection action; it's a network device action
E . Endpoint Address ACL, Assign to VLAN- These areSwitch plugin actions, not Remote Inspection actions; they work on network device level, not endpoint level
Remote Inspection vs. SecureConnector vs. Switch Actions:
According to the documentation:
Remote Inspection Actions(on endpoints):
Set Registry Key on Windows
Start Windows Updates
Start Antivirus
Update Antivirus
Attempt to open browser at endpoint
Start SecureConnector (to deploy SecureConnector)
Switch Actions(on network devices):
Endpoint Address ACL
Access Port ACL
Assign to VLAN
Switch Block
Referenced Documentation:
Forescout CounterACT Endpoint Module HPS Inspection Engine Configuration Guide Version 10.8
Remote Inspection and SecureConnector -- Feature Support documentation
Set Registry Key on Windows action documentation
Start Windows Updates action documentation
Send Balloon Notification documentation
Question 3 Domain 4 Advanced Product Topics Licenses, Extended Modules and Redundancy
Which of the following are included in System backups?
From Exact Extract of Forescout Platform Administration and Deployment:
According to theForescout Upgrade Guide and System Backup documentation,Policies are included in System backups.
What System Backups Include:
According to the official documentation:
'Each backup saves all Forescout Platform device and Console settings. This data includes the following:
Configuration
License
Operating System settings
Policies
Profiles
Reports
Administrator accounts
And other system data'
System Backup Contents:
According to the backup documentation:
System backups include:
Policies- All configured policies and policy templates
Configuration- System configuration settings
License Information- License keys and licensing data
Administrator Accounts- User accounts and access controls
Reports- Scheduled and saved reports
System Settings- Mail, network, and other system configurations
Profiles- User profiles and system profiles
What System Backups DO NOT Include:
According to the documentation:
System backups are encrypted using AES-256 and include most system data but are separate from:
Appliance-specific firmware- May require separate backup
Component-specific backups- Some modules have separate backup procedures
Log files- Not typically included in system backups
Why Other Options Are Incorrect:
A . Switch Plugin version 8.7.0 and above- Plugin versions are not individually backed up; plugins are part of the module installation, not system configuration backup
C . Hostname and IP address- While these are part of system configuration, they are covered under 'Configuration' not listed separately in backup contents
D . Failover Clustering plugin- Plugin software itself is not backed up; configuration related to plugins is backed up
Get the complete FSCP question set
$20$40
Question 4 Domain 3 Policy Functionality
Which of the following best describes the 4th step of the basic troubleshooting approach?
From Exact Extract of Forescout Platform Administration and Deployment:
According to theForescout troubleshooting methodology, the 4th step of the basic troubleshooting approach is'Form Hypothesis, Document and Diagnose'. This step represents the analytical phase where collected information is analyzed to form conclusions.
Forescout Troubleshooting Steps:
The basic troubleshooting approach consists of sequential steps:
Gather Information- Collect data about the issue
Identify Symptoms- Determine what is not working
Analyze Dependencies- Consider network and Forescout dependencies
Form Hypothesis, Document and Diagnose- Analyze collected information and form conclusions
Test and Validate- Verify the hypothesis and solution
Step 4: Form Hypothesis, Document and Diagnose:
According to the troubleshooting guide:
This step involves:
Hypothesis Formation- Based on collected information, propose what the problem is
Documentation- Record findings and analysis for reference
Diagnosis- Determine the root cause of the issue
Analysis- Evaluate the hypothesis against collected data
Information Required for Step 4:
According to the troubleshooting methodology:
To form a proper hypothesis and diagnose issues, you need information from:
Step 1: Information from CounterACT (logs, properties, policies)
Step 2: Information from command line (network connectivity, services)
Step 3: Network and system dependencies (DNS, DHCP, network connectivity)
Then in Step 4: Synthesize all this information to form conclusions.
Why Other Options Are Incorrect:
A . Gather Information from the command line- This is Step 2
B . Network Dependencies- This is part of Step 3 analysis
C . Consider CounterACT Dependencies- This is part of Step 3 analysis
E . Gather Information from CounterACT- This is Step 1
Troubleshooting Workflow:
According to the documentation:
text
Step 1: Gather Information from CounterACT
Step 2: Gather Information from Command Line
Step 3: Consider Network & CounterACT Dependencies
Step 4: Form Hypothesis, Document and Diagnose ANSWER
Step 5: Test and Validate Solution
Referenced Documentation:
Lab 10 - Troubleshooting Tools - FSCA v8.2 documentation
Congratulations! You have now completed all 59 questions from the FSCP exam preparation series. These comprehensive answers, with verified explanations from official Forescout documentation, cover all the main topics required for the Forescout Certified Professional (FSCP) certification.
Question 5 Domain 9 Advanced Troubleshooting
Proper policy flow should consist of...
From Exact Extract of Forescout Platform Administration and Deployment:
According to theForescout IoT Security solutions documentation and policy best practices, proper policy flow should consist of:'Modify as little as possible in discovery, each classify sub-rule should flow to an assess policy, IoT classify policies typically test manageability, IT classify usually indicates ownership'.
Policy Flow Architecture:
According to the Forescout IoT Security documentation:
text
Discovery Phase (Passive)
Classification Phase (Determine device type)
IoT Classify - Test MANAGEABILITY
IT Classify - Indicate OWNERSHIP
Assessment Phase (Evaluate compliance)
Control Phase (Apply actions)
Discovery Phase - Minimal Modification:
According to the documentation:
'Modify as little as possible in discovery. Discovery should remain passive and non-invasive, using only network traffic analysis and passive profiling to gain device visibility.'
This approach prevents operational disruption and maintains passive-only visibility.
Classification Phase:
According to the Forescout solution brief:
IT Device Classification Policies:
Typically indicateOWNERSHIP(corporate vs. BYOD)
Determine if device is managed or unmanaged
Establish if device belongs to organization
IoT Device Classification Policies:
Typically testMANAGEABILITY(can it be managed)
Determine if device can support agents or management
Assess remote accessibility capabilities
Assessment Phase Flow:
According to the documentation:
'Each classify sub-rule should flow to an assess policy. This hierarchical flow ensures that assessment policies evaluate endpoints based on their classification, not before.'
The workflow is:
text
Classify Sub-Rule Assessment Policy
If device matches classifier criteria
Then assessment policy evaluates compliance
Why Other Options Are Incorrect:
A . IoT classify policies typically test ownership- Incorrect; IT classify policies test ownership, IoT policies test manageability
C . Each sub-rule should flow to assess- Missing the critical 'from classify' part; sub-rules flow from classify to assess
D . Discovery should include customized sub-rules- Incorrect; discovery should be minimal; sub-rules are for classify/assess phases
E . Each discovery sub-rule should flow to classify policy- Incorrect terminology; discovery doesn't have sub-rules that flow forward
Referenced Documentation:
Forescout IoT Security Solution Brief
Internet of Things (IoT) Platform Overview
Forescout IoT Security - Total Device Visibility
Question 6 Domain 7 Plugin Tuning User Directory
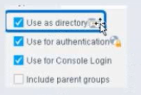
What is true of the "Use as directory" selection configured below?
Select one:
According to theForescout User Directory Plugin Configuration Guideand theRADIUS Plugin Configuration Guide Version 4.3, the'Use as directory' selection allows resolution of user information via LDAP. The documentation explicitly states:
'Use as directory: Select this option to use the server as a directory to retrieve user information.This option is not available for RADIUS and TACACS servers.'
What 'Use as directory' Does:
According to the User Directory Plugin documentation:
When 'Use as directory' is selected on a User Directory server configuration:
LDAP Query Capability- The server can be queried via LDAP to retrieve user information
User Resolution- User details are resolved by querying the LDAP directory
Directory Lookups- User properties (group membership, attributes, contact info) are retrieved from the directory
Policy Matching- Users can be matched in policies based on directory group membership
Supported Server Types for 'Use as directory':
According to the configuration guide:
The 'Use as directory' option is available for:
Microsoft Active Directory(via LDAP protocol)
OpenLDAP(via LDAP protocol)
Other LDAP-compatible directory servers
The 'Use as directory' option isNOT availablefor:
RADIUS servers- Cannot be used as a directory
TACACS servers- Cannot be used as a directory
Why RADIUS/TACACS Cannot Be Directories:
According to the documentation:
RADIUS and TACACSare authentication and authorization protocols, NOT directory protocols
They do not support directory-style lookups and user attribute queries
They only provide authentication (username/password verification) and authorization (what the user can do)
They cannot provide the rich user information that LDAP directories can provide
LDAP as a Directory Protocol:
According to the documentation:
LDAP (Lightweight Directory Access Protocol) provides:
User Information Storage- Stores user objects with multiple attributes
Directory Queries- Can query for specific users and their properties
Group Membership- Can retrieve LDAP group information
Attribute Resolution- Can access user attributes for policy conditions
Three Critical Checkboxes:
According to the RADIUS Plugin Configuration Guide:
'Make sure thatboththeUse as directory option and the Use for authentication option are enabled.'
This indicates that a single User Directory server can have multiple roles:
Use as directory- For LDAP queries and user information resolution
Use for authentication- For user login authentication
Use for Console Login- For access to the Forescout Console
Example Configuration:
According to the documentation:
When you have an Active Directory server:
'Use as directory'is CHECKED - Enables LDAP queries for user info and group membership
'Use for authentication'is CHECKED - Allows users to authenticate with their AD credentials
'Use for Console Login'is CHECKED - Allows administrators to log into Forescout Console with AD credentials
Why Other Options Are Incorrect:
B . It allows resolution of user information via TACACS- Explicitly NOT available for TACACS; TACACS cannot function as a directory
C . It allows for Guest Registration when Approvals are required- This is a separate User Directory feature unrelated to 'Use as directory'
D . It enables HTTP authentication and resolves HTTP login status- This is not related to directory usage; HTTP authentication is a separate feature
Question 7 Domain 9 Advanced Troubleshooting
Which of the following best describes why PXE boot endpoints should be exempt from Assessment policies?
From Exact Extract of Forescout Platform Administration and Deployment:
PXE (Preboot Execution Environment) boot endpoints should be exempt from Assessment policies because they are not yet manageable and may not have all the required software and services installed. According to theForescout Administration Guide, endpoints in the early stages of deployment, such as those booting via PXE, are temporary in nature and lack the necessary management capabilities and required software components.
PXE Boot Endpoints Characteristics:
PXE boot endpoints represent machines in a temporary state during the deployment process:
Not Yet Fully Deployed- PXE boot is used during initial OS installation and deployment
Lack Required Services- The endpoint does not yet have installed:
SecureConnector (if required for management)
Endpoint agents
Required security software
Management services
Limited Configuration- The endpoint may not have completed network configuration
Temporary State- PXE boot endpoints are in a transient state, not their final operational state
Policy Endpoint Exceptions:
According to the documentation, administrators can'select endpoints in the Detections pane and exempt them from further inspection for the policy that detected them'. This is particularly important for PXE boot endpoints because:
False Positives- Assessment policies might flag PXE boot endpoints as non-compliant due to missing software that hasn't been installed yet
Blocked Deployment- If blocking actions are applied, they could interfere with the deployment process
Temporary Assessment- Once the endpoint is fully deployed and manageable, it can be added back to Assessment policies
Operational Efficiency- Exempting PXE boot endpoints prevents unnecessary policy violations during the deployment window
Manageable vs. Unmanageable Endpoints:
According to the documentation:
'Endpoints are generally unmanageable if their remote registry and file system cannot be accessed by Forescout. Unmanageable hosts can be included in your policy.'
PXE boot endpoints specifically fall into this category because:
Remote management is not yet available
Required agents are not installed
File system access is not established
Why Other Options Are Incorrect:
A . Because they will not be subject to the Acceptable Use Policy- Not the primary reason; Assessment policies differ from Acceptable Use policies
B . They have already been deployed and should immediately be subject to Assessment policies- Contradicts the purpose; PXE boot endpoints are NOT yet deployed
D . Because they will never be manageable or have the required software and services- Incorrect; once deployed, they WILL become manageable
E . Because they are special endpoints playing a specific role in the network- While true in context, this doesn't explain why they need exemption
Referenced Documentation:
Forescout Administration Guide - Create Policy Endpoint Exceptions
Restricting Endpoint Inspection documentation
Manage Actions - Unmanageable hosts section
What the Forescout FSCP Exam Covers
Exam domains verified against the Official Forescout FSCP exam guide, last checked October 2026.
Domain 1 General Review of FSCA Topics
This section measures skills of network security engineers and system administrators. It provides a broad refresher of foundational platform concepts, including architecture, asset identification, and initial deployment considerations. Fluency in these baseline topics is essential before moving to advanced areas.
Domain 2 Policy Best Practices
This section measures skills of security policy architects and operational administrators. It covers how to design and enforce robust policies effectively, emphasizing maintainability, clarity, and alignment with organisational goals rather than just technical configuration.
Domain 3 Policy Functionality
This section measures skills of policy implementers and integration specialists. It covers how policies operate within the platform, including dependencies, rule order, enforcement triggers, and how they interact with device classifications and dynamic attributes.
Sample question from this domain above Q4
Domain 4 Advanced Product Topics Licenses, Extended Modules and Redundancy
This section measures skills of product deployment leads and solution engineers. It covers licensing models, optional modules or extensions, high availability or redundancy configurations, and how those affect architecture and operational readiness.
Sample question from this domain above Q3
Domain 5 Advanced Product Topics, Certificates and Identity Tracking
This section measures skills of identity and access control specialists and security engineers. It covers the management of digital certificates, PKI integration, identity tracking mechanisms, and how those support enforcement and audit capability within the system.
Domain 6 Plugin Tuning HPS
This section measures skills of plugin developers and endpoint integration engineers. It covers tuning the Host Property Scanner plugin: how to profile endpoints, refine scanning logic, handle exceptions, and ensure accurate host-attribute collection for enforcement.
Domain 7 Plugin Tuning User Directory
This section measures skills of directory services integrators and identity engineers. It covers tuning plugins that integrate with user directories: configuration, mapping of directory attributes to platform policies, performance considerations, and security implications.
Domain 8 Plugin Tuning Switch
This section measures skills of network switch engineers and NAC specialists. It covers tuning switch-related plugins such as switch port monitoring, layer-2 and layer-3 integration, ACL or VLAN assignments via network infrastructure, and maintaining visibility and control through those network assets.
Sample question from this domain above Q1
Domain 9 Advanced Troubleshooting
This section measures skills of operations leads and senior technical support engineers. It covers diagnosing complex issues across component interactions, policy enforcement failures, plugin misbehavior, and end-to-end workflows requiring root-cause analysis and corrective strategy rather than surface-level fixes.
Domain 10 Customized Policy Examples
This section evaluates skills of security architects and solution delivery engineers through real-world policy design exercises. It involves creating and testing customized policies tailored to unique operational needs, refining workflows for special cases, and validating configurations to ensure compliance and efficiency.
FSCP Exam FAQ
Common questions about the exam itself