
F5 Networks F5CAB5 Practice Exam Questions & Answers
F5 Networks F5CAB5 Exam Details
Key details for this exam, checked against the published exam outline
- Exam Code
- F5CAB5
- Full Name
- BIG-IP Administration Support and Troubleshooting (F5CAB5)
- Issuing Body
- F5 Networks
- Question Format (Our Bank)
- Multiple Choice
- Delivery
- Online proctored or at a Pearson VUE test centre or via Certiverse
- Eligibility
- Basic understanding of how to install, configure and upgrade BIG-IP
- Full Question Set
- 65 questions Get All Questions
Free F5CAB5 Practice Questions
Each question shows the correct answer and an explanation of why it is right
Question 1 Domain 4 Identify the reason a virtual server is not working as expected
A BIG-IP Administrator uses backend servers to host multiple services per server. There are multiple virtual servers and pools defined, referencing the same backend servers. Which load balancing algorithm is most appropriate to have an equal number of connections on each backend server?17
When load balancing is not working as 23expected and connections appear skewed across physical hardware, the administrator must distinguish between 'member'24 and 'node' level balancing. A 'member' refers to a specific IP and Port combination (e.g., 10.1.1.1:80), whereas a 'node' refers to the underlying IP address (10.1.1.1) regardless of the port25. If a single server hosts multiple services (Web, FTP, API) across different pools, using 'Least Connections (member)' would only balance connections within each individual pool26. This could lead to a scenario where one server is overwhelmed because it is winning the 'least connections' count in three different pools simultaneously. By selecting 'Least Connections (node),' the BIG-IP tracks the total number of concurrent connections to the physical IP address across all pools it belongs to27. This ensures that the administrator can maintain an equal distribution of work across the hardware, preventing performance degradation on backend servers that host multiple application services.
Question 2 Domain 5 Identify the reason a pool is not working as expected
Users report that traffic is negatively affected every time a BIG-IP device fails over. The traffic becomes stabilized after a few minutes. What should the BIG-IP Administrator do to reduce the impact of future failovers?
When traffic 'stabilizes after a few minutes' following a failover, it points to a network-level performance issue involving ARP cache on upstream routers and switches. Each BIG-IP interface has a unique hardware MAC address. During failover, the Standby device takes over the floating IP address, but the upstream switch still associates that IP with the MAC of the now-offline device. Traffic is lost until the switch learns the new MAC or its ARP entry expires. 'MAC Masquerading' solves this by creating a shared, virtual MAC address for the floating traffic group. This virtual MAC is used by whichever device is currently active. Because the MAC address for the virtual server IP never changes from the perspective of the network, the upstream devices do not need to update their ARP tables. This troubleshooting solution eliminates the delay associated with failover, providing a seamless transition and ensuring that application traffic flow is not disrupted when the BIG-IP HA state changes.
Question 3 Domain 3 Identify the reason load balancing is not working as expected
A device group is currently in theChanges Pendingsync status. How can the BIG-IP Administrator determine which member of the device group has the most recent configuration? (Choose one answer)
When a BIG-IP device group shows aChanges Pendingstatus, it indicates that one or more devices in the group have configuration changes that have not yet been synchronized to the other members. To identifywhich device has the most recent (authoritative) configuration, the administrator must view the detailed synchronization status at thedevice group level.
The correct location isDevice Management > Device Groups (Option D). Within this menu, the BIG-IP Configuration Utility displays each device group along with its synchronization status and provides details about which device has pending changes. From this view, the administrator can clearly see which device is marked as havingchanges pending, making it the source device that should be used to initiate aSync to Groupoperation.
The other options do not provide the required level of detail:
Device Management > Overview (Option A)shows general HA status but not configuration ownership.
Device Management > Devices (Option B)lists devices but does not clearly identify which one holds unsynchronized changes.
System > High Availability (Option C)focuses on failover and traffic groups, not configuration sync state.
This workflow aligns with BIG-IP best practices for configuration synchronization and ensures changes are propagated correctly without overwriting newer configurations.
Get the complete F5CAB5 question set
$20$40
Question 4 Domain 2 Identify network level performance issues
Where should the BIG-IP Administrator go in the GUI to verify the status of pool members of a pool?
To verify the specific health and availability status of individual members within a specific pool, the administrator must navigate to the Members tab of that specific pool.
Navigation Path: The correct path is Local Traffic > Pools > Pool List, then clicking on the name of the
Why Option A is correct: While you can see a general status summary on the Pool List page (Option B), that page only shows the status of the pool as a whole. To troubleshoot why a pool is not working or to see which specific member is down, you must drill down into the Members tab.
Evaluation of Other Options:
Local Traffic ---> Pools (Option B): This leads to the Pool List. It shows the aggregate status of all pools but does not list individual member details or their specific monitor results without further clicking.
Local Traffic ---> Virtual Servers ---> Statistics (Option C): This path shows traffic statistics (bits in/out, connections) for virtual servers, not the health monitor status of individual pool members.
Local Traffic ---> Nodes (Option D): While this shows the health of the underlying IP address (Node), it does not show the status of the specific service (Port/Member) within a pool. A Node might be 'Up' (ICMP), while the Pool Member is 'Down' (HTTP failure).
Question 5 Domain 6 Given a scenario, review basic stats to confirm functionality
Clients report that they cannot reach the virtual server vs-production on port 80, but are able to ping the virtual server address. The configuration is shown below:
Plaintext
ltm virtual vs-production {
destination 10.99.20.50:http
ip-protocol tcp
mask 255.255.255.255
profiles {
http {}
tcp {}
}
source 192.168.0.0/16
translate-address enabled
translate-port enabled
vlans {
external
}
vlans-enabled
}
What is the cause?
The issue is caused by the Source Address restriction configured on the virtual server.
Source Filter: The configuration contains the line source 192.168.0.0/16. This acts as an implicit Access Control List (ACL). The virtual server will only accept and process TCP connections if the client's source IP address falls within the 192.168.x.x range.
Why Ping Works: ICMP (Ping) is handled by the Virtual Address object, not the Virtual Server object. Unless ICMP is specifically disabled on the Virtual Address, it will respond to pings from any subnet, even if the Virtual Server itself is restricted by a source filter or is even disabled.
Evaluation of Other Options:
Disabled (Option A): If the VS were disabled, the configuration would typically show disabled or state down, and the symptoms would be similar, but the source filter is a more specific 'misconfiguration' in this context.
Port 80 (Option C): The configuration destination 10.99.20.50:http explicitly confirms it is listening on port 80.
Unallowed Subnet: If a client from a different network (e.g., 10.10.1.5) tries to connect, the BIG-IP will silently drop the connection or send a reset because it does not match the defined source criteria.
Question 6 Domain 3 Identify the reason load balancing is not working as expected
A BIG-IP Administrator needs to view the CPU utilization of a particular Virtual Server. Which section of the Configuration Utility should the administrator use for this purpose?
When a BIG-IP system experiences high overall CPU usage, troubleshooting requires identifying which specific application or service is the primary consumer of resources. While the system-wide performance graphs provide a global view, the granular data necessary to isolate a 'top talker' is found in the 'Local Traffic' statistics. Navigating to Statistics > Module Statistics > Local Traffic > Virtual Servers allows the administrator to see specific metrics for each configured virtual server, including the number of packets processed, current connections, and critical CPU cycles consumed. This is essential for troubleshooting performance issues where an inefficient iRule, high SSL handshake volume, or complex L7 profiles (like Compression or ASM) might be overtaxing the Traffic Management Microkernel (TMM) for one specific application. By reviewing these basic stats, an administrator can determine if a performance bottle-neck is a system-wide h1ardware issue or if it is isolated to a single virtual server, enabling targeted remediation such as optimizing iRule logic or moving the high-load virtual server to a dedicated device.
Question 7 Domain 2 Identify network level performance issues
Refer to the exhibit.
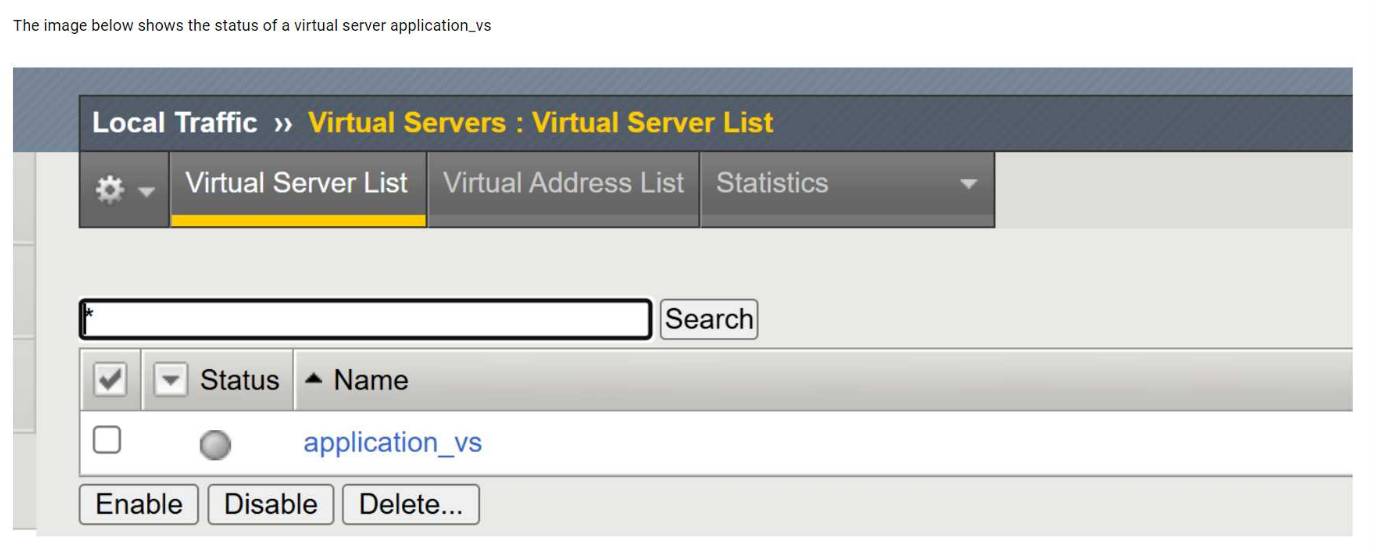
The image shows the status of a virtual server namedapplication_vsin the BIG-IP Configuration Utility.
What is the cause of the status shown? (Choose two answers)
The exhibit shows the virtual serverapplication_vswith a status indicating it isoffline but enabled. In BIG-IP terminology, this status means the virtual server itself is administratively enabled, but it is unable to pass traffic becauseno usable pool members are available.
Two common and documented causes for this condition are:
Pool member(s) administratively disabled (Option A):When all pool members are administratively disabled, BIG-IP removes them from load-balancing decisions. Even though the virtual server remains enabled, it has no available pool members to send traffic to, resulting in an offline status.
Node(s) administratively disabled (Option C):Pool members inherit the status of their parent nodes. If a node is administratively disabled, all associated pool members are also marked unavailable. This condition causes the virtual server to show as offline, even though the virtual server configuration itself is correct.
The other options are incorrect:
Forced offline pool members (Option B)result in a different operational intent and are explicitly set for maintenance scenarios.
Virtual server administratively disabled (Option D)would show the virtual server as disabled, not enabled/offline.
This behavior is consistent with BIG-IP traffic management logic and is commonly verified by reviewingpool and node availability stateswhen diagnosing virtual server availability issues.
What the F5 Networks F5CAB5 Exam Covers
Exam domains verified against the Official F5 Networks F5CAB5 exam guide, last checked November 2026.
Domain 1 Determine resource utilization
Distinguish between control plane and data plane resources to understand where processing occurs. Identify CPU statistics per virtual server and interpret statistics for interfaces to spot performance bottlenecks.
Domain 2 Identify network level performance issues
Identify when a packet capture is needed to diagnose problems and interpret availability status of interfaces. Recognize when drops are occurring and distinguish between TCP profiles to optimize throughput.
Domain 3 Identify the reason load balancing is not working as expected
Review persistence settings, priority group activation, and rate and connection limits that prevent balanced traffic distribution. Check for misconfigurations in health checks and action on service down settings.
Domain 4 Identify the reason a virtual server is not working as expected
Check the availability status of the virtual server and identify conflicting or misconfigured profiles that block requests. Verify the IP address and port are configured correctly for the intended traffic.
Sample question from this domain above Q1
Domain 5 Identify the reason a pool is not working as expected
Determine why health monitors have marked pool members down and confirm they are in the active priority group. Review the current configured and availability status of the pool and its members.
Sample question from this domain above Q2
Domain 6 Given a scenario, review basic stats to confirm functionality
Interpret traffic object statistics and network configuration statistics to verify the system is operating as designed. Use statistics to prove that virtual servers, pools, and profiles are configured and functioning correctly.
Sample question from this domain above Q5
Domain 7 Given a scenario, interpret traffic flow
Explain how application client-server communication flows through BIG-IP and interpret traffic graphs showing SNMP results. Trace packets from client through the BIG-IP to the backend server to understand path and transformations.
F5CAB5 Exam FAQ
Common questions about the exam itself
What is the difference between control plane and data plane troubleshooting on BIG-IP?
Do I need to pass the other BIG-IP Administration exams before taking F5CAB5?
How do I interpret packet captures to diagnose BIG-IP performance issues?
What job role is F5CAB5 designed for?
How long should I prepare for the F5CAB5 exam?
Can I reschedule my F5CAB5 exam if I need to?
How many times can I retake the F5CAB5 exam if I fail?
Which F5CAB5 objective area do most candidates find most challenging?
What is the passing score for F5CAB5?
How does F5CAB5 relate to the old F5 201 TMOS Administration exam?
Other F5 Networks Exams
Free practice questions for more F5 Networks certification exams