
F5 Networks F5CAB2 Practice Exam Questions & Answers
F5 Networks F5CAB2 Exam Details
Key details for this exam, checked against the published exam outline
- Exam Code
- F5CAB2
- Full Name
- BIG-IP Administration Data Plane Concepts
- Issuing Body
- F5 Networks
- Question Format (Our Bank)
- Multiple Choice
- Official Exam Fee
- USD 50. USD 65
- Delivery
- Online proctored via Certiverse (requires camera access) or test center proctored via Pearson VUE
- Full Question Set
- 87 questions Get All Questions
Free F5CAB2 Practice Questions
Each question shows the correct answer and an explanation of why it is right
Question 1 Domain 5 Explain high availability (HA) concepts
A virtual server is listening at 10.10.1.100:any and has the following iRule associated with it:
when CLIENT_ACCEPTED { if {[TCP::local_port] equals 21 } { pool
ftppool } elseif {[TCP::local_port] equals 23 } { pool telnetpool }
If a user connects to 10.10.1.100 and port 22, which pool will receive the request?
The iRule checks if the TCP local port equals 21 (FTP) or 23 (Telnet). When a user connects to port 22, neither condition is met. The iRule does not contain an else clause to handle ports other than 21 and 23, so no pool selection is made by the iRule. The request will be rejected or handled according to the virtual server's default behavior, as no valid pool destination is specified. In practice, this would typically result in a connection error or be handled by the virtual server's default pool if one is configured.
Question 2 Domain 1 Explain the relationship between interfaces, trunks, VLANs, self-IPs, routes and their status/statistics
Refer to the exhibit.
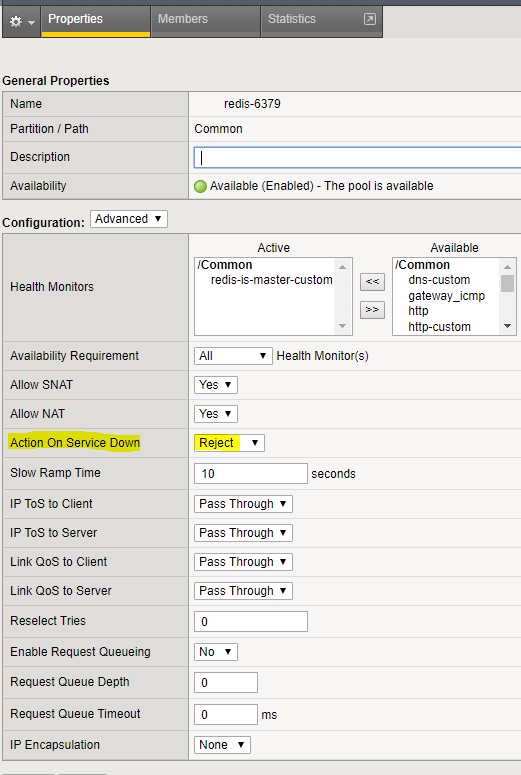
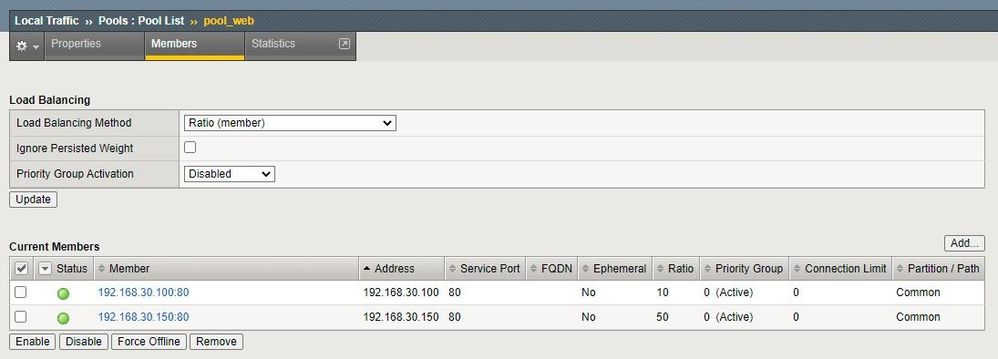
The BIG-IP Administrator needs to avoid overloading any of the pool members with connections when they become active. What should the BIG-IP Administrator configure to meet this requirement? (Choose one answer)
This question focuses on connection behavior when pool members transition from down to up, which is a classic data plane consideration in BIG-IP environments.
What problem is being solved?
When a pool member:
Recovers from a failure
Is enabled after maintenance
Transitions from inactive to active
...it can suddenly receive a large burst of new connections, especially when using load-balancing methods such as Least Connections. This sudden surge can overload the server.
Why Slow Ramp Time is the correct solution:
Slow Ramp Time is a pool-level setting that:
Gradually increases the number of connections sent to a newly available pool member
Prevents sudden spikes in traffic
Allows the server to warm up (application cache, JVM, DB connections, etc.)
From BIG-IP Administration Data Plane Concepts:
Slow Ramp Time controls the rate at which BIG-IP increases load to a pool member that has just become available
During the ramp period, BIG-IP artificially increases the member's connection count, making it appear ''busier'' and therefore less attractive for new connections
This directly satisfies the requirement to avoid overloading pool members when they become active.
Why the Other Options Are Incorrect:
B . Different Ratio for each member
Ratios control relative distribution under normal operation
They do not prevent a sudden surge when a member becomes active
C . Action On Service Down to Reselect
Controls persistence behavior when a member goes down
Has no impact on connection ramp-up when a member comes back online
D . Same Priority Group to each member
Affects failover logic between priority groups
Does not control connection rate or ramp-up behavior
Key Data Plane Concept Reinforced:
To protect backend servers during recovery events, BIG-IP provides Slow Ramp Time, ensuring graceful reintroduction of traffic and preventing connection storms that can occur during high-load scenarios.
Question 3 Domain 1 Explain the relationship between interfaces, trunks, VLANs, self-IPs, routes and their status/statistics
and their status/statistics]
Refer to the exhibit.
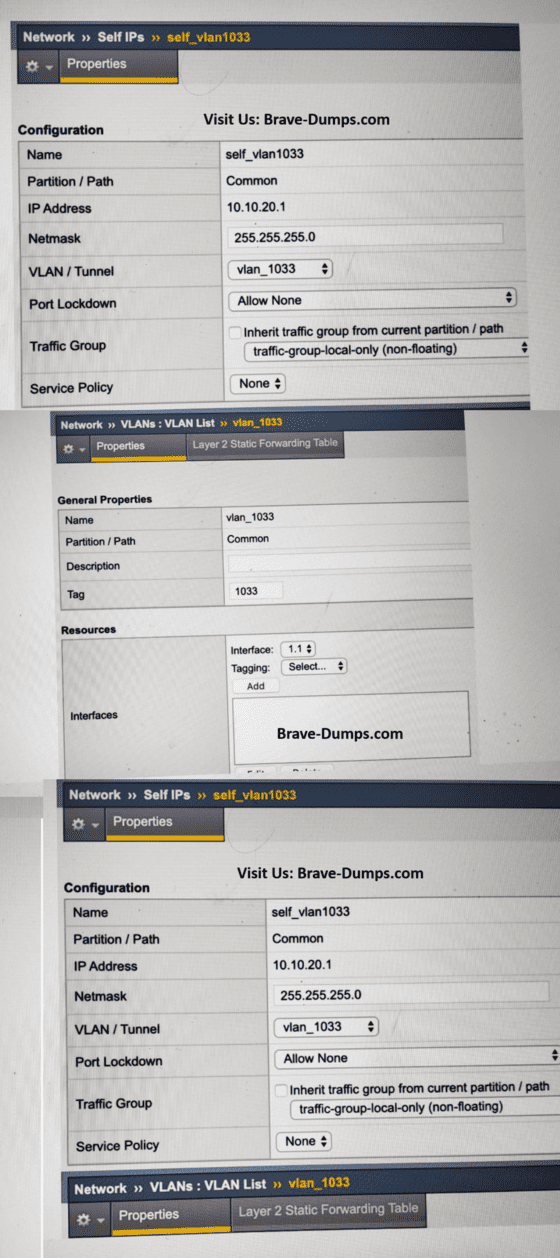
The network team creates a new VLAN on the switches. The BIG-IP Administrator creates a new VLAN and a Self IP on the BIG-IP device, but the servers on the new VLAN are NOT reachable from the BIG-IP device.
Which action should the BIG-IP Administrator take to resolve this issue? (Choose one answer)
For BIG-IP to send or receive traffic on a VLAN, that VLAN must be bound to a physical interface or a trunk. Creating a VLAN object and a Self IP alone is not sufficient to establish data-plane connectivity.
From the exhibit:
The VLAN (vlan_1033) exists and has a tag defined.
A Self IP is configured and associated with the VLAN.
However, traffic cannot reach servers on that VLAN.
This indicates a Layer 2 connectivity issue, not a Layer 3 or HA issue.
Why assigning a physical interface fixes the problem:
BIG-IP VLANs do not carry traffic unless they are explicitly attached to:
A physical interface (e.g., 1.1), or
A trunk
Without an interface assignment, the VLAN is effectively isolated and cannot transmit or receive frames, making servers unreachable regardless of correct IP addressing.
Why the other options are incorrect:
A . Set Port Lockdown to Allow All
Port Lockdown controls which services can be accessed on the Self IP (management-plane access), not whether BIG-IP can reach servers on that VLAN.
B . Change Auto Last Hop to enabled
Auto Last Hop affects return traffic routing for asymmetric paths. It does not fix missing Layer 2 connectivity.
D . Create a Floating Self IP address
Floating Self IPs are used for HA failover. They do not resolve reachability issues on a single device when the VLAN itself is not connected to an interface.
Conclusion:
The servers are unreachable because the VLAN has no physical interface assigned. To restore connectivity, the BIG-IP Administrator must assign a physical interface (or trunk) to the VLAN, enabling Layer 2 traffic flow.
Get the complete F5CAB2 question set
$20$40
Question 4 Domain 4 Identify the different virtual server types
A BIG-IP Administrator assigns the default HTTP health monitor to a pool that has three members listening on port 80. When the administrator connects to each pool member using the curl utility, two of the members respond with a status of 404 Not Found, while the third responds with 200 OK. What will the pool show for member availability? (Choose one answer)
In BIG-IP LTM, health monitors are used to determine the availability of pool members and directly influence traffic flow decisions in the data plane.
Key characteristics of the default HTTP monitor according to BIG-IP Administration Data Plane Concepts:
Sends an HTTP request (typically GET /)
Expects an HTTP response code of 200 OK
Any response other than 200 is treated as a monitor failure
A failed monitor causes the pool member to be marked offline (down)
In this scenario:
Two pool members return 404 Not Found
A 404 response indicates that the requested object was not found
This does not meet the success criteria of the default HTTP monitor
These two members are therefore marked offline
One pool member returns 200 OK
This matches the expected response
The member is marked online
Resulting Pool Member Availability:
2 members: Offline
1 member: Online
Why the Other Options Are Incorrect:
B -- 404 responses are not considered healthy by the default HTTP monitor
C -- At least one member responds with the expected 200 OK
D -- Members returning 404 responses fail the monitor and cannot be marked online
Key Data Plane Concept Reinforced:
BIG-IP health monitors make binary availability decisions based strictly on configured success criteria. For HTTP monitors, response codes matter---404 is a failure, even if the service is technically reachable.
Question 5 Domain 5 Explain high availability (HA) concepts
their status/statistics]
A BIG-IP Administrator needs to have a BIG-IP linked to two upstream switches for resilience of the external network. The network engineer who is going to configure the switch instructs the BIG-IP Administrator to configure interface binding with LACP. Which configuration should the administrator use?
In BIG-IP terminology, a Trunk is the object used to implement Link Aggregation (IEEE 802.3ad/802.1AX). When a network engineer refers to 'interface binding' or 'EtherChannel' with LACP, the BIG-IP equivalent is a Trunk.
LACP (Link Aggregation Control Protocol): This is a protocol that allows the BIG-IP system to communicate with the upstream switches to negotiate the bundling of multiple physical links into a single logical link.
Resilience and Redundancy: By creating a trunk that includes interfaces connected to two different switches (typically configured as a VPC, VSS, or MLAG cluster on the switch side), the administrator ensures that the BIG-IP remains reachable even if one physical interface or one switch fails.
Data Plane Logic: The BIG-IP treats the trunk as a single Layer 2 interface. VLANs are then associated with the trunk rather than individual physical ports.
Why the other options are incorrect:
Option B: Trunks aggregate physical interfaces. While VLANs are associated with trunks, the trunk configuration itself does not 'list' MAC addresses of the switches; it uses LACP to negotiate the connection.
Options C & D: Virtual Servers are Layer 4-7 objects used for traffic processing and load balancing. They do not possess 'LACP profiles,' nor are physical interfaces or management IPs treated as pool members for the purpose of link aggregation.
Question 6 Domain 3 Determine expected traffic behavior based on configuration
Refer to the exhibit above.
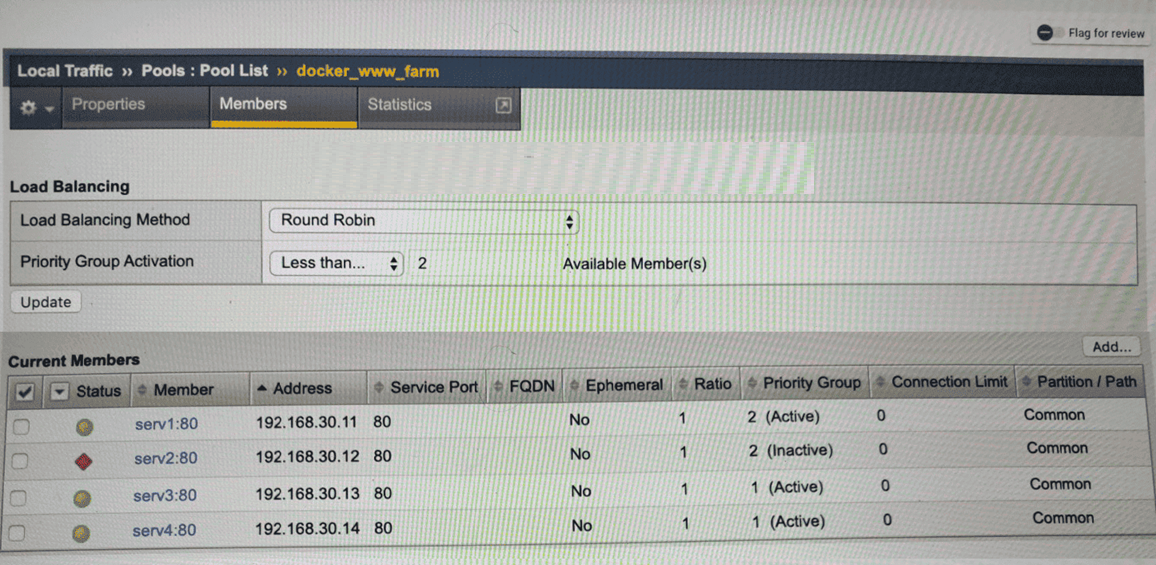
A BIG-IP pool is configured with Priority Group Activation = Less than 2 available members. The pool members have different priority groups and availability states. Which pool members are receiving traffic? (Choose one answer)
This question tests understanding of Priority Group Activation (PGA) and how BIG-IP determines which pool members are eligible to receive traffic.
Key BIG-IP Priority Group Concepts:
Higher priority group numbers = higher priority
BIG-IP will only send traffic to the highest priority group that meets the Priority Group Activation condition
Lower priority groups are activated only when the condition is met
Only available (green) members count toward the activation threshold
Configuration from the Exhibit:
Priority Group Activation: Less than 2 available members
Pool Members and Status:
Pool Member
Priority Group
Status
serv1
2
Active (available)
serv2
2
Inactive (down)
serv3
1
Active (available)
serv4
1
Active (available)
Step-by-Step Traffic Decision:
BIG-IP first evaluates the highest priority group (Priority Group 2)
Priority Group 2 has:
serv1 available
serv2 unavailable
Total available members = 1
Activation rule is Less than 2 available members
Condition is true (1 < 2)
BIG-IP activates the next lower priority group (Priority Group 1)
Traffic is now sent to:
serv1 (Priority Group 2)
serv3 and serv4 (Priority Group 1)
Final Result:
Traffic is distributed to serv1, serv3, and serv4
Why the Other Options Are Incorrect:
A -- Ignores activation of the lower priority group
B -- serv4 is also active and eligible
C -- serv2 is down and cannot receive traffic
Key Data Plane Concept Reinforced:
Priority Group Activation controls when lower-priority pool members are allowed to receive traffic, based strictly on the number of available members in the higher-priority group. In this case, the failure of one high-priority member caused BIG-IP to expand traffic distribution to lower-priority members to maintain availability.
Question 7 Domain 4 Identify the different virtual server types
Which statement is true concerning the default communication between a redundant pair of BIG-IP devices?
Redundant BIG-IP systems (HA pairs) must maintain constant communication to monitor the health of the peer and synchr15onize states.16
Heartbeats: By default, even with a serial cable, th17e BIG-IP systems exchange 'heartbeat' packets over the network to determine if the peer is still alive.
Network Failover: This involves the exchange of UDP packets (typically on port 1026) at regular intervals.
Device Service Clustering (DSC): Modern BIG-IP versions use the Central Management (cm) infrastructure to communicate configuration status and sync status constantly.
Clarification on others: Port lockdown does affect HA communication if misconfigured (A is false). Mirroring uses separate channels (B is false). Mirroring is never sent over the serial cable because it requires high bandwidth (D is false).
What the F5 Networks F5CAB2 Exam Covers
Exam domains verified against the Official F5 Networks F5CAB2 exam guide, last checked November 2026.
Domain 1 Explain the relationship between interfaces, trunks, VLANs, self-IPs, routes and their status/statistics
Understand how trunk configurations enable multiple VLANs to share physical interfaces in BIG-IP deployments. Learn to assign VLANs to interfaces and trunks, identify which VLAN and egress route handles specific traffic patterns, and distinguish between tagged and untagged VLAN handling.
Domain 2 Define ADC application objects
Grasp the core functions of application delivery controllers including intelligent load balancing algorithms and server selection mechanisms. Study the key features and business benefits that ADCs deliver for optimizing application performance and availability.
Domain 3 Determine expected traffic behavior based on configuration
Predict how persistence profiles redirect existing connections and analyze packet processing order with wildcard virtual servers. Evaluate how status changes in virtual servers, pools, and pool members affect traffic flow and identify when connection or rate limits trigger.
Sample question from this domain above Q6
Domain 4 Identify the different virtual server types
Classify virtual servers into Standard, Forwarding IP, Stateless, Reject, Performance Layer 4, and Performance HTTP categories. Understand the distinct packet handling and use case for each type in data plane operations.
Domain 5 Explain high availability (HA) concepts
Learn the mechanisms that ensure HA integrity and maintain synchronized state across redundant systems. Examine the advantages of redundant deployments in preventing single points of failure and meeting service continuity requirements.
F5CAB2 Exam FAQ
Common questions about the exam itself
What background do I need before attempting F5CAB2?
How does F5CAB2 fit into the F5 Certified Administrator, BIG-IP certification path?
What makes virtual server configuration the hardest topic on F5CAB2?
How long should I study to pass F5CAB2?
What happens on exam day for F5CAB2?
What are the retake rules if I fail F5CAB2?
How long is the F5 Certified Administrator, BIG-IP certification valid?
What is the difference between F5CAB2 Data Plane Concepts and F5CAB3 Data Plane Configuration?
Can I reschedule my F5CAB2 exam?
Which job roles does the F5 Certified Administrator, BIG-IP credential target?
Other F5 Networks Exams
Free practice questions for more F5 Networks certification exams