Eccouncil 312-96 Practice Exam Questions & Answers
7 Free Questions
· Last reviewed: October 18, 2026
· Prepared & Reviewed by the ValidExamDumps Editorial Team
Exam Facts
Eccouncil 312-96 Exam Details
Key details for this exam, checked against the published exam outline
47
Practice Questions (Our Bank)
- Exam Code
- 312-96
- Full Name
- Certified Application Security Engineer (CASE) JAVA
- Issuing Body
- EC-Council
- Question Format (Our Bank)
- Multiple Choice
- Delivery
- Online proctored or at a Pearson VUE test centre
- Validity
- 3 years
Practice Questions
Free 312-96 Practice Questions
Each question shows the correct answer and an explanation of why it is right
VA
ValidExamDumps Editorial Team
Every question and its answer is checked by our 312-96 exam
preparation team, who also write the explanation shown with each one.
How we research and review these pages
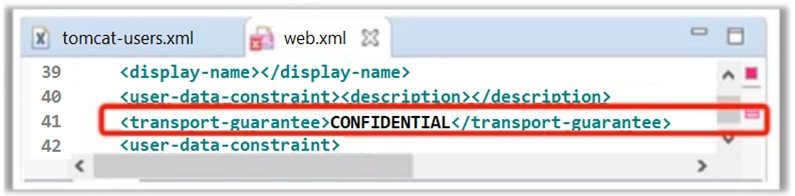
Oliver, a Server Administrator (Tomcat), has set configuration in web.xml file as shown in the following screenshot. What is he trying to achieve?
Correct Answer:
A
Explanation
Oliver is configuring Tomcat to use HTTPS, which transfers data over an encrypted channel. By setting up SSL/TLS in the web.xml file, all communication between client and server becomes encrypted. This protects sensitive data like session cookies and user credentials from being intercepted. Other options might focus on compression or specific protocol versions, but the core goal is encryption.
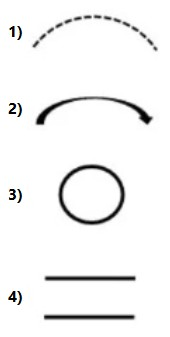
Which of the following DFD component is used to represent the change in privilege levels?
Correct Answer:
D
Explanation
Data Flow Diagrams (DFDs) use specific symbols to represent different elements in system architecture. A trust boundary is the DFD component that shows where privilege levels change or where data moves between different security contexts. This is critical in secure design because it identifies where additional validation and security controls are needed. The other options represent data stores, processes, or data flows, which do not specifically indicate changes in privilege or trust levels.
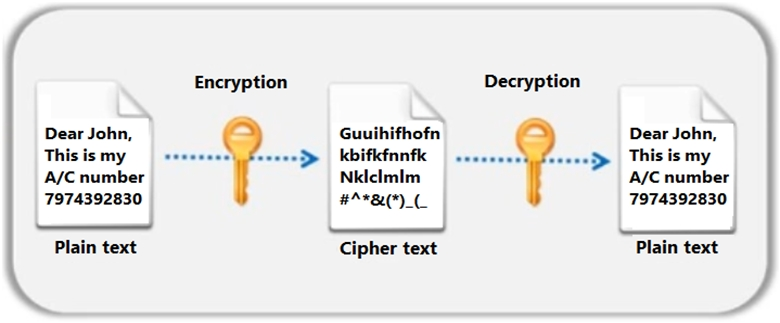
Identify the type of encryption depicted in the following figure.
Correct Answer:
C
Explanation
Symmetric encryption uses the same key for both encrypting and decrypting data. The figure shows this relationship where a single key encrypts plaintext into ciphertext and the same key decrypts it back. Asymmetric encryption would use two different keys, a public key and a private key. Hash functions don't involve keys or decryption at all.
A US-based ecommerce company has developed their website www.ec-sell.com to sell their products online. The website has a feature that allows their customer to search products based on the price. Recently, a bug bounty has discovered a security flaw in the Search page of the website, where he could see all products from the database table when he altered the website URL http://www.ec-sell.com/products.jsp?val=100 to http://www.ec-sell.com/products.jsp?val=200 OR '1'='1 -. The product.jsp page is vulnerable to
Correct Answer:
C
Explanation
The altered URL contains SQL injection syntax. By appending OR '1'='1' to the search parameter, the attacker changes the SQL logic to return all products regardless of the price filter. The single quotes manipulate the query structure and the condition '1'='1' is always true, bypassing the intended search logic. This is a classic example of injection attack where user input is not properly validated or sanitized before being used in a database query.
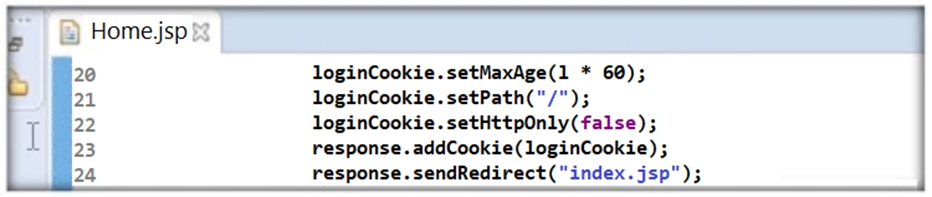
Thomas is not skilled in secure coding. He neither underwent secure coding training nor is aware of the consequences of insecure coding. One day, he wrote code as shown in the following screenshot. He passed 'false' parameter to setHttpOnly() method that may result in the existence of a certain type of vulnerability. Identify the attack that could exploit the vulnerability in the above case.
Correct Answer:
B
Explanation
Setting setHttpOnly() to false allows JavaScript to access the session cookie. This leaves the cookie vulnerable to cross-site scripting attacks where malicious scripts can steal the cookie value. With HttpOnly set to true, browsers block JavaScript access to the cookie, preventing this type of attack. The vulnerability exists at session level, making the application susceptible to client-side script attacks that steal authentication tokens.
Alice, a Server Administrator (Tomcat), wants to ensure that Tomcat can be shut down only by the user who owns the Tomcat process. Select the appropriate setting of the CATALINA_HOME/conf in server.xml that will enable him to do so.
Correct Answer:
B
Explanation
Parameter tampering attacks involve modifying request parameters, such as form fields or URL query strings, to manipulate application behavior. By changing values like prices, user IDs, or permissions, attackers can bypass validation or access unauthorized data. Input validation and proper server-side verification prevent this attack by ensuring submitted parameters match expected values and constraints. This is a core input validation concern for developers.
Ted is an application security engineer who ensures application security activities are being followed during the entire lifecycle of the project. One day, he was analyzing various interactions of users depicted in the use cases of the project under inception. Based on the use case in hand, he started depicting the scenarios where attacker could misuse the application. Can you identify the activity on which Ted is working?
Correct Answer:
A
Explanation
Ted is performing threat modeling by analyzing use cases and identifying how attackers could misuse the application. This activity is called abuse case or misuse case development. During the design phase, security architects document scenarios showing potential attacker actions and malicious interactions. By understanding these scenarios early, developers can design security controls to prevent the attacks. This proactive approach to threat identification is essential for secure application architecture.
Full Access
Get the complete 312-96 question set
- 47 questions covering all exam domains
- Correct answers with explanations, like the free questions above
- PDF and online practice test
- 90 days of free updates
Study Guide
What the Eccouncil 312-96 Exam Covers
9 domains from the Eccouncil 312-96 exam outline, with approximate weightings. Every sample question above is tagged
with the domain it comes from
Domain 1: Understanding Application Security, Threats, and Attacks:
This domain covers core concepts of application security for developers, security experts, and IT managers. It explores prevalent threats and various attack vectors, highlighting the critical nature of secure application development and the potential consequences of security vulnerabilities.
Domain 2: Security Requirements Gathering
Aimed at project managers, business analysts, and security architects, this area concentrates on early identification and documentation of security requirements within the software development lifecycle. It stresses the significance of incorporating security considerations from the outset of application planning.
Sample question from this domain above:
Q7
Domain 3: Secure Application Design and Architecture
Designed for software architects, system designers, and experienced developers, this segment explores principles of secure application design and architecture. It covers threat modeling, secure design patterns, and architectural risk assessment to embed security into the core structure of applications.
Sample question from this domain above:
Q2
Domain 4: Secure Coding Practices for Input Validation
Targeting software developers and quality assurance professionals, this section explores methodologies for validating and sanitizing user inputs. It equips professionals with skills to prevent common security flaws including injection attacks, cross-site scripting, and buffer overflow vulnerabilities.
Sample question from this domain above:
Q4
Domain 5: Secure Coding Practices for Authentication and Authorization
Catering to application developers and identity management specialists, this domain examines implementation of strong authentication mechanisms and appropriate authorization controls. It encompasses secure password management, multi-factor authentication implementation, and various access control frameworks.
Domain 6: Secure Coding Practices for Cryptography
Focused on developers and security engineers, this part covers appropriate implementation of cryptographic functions within applications. It encompasses encryption techniques, hashing methods, effective key management strategies, and generation of secure random numbers.
Sample question from this domain above:
Q3
Domain 7: Secure Coding Practices for Session Management:
Designed for web developers and application security professionals, this section focuses on secure session handling methods to mitigate session-related vulnerabilities. It covers session hijacking, session fixation, and cross-site request forgery attack prevention.
Sample questions from this domain above:
Q1Q5
Domain 8: Static and Dynamic Application Security Testing (SAST & DAST)
Crucial for security analysts, quality assurance professionals, and penetration testers, this segment explores techniques and tools for identifying application security vulnerabilities. It covers both static code analysis and dynamic runtime testing methodologies.
Domain 9: Secure Deployment and Maintenance
Targeted at system administrators, DevOps engineers, and security operations professionals, this section examines best practices for secure application deployment. It covers strategies for managing updates and maintaining security posture throughout the entire application lifecycle.
Sample question from this domain above:
Q6
FAQ
312-96 Exam FAQ
Common questions about the exam itself
What skills do I need before attempting the 312-96 CASE Java exam?
You should have solid background in Java application development and understand foundational security concepts. Prior experience with secure coding practices and basic knowledge of authentication, encryption, and common vulnerabilities like injection attacks and cross-site scripting will help you pass more easily.
How is the 312-96 exam structured and what format are the questions?
The exam consists of multiple-choice questions delivered in formats 1, 2, and 3. You will need to answer questions covering all nine domains of application security from design through deployment.
Which domain in 312-96 do most candidates find most difficult?
Secure Coding Practices for Cryptography and Secure Application Design and Architecture tend to be challenging because they require deep understanding of both theory and practical implementation. Focus on understanding encryption algorithms, key management, threat modeling, and architectural risk assessment during your preparation.
How long does it typically take to prepare for the 312-96 exam?
Most candidates need between 8 to 12 weeks of focused study, depending on their existing development and security background. Those with strong Java experience and some security knowledge may prepare faster, while those new to application security may need longer.
What happens on exam day for 312-96?
You can take the exam online with proctoring or at a Pearson VUE test centre. You will sit at a computer and answer multiple-choice questions covering all nine domains. Make sure you have a stable internet connection if testing online and arrive early to complete the check-in process.
How long is the 312-96 certification valid after I pass?
The Certified Application Security Engineer certification remains valid for 3 years from the date you pass the exam. After that period, you will need to recertify by retaking the exam or completing renewal requirements set by EC-Council.
What job roles does the 312-96 CASE Java certification suit?
The certification is ideal for application developers, security engineers, software architects, and DevSecOps engineers who need to build and maintain secure applications. It also suits security analysts and quality assurance professionals focused on application security testing.
How does 312-96 CASE Java relate to other EC-Council application security certifications?
The 312-96 CASE Java exam is a specialization focused specifically on securing Java applications. The 312-97 DevSecOps Engineer exam builds on application security knowledge by adding deployment, integration, and operations aspects. If you need to understand the full lifecycle of secure applications, you might pursue both certifications.
What if I fail the 312-96 exam? Can I retake it?
Yes, you can retake the exam. EC-Council typically allows you to schedule another attempt, though there may be waiting periods between attempts. Contact EC-Council or your testing provider for their current retake and rescheduling policies.
Why should I choose 312-96 over general application security training without certification?
The 312-96 certification provides formal validation of your application security skills that employers recognize and trust. It covers the complete application lifecycle from design through deployment and maintenance, not just coding practices. The credential demonstrates you can implement security at multiple levels and solve real-world application security problems.

