
CompTIA CS0-003 Practice Exam Questions & Answers
CompTIA CS0-003 Exam Details
Key details for this exam, checked against the published exam outline
- Exam Code
- CS0-003
- Full Name
- CompTIA Cybersecurity Analyst (CySA+) Exam
- Issuing Body
- CompTIA
- Question Format (Our Bank)
- Multiple Choice, Hotspot
- Delivery
- Pearson VUE test centre or online proctored
- Eligibility
- 6-12 months of hands-on cybersecurity experience recommended. no required prior certification
- Validity
- 3 years
- Full Question Set
- 494 questions Get All Questions
Free CS0-003 Practice Questions
Each question shows the correct answer and an explanation of why it is right
Question 1 Domain 3 Vulnerability Management
Which of the following characteristics ensures the security of an automated information system is the most effective and economical?
Comprehensive Detailed The most effective and economical way to ensure the security of an automated information system is to design it with security in mind from the outset. This is often referred to as 'security by design.' Here's a breakdown of each option and why option A is correct:
A . Originally designed to provide necessary security
Systems designed with security from the beginning integrate secure practices and considerations during the development process. This approach mitigates the need for costly and complex retroactive security implementations, which are common in systems where security was an afterthought.
Cost Efficiency: Security implementations at the design stage can be embedded into the system architecture, reducing the costs associated with later modifications.
Effectiveness: Security-by-design approaches often result in robust systems that are more resilient to vulnerabilities because they address security concerns at each development phase.
B . Subjected to intense security testing
While rigorous security testing (such as penetration testing and vulnerability assessments) is essential, it is reactive. Security testing is more effective when applied to systems already designed with foundational security principles, ensuring that tests identify potential flaws in an inherently secure system.
C . Customized to meet specific security threats
Customizing security to meet specific threats addresses unique risks, but such a targeted approach may miss new or emerging threats not initially considered. It also risks neglecting fundamental security practices that apply universally, leading to potential vulnerabilities.
D . Optimized prior to the addition of security
Optimizing a system before adding security features may enhance performance but does not guarantee security. Security cannot be effectively added onto a system as an afterthought without incurring additional costs or creating potential weaknesses.
NIST SP 800-160: Systems Security Engineering, which emphasizes designing systems with security integrated from the beginning.
OWASP Security by Design Principles: Explores how security considerations are most effective when included early in development.
Question 2 Domain 3 Vulnerability Management
Patches for two highly exploited vulnerabilities were released on the same Friday afternoon. Information about the systems and vulnerabilities is shown in the tables below:
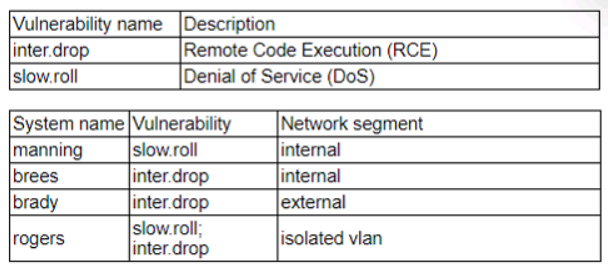
Which of the following should the security analyst prioritize for remediation?
Brady should be prioritized for remediation, as it has the highest risk score and the highest number of affected users. The risk score is calculated by multiplying the CVSS score by the exposure factor, which is the percentage of systems that are vulnerable to the exploit. Brady has a risk score of 9 x 0.8 = 7.2, which is higher than any other system. Brady also has 500 affected users, which is more than any other system. Therefore, patching brady would reduce the most risk and impact for the organization. The other systems have lower risk scores and lower numbers of affected users, so they can be remediated later.
Question 3 Domain 3 Vulnerability Management
Several vulnerability scan reports have indicated runtime errors as the code is executing. The dashboard that lists the errors has a command-line interface for developers to check for vulnerabilities. Which of the following will enable a developer to correct this issue? (Select two).
Reviewing the code and debugging the code are two methods that can help a developer identify and fix runtime errors in the code. Reviewing the code involves checking the syntax, logic, and structure of the code for any errors or inconsistencies. Debugging the code involves running the code in a controlled environment and using tools such as breakpoints, watches, and logs to monitor the execution and find the source of errors. Both methods can help improve the quality and security of the code.
Get the complete CS0-003 question set
$20$40
Question 4 Domain 2 Incident Response Management
A network analyst notices a long spike in traffic on port 1433 between two IP addresses on opposite sides of a WAN connection. Which of the following is the most likely cause?
Port 1433 is commonly used by Microsoft SQL Server, which is a database management system. A spike in traffic on this port between two IP addresses on opposite sides of a WAN connection could indicate a database replication process, which is a way of copying and distributing data from one database server to another. This could be a legitimate activity performed by an administrator, but it should be communicated to the security operations center (SOC) to avoid confusion and false alarms.
Question 5 Domain 3 Vulnerability Management
Which of the following describes a contract that is used to define the various levels of maintenance to be provided by an external business vendor in a secure environment?
SLA stands for Service Level Agreement, which is a contract that defines the various levels of maintenance to be provided by an external business vendor in a secure environment. An SLA specifies the expectations, responsibilities, and obligations of both parties, such as the scope, quality, availability, and performance of the service, as well as the metrics and methods for measuring and reporting the service level. An SLA also outlines the penalties or remedies for any breach or failure of the service level. An SLA can help ensure that the external business vendor delivers the service in a timely, consistent, and secure manner, and that the customer receives the service that meets their needs and requirements. Official Reference:
https://partners.comptia.org/docs/default-source/resources/comptia-cysa-cs0-002-exam-objectives
https://www.comptia.org/certifications/cybersecurity-analyst
https://www.comptia.org/blog/the-new-comptia-cybersecurity-analyst-your-questions-answered
Question 6 Domain 2 Incident Response Management
An employee is no longer able to log in to an account after updating a browser. The employee usually has several tabs open in the browser. Which of
the following attacks was most likely performed?
The most likely attack that was performed is CSRF (Cross-Site Request Forgery). This is an attack that forces a user to execute unwanted actions on a web application in which they are currently authenticated1. If the user has several tabs open in the browser, one of them might contain a malicious link or form that sends a request to the web application to change the user's password, email address, or other account settings. The web application will not be able to distinguish between the legitimate requests made by the user and the forged requests made by the attacker. As a result, the user will lose access to their account.
To prevent CSRF attacks, web applications should implement some form of anti-CSRF tokens or other mechanisms that validate the origin and integrity of the requests2. These tokens are unique and unpredictable values that are generated by the server and embedded in the forms or URLs that perform state-changing actions. The server will then verify that the token received from the client matches the token stored on the server before processing the request. This way, an attacker cannot forge a valid request without knowing the token value.
Some other possible attacks that are not relevant to this scenario are:
RFI (Remote File Inclusion) is an attack that allows an attacker to execute malicious code on a web server by including a remote file in a script. This attack does not affect the user's browser or account settings.
LFI (Local File Inclusion) is an attack that allows an attacker to read or execute local files on a web server by manipulating the input parameters of a script. This attack does not affect the user's browser or account settings.
XSS (Cross-Site Scripting) is an attack that injects malicious code into a web page that is then executed by the user's browser. This attack can affect the user's browser or account settings, but it requires the user to visit a compromised web page or click on a malicious link. It does not depend on having several tabs open in the browser.
Question 7 Domain 4 Security Operations
Security analysts review logs on multiple servers on a daily basis. Which of the following implementations will give the best central visibility into the events occurring throughout the corporate environment without logging in to the servers individually?
The best implementation to give the best central visibility into the events occurring throughout the corporate environment without logging in to the servers individually is B. Configure the servers to forward logs to a SIEM.
A SIEM (Security Information and Event Management) is a security solution that helps organizations detect, analyze, and respond to security threats before they disrupt business1. SIEM tools collect, aggregate, and correlate log data from various sources across an organization's network, such as applications, devices, servers, and users.SIEM tools also provide real-time alerts, dashboards, reports, and incident response capabilities to help security teams identify and mitigate cyberattacks2345.
By configuring the servers to forward logs to a SIEM, the security analysts can have a central view of potential threats and monitor security incidents across the corporate environment without logging in to the servers individually.This can save time, improve efficiency, and enhance security posture2345.
Deploying a database to aggregate the logging (A) may not provide the same level of analysis, correlation, and alerting as a SIEM tool. Sharing the log directory on each server to allow local access may not be scalable or secure for a large number of servers. Automating the emailing of logs to the analysts (D) may not be timely or effective for real-time threat detection and response. Therefore, B is the best option among the choices given.
What the CompTIA CS0-003 Exam Covers
Exam domains verified against the Official CompTIA CS0-003 exam guide, last checked November 2026.
Domain 1 Reporting and Communication
17%Report findings from vulnerability assessments and incident investigations to stakeholders in actionable terms. Communicate security risks and remediation status in ways that inform business decisions.
Domain 2 Incident Response Management
20%Perform tactical incident response activities and follow the incident management lifecycle from preparation through post-incident review. Apply frameworks like MITRE ATT&CK to understand attack methodology.
Domain 3 Vulnerability Management
30%Execute vulnerability scanning and assessment to discover weaknesses in systems and applications. Prioritize vulnerabilities based on risk and recommend specific technical controls to remediate them.
Domain 4 Security Operations
33%Analyze network and system architecture as it applies to threat detection and response. Use tools and techniques to identify malicious activity and distinguish between genuine attacks and false positives in security operations.
Sample question from this domain above Q7
CS0-003 Exam FAQ
Common questions about the exam itself
What experience do I need before taking CS0-003?
How hard is the CySA+ exam compared to Security+?
Which domain is the hardest to study for on CS0-003?
How long should I study for the CySA+ exam?
What happens on exam day for CS0-003?
Can I retake the CySA+ exam if I fail?
How long does the CySA+ certification stay valid?
What job role does CySA+ prepare me for?
How does CS0-003 fit into the CompTIA security track?
What is the passing score for CS0-003?
Other CompTIA Exams
Free practice questions for more CompTIA certification exams