
CompTIA CS0-003 Practice Exam Questions & Answers
CompTIA CS0-003 Exam Details
Key details for this exam, checked against the published exam outline
- Exam Code
- CS0-003
- Full Name
- CompTIA Cybersecurity Analyst (CySA+) Exam
- Issuing Body
- CompTIA
- Question Format (Our Bank)
- Multiple Choice, Hotspot
- Delivery
- Pearson VUE test centre or online proctored
- Eligibility
- 6-12 months of hands-on cybersecurity experience recommended. no required prior certification
- Validity
- 3 years
- Full Question Set
- 494 questions Get All Questions
Free CS0-003 Practice Questions
Each question shows the correct answer and an explanation of why it is right
Question 1 Domain 3 Vulnerability Management
A security analyst is trying to validate the results of a web application scan with Burp Suite. The security analyst performs the following:
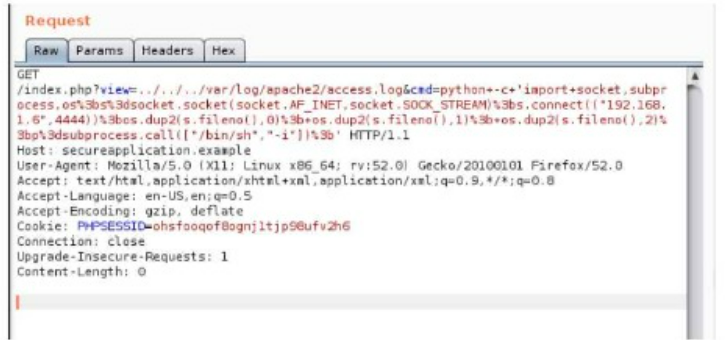
Which of the following vulnerabilitles Is the securlty analyst trylng to valldate?
The security analyst is validating a Local File Inclusion (LFI) vulnerability, as indicated by the ''/.../.../.../'' in the GET request which is a common indicator of directory traversal attempts associated with LFI. The other options are not relevant for this purpose: SQL injection involves injecting malicious SQL statements into a database query; XSS involves injecting malicious scripts into a web page; CSRF involves tricking a user into performing an unwanted action on a web application.
Question 2 Domain 3 Vulnerability Management
A cybersecurity team has witnessed numerous vulnerability events recently that have affected operating systems. The team decides to implement host-based IPS, firewalls, and two-factor authentication. Which of the following
does this most likely describe?
The correct answer is A. System hardening.
System hardening is the process of securing a system by reducing its attack surface, applying patches and updates, configuring security settings, and implementing security controls. System hardening can help prevent or mitigate vulnerability events that may affect operating systems. Host-based IPS, firewalls, and two-factor authentication are examples of security controls that can be applied to harden a system1.
The other options are not the best descriptions of the scenario. A hybrid network architecture (B) is a network design that combines on-premises and cloud-based resources, which may or may not involve system hardening. Continuous authorization is a security approach that monitors and validates the security posture of a system on an ongoing basis, which is different from system hardening. Secure access service edge (D) is a network architecture that delivers cloud-based security services to remote users and devices, which is also different from system hardening.
Question 3 Domain 3 Vulnerability Management
An analyst reviews the following web server log entries:
%2E%2E/%2E%2E/%2ES2E/%2E%2E/%2E%2E/%2E%2E/etc/passwd
No attacks or malicious attempts have been discovered. Which of the following most likely describes what took place?
Comprehensive and Detailed Step-by-Step Directory traversal, also known as path traversal, is an attack that allows attackers to access restricted directories and execute commands outside the web server's root directory. The %2E encoding corresponds to a dot (.) in ASCII, and %2E%2E resolves to ../. The log entries indicate attempts to navigate directories upward to access sensitive files like /etc/passwd. Since no malicious activity was flagged, it is inferred this was either an unsuccessful or reconnaissance attempt.
CompTIA CySA+ Study Guide (Chapter 3: Malicious Activity, Page 79)
CompTIA CySA+ Objectives (Domain 1.2 - Indicators of Potentially Malicious Activity)
Get the complete CS0-003 question set
$20$40
Question 4 Domain 2 Incident Response Management
The SOC receives a number of complaints regarding a recent uptick in desktop error messages that are associated with workstation access to an internal web application. An analyst, identifying a recently modified XML file on the web server, retrieves a copy of this file for review, which contains the following code:
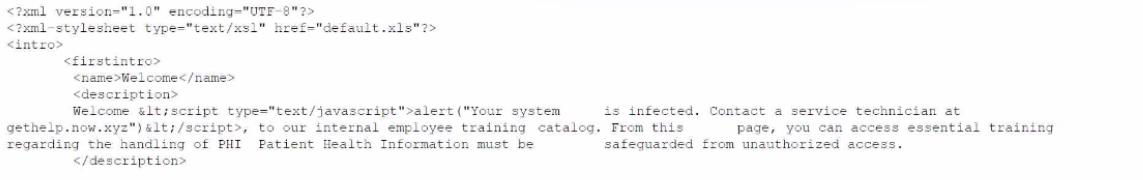
Which of The following XML schema constraints would stop these desktop error messages from appearing?
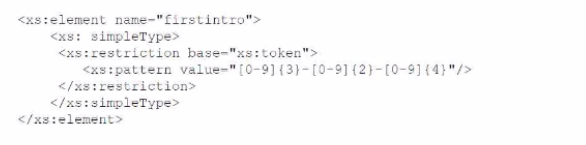
A.
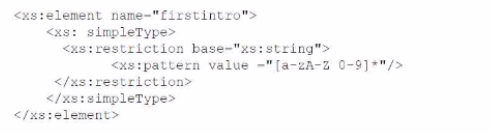
B.
C.
D.
The XML file contains JavaScript embedded within a <description> tag that executes an alert message, which is a common Cross-Site Scripting (XSS) attack vector. The issue occurs because the XML schema does not restrict the input to safe characters, allowing arbitrary script execution when the XML file is processed by a vulnerable application.
Solution: Implement Input Validation Using an XML Schema Constraint
Option B enforces a whitelist approach by allowing only alphanumeric characters and spaces ([a-zA-Z 0-9]*).
This prevents the inclusion of malicious JavaScript or special characters such as <, >, or &, which are required for XSS injection.
Why are the other options incorrect?
Option A: Restricts input to a Social Security Number (SSN) format ([0-9]{3}-[0-9]{2}-[0-9]{4}). While it prevents JavaScript injection, it is too restrictive and would break legitimate text-based content in the XML.
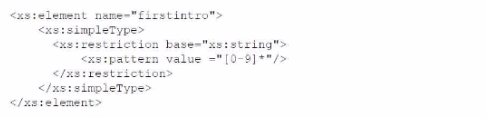
Option C: Restricts input to only numeric values ([0-9]*), preventing JavaScript injection but also breaking legitimate non-numeric content in the <description> field.
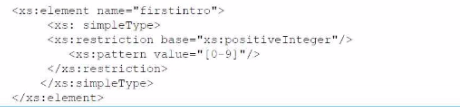
Option D: Restricts input to a single positive integer, which does not align with the expected text-based content.
Thus, Option B is the correct answer, as it enforces proper input validation while still allowing expected text input.
Question 5 Domain 3 Vulnerability Management
Given the following CVSS string-
CVSS:3.0/AV:N/AC:L/PR:N/UI:N/3:U/C:K/I:K/A:H
Which of the following attributes correctly describes this vulnerability?
The vulnerability is network based is the correct attribute that describes this vulnerability, as it can be inferred from the CVSS string. CVSS stands for Common Vulnerability Scoring System, which is a framework that assigns numerical scores and ratings to vulnerabilities based on their characteristics and severity. The CVSS string consists of several metrics that define different aspects of the vulnerability, such as the attack vector, the attack complexity, the privileges required, the user interaction, the scope, and the impact on confidentiality, integrity and availability. The first metric in the CVSS string is the attack vector (AV), which indicates how the vulnerability can be exploited. The value of AV in this case is N, which stands for network. This means that the vulnerability can be exploited remotely over a network connection, without physical or logical access to the target system. Therefore, the vulnerability is network based. Official Reference:
https://partners.comptia.org/docs/default-source/resources/comptia-cysa-cs0-002-exam-objectives
https://www.comptia.org/certifications/cybersecurity-analyst
https://packitforwarding.com/index.php/2019/01/10/comptia-cysa-common-vulnerability-scoring-system-cvss/
Question 6 Domain 2 Incident Response Management
Which of the following techniques can help a SOC team to reduce the number of alerts related to the internal security activities that the analysts have to triage?
To reduce alerts from internal security activities, a SOC team should implement techniques that filter out known-benign activities:
- Whitelisting: Create approved lists of known-good internal security tools, scans, and activities (vulnerability assessments, penetration tests, security audits) so their traffic isn't flagged
- Alert tuning/rule optimization: Modify SIEM rules and detection logic to exclude known internal activities with documented business purposes
- Baseline exclusions: Establish baselines for legitimate security operations and exclude them from triggering alerts
- Why this reduces alert fatigue:
- SOC analysts spend less time triaging false positives from authorized internal activities
- Frees analyst time for genuine security events
- Improves detection effectiveness by reducing noise
- Key consideration: Must maintain audit trails and documentation of excluded activities to ensure they remain legitimate and authorized
Question 7 Domain 4 Security Operations
Which of the following is a benefit of the Diamond Model of Intrusion Analysis?
The Diamond Model of Intrusion Analysis is a framework that helps analysts to understand the relationships between the adversary, the victim, the infrastructure, and the capability involved in an attack. It also enables analytical pivoting, which is the process of moving from one piece of information to another related one, and identifies knowledge gaps that need further investigation.
What the CompTIA CS0-003 Exam Covers
Exam domains verified against the Official CompTIA CS0-003 exam guide, last checked November 2026.
Domain 1 Reporting and Communication
17%Report findings from vulnerability assessments and incident investigations to stakeholders in actionable terms. Communicate security risks and remediation status in ways that inform business decisions.
Domain 2 Incident Response Management
20%Perform tactical incident response activities and follow the incident management lifecycle from preparation through post-incident review. Apply frameworks like MITRE ATT&CK to understand attack methodology.
Domain 3 Vulnerability Management
30%Execute vulnerability scanning and assessment to discover weaknesses in systems and applications. Prioritize vulnerabilities based on risk and recommend specific technical controls to remediate them.
Domain 4 Security Operations
33%Analyze network and system architecture as it applies to threat detection and response. Use tools and techniques to identify malicious activity and distinguish between genuine attacks and false positives in security operations.
Sample question from this domain above Q7
CS0-003 Exam FAQ
Common questions about the exam itself
What experience do I need before taking CS0-003?
How hard is the CySA+ exam compared to Security+?
Which domain is the hardest to study for on CS0-003?
How long should I study for the CySA+ exam?
What happens on exam day for CS0-003?
Can I retake the CySA+ exam if I fail?
How long does the CySA+ certification stay valid?
What job role does CySA+ prepare me for?
How does CS0-003 fit into the CompTIA security track?
What is the passing score for CS0-003?
Other CompTIA Exams
Free practice questions for more CompTIA certification exams