Key details for this exam, checked against the published exam outline
Each question shows the correct answer and an explanation of why it is right
A healthcare system recently suffered from a ransomware incident. As a result, the board of directors decided to hire a security consultant to improve existing network security. The security consultant found that the healthcare network was completely flat, had no privileged access limits, and had open RDP access to servers with personal health information. As the consultant builds the remediation plan, which of the following solutions would best solve these challenges? (Select three).
Privileged Access Management (PAM)restricts elevated permissions, reducing the risk of widespread ransomware attacks.Multi-Factor Authentication (MFA)protects against credential theft and ensures that even if passwords are compromised, accounts are not easily accessible.Network segmentationbreaks the flat network into secure zones, limiting lateral movement by attackers. SD-WAN and BGP relate to network routing and efficiency, not security architecture specifically. Remote access VPN secures external access but does not solve internal flat network issues. Network Access Control (NAC) is helpful but secondary compared to PAM, MFA, and segmentation in this context.
A developer needs toimprove the cryptographic strength of a password-storage component in a web application without completely replacing the crypto-module. Which of the following is the most appropriate technique?
The most appropriate technique to improve the cryptographic strength of a password-storage component in a web application without completely replacing the crypto-module is key stretching. Here's why:
Enhanced Security: Key stretching algorithms, such as PBKDF2, bcrypt, and scrypt, increase the computational effort required to derive the encryption key from the password, making brute-force attacks more difficult and time-consuming.
Compatibility: Key stretching can be implemented alongside existing cryptographic modules, enhancing their security without the need for a complete overhaul.
Industry Best Practices: Key stretching is a widely recommended practice for securely storing passwords, as it significantly improves resistance to password-cracking attacks.
CompTIA Security+ SY0-601 Study Guide by Mike Chapple and David Seidl
NIST Special Publication 800-63B: Digital Identity Guidelines - Authentication and Lifecycle Management
OWASP Password Storage Cheat Sheet
SIMULATION
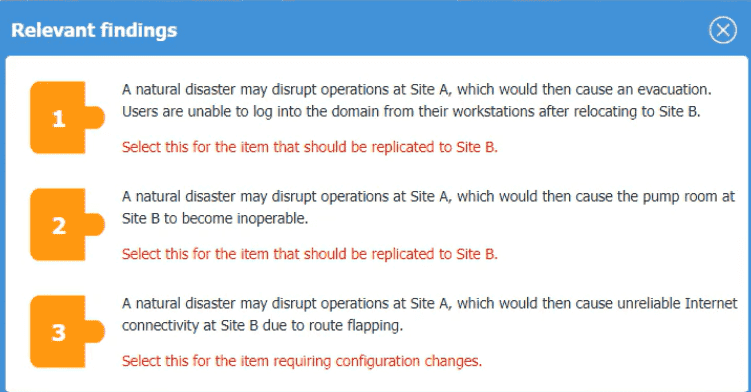
An organization is planning for disaster recovery and continuity ofoperations, and has noted the following relevant findings:
1. A natural disaster may disrupt operations at Site A, which would then cause an evacuation. Users are
unable to log into the domain from-their workstations after relocating to Site B.
2. A natural disaster may disrupt operations at Site A, which would then cause the pump room at Site B
to become inoperable.
3. A natural disaster may disrupt operations at Site A, which would then cause unreliable internet
connectivity at Site B due to route flapping.
INSTRUCTIONS
Match each relevant finding to the affected host by clicking on the host name and selecting the appropriate number.
For findings 1 and 2, select the items that should be replicated to Site B. For finding 3, select the item requiring configuration changes, then select the appropriate corrective action from the drop-down menu.
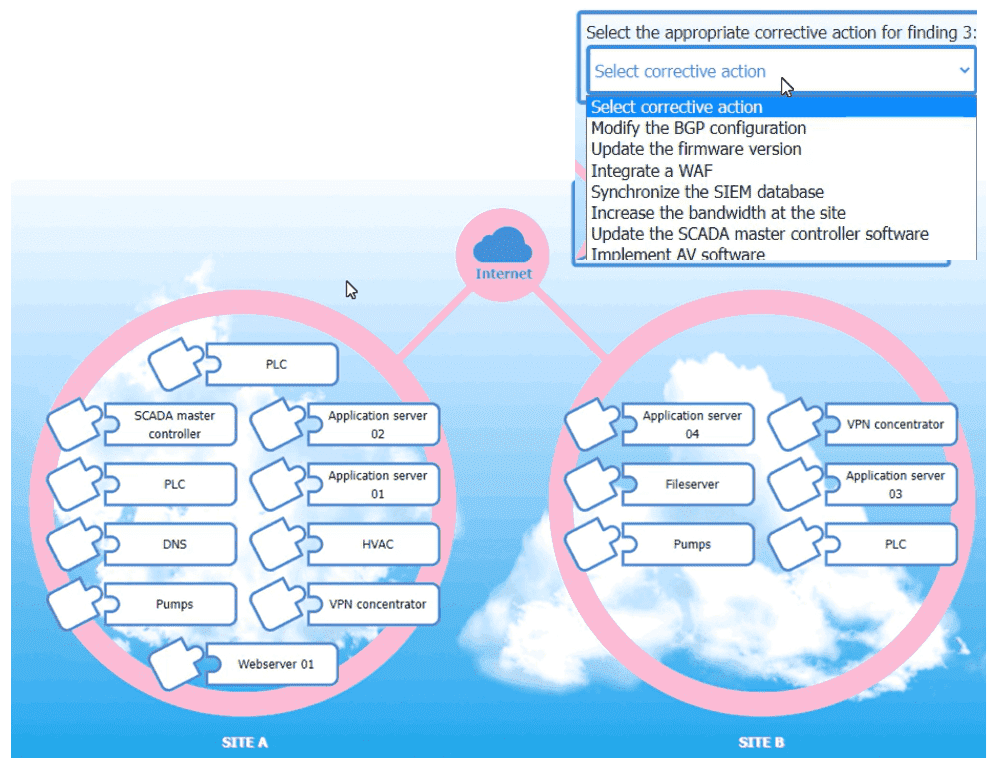
Matching Relevant Findings to the Affected Hosts:
Finding 1:
Affected Host: DNS
Reason: Users are unable to log into the domain from their workstations after relocating to Site B, which implies a failure in domain name services that are critical for user authentication and domain login.
Finding 2:
Affected Host: Pumps
Reason: Thepump room at Site B becoming inoperable directly points to the critical infrastructure components associated with pumping operations.
Finding 3:
Affected Host: VPN Concentrator
Reason: Unreliable internet connectivity at Site B due to route flapping indicates issues with network routing, which is often managed by VPN concentrators that handle site-to-site connectivity.
Corrective Actions for Finding 3:
Finding 3 Corrective Action:
Action: Modify the BGP configuration
Reason: Route flapping is often related to issues with Border Gateway Protocol (BGP) configurations. Adjusting BGP settings can stabilize routes and improve internet connectivity reliability.
Replication to Site B for Finding 1:
Affected Host: DNS
Domain Name System (DNS) services are essential for translating domain names into IP addresses, allowing users to log into the network. Replicating DNS services ensures that even if Site A is disrupted, users at Site B can still authenticate and access necessary resources.
Replication to Site B for Finding 2:
Affected Host: Pumps
The operation of the pump room is crucial for maintaining various functions within the infrastructure. Replicating the control systems and configurations for the pumps at Site B ensures that operations can continue smoothly even if Site A is affected.
Configuration Changes for Finding 3:
Affected Host: VPN Concentrator
Route flapping is a situation where routes become unstable, causing frequent changes in the best path for data to travel. This instability can be mitigated by modifying BGP configurations to ensure more stable routing. VPN concentrators, which manage connections between sites, are typically configured with BGP for optimal routing.
CompTIA Security+ Study Guide: This guide provides detailed information on disaster recovery and continuity of operations, emphasizing the importance of replicating critical services and making necessary configuration changes to ensure seamless operation during disruptions.
CompTIA Security+ Exam Objectives: These objectives highlight key areas in disaster recovery planning, including the replication of critical services and network configuration adjustments.
Disaster Recovery and Business Continuity Planning (DRBCP): This resource outlines best practices for ensuring that operations can continue at an alternate site during a disaster, including the replication of essential services and network stability measures.
By ensuring that critical services like DNS and control systems for pumps are replicated at the alternate site, and by addressing network routing issues through proper BGP configuration, the organization can maintain operational continuity and minimize the impact of natural disasters on their operations.
A cybersecurity architect seeks to improve vulnerability management and orchestrate a large number of vulnerability checks. Key constraints include:
. There are 512 containerized microservices.
. Vulnerability data is sourced from multiple scanners.
. CIS baselines must be enforced.
. Scan activity must be scheduled.
Which of the following automation workflows best meets this objective?
A security operations analyst is reviewing network traffic baselines for nightly database backups. Given the following information:
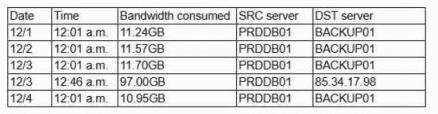
Which of the following should the security analyst do next?
An organization is implementing Zero Trust architecture A systems administrator must increase the effectiveness of the organization's context-aware access system. Which of the following is the best way to improve the effectiveness of the system?
Microsegmentation is a critical strategy within Zero Trust architecture that enhances context-aware access systems by dividing the network into smaller, isolated segments. This reduces the attack surface and limits lateral movement of attackers within the network. It ensures that even if one segment is compromised, the attacker cannot easily access other segments. This granular approach to network security is essential for enforcing strict access controls and monitoring within Zero Trust environments.
Emails that the marketing department is sending to customers are going to the customers' spam folders. The security team is investigating the issue and discovers that the certificates used by the email server were reissued, but DNS records had not been updated. Which of the following should the security team update in order to fix this issue? (Select three).
Exam domains verified against: Official CompTIA CAS-005 exam guide, last checked October 2026.
Implement governance components that align with organizational security requirements and compliance frameworks. Focus on phishing and social engineering threats, security communication protocols, and risk assessment methods like COBIT framework implementation.
Analyze security requirements to design resilient systems with proper component placement and configuration. Design secure network architectures, including firewalls and intrusion prevention systems, for complex enterprise environments supporting zero-trust and hybrid cloud scenarios.
Troubleshoot common issues with identity and access management components in enterprise environments. Apply cryptographic solutions, design secure integrations, and solve real-world authentication and authorization challenges across diverse platforms.
Sample question from this domain above: Q2
Analyze security data to enable monitoring and response across complex environments. Implement threat detection, incident response procedures, and digital forensics capabilities to identify and mitigate security events in real time.
Sample question from this domain above: Q5
Common questions about the exam itself

