
CompTIA CAS-005 Practice Exam Questions & Answers
CompTIA CAS-005 Exam Details
Key details for this exam, checked against the published exam outline
- Exam Code
- CAS-005
- Full Name
- CompTIA SecurityX Certification Exam
- Issuing Body
- CompTIA
- Question Format (Our Bank)
- Multiple Choice, Drag & Drop
- Delivery
- Online proctored (OnVUE) or at Pearson VUE test centre
- Eligibility
- No formal prerequisites. Recommended: minimum 10 years general hands-on IT experience including at least 5 years hands-on IT security experience
- Validity
- 3 years. renewable with 75 continuing education units (CEUs)
- Full Question Set
- 345 questions Get All Questions
Free CAS-005 Practice Questions
Each question shows the correct answer and an explanation of why it is right
Question 1 Domain 2 Security Architecture
A cloud engineer needs to identify appropriate solutions to:
* Provide secure access to internal and external cloud resources.
* Eliminate split-tunnel traffic flows.
*Enable identity and access management capabilities.
Which of the following solutions arc the most appropriate? (Select two).
To provide secure access tointernal and external cloud resources, eliminate split-tunnel traffic flows, and enable identity and access management capabilities, the most appropriate solutions are CASB (Cloud Access Security Broker) and SASE (Secure Access Service Edge).
Why CASB and SASE?
CASB (Cloud Access Security Broker):
Secure Access: CASB solutions provide secure access to cloud resources by enforcing security policies and monitoring user activities.
Identity and Access Management: CASBs integrate with identity and access management (IAM) systems to ensure that only authorized users can access cloud resources.
Visibility and Control: They offer visibility into cloud application usage and control over data sharing and access.
SASE (Secure Access Service Edge):
Eliminate Split-Tunnel Traffic: SASE integrates network security functions with WAN capabilities to ensure secure access without the need for split-tunnel configurations.
Comprehensive Security: SASE provides a holistic security approach, including secure web gateways, firewalls, and zero trust network access (ZTNA).
Identity-Based Access: SASE leverages IAM to enforce access controls based on user identity and context.
Other options, while useful, do not comprehensively address all the requirements:
A . Federation: Useful for identity management but does not eliminate split-tunnel traffic or provide comprehensive security.
B . Microsegmentation: Enhances security within the network but does not directly address secure access to cloud resources or split-tunnel traffic.
D . PAM (Privileged Access Management): Focuses on managing privileged accounts and does not provide comprehensive access control for internal and external resources.
E . SD-WAN: Enhances WAN performance but does not inherently provide the identity and access management capabilities or eliminate split-tunnel traffic.
CompTIA SecurityX Study Guide
'CASB: Cloud Access Security Broker,' Gartner Research
Question 2 Domain 3 Security Engineering
SIMULATION
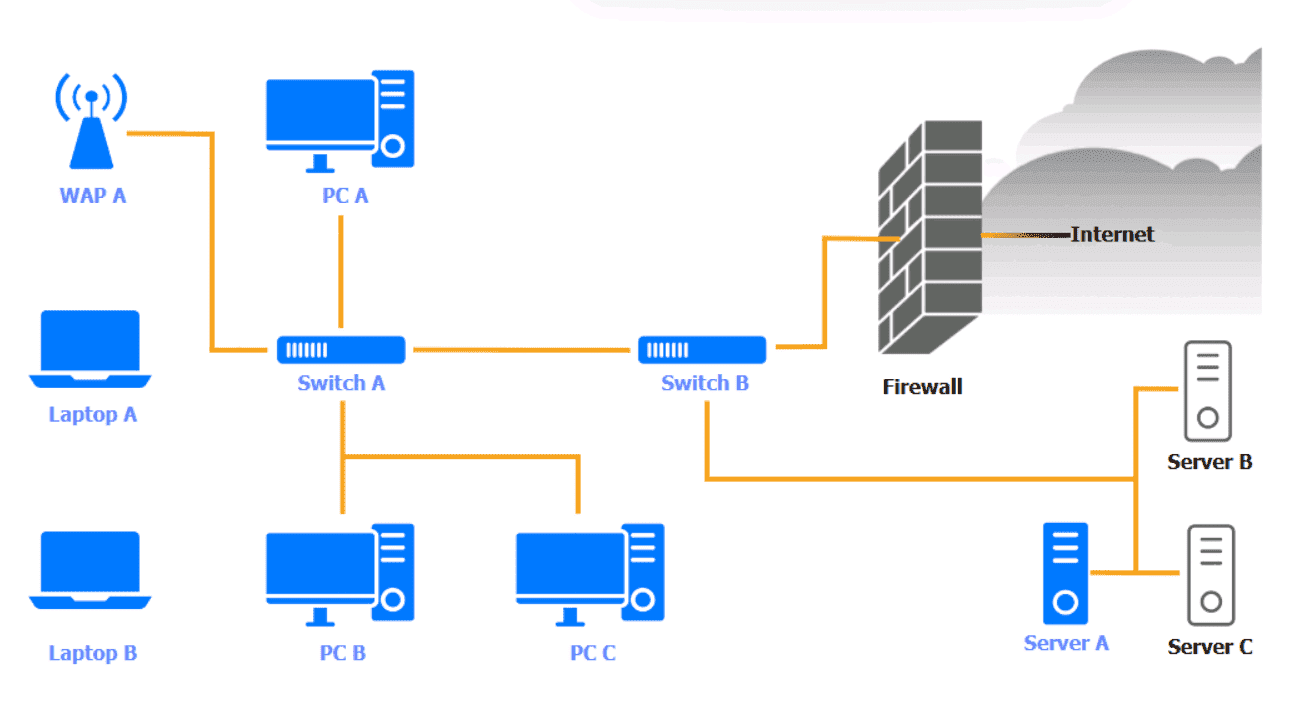
A security engineer needs to review the configurations of several devices on the network to meet the following requirements:
* The PostgreSQL server must only allow connectivity in the 10.1.2.0/24
subnet.
* The SSH daemon on the database server must be configured to listen
to port 4022.
* The SSH daemon must only accept connections from a Single
workstation.
* All host-based firewalls must be disabled on all workstations.
* All devices must have the latest updates from within the past eight
days.
*All HDDs must be configured to secure data at rest.
* Cleartext services are not allowed.
* All devices must be hardened when possible.
Instructions:
Click on the various workstations and network devices to review the posture assessment results. Remediate any possible issues or indicate that no issue is found.
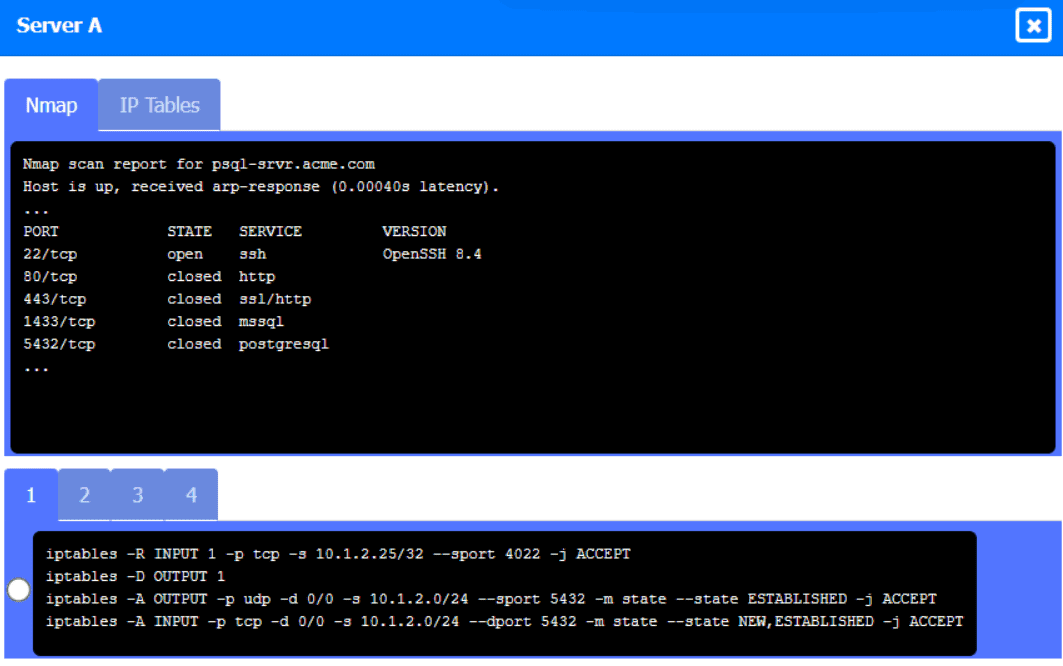
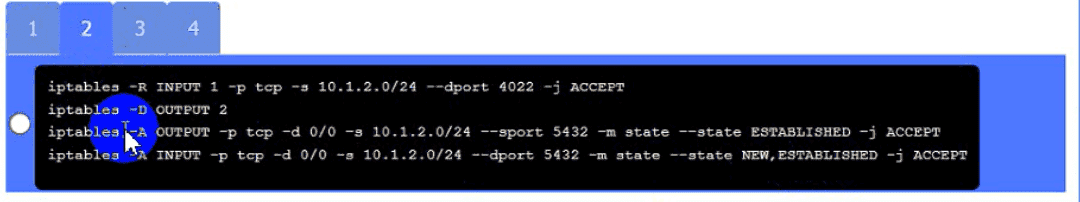
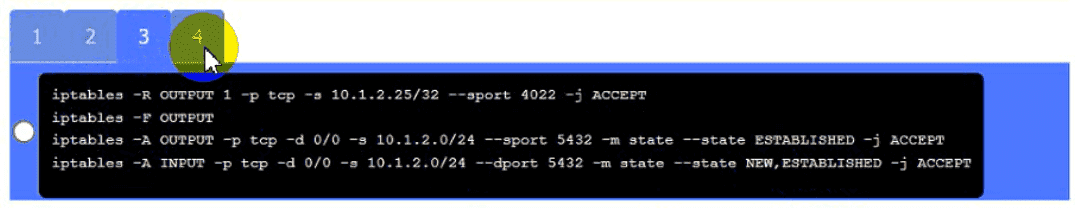
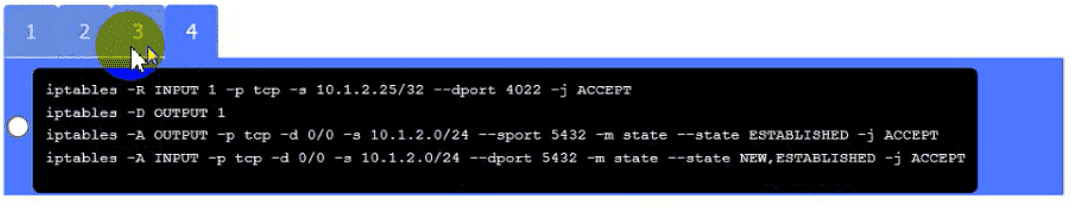
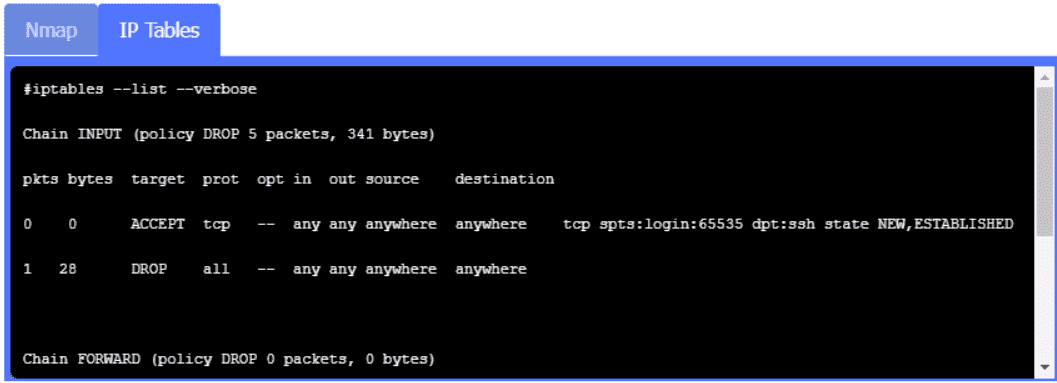
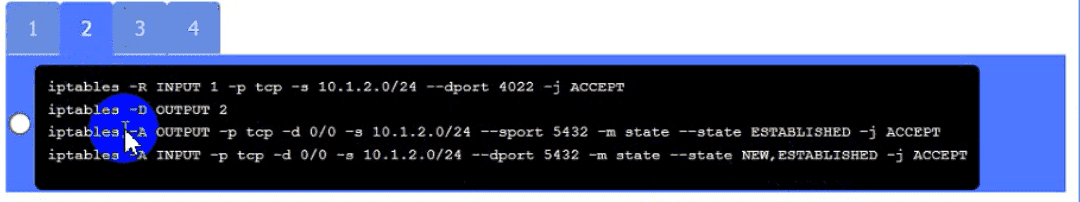
Click on Server A to review output data. Select commands in the appropriate tab to remediate connectivity problems to the pOSTGREsql DATABASE VIA ssh
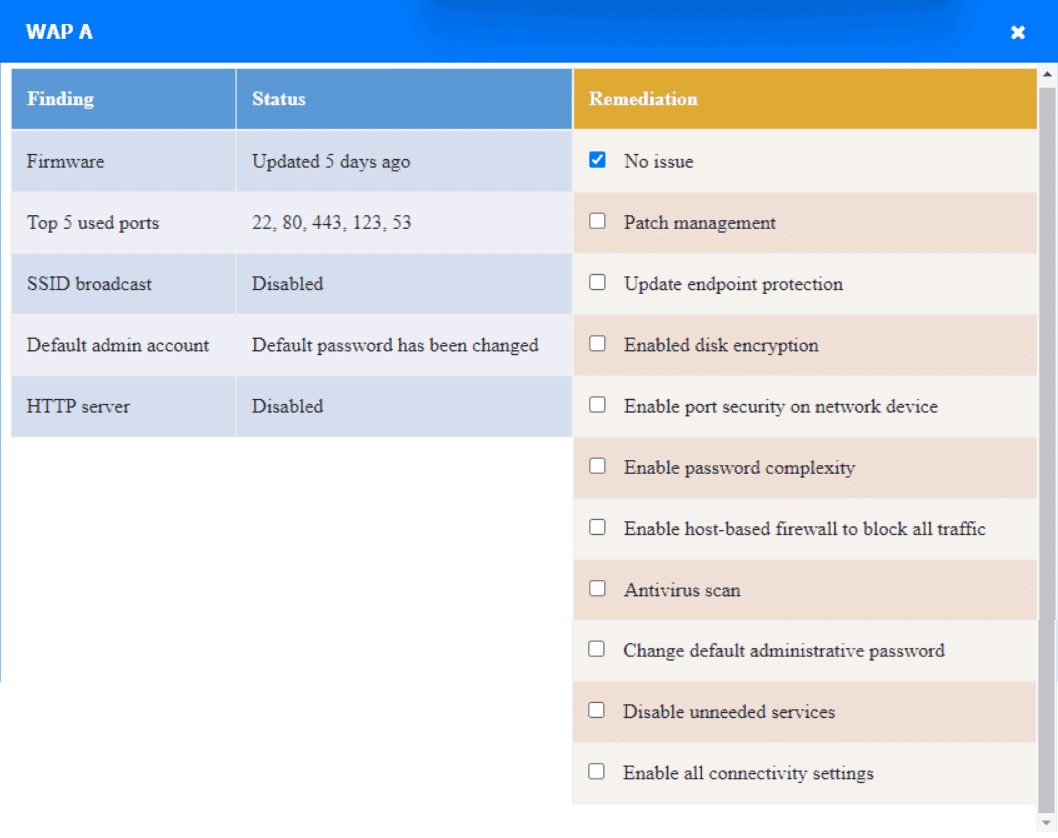
WAP A
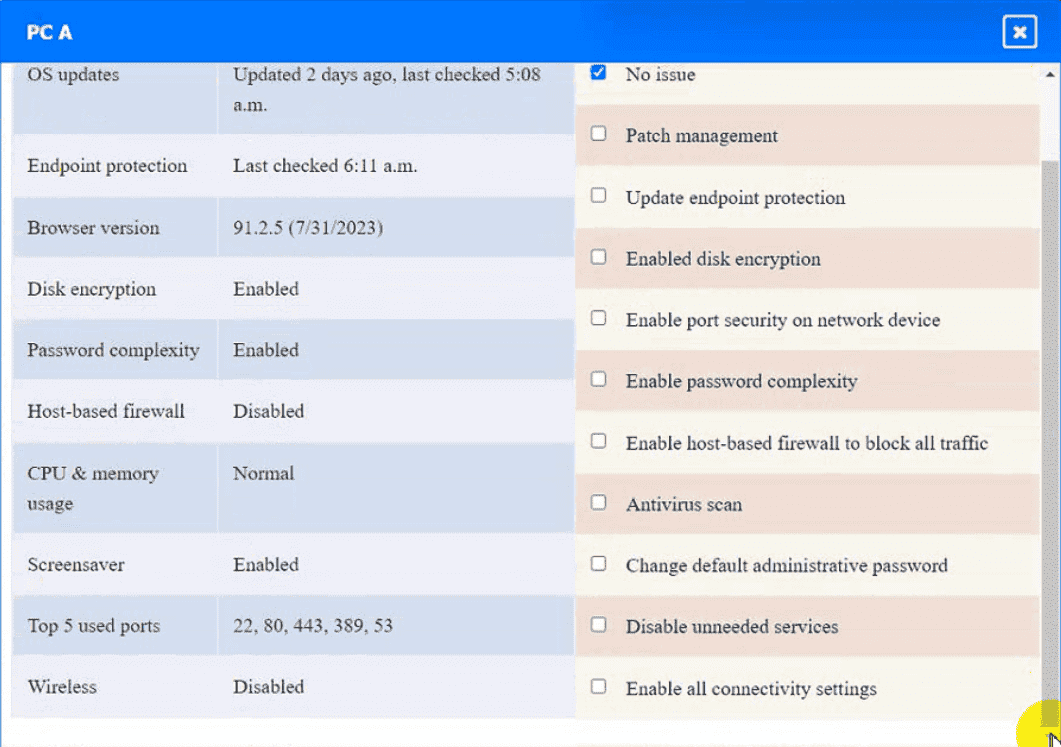
PC A
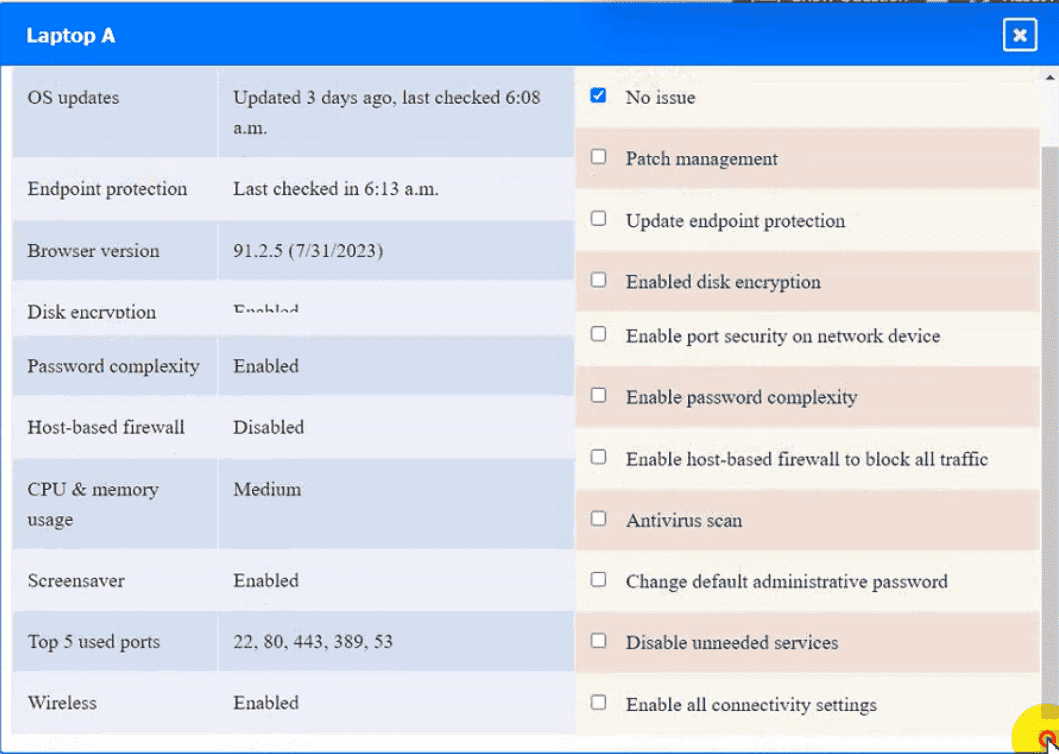
Laptop A
Switch A
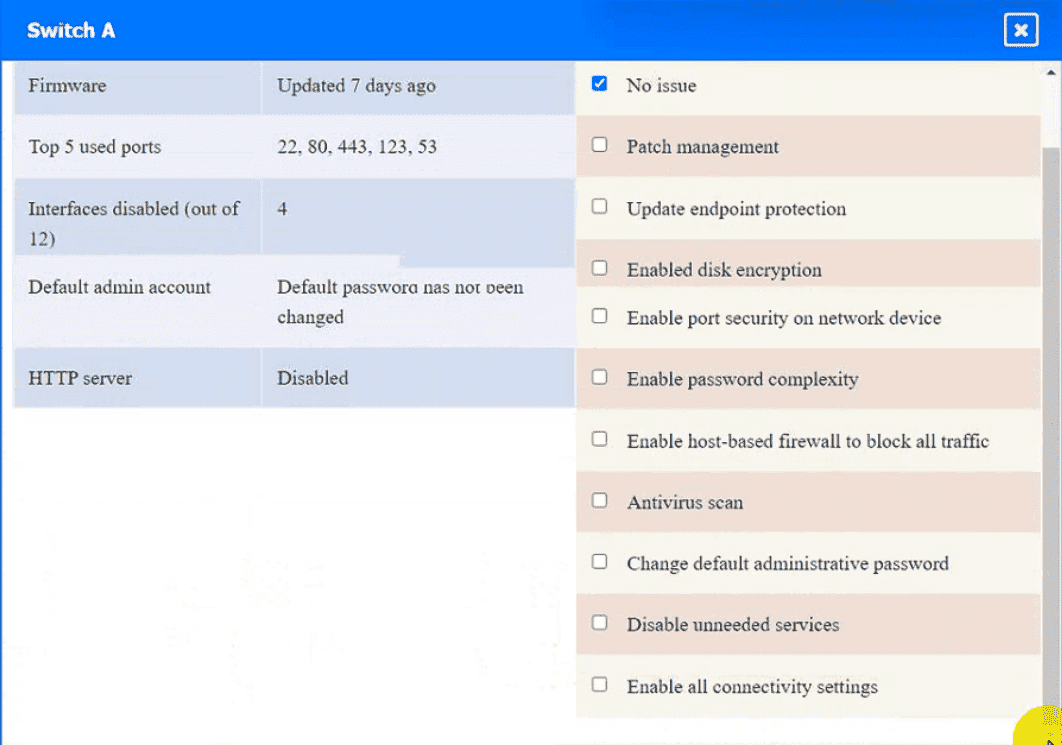
Switch B:
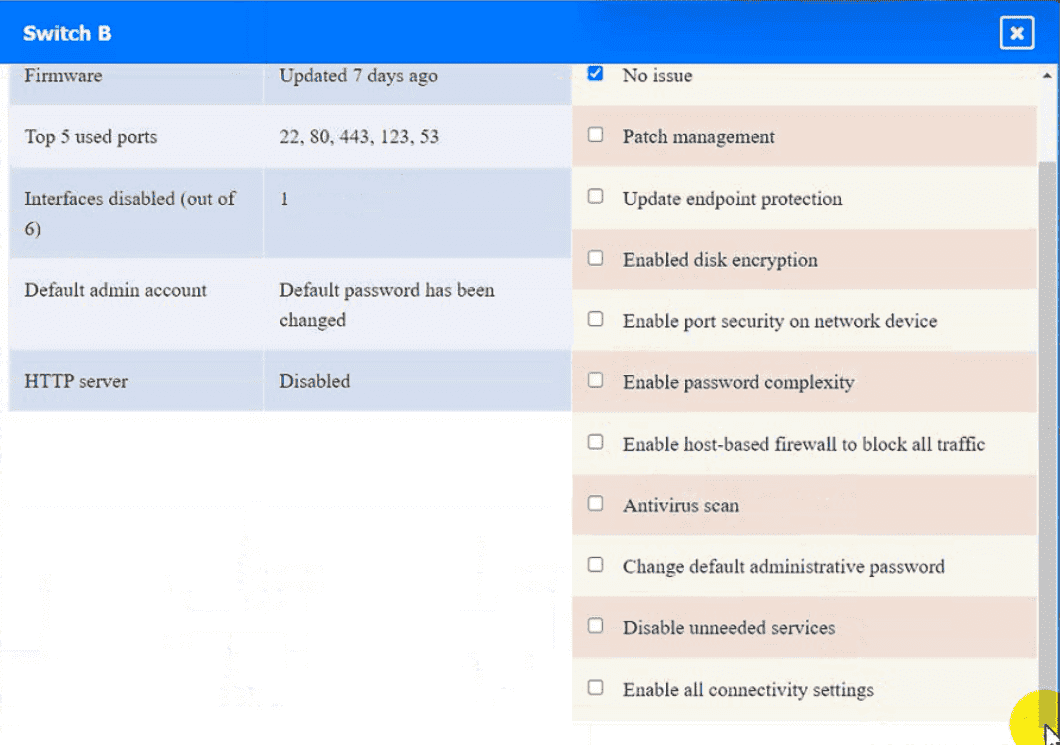
Laptop B
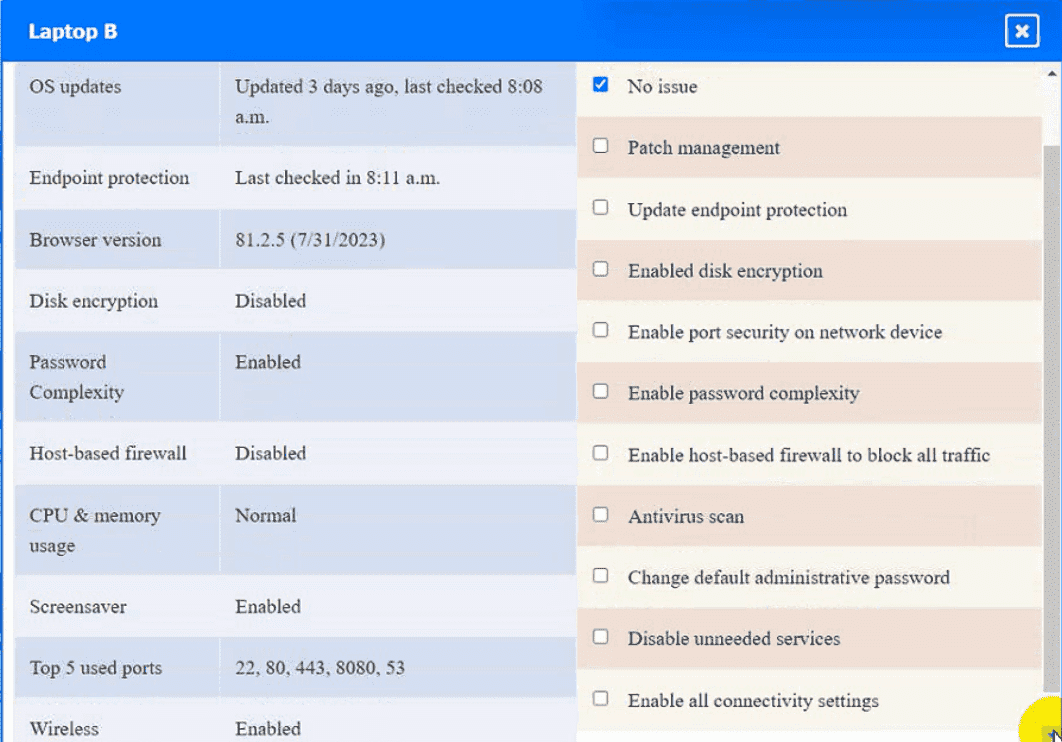
PC B
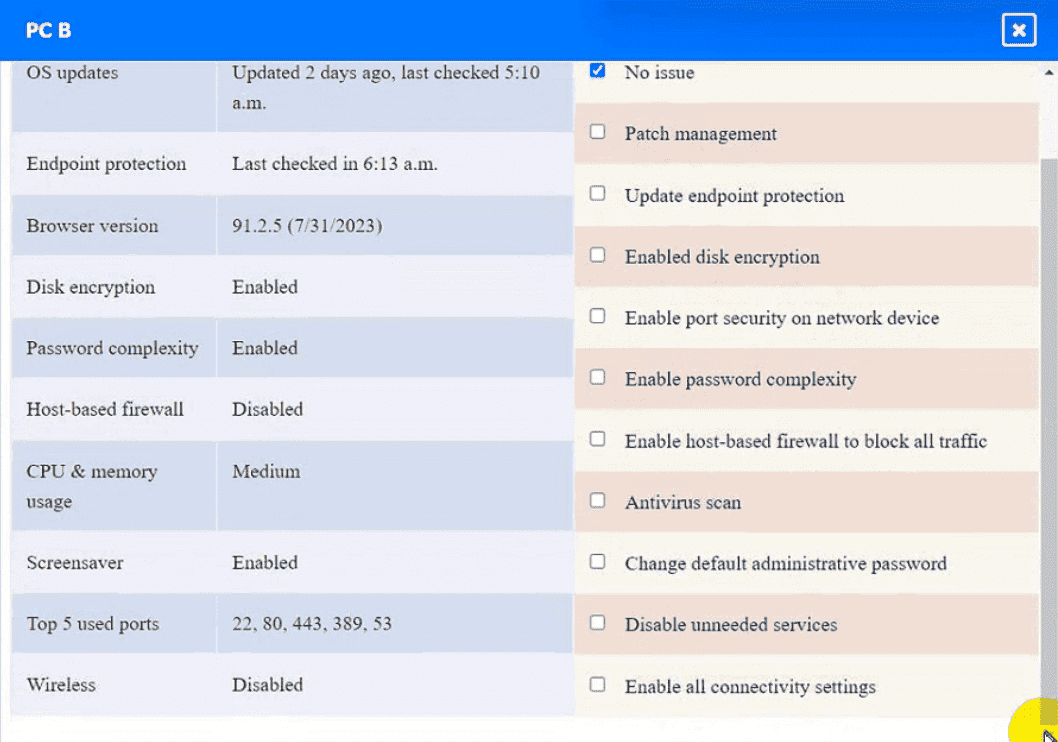
PC C
Server A
WAP A: No issue found. The WAP A is configured correctly and meets therequirements.
PC A = Enable host-based firewall to block all traffic
This option will turn off the host-based firewall and allow all traffic to pass through. This will comply with the requirement and also improve the connectivity of PC A to other devices on the network. However, this option will also reduce the security of PC A and make it more vulnerable to attacks. Therefore, it is recommended to use other security measures, such as antivirus, encryption, and password complexity, to protect PC A from potential threats.
Laptop A: Patch management
This option will install the updates that are available for Laptop A and ensure that it has the most recent security patches and bug fixes. This will comply with the requirement and also improve the performance and stability of Laptop A. However, this option may also require a reboot of Laptop A and some downtime during the update process. Therefore, it is recommended to backup any important data and close any open applications before applying the updates.
Switch A: No issue found. The Switch A is configured correctly and meets the requirements.
Switch B: No issue found. The Switch B is configured correctly and meets the requirements.
Laptop B: Disable unneeded services
This option will stop and disable the telnet service that is using port 23 on Laptop B. Telnet is a cleartext service that transmits data in plain text over the network, which exposes it to eavesdropping, interception, and modification by attackers. By disabling the telnet service, you will comply with the requirement and also improve the security of Laptop B. However, this option may also affect the functionality of Laptop B if it needs to use telnet for remote administration or other purposes. Therefore,it is recommended to use a secure alternative to telnet, such as SSH or HTTPS, that encrypts the data in transit.
PC B:Enable disk encryption
This option will encrypt the HDD of PC B using a tool such as BitLocker or VeraCrypt. Disk encryption is a technique that protects data at rest by converting it into an unreadable format that can only be decrypted with a valid key or password. By enabling disk encryption, you will comply with the requirement and also improve the confidentiality and integrity of PC B's data. However, this option may also affect the performance and usability of PC B, as it requires additional processing time and user authentication to access the encrypted data. Therefore, it is recommended to backup any important data and choose a strong key or password before encrypting the disk.
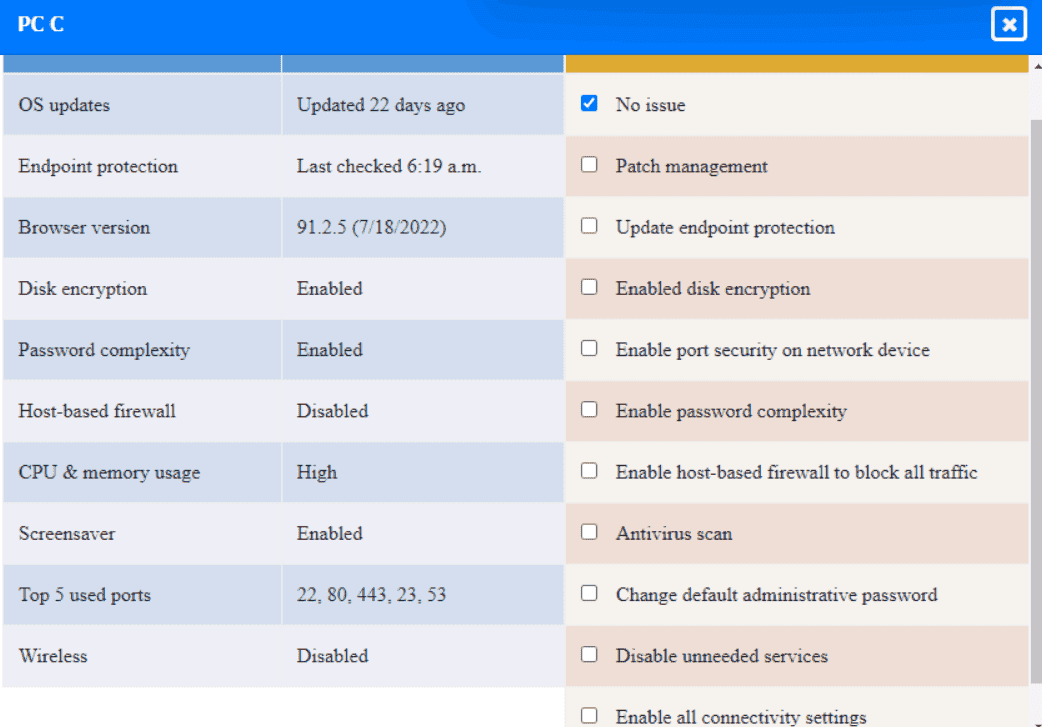
PC C: Disable unneeded services
This option will stop and disable the SSH daemon that is using port 22 on PC C. SSH is a secure service that allows remote access and command execution over an encrypted channel. However, port 22 is thedefault and well-known port for SSH, which makes it a common target for brute-force attacks and port scanning. By disabling the SSH daemon on port 22, you will comply with the requirement and also improve the security of PC C. However, this option may also affect the functionality of PC C if it needs to use SSH for remote administration or other purposes. Therefore, it is recommended to enable the SSH daemon on a different port, such as 4022, by editing the configuration file using the following command:
sudo nano /etc/ssh/sshd_config
Server A. Need to select the following:
Question 3 Domain 1 Governance, Risk, and Compliance
After an organization met with its ISAC, the organization decided to test the resiliency of its security controls against a small number of advanced threat actors. Which of the following will enable the security administrator to accomplish this task?
Adversary emulation simulates specific advanced persistent threat (APT) behaviors and techniques to test an organization's security posture. In SecurityX CAS-005, this is part of red-teaming and purple-teaming strategies for realistic resilience testing.
Reliability factors (B) relate to operational uptime, not threat simulation.
Honeypots (C) attract attackers but do not directly emulate specific adversaries.
Internal reconnaissance (D) is one phase of an attack simulation, not the full emulation of advanced threat actors.
Get the complete CAS-005 question set
$20$40
Question 4 Domain 2 Security Architecture
A security architect is troubleshooting an issue with an OIDC implementation. The architect reviews the following configuration and errors:
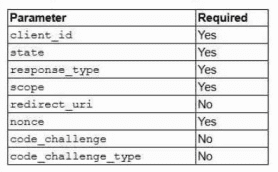
Error: Invalid authentication request code
Which of the following is the most likely cause of the error?
Question 5 Domain 4 Security Operations
Which of the following supports the process of collecting a large pool of behavioral observations to inform decision-making?
Collecting a large pool of behavioral observations requires handling vast datasets, which is the domain ofBig Data. Big Data technologies enable the storage, processing, and analysis of large-scale data (e.g., user behavior logs) to inform decisions, a key capability in security analytics.
Option A:Linear regression is a statistical method for modeling relationships, not collecting data.
Option B:Distributed consensus relates to agreement in distributed systems (e.g., blockchain), not data collection.
Option C:Big Data directly supports collecting and analyzing large datasets for insights, fitting the question perfectly.
Option D:Machine learning uses data to train models but relies on data being collected first, often via Big Data.
Question 6 Domain 2 Security Architecture
An organization recently implemented a policy that requires all passwords to be rotated every 90 days. An administrator observes a large volume of failed sign-on logs from multiple servers that are often accessed by users. The administrator determines users are disconnecting from the RDP session but not logging off. Which of the following should the administrator do to prevent account lockouts?
When users disconnect from Remote Desktop Protocol (RDP) sessions without properly logging off, their sessions remain active on the server. If their passwords are changed due to the 90-day rotation policy, these lingering sessions may attempt to reauthenticate using outdated credentials, leading to multiple failed login attempts and potential account lockouts.
Automating the logout of inactive sessions ensures that disconnected or idle sessions are terminated after a specified period, preventing stale sessions from causing authentication issues. This approach aligns with best practices for session management and helps maintain security compliance.
Question 7 Domain 1 Governance, Risk, and Compliance
An organization is prioritizing efforts to remediate or mitigate risks identified during the latest assessment. For one of the risks, a full remediation was not possible, but the organization was able to successfully apply mitigations to reduce the likelihood of the impact. Which of the following should the organization perform next?
After applying mitigations that reduce the likelihood of a risk's impact, the next step is toassess the residual risk---the risk that remains after controls are implemented. This ensures the organization understands if the mitigation is sufficient or if further action is needed, aligning with risk management best practices.
Option A:Correct---residual risk assessment is the logical next step to evaluate the effectiveness of mitigations.
Option B:Updating the threat model might follow but isn't immediate; residual risk comes first.
Option C:Moving to the next risk skips evaluating the current mitigation's success.
Option D:Recalculating impact magnitude is part of residual risk assessment but isn't the full process.
What the CompTIA CAS-005 Exam Covers
Exam domains verified against the Official CompTIA CAS-005 exam guide, last checked November 2026.
Domain 1 Governance, Risk, and Compliance
20%Implement governance components that align with organizational security requirements and compliance frameworks. Focus on phishing and social engineering threats, security communication protocols, and risk assessment methods like COBIT framework implementation.
Domain 2 Security Architecture
27%Analyze security requirements to design resilient systems with proper component placement and configuration. Design secure network architectures, including firewalls and intrusion prevention systems, for complex enterprise environments supporting zero-trust and hybrid cloud scenarios.
Domain 3 Security Engineering
31%Troubleshoot common issues with identity and access management components in enterprise environments. Apply cryptographic solutions, design secure integrations, and solve real-world authentication and authorization challenges across diverse platforms.
Sample question from this domain above Q2
Domain 4 Security Operations
22%Analyze security data to enable monitoring and response across complex environments. Implement threat detection, incident response procedures, and digital forensics capabilities to identify and mitigate security events in real time.
Sample question from this domain above Q5
CAS-005 Exam FAQ
Common questions about the exam itself
What makes the CAS-005 SecurityX exam harder than CompTIA's mid-level security certifications?
Do I need Security+ or CySA+ before attempting SecurityX CAS-005?
Which objective area on CAS-005 gives most candidates the most trouble?
How long should I realistically prepare for SecurityX CAS-005?
What happens on exam day for CAS-005, and is it different from lower-level CompTIA exams?
What are the retake and rescheduling rules for CAS-005?
How long does SecurityX certification stay valid and what renewal looks like?
What job roles does SecurityX CAS-005 prepare me for?
How does SecurityX CAS-005 relate to the old CASP+ exam, and should I worry about version changes?
Is there an exam track or pathway that SecurityX fits into?
Other CompTIA Exams
Free practice questions for more CompTIA certification exams