
Free Citrix 1Y0-440 Exam Practice Questions & Explanations
Prepared & Reviewed by the ValidExamDumps Editorial Team
At ValidExamDumps, we consistently monitor updates to the Citrix 1Y0-440 exam questions by Citrix. Whenever our team identifies changes in the exam questions, objectives, focus areas or requirements, We immediately update our exam questions for both PDF and online practice exams. This commitment ensures our customers always have access to the most current and accurate questions. By preparing with these up to date and 100% exam domain coverage questions, our customers can successfully pass the Citrix Architecting a Citrix Networking Solution exam on their first attempt without needing additional materials or study guides.
Other certification materials providers often include outdated or removed questions by Citrix in their 1Y0-440 exam. These outdated questions lead to customers failing their Citrix Architecting a Citrix Networking Solution exam. In contrast, we ensure our questions bank includes only precise and up-to-date questions. Our main priority is your success in the Citrix 1Y0-440 exam, not profiting from selling obsolete exam questions in PDF or Online Practice Test.
Scenario: A Citrix Architect has set up NetScaler MPX devices in high availability mode with version 12.0. 53.13 nc. These are placed behind a Cisco ASA 5505 Firewall is configured to block traffic using access control lists. The network address translation (NAT) is also performed on the firewall.
The following requirements were captured by the architect during the discussion held as part of the NetScaler security implementation project with the customer's security team:
The NetScaler device:
Should monitor the rate of traffic either on a specific virtual entity or on the device. It should be able to mitigate the attacks from a hostile client sending a flood of requests. The NetScaler device should be able to stop the HTTP, TCP, and DNS based requests.
Needs to protect backend servers from overloading.
Needs to queue all the incoming requests on the virtual server level instead of the service level.
Should provide access to resources on the basis of priority.
Should provide protection against well-known Windows exploits, virus-infected personal computers, centrally managed automated botnets, compromised webservers, known spammers/hackers, and phishing proxies.
Should provide flexibility to enforce the desired level of security check inspections for the requests originating from a specific geolocation database.
Should block the traffic based on a pre-determined header length, URL length, and cookie length. The device should ensure that characters such as a single straight quote (*); backslash(\), and semicolon (;) are either blocked, transformed, or dropped while being sent to the backend server.
Which two security features should the architect configure to meet these requirements? (Choose two.)
Scenario: A Citrix Architect has set up Citrix ADC MPX devices in high availability mode with version 12.0.53.13 nc. These are placed behind a Cisco ASA 5505 firewall. The Cisco ASA firewall is configured to block traffic using access control lists. The network address translation (NAT) is also performed on the firewall. The following requirements were captured by the architect during the discussion held as part of the Citrix ADC security implementation project with the customer's security team: The Citrix ADC MPX device:
* should monitor the rate of traffic either on a specific virtual entity or on the device. It should be able to mitigate the attacks from a hostile client sending a flood of requests. The Citrix ADC device should be able to stop the HTTP, TOP, and DNS based requests.
* needs to protect backend servers from overloading.
* needs to queue all the incoming requests on the virtual server level instead of the service level.
* should provide access to resources on the basis of priority.
* should provide protection against well-known Windows exploits, virus-infected personal computers, centrally managed automated botnets. compromised webservers, known spammersThackers. and phishing proxies.
* should provide flexibility to enforce the desired level of security check inspections for the requests originating from a specific geolocation database.
* should block the traffic based on a predetermined header length, URL length, and cookie length.The device should ensure that characters such as a single straight quote (') backslash (): and semicolon (;) are either blocked, transformed, or dropped while being sent to the backend server.
Which security feature should the architect implement to meet these requirements?
Scenario: A Citrix Architect needs to design a new solution within Amazon Web Services (AWS) The architect would like to create a high availability Citrix ADC VPX pair to provide load balancing for applications hosted in the AWS deployment within a single availability zone which will receive traffic arriving from the Internet.
Which configuration should the architect choose to accomplish this?
Scenario: A Citrix Architect needs to conduct a capabilities assessment for an organization that wants to create a new Citrix ADC deployment. One of the
organization's core business drivers is to ensure that key applications are always available to users.
Which capabilities must the architect verify to assess if the requirement is feasible with the current infrastructure?
Scenario: A Citrix Architect has deployed an authentication setup with a ShareFile load-balancing virtual server. The NetScaler is configured as the Service Provider and Portalguard server is utilized as the SAML Identity Provider. While performing the functional testing, the architect finds that after the users enter their credentials on the logon page provided by Portalguard, they get redirected back to the Netscaler Gateway page at uri /cgi/samlauth/ and receive the following error.

The events in the /var/log/ns.log at the time of this issue are as follows:
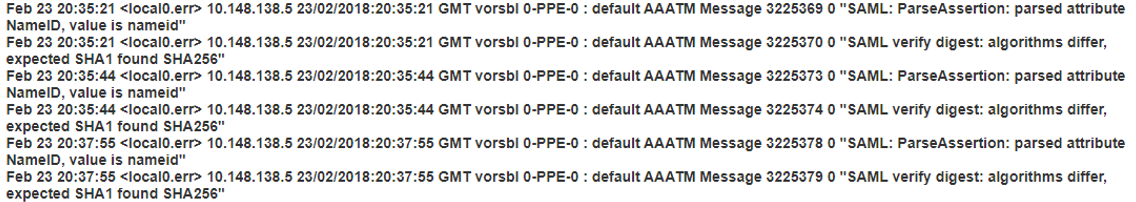
What should the architect change in the SAML action to resolve this issue?