Key details for this exam, checked against the published exam outline
Each question shows the correct answer and an explanation of why it is right
[Security Concepts]
What is the term for having information about threats and threat actors that helps mitigate harmful events that would otherwise compromise networks or systems?
Threat intelligence is the term for having information about threats and threat actors that helps mitigate harmful events that would otherwise compromise networks or systems. Threat intelligence is the result of collecting, analyzing, and contextualizing data from various sources, such as network traffic, logs, feeds, reports, etc. Threat intelligence provides insights into the tactics, techniques, and procedures (TTPs) of adversaries, as well as their motivations, intentions, and capabilities.Threat intelligence can help organizations to detect, prevent, and respond to cyberattacks, as well as to improve their security posture and resilience12. The other options are not correct, because they are not terms for having information about threats and threat actors.Trusted automated exchange is a concept that refers to the sharing of threat intelligence among trusted entities in a timely and secure manner3. Indicators of Compromise (IoCs) are pieces of forensic data, such as IP addresses, domains, hashes, etc., that indicate a potential intrusion or compromise of a system or network. The Exploit Database is a public repository of exploits and vulnerable software, maintained by Offensive Security.Reference:
1: What is Cyber Threat Intelligence? - Cisco
2: Cisco Talos Intelligence Group - Comprehensive Threat Intelligence
3: Trusted Automated Exchange of Intelligence Information (TAXII) Version 2.0
[4]: What Are Indicators of Compromise (IOCs)? - Cisco
[5]: The Exploit Database - Exploits for Penetration Testers, Researchers, and Ethical Hackers
[Security Concepts]
An organization deploys multiple Cisco FTD appliances and wants to manage them using one centralized
solution. The organization does not have a local VM but does have existing Cisco ASAs that must migrate over
to Cisco FTDs. Which solution meets the needs of the organization?
Cisco FMC is the centralized management solution for Cisco FTD appliances. It provides configuration, monitoring, analysis, and reporting capabilities for FTD devices. Cisco FMC can also manage Cisco ASAs that have been converted to FTD devices. Cisco FMC can be deployed as a physical or virtual appliance, or as a cloud service (CDO). However, since the organization does not have a local VM, CDO is not an option. Cisco FDM is the on-box management solution for FTD devices, which does not support centralized management or ASA migration. CSM is the legacy management solution for Cisco ASAs, which does not support FTD devices.Reference:=
Some possible references are:
Cisco Firepower Management Center Configuration Guide, Version 6.7
Install and Upgrade FTD on Firepower Appliances
Firepower Threat Defense simplifies application security
[Security Concepts]
Which Talos reputation center allows for tracking the reputation of IP addresses for email and web traffic?
The IP and Domain Reputation Center is a service provided by Talos, Cisco's Security Intelligence and Research Group, that tracks the reputation of IP addresses and domains for email and web traffic. The IP and Domain Reputation Center collects and analyzes data from millions of deployed web, email, firewall and IPS appliances, as well as open-source data sets, endpoint intelligence, and network intrusions. The IP and Domain Reputation Center transforms this data into actionable threat intelligence and tools to improve security posture. The IP and Domain Reputation Center allows users to look up websites, URLs and IP addresses and the information Talos has about them, such as their reputation score, category, volume, and threat level.The IP and Domain Reputation Center also provides threat data overviews, such as the top email and spam senders by country, and the standard categories used to classify website content and attack types123.Reference:=1: Reputation Center - A Real Time Threat Detection Service || Cisco Talos Intelligence Group - Comprehensive Threat Intelligence2: IP & Domain Reputation Center - Talos Intelligence3: Talos Reputation Center overview | Talos Support Documents
[Security Concepts]
Which DevSecOps implementation process gives a weekly or daily update instead of monthly or quarterly in the applications?
Unlike the traditional software life cycle, the CI/CD implementation process gives a weekly or daily update
instead of monthly or quarterly. The fun part is customers won't even realize the update is in their applications,
as they happen on the fly.
[Content Security]
How does the Cisco WSA enforce bandwidth restrictions for web applications?
The Cisco WSA can enforce bandwidth restrictions for web applications by using the Application Visibility and Control (AVC) engine. The AVC engine allows the WSA to identify and control application activity on the network, and to apply bandwidth limits to certain application types or individual applications. The WSA dynamically creates a scavenger class QoS policy and applies it to each client that connects through the WSA. The scavenger class QoS policy assigns a low priority to the application traffic and limits the bandwidth usage based on the configured settings. This way, the WSA can prevent congestion and ensure fair allocation of bandwidth among different applications and users.Reference:
User Guide for AsyncOS 11.8 for Cisco Web Security Appliances - GD (General Deployment) - Managing Access to Web Applications
WSA - limit bandwidth - Cisco Community
[Security Concepts]
Which CLI command is used to register a Cisco FirePower sensor to Firepower Management Center?
a Cisco FirePower sensor to Firepower Management Center isconfigure manager add <host><key>. This command establishes a secure connection between the sensor and the FMC using a registration key. The<host>parameter can be either the IP address or the hostname of the FMC. The<key>parameter can be any alphanumeric string that matches the one configured on the FMC.This command is executed on the sensor's CLI in the privileged EXEC mode12.Reference:1: Implementing and Operating Cisco Security Core Technologies (SCOR) course, Module 2: Network Security, Lesson 2: Deploying Cisco Firepower Next-Generation Firewall, Topic: Registering the Cisco Firepower NGFW to the FMC2: Firepower Management Center Configuration Guide, Version 6.6 - Device Management Basics
[Cisco Secure Firewall Management Center] - Cisco.
[Security Concepts]
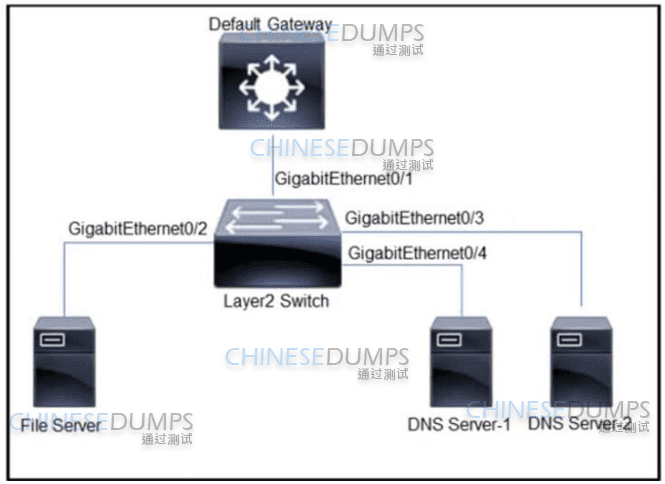
Refer to the exhibit. All servers are in the same VLAN/Subnet. DNS Server-1 and DNS Server-2 must communicate with each other, and all servers must communicate with default gateway multilayer switch. Which type of private VLAN ports should be configured to prevent communication between DNS servers and the file server?
to configure GigabitEthernet0/1 as promiscuous port, GigabitEthernet0/2 as isolated port and GigabitEthernet0/3 and GrgabitEthernet0/4 as community ports. This way, the default gateway can communicate with all servers, the isolated port can only communicate with the promiscuous port, and the community ports can communicate with each other and the promiscuous port. This prevents the file server from communicating with the DNS servers, as required by the question.
To understand the concept of private VLANs and port types, you can refer to the following sections of the source book:
Section 1.1.2: Describe the concepts of network security
Section 1.1.2.1: Describe the concepts of private VLANs
Section 1.1.2.2: Describe the concepts of port types
Section 1.1.2.3: Describe the concepts of PVLAN edge
Section 1.1.2.4: Describe the concepts of protected ports
Section 1.1.2.5: Describe the concepts of PVLAN configuration
Implementing and Operating Cisco Security Core Technologies (SCOR) v1.0
Private VLAN - GeeksforGeeks
A quick summarized view to Private VLAN (PVLAN) - Cisco Learning Network
Exam domains verified against: Official Cisco 350-701 exam guide, last checked October 2026.
Understand network security strategies and firewall-based intrusion prevention to protect infrastructure. Learn network segmentation with VLANs and Layer 2 security, plus NetFlow components and configuration for security monitoring.
2.1 Describe network security solutions and deployment models that provide intrusion prevention and firewall capabilities; 2.2 Describe security monitoring and telemetry technologies; 2.3 Configure network infrastructure security methods (network segmentation using VLANs or SGTs; Layer 2 and port security; DHCP snooping; Dynamic ARP inspection; storm control; and defenses against MAC, ARP, VLAN hopping, STP, and DHCP rogue attacks); 2.4 Select management options for network security solutions (single vs. multidevice manager, in-band vs. out-of-band, on-premises vs. cloud with Cisco Security Cloud Control); 2.5 Describe CIS benchmarks for hardening devices such as Cisco Secure Firewall (FTD) and Cisco IOS XE; 2.6 Troubleshoot AAA for device and network access such as TACACS+ and RADIUS; 2.7 Configure secure network management of perimeter security and infrastructure devices such as SNMPv3, NetConf, RestConf, APIs, secure syslog, and NTP with authentication; 2.8 Implement access control policies, AVC, URL filtering, malware protection, and intrusion prevention using Cisco Secure Firewall (FTD); 2.9 Configure site-to-site and remote access VPN using Cisco Secure Firewall (FTD) and Cisco Secure Client; 2.10 Troubleshoot VPN tunnel establishment on Cisco Secure Firewall (FTD)
3.1 Describe security responsibility within common Cloud Shared Responsibility Models; 3.2 Select security capabilities, deployment models, cloud security frameworks, and policy management to secure the cloud; 3.3 Select security solutions for cloud environments (public; private; hybrid; community cloud; NIST 800-145 SaaS, PaaS, and IaaS; and Cloud Access Security Broker); 3.4 Describe network, application, and data security in cloud environments with solutions such as Cisco Multicloud Defense and Cisco Secure Workload; 3.5 Configure Splunk to ingest cloud logging and monitoring data from other security solutions; 3.6 Describe application and workload security concepts including eBPF; 3.7 Describe DevSecOps (Infrastructure as Code security, CI/CD pipeline, container orchestration, and secure software development)
4.1 Describe Security Service Edge (SSE) and Secure Access Service Edge (SASE); 4.2 Configure Cisco Secure Access Secure Internet Access; 4.3 Configure Cisco Secure Access Secure Private Access; 4.4 Configure data loss prevention and AI guardrails for secure internet access; 4.5 Interpret Cisco Secure Access Investigate scores and indicators
Compare Endpoint Protection Platforms with Endpoint Detection and Response solutions, then configure antimalware using Cisco Secure Endpoint. Establish outbreak control and quarantine procedures, and deploy multifactor authentication strategies for endpoint devices.
Configure network access control mechanisms including 802.1X, MAC Authentication Bypass, and WebAuth for guest services and BYOD policies. Apply identity management and posture assessment, then use Change of Authorization mechanisms for detailed network access control.
Common questions about the exam itself

