At ValidExamDumps, we consistently monitor updates to the Cisco 350-501 exam questions by Cisco. Whenever our team identifies changes in the exam questions, objectives, focus areas or requirements, We immediately update our exam questions for both PDF and online practice exams. This commitment ensures our customers always have access to the most current and accurate questions. By preparing with these up to date and 100% exam domain coverage questions, our customers can successfully pass the Cisco Implementing and Operating Cisco Service Provider Network Core Technologies exam on their first attempt without needing additional materials or study guides.
Other certification materials providers often include outdated or removed questions by Cisco in their 350-501 exam. These outdated questions lead to customers failing their Cisco Implementing and Operating Cisco Service Provider Network Core Technologies exam. In contrast, we ensure our questions bank includes only precise and up-to-date questions. Our main priority is your success in the Cisco 350-501 exam, not profiting from selling obsolete exam questions in PDF or Online Practice Test.
A network engineer must implement SNMPv2 with these parameters
Enable SNMP community string C1sc0 with read-only permissions.
Enable interface index persistence.
Restrict the SNMP community to only the monitoring server with IP address 198.18 19 100/32.
Provide view-only access to ospflfEntry and ospfNbrEntry.
Which configuration must the engineer apply?
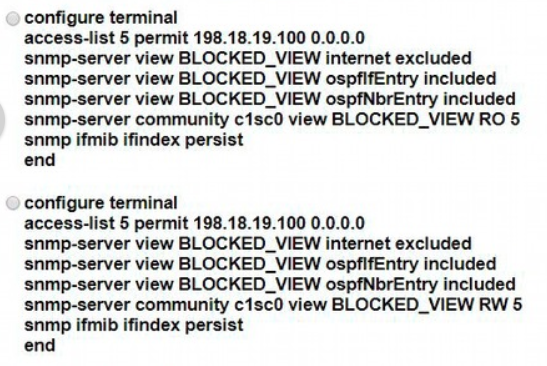
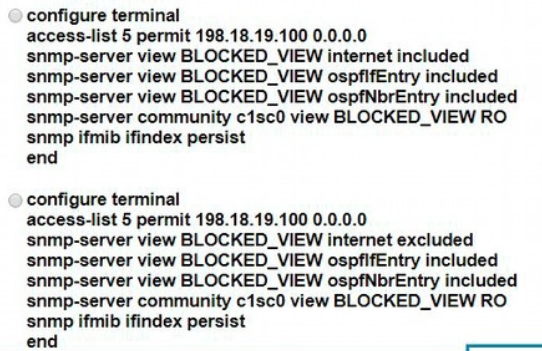
SNMP Community String: Enable SNMP community stringC1sc0with read-only permissions.
Interface Index Persistence: Enable interface index persistence.
Restrict SNMP Community: Restrict the SNMP community to only the monitoring server with IP address198.18.19.100/32.
View-Only Access: Provide view-only access toospflfEntryandospfNbrEntry.
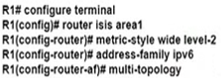
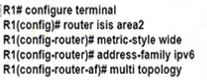
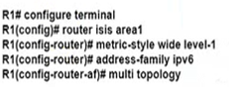
Refer to the exhibit.
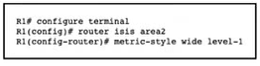
An engineer is configuring multitiopology IS-IS for IPv6 on router R1. Which additional configuration must be applied to complete the task?
A)
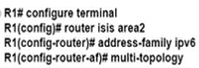
B)
C)
How can a network administrator secure rest APIs?
To secure REST APIs, a network administrator should ensure that user sessions are authenticated and that the appropriate privilege level is provided for each user. This means that each API request should come with authentication credentials, and the server should validate these credentials for every request. This approach helps to maintain the stateless nature of REST APIs and ensures that only authorized users can access or modify resources.Reference: Best practices for securing REST APIs include using HTTPS, token-based authentication, and proper validation of input parameters to prevent common security vulnerabilities.
Which two tasks must an engineer perform when implementing LDP NSF on the network? (Choose two.)
When implementing LDP NSF (Nonstop Forwarding) on the network, an engineer must perform the following tasks:
Implement direct connections for LDP peers: This ensures that LDP sessions can be reestablished quickly after a switchover.
Enable NSF for the link-state routing protocol in use on the network: This allows the routing protocol to maintain its state during a switchover, ensuring seamless operation.
How does an untrusted interface at the boundary of an administrative domain handle incoming packets?

