
Free Amazon SCS-C02 Exam Practice Questions & Explanations
Prepared & Reviewed by the ValidExamDumps Editorial Team
At ValidExamDumps, we consistently monitor updates to the Amazon SCS-C02 exam questions by Amazon. Whenever our team identifies changes in the exam questions, objectives, focus areas or requirements, We immediately update our exam questions for both PDF and online practice exams. This commitment ensures our customers always have access to the most current and accurate questions. By preparing with these up to date and 100% exam domain coverage questions, our customers can successfully pass the Amazon AWS Certified Security - Specialty (old) exam on their first attempt without needing additional materials or study guides.
Other certification materials providers often include outdated or removed questions by Amazon in their SCS-C02 exam. These outdated questions lead to customers failing their Amazon AWS Certified Security - Specialty (old) exam. In contrast, we ensure our questions bank includes only precise and up-to-date questions. Our main priority is your success in the Amazon SCS-C02 exam, not profiting from selling obsolete exam questions in PDF or Online Practice Test.
[Incident Response]
A company has a requirement that no Amazon EC2 security group can allow SSH access from the CIDR block 0.0.0.070. The company wants to monitor compliance with this requirement at all times and wants to receive a near-real-time notification if any security group is noncompliant.
A security engineer has configured AWS Config and will use the restricted-ssh managed rule to monitor the security groups.
What should the security engineer do next to meet these requirements?
Enable AWS Config Managed Rule:
Activate therestricted-sshAWS Config managed rule to evaluate security groups for SSH access from0.0.0.0/0.
Create an EventBridge Rule:
Configure an EventBridge rule to trigger on compliance change events generated by therestricted-sshmanaged rule.
Set Target to SNS:
Configure the EventBridge rule to target an SNS topic that notifies the security team when a noncompliant security group is detected.
Advantages:
Provides near-real-time notifications.
Fully integrates with AWS native services for compliance monitoring.
AWS Config Managed Rules
Amazon EventBridge Documentation
[Identity and Access Management]
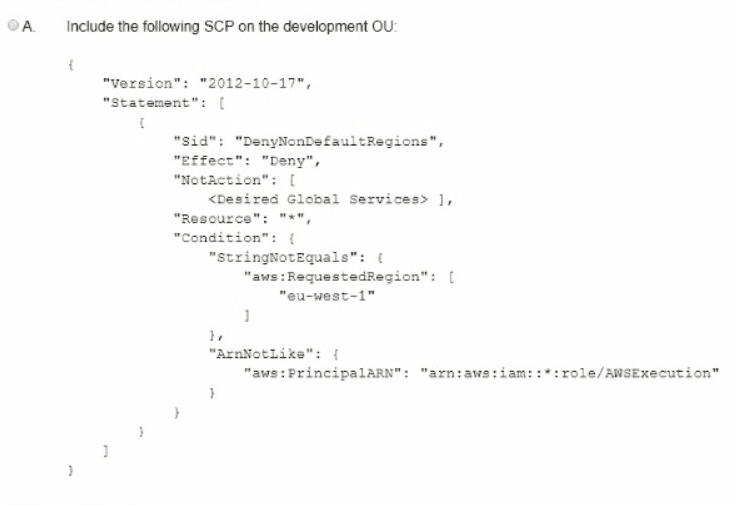
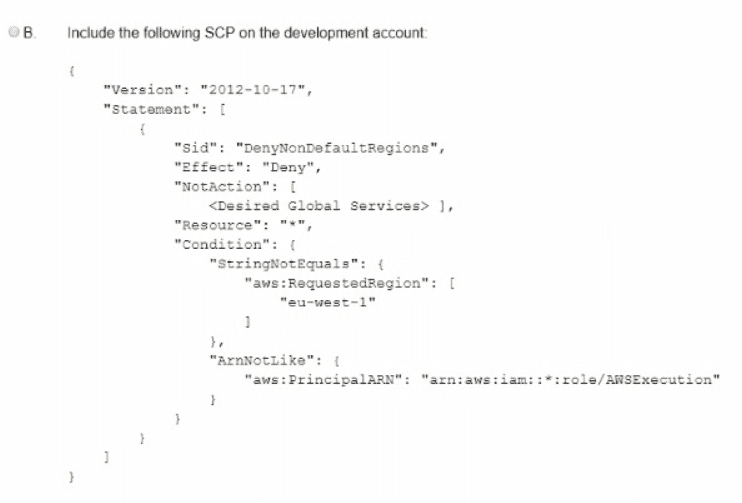
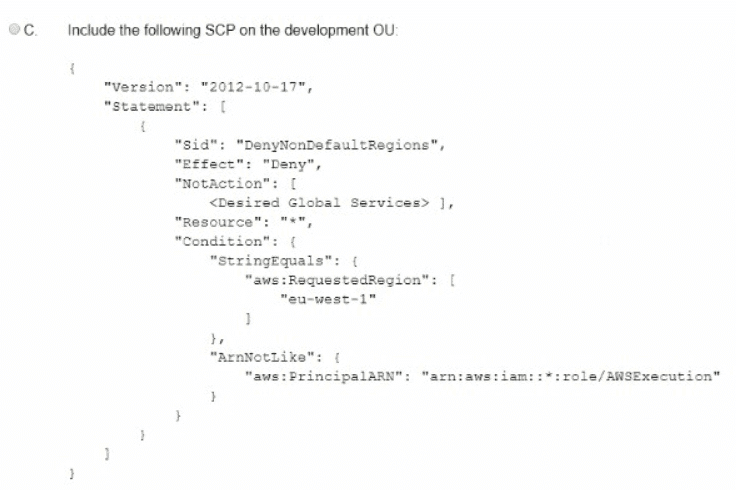
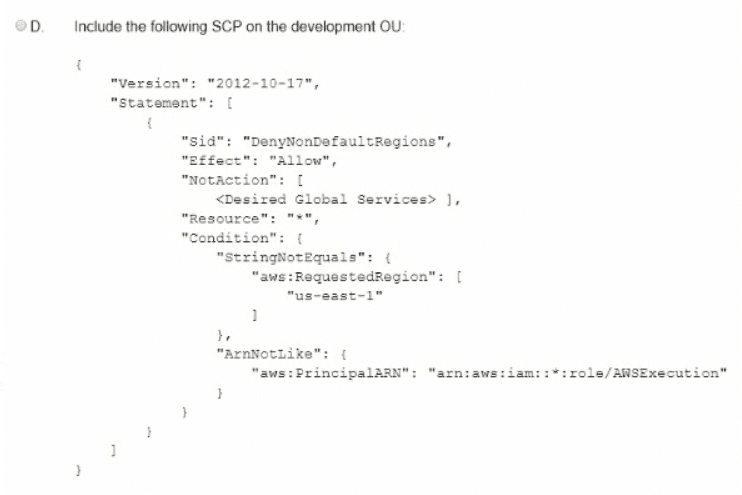
A company is using IAM Organizations. The company wants to restrict IAM usage to the eu-west-1 Region for all accounts under an OU that is named "development." The solution must persist restrictions to existing and new IAM accounts under the development OU.
[Identity and Access Management]
A company uses HTTP Live Streaming (HL'S) to stream live video content to paying subscribers by using Amazon CloudFront. HLS splits the video content into chunks sothat the user can request the right chunk based on different conditions. Because the video events last for several hours, the total video is made up of thousands of chunks.
The origin URL is not disclosed, and every user is forced to access the CloudFront URL. The company has a web application that authenticates the paying users against aninternal repository and a CloudFront key pair that is already issued.
What is the simplest and MOST effective way to protect the content?
Utilizing CloudFront signed cookies is the simplest and most effective way to protect HLS video content for paying subscribers. Signed cookies provide access control for multiple files, such as video chunks in HLS streaming, without the need to generate a signed URL for each video chunk. This method simplifies the process for long video events with thousands of chunks, enhancing user experience while ensuring content protection.
[Infrastructure Security]
An online media company has an application that customers use to watch events around the world. The application is hosted on a fleet of Amazon EC2 instances that run Amazon Linux 2. The company uses AWS Systems Manager to manage the EC2 instances. The company applies patches and application updates by using the AWS-AmazonLinux2DefaultPatchBaseline patching baseline in Systems Manager Patch Manager.
The company is concerned about potential attacks on the application during the week of an upcoming event. The company needs a solution that can immediately deploy patches to all the EC2 instances in response to a security incident or vulnerability. The solution also must provide centralized evidence that the patches were applied successfully.
Which combination of steps will meet these requirements? (Select TWO.)
[Identity and Access Management]
A security engineer must troubleshoot an administrator's inability to make an existingAmazon S3 bucket public in an account that is part of an organization n IAM Organizations. The administrator switched the role from the master account to a member account and then attempted to make one S3 bucket public. This action was immediately denied
Which actions should the security engineer take to troubleshoot the permissions issue? (Select TWO.)
A is incorrect because reviewing the cross-account role permissions and the S3 bucket policy is not enough to troubleshoot the permissions issue. You also need to verify that the Amazon S3 block public access option in the member account is deactivated, as well as the permissions boundary and the SCPs of the role in the member account.
D is correct because evaluating the SCPs and the permissions boundary of the role in the member account can help you identify any missing permissions or explicit denies that could prevent the administrator from making the S3 bucket public.
E is correct because ensuring that the S3 bucket policy explicitly allows the s3 PutBucketPublicAccess action for the role in the member account can help you override any block public access settings that could prevent the administrator from making the S3 bucket public.